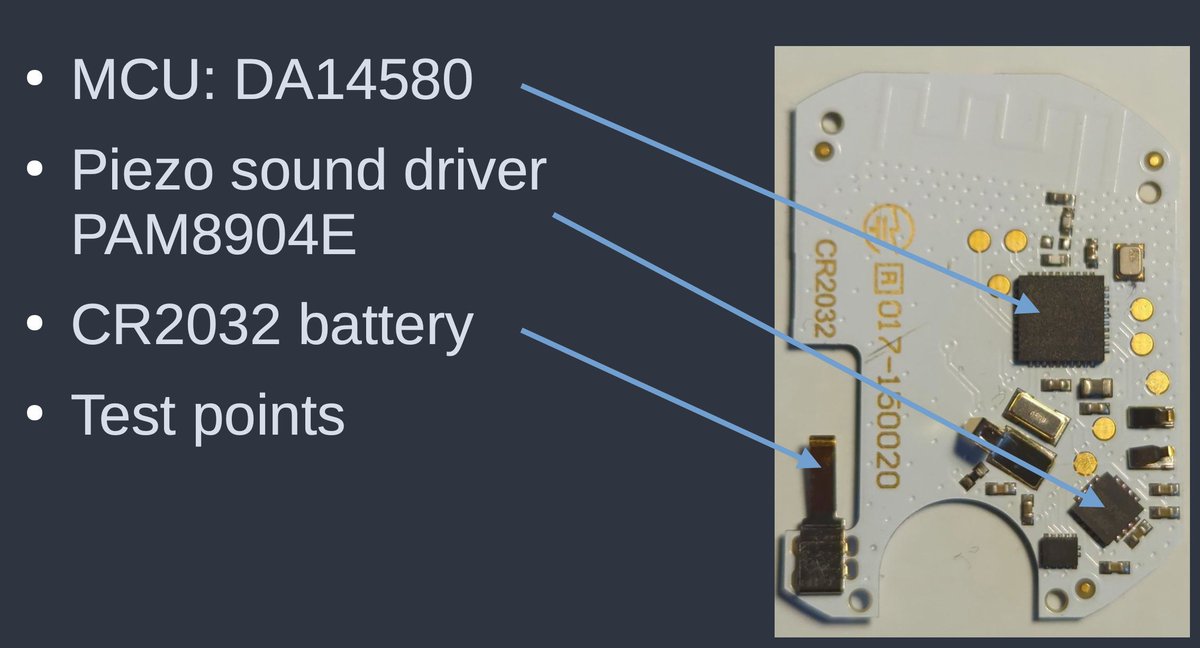
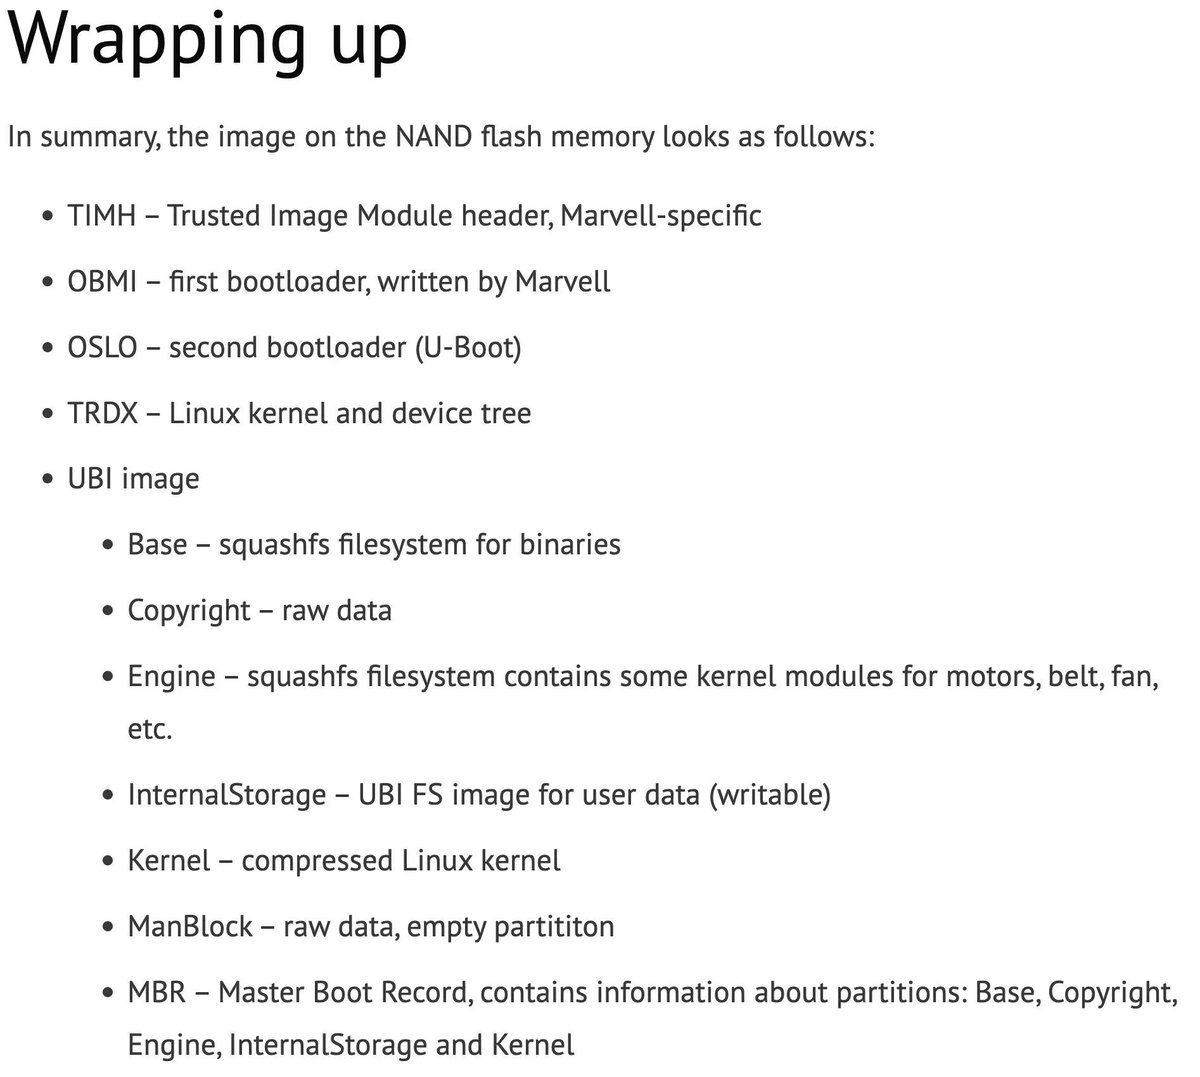
Claude built a QEMU machine that boots the Xiaomi Smart Band 10's real kernel and OS from flash and NAND dumps of my own band.
It emulated: LCD controller, VG-Lite GPU, SPI-NAND, DMA, I2C, touchscreen and a minimal Bluetooth HCI controller.
Pokémon inspired many of us. The Missingno glitches and others and created a mythology and asked us to peek behind the curtain, and see the bare machine.
Now presenting: an over-the-air remote-code-execution across the Nintendo Wireless Adapter packet parser. On the right is Pokémon FireRed and on the left is a custom ROM working with the radio
Found this amazing repo today:
"This project documents the Nintendo Family Computer from Japan. The goal is to provide complete, verified, schematics and PCB for every version of the console and essential accessories."
https://t.co/mPOZTJkAQ4
#nintendo#retrogames#reverseng
Just built an MCP for Ghidra.
Now basically any LLM (Claude, Gemini, local...) can Reverse Engineer malware for you. With the right prompting, it automates a *ton* of tedious tasks.
One-shot markups of entire binaries with just a click.
Open source, on Github now.
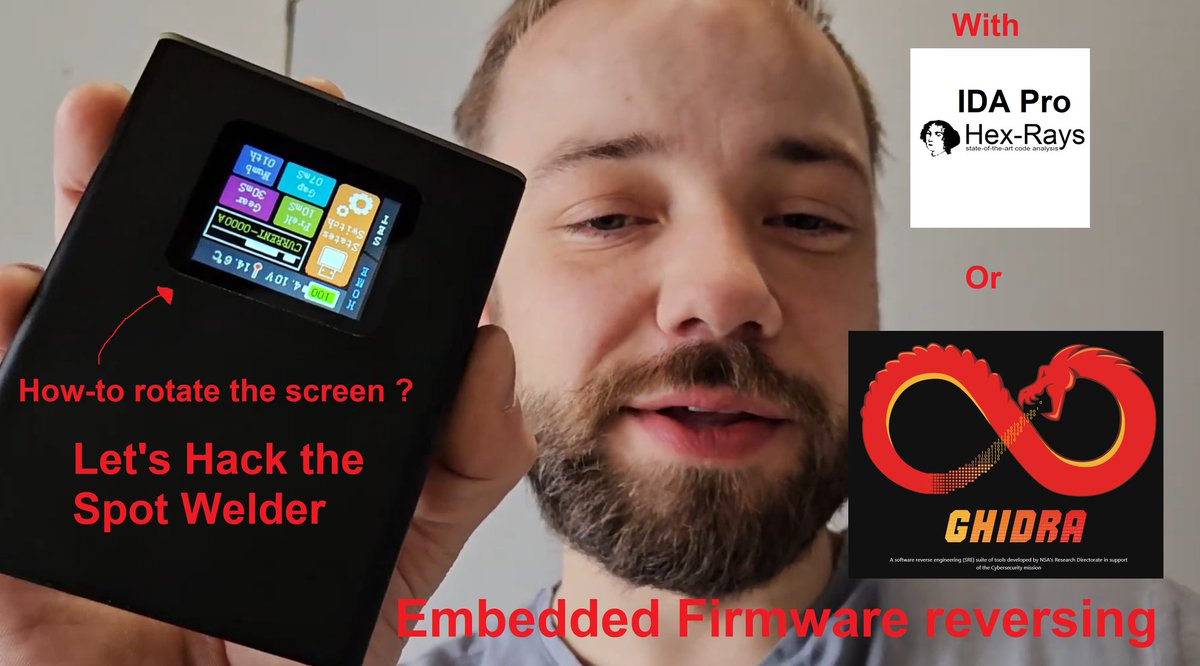
Would anyone be interested in a detailed how-to Reverse engineer with IDA video?
Well here it is🥳
A how-to Hack the 30€ Spot Welding firmware to get a rotated screen:
(Looong video)🎬 https://t.co/Y9TNw1o5Xc
A while back, @david_rysk asked me to dump the firmware of the Wersi SL-M2 51173 Slave Sound Generator, a plugin module for Wersi's DX10 synthesizer. @p4ula sent me three boards from Germany, and this thread will show the extraction process from the saw to the bits. 1/n
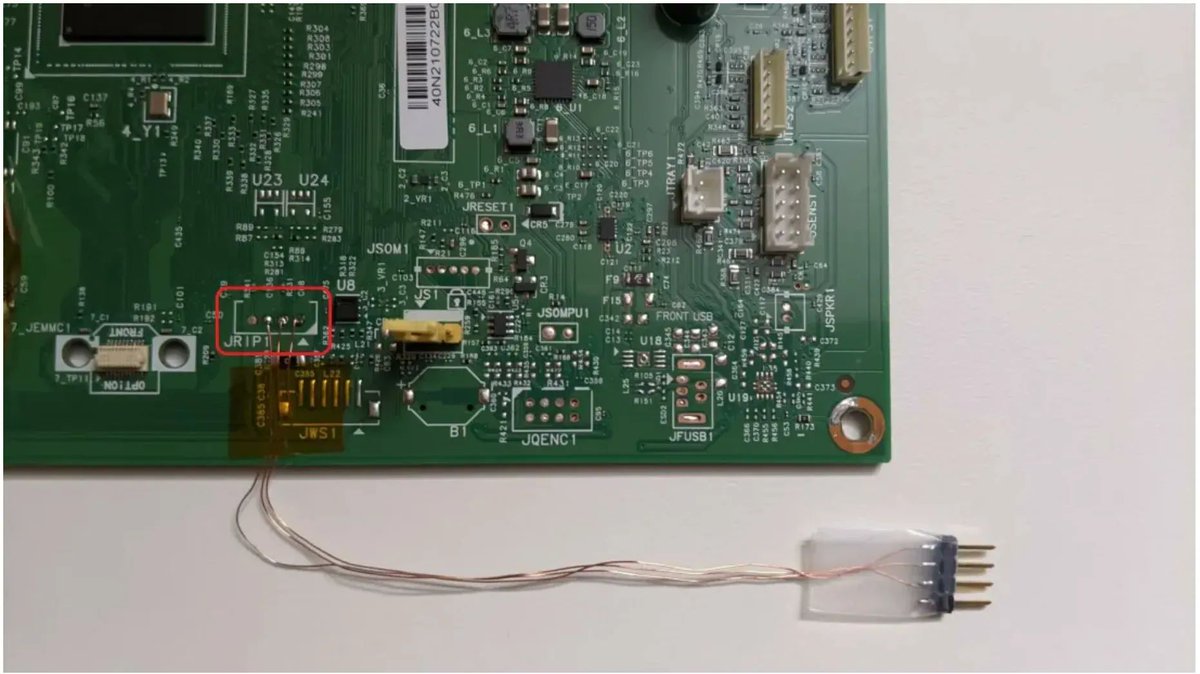
Two part series on extracting, analysing and exploiting the firmware of a Lexmark MC3224i printer
Credits @NCCGroupInfosec
Extracting the printer firmware: https://t.co/srZwnZvmno
Exploiting the printer https://t.co/YOkGYoJphB
#iot#embedded#infosec