🇰🇵
For a few months, I posed as a recruiter and engaged a DPRK persona known as Jason Kwon, who appeared to be operating as hightechrun shortly after news of m00n was shared. He later introduced himself as Roy Hensley. At the present, there is a possibility his current alias is on a shared upwork profile. Without knowing when that profile was put into play, it’s unconfirmed if that alias has entered any projects or been exposed.
Some of this will be familiar to researchers who follow DPRK activity as this wasn’t attribution built from scratch. It started with existing research from @zachxbt being publicly shared and some tracking by @intell_on_chain (@rugpullfinder). During our conversations and conveniently in the Beanstalk discord, he shared the 0xm00n GitHub account and later explained it as an “agency” account.
I used decoy documents, and CanaryTokens to collect what was possible about working environments. The summary covers the identity changes I could follow and connections collected during the small engagement.
I’m publishing this now because I want to get back into documenting, not leaving helpful info sitting in DMs, screenshots, and drafts. Additional context can help someone else connect an account, recognize a recycled persona, or pick up a thread you couldn’t follow further.
Link to medium article ⬇️ and thanks to all involved in this. @0xfigo has recently shared some work done behind the scenes with @north_scan involving tracking DPRK so I’m mentioning that as a resource available for those doing work on our beloved IT Workers.
https://t.co/34jL8Ra2oi
The initial version of the Prolog WinDbg extension is out there: https://t.co/4xMLzwpT1y The accompanying book will be published later today. Finally, I resumed work that I started more than 15 years ago... https://t.co/EYJktc2hxN
🚨 UNC6671 INFRASTRUCTURE UPDATE
Three hostnames under myaccountsetup[.]com:
⚖️ mccarthy
⚖️ blakes
🏗️ mastec
Legal-firm impersonation continues, with infrastructure branding alongside it.
VT: mccarthy 5/92; the other two 0/92.
Tracking continues. 👀
#UNC6671#ThreatIntel
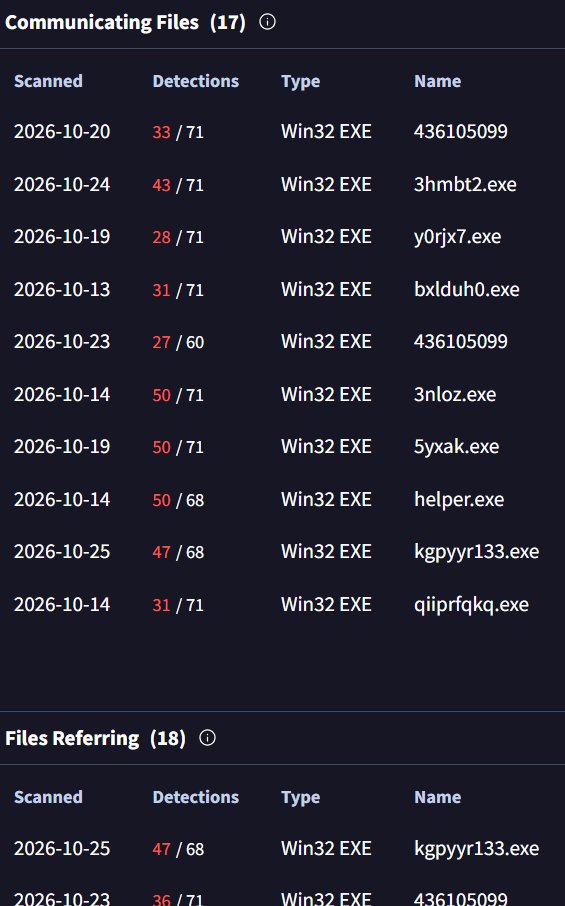
🔥A NEW PowerShell reverse shell in the PSSW100AVB repository
✅ 100% AV bypass (October 2026)
✅ Ready for red team operations (OSCP/OSAI/CRTP)
✅ AI-Evasive Comment to Bypass LLM Detection
https://t.co/GV76ojvgJN
Ransomware leak sites list 56 new victims today, up by about half over baseline, as Qilin posts 42, including https://t.co/Eef1gxNV5Q at 1.20 TB. https://t.co/2mfk2H7bO3
Check Point Research analysed Aokigahara, a new infostealer with a dedicated module targeting authentication and session data from Codex, Claude, Cursor, Copilot and Gemini. https://t.co/IbF3ZCq6lZ
Two related samples from Hungary @abuse_ch
'SAP_Concur_Extension.msix'
https://t.co/NE5YBgvv1A
Source URL: hxxps://cmp1.s3.filebase(.)io/SAP_Concur_Extension.msix
'SAP_Concur_Extension_3.12.msix'
https://t.co/3OKKNTgzRn
Source URL: hxxps://cmp2.s3.filebase(.)io/SAP_Concur_Extension_3.12.msix
...and one from Canada:
'SAP-Concur-Extension_8.1.18.0_x64_f1.msix'
https://t.co/oRXI8mR52v
Microsoft researchers analysed a compromised LiteLLM 1.107.0 release published to the PyPI & distributed through official container images. They explain the startup mechanisms, the credentials the payload could reach, & the evidence to investigate exposure https://t.co/m0hcR5QeqN
Hi @majorgeeks, I haven't been able to access your site for ~2 days.
I thought it might be from php updates, but none of the "is is up" websites say you're offline, and a traceroute is showing, well, this.
Is your web host having peering problems?
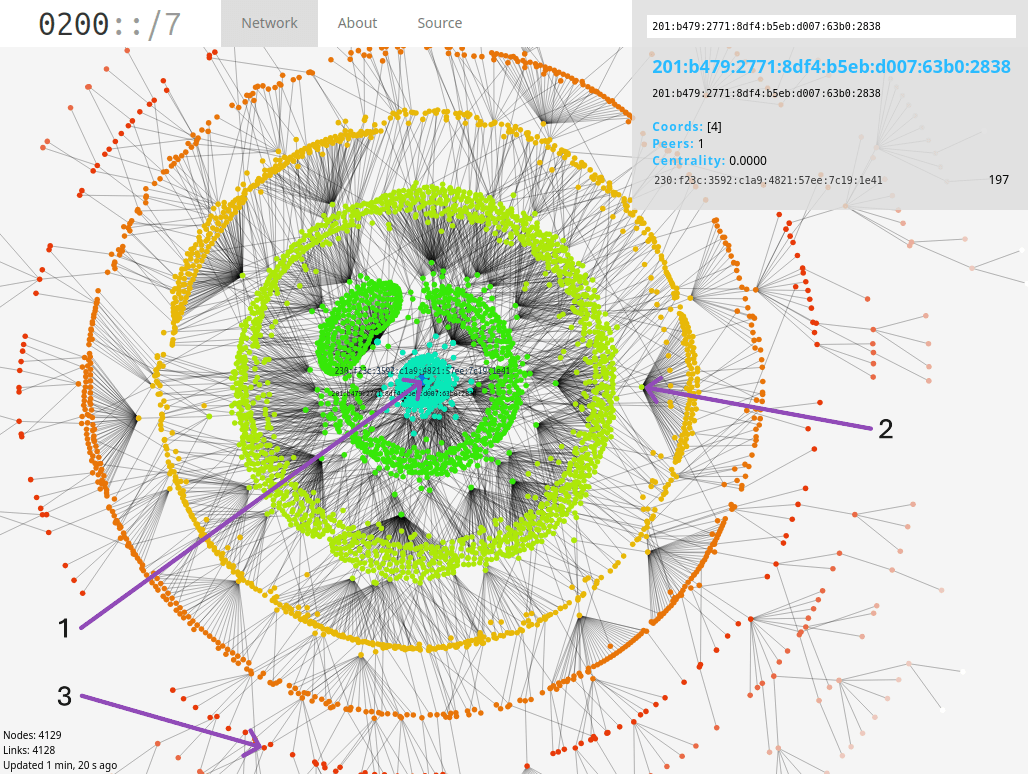
ESET researchers Anton Cherepanov & Peter Strýček uncover MythicRatatoskr – a previously unknown Go-based backdoor hiding its C&C server inside the Yggdrasil mesh network – which paved the way for a destructive attack against a Ukrainian grain firm. https://t.co/XnGLQj9Bd5
Related 'NARCOTICS NETWORK AND POLICE FACILITATION.doc' seen from Pakistan @abuse_ch
e6eca876f1e4423eadde8298c879774118f094d0b714a9dd202883b50ddc02dc
https://t.co/HQb5CueaDc
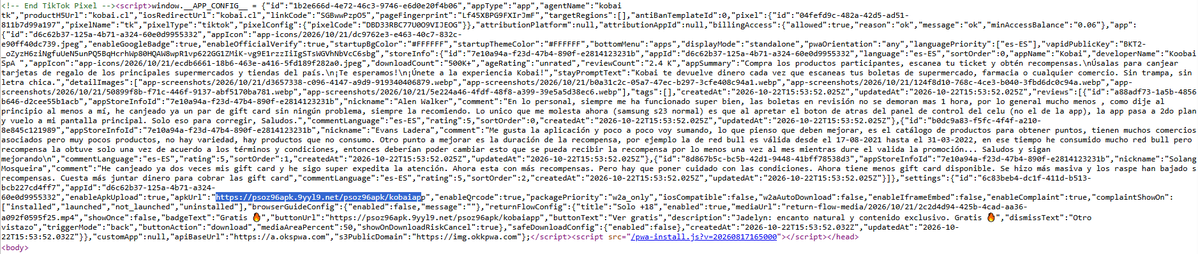
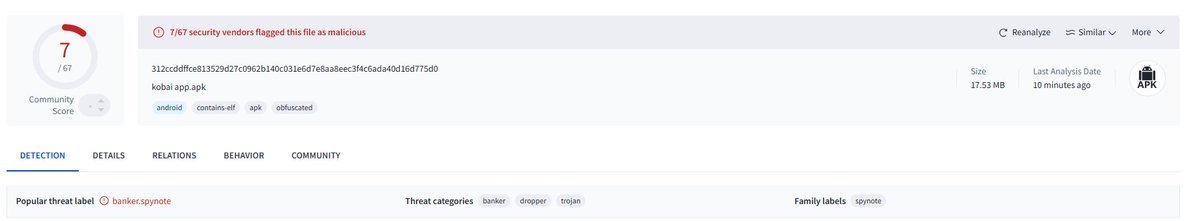
🚨 SpyNote Android RAT
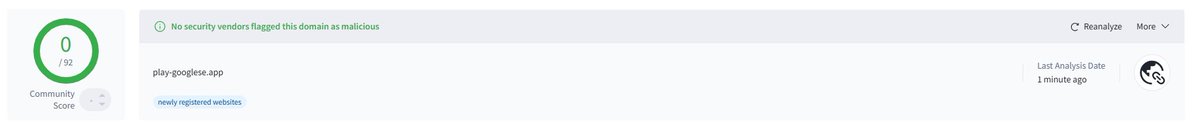
A fake Google Play Store page is distributing a suspicious APK identified as SpyNote.
IOCs:
Domain:
play-googlese[.]app
APK host:
psoz96apk[.]9yyl9[.]net
psoz96apk[.]9yyl9[.]net/psoz96apk/kobaiapp
Filename: kobai app.apk
312ccddffce813529d27c0962b140c031e6d7e8aa8eec3f4c6ada40d16d775d0
#SpyNote #AndroidMalware #ThreatIntel @500mk500@skocherhan
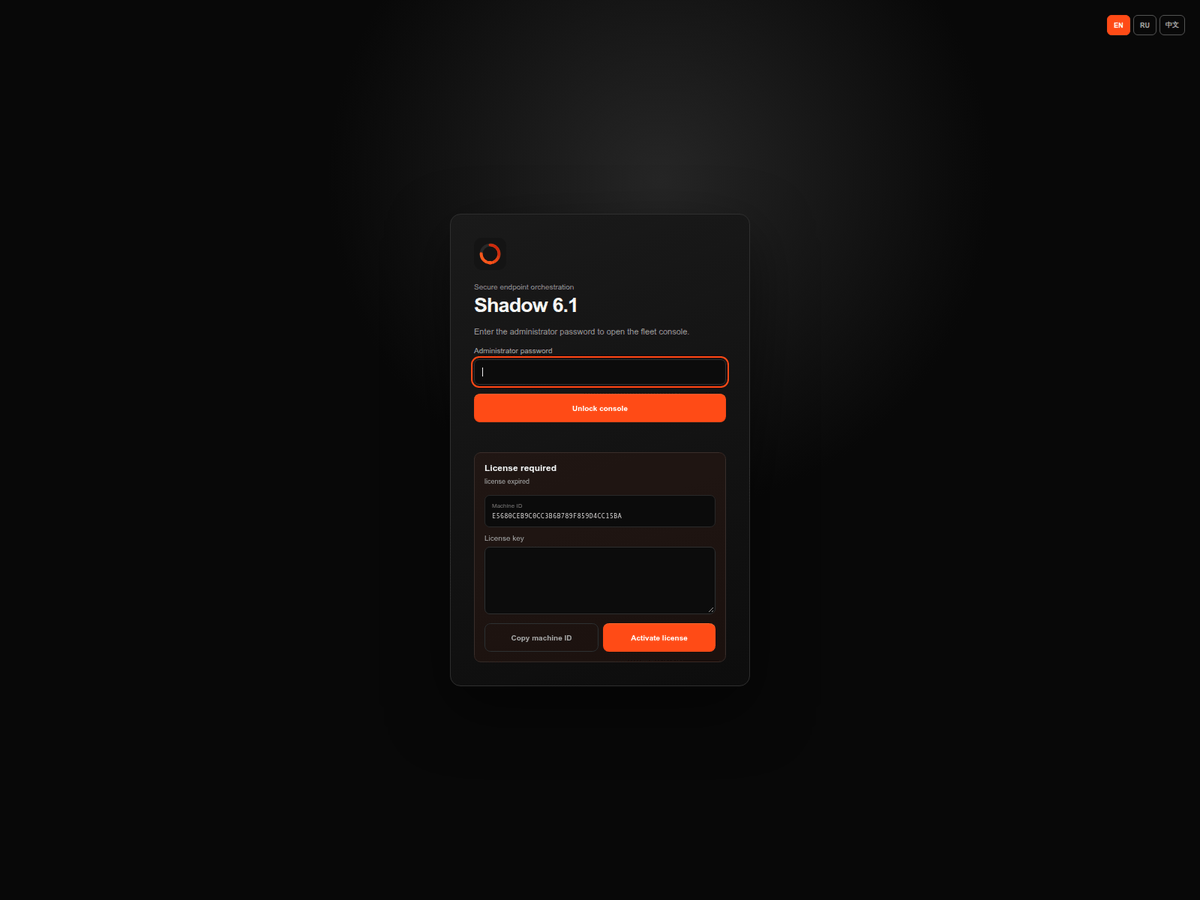
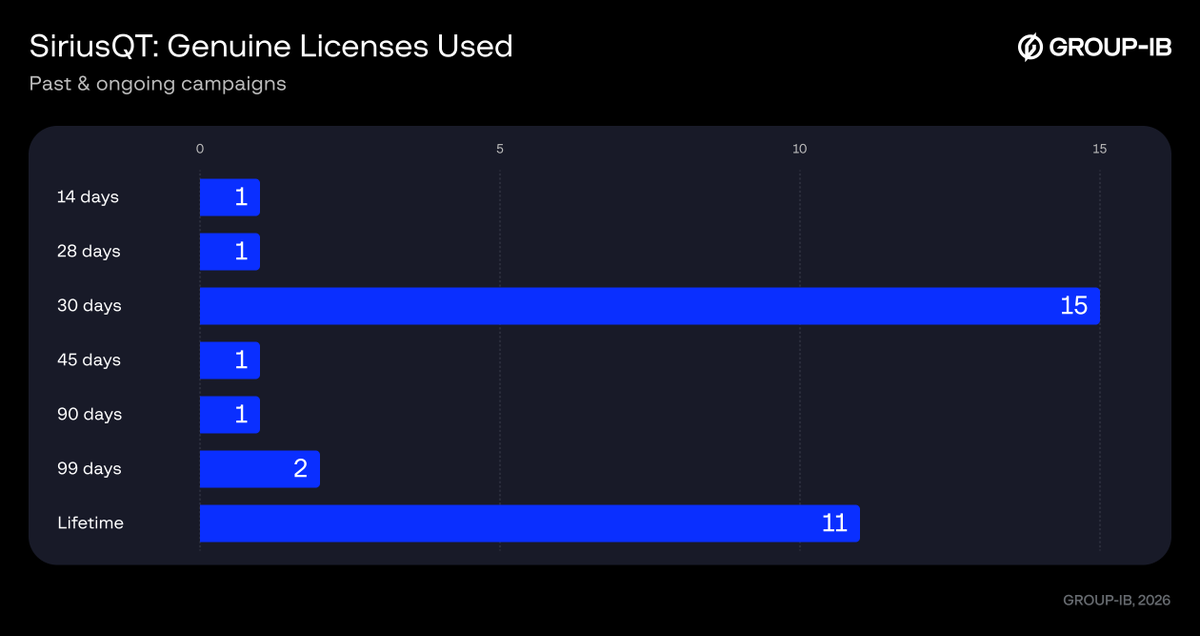
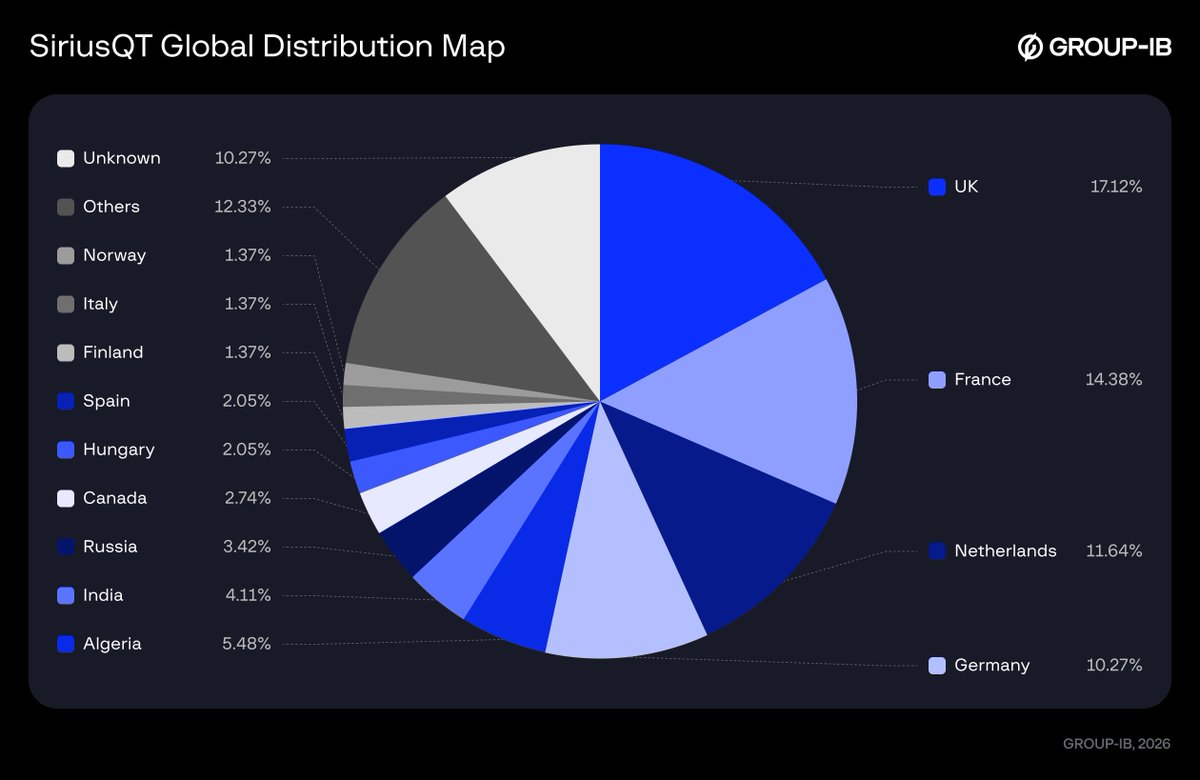
First observed in April 2026, #SiriusQT is more than just another Windows RAT. Our investigation uncovered more than 280 publicly available SiriusQT client samples linked to different campaigns and identified 146 unique licenses, 110 of which were leaked. At least 30 users purchased valid licenses, while 30-day, 90-day, lifetime, and customized license periods point to an active commercial ecosystem around the #malware. #ThreatIntelligence