The Penguins managed all of two shots on goal when they had a power play for 4:23 in the second period. Of course, they only had a 5 on 3 for 1:37 of that stretch.
Just awful.
Data brokers use your phone's ad ID to track and profile you. Disabling it does a lot for protecting your data privacy, and only takes 1 minute. Here’s how, for Android and iOS: https://t.co/VsPjMbtk6u
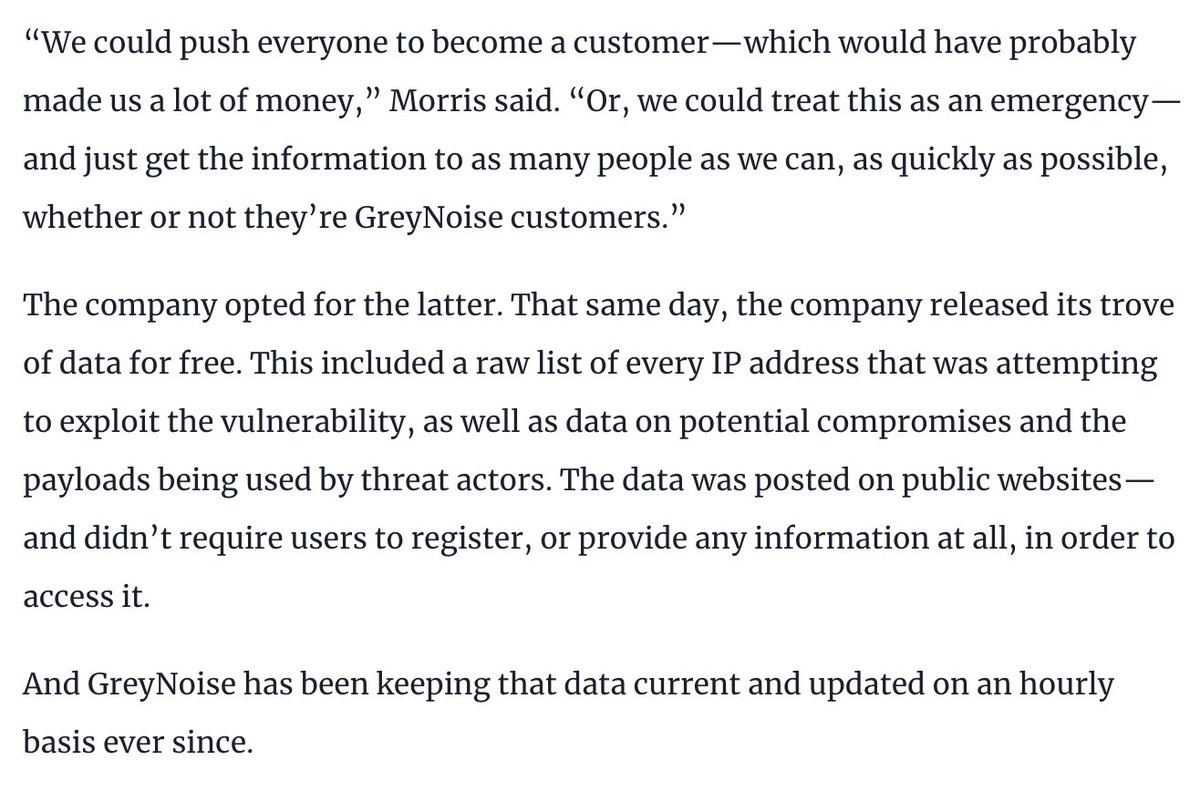
There's no way for me to amplify this article without seeming self-congratulatory. @KyleAlspach at @VentureBeat wrote a story about how we at @GreyNoiseIO made the decision to give everything re #log4j / #Log4Shell / CVE-2021-44228 away for free. We'd do it again in a heartbeat.
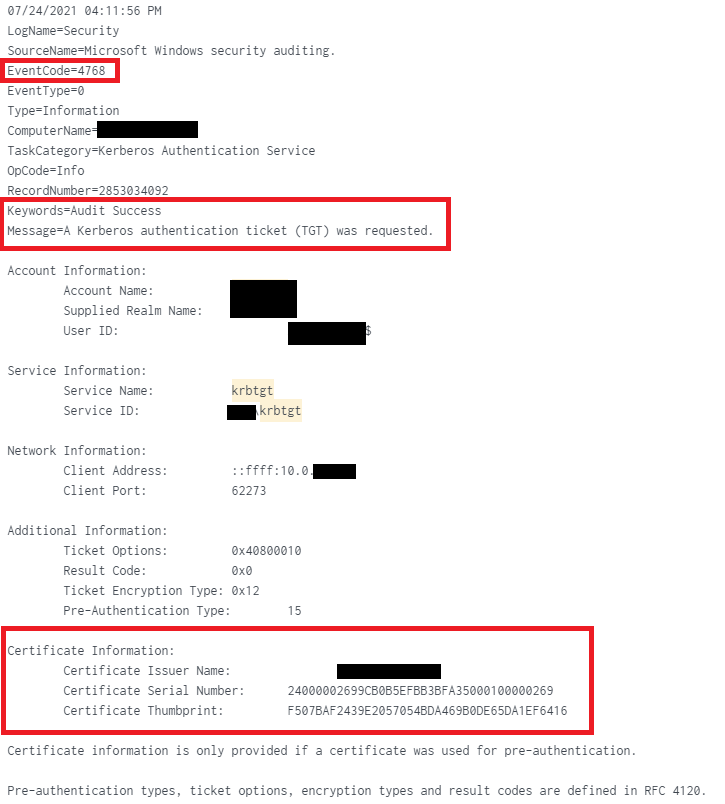
You can detect the #PetitPotam ADCS attacks by looking for Event ID 4768 (TGT) events where a certificate was used for authentication. Here's what it looks like in #Splunk (search index=windows EventCode=4768 Certificate_Issuer_Name=*)
Is this the worst Microsoft week ever? The vulnerability where the #PetitPotam vulnerability is chained with NTLM relay to #ADCS allows a user to get full control over a Windows domain.
New diary at https://t.co/HqlAU0F4Kt
On April 29, the #RansomwareTaskForce will launch our framework to combat #ransomware. This work addresses ransomware as both a financial crime and national security threat. Join us for this groundbreaking event. RSVP now: https://t.co/hr42WUpwry
If SolarWinds was used to hack Microsoft, and Microsoft was then used to hack Microsoft customers, this essentially means one supply chain was used to hack another supply chain. That's an impressive kill chain.