Interested in volunteering at Wild West Hackin' Fest @ Mile High 2027? There's still time! Final deadline is Saturday, Oct. 31! Submit your application here: https://t.co/keSrddB3jZ
NEW BHIS | Blog
Drowning in alerts that don’t matter? Learn how detection engineering turns raw logs and telemetry into detections your analysts can actually trust... and how to balance precision and recall so real threats don’t slip through.
Detection Engineering: Stop Drowning in Alerts and Start Catching Bad Guys
by: Wade Wells
Published: [10/22/2026]
Learn more: [https://t.co/aCnphji1DD
Half machine, half seasoned pentester, all bad news for attackers! Fusion PenTest pairs a purpose built AI with a senior BHIS tester, so you get the speed of automation and someone who knows the difference between a real problem and a false alarm.
https://t.co/1CyzkZHYRe
Thanks to everyone who stopped by the Active Countermeasures booth at Wild West Hackin' Fest! We loved chatting threat hunting with you, and we hope you’re rocking your new Threat Hunter shirt (and maybe still trying to land every ring in that water game).
Until next time!
You all should come to Right of Boom this February 2-5th.
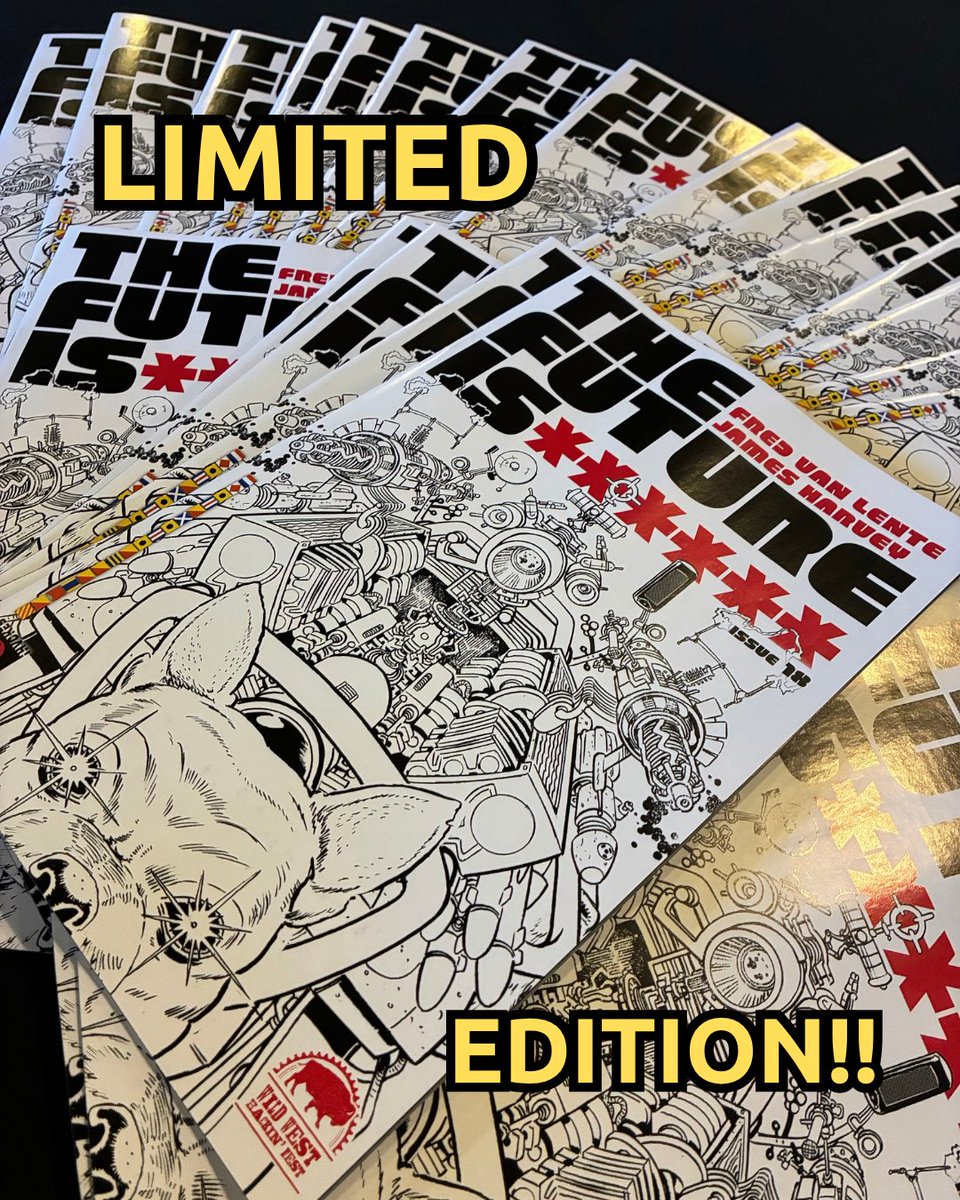
There is also a video teaser of the special edition of The Future Is ****** in the video as well.
New week, new things to learn! Kick off Monday with Talkin’ About [Infosec] News, get into containers and AI sandboxing with Jay Beale on Wednesday, then swing by Thursday’s BHIS Webcast to say hi. See you there!
https://t.co/FBXAC3Nknl
Hey everyone,
I was supposed to be at @WWHackinFest this week but I've been having some health issues the last week.
I sincerely apologize for not making it out. I'll be working with the con to maybe offer a webinar in the future or something.
@TCraf7 was featured in episode 100, but so much has happend with Trey since that episode. We sat down this week to discuss all he has done and what's new. His episode drops on October 27. Check out episode 100 in the comments.
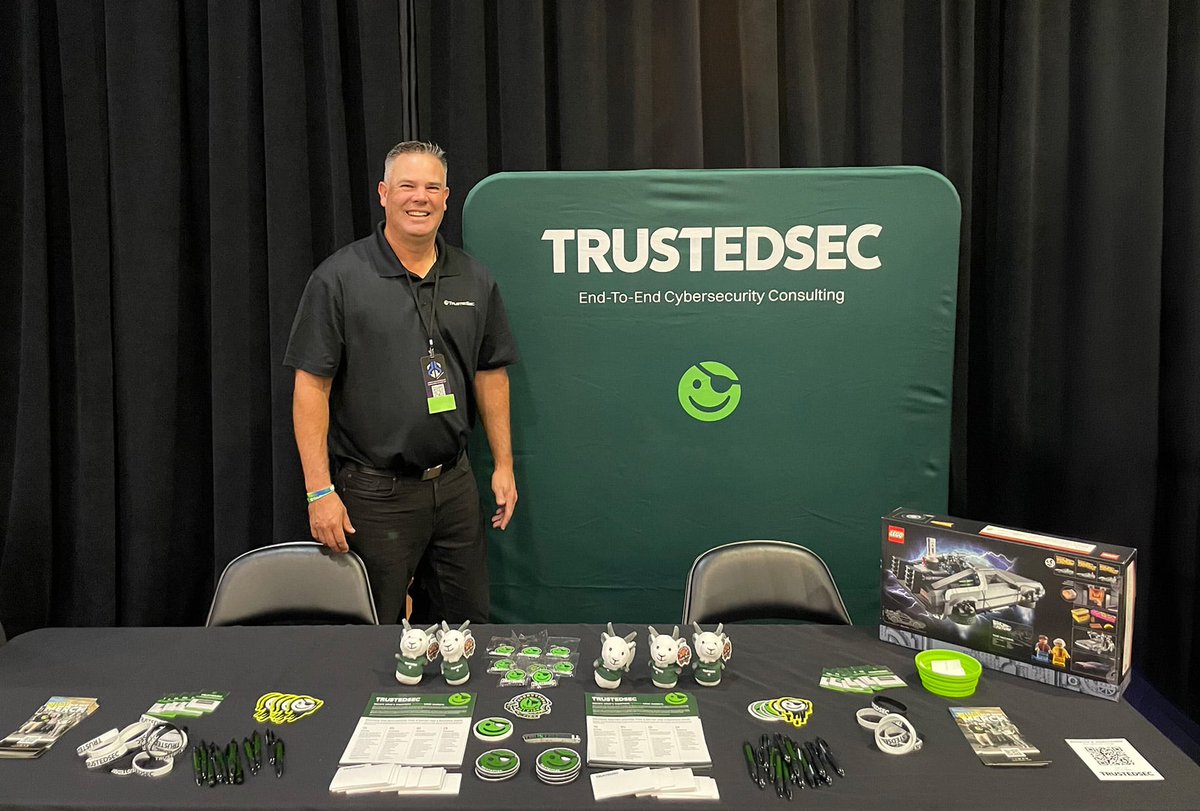
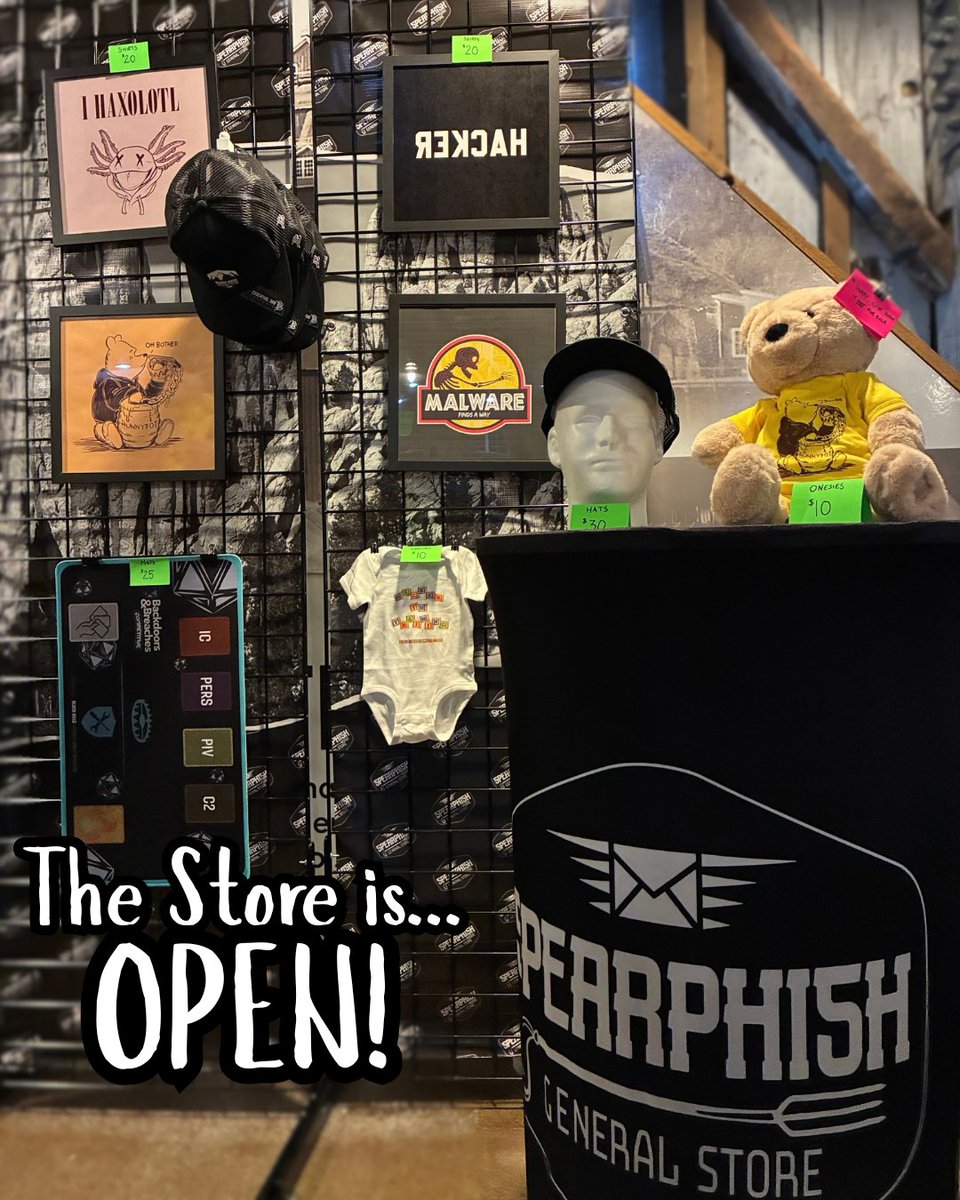
It's been a great day at @WWHackinFest and the fun is still going! Stop by our booth, say hi to this guy and the team—we'd love to connect. While you're there, grab some awesome swag 🤠
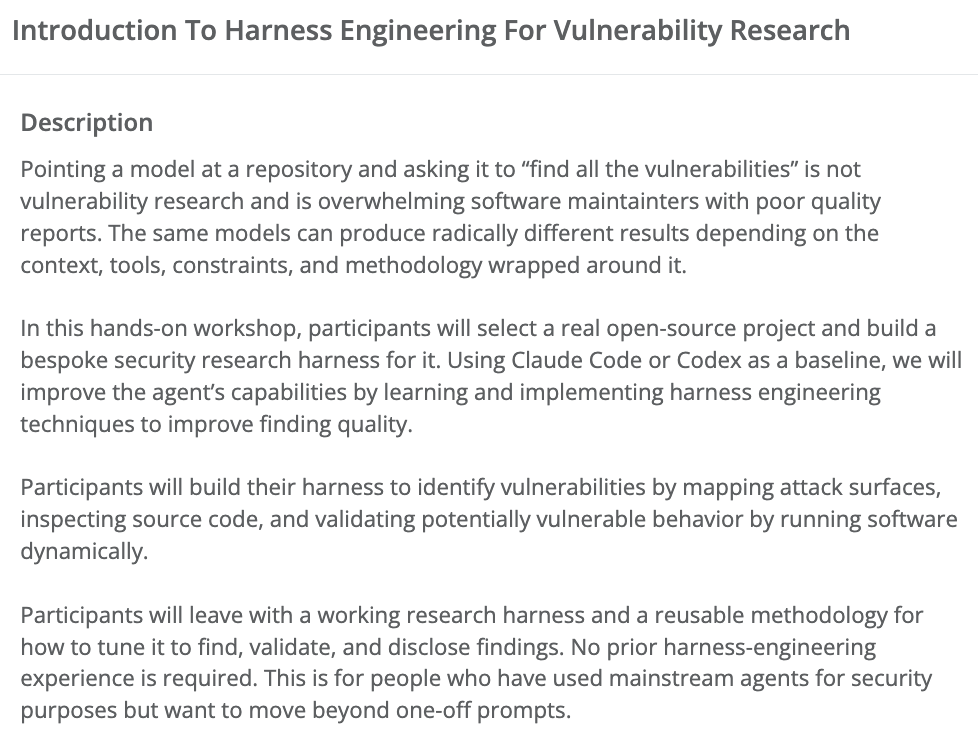
Exciting news. I'm teaming up with @_rybaz to teach a FREE training at @unpromptedconf
You'll learn harness engineering components that can augment your research to find more complex vulns. Each student will pick an open source target and build a bespoke security harness for it.
We are all back in boot camp. The security profession is changing, and the job right now is to work on your skills, to get into the room, and learn what other people are seeing. Figure out what you can take back to your organization and use immediately.
Joshua Wright @joswr1ght just published the first rebuild of the SANS incident response framework in 20 years. It is called Dynamic Incident Response, and it is free in every digital format.
The old process was basically Contain. Eradicate. Recover. That worked when incidents were more linear. Now, you contain the incident, bring the systems back, and then the attacker shows up again. Or you find new evidence that changes what you thought the incident was in the first place.
Joshua Wright is a @SANSInstitute Faculty Fellow and the author of SEC504. He built coWPAtty and KillerBee. He spent 18 months writing this book, with contributed chapters from Megan Roddie-Fonseca on cloud response, Dean Parsons on OT, and Ryan Chapman @rj_chap on ransomware. John Strand @strandjs wrote the foreword.
It is 720 pages and free under Creative Commons. Run it in a real incident. Tell Josh what it missed.
But we all know the field is moving too fast for one person or one organization to have all the answers.
You cannot base your knowledge on the news or whatever you happen to see on X.
As a CISO or manager, you need to understand what is coming at you. What do you need to worry about? What capabilities do you need to build? How do you argue for additional budget?
That takes actual knowledge and actual skills. Josh will be teaching the hands on version at the SANS Institute @SANSInstitute AI Cybersecurity Summit on November 2-3, including how to scope AI swarms when the intrusion keeps regenerating identities, accounts, and infrastructure while you are trying to remove the attacker.
Get the book: https://t.co/67txdiPNxh
Summit details: https://t.co/B7AJBXRfUy
Rare drop alert!!! A special edition cover of The Future Is, Issue 18, is in the wild, and it's only showing up at our gold sponsor booths. Track down LimaCharlie, Concentric AI, and Intigriti to claim your free copy before someone else does!
#WWHFDeadwood2026
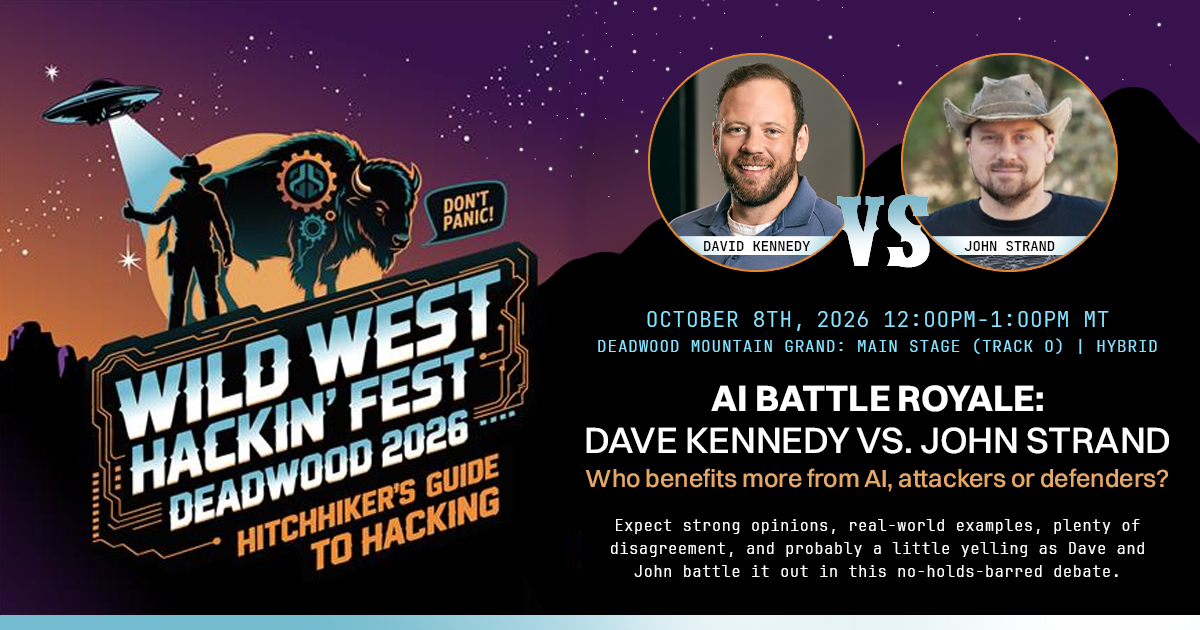
Who benefits more from AI, attacker or defenders? Don't miss the debate on Oct 8 with @HackingDave as he goes toe-to-toe with @strandjs from @BHinfoSecurity at @WWHackinFest! Check it out at noon MT if you'll be there! #WWHF https://t.co/SLRhjbaGPX