Specializing in pen testing, red teaming, and Active SOC. We share our knowledge through blogs, webcasts, open-source tools, and Backdoors & Breaches game.
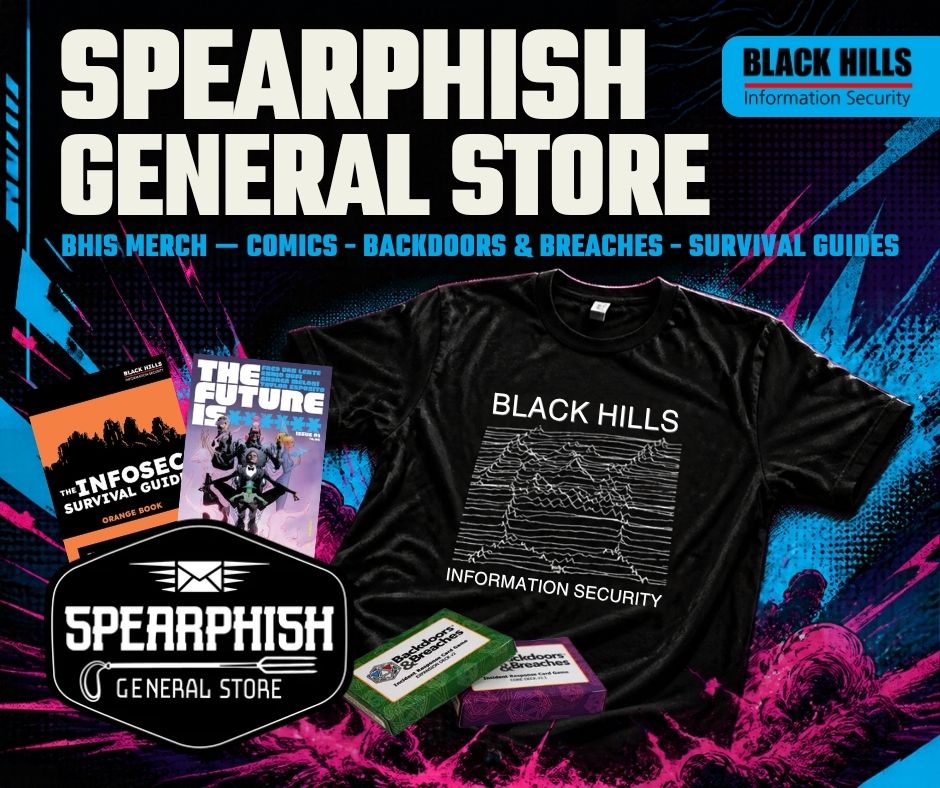
Your infosec survival guide is ready, in whichever format you like. 📘
Want a physical copy for your desk? Grab one at the Spearphish General Store. Prefer digital? Download it for free.
Because surviving in infosec is easier with a guide 🛒 https://t.co/4LWRCFEn0D
Level up your incident response game. 🃏🛡️
Backdoors & Breaches Core decks, Competitive decks, and playmats are all available now at the Spearphish General Store.
🃏 Core deck: the classic IR tabletop experience
⚔️ Competitive deck: attackers vs. defenders, head to head
🎲 Playmat: because every breach deserves a proper battlefield
Grab yours 🛒 https://t.co/aTVERes41s
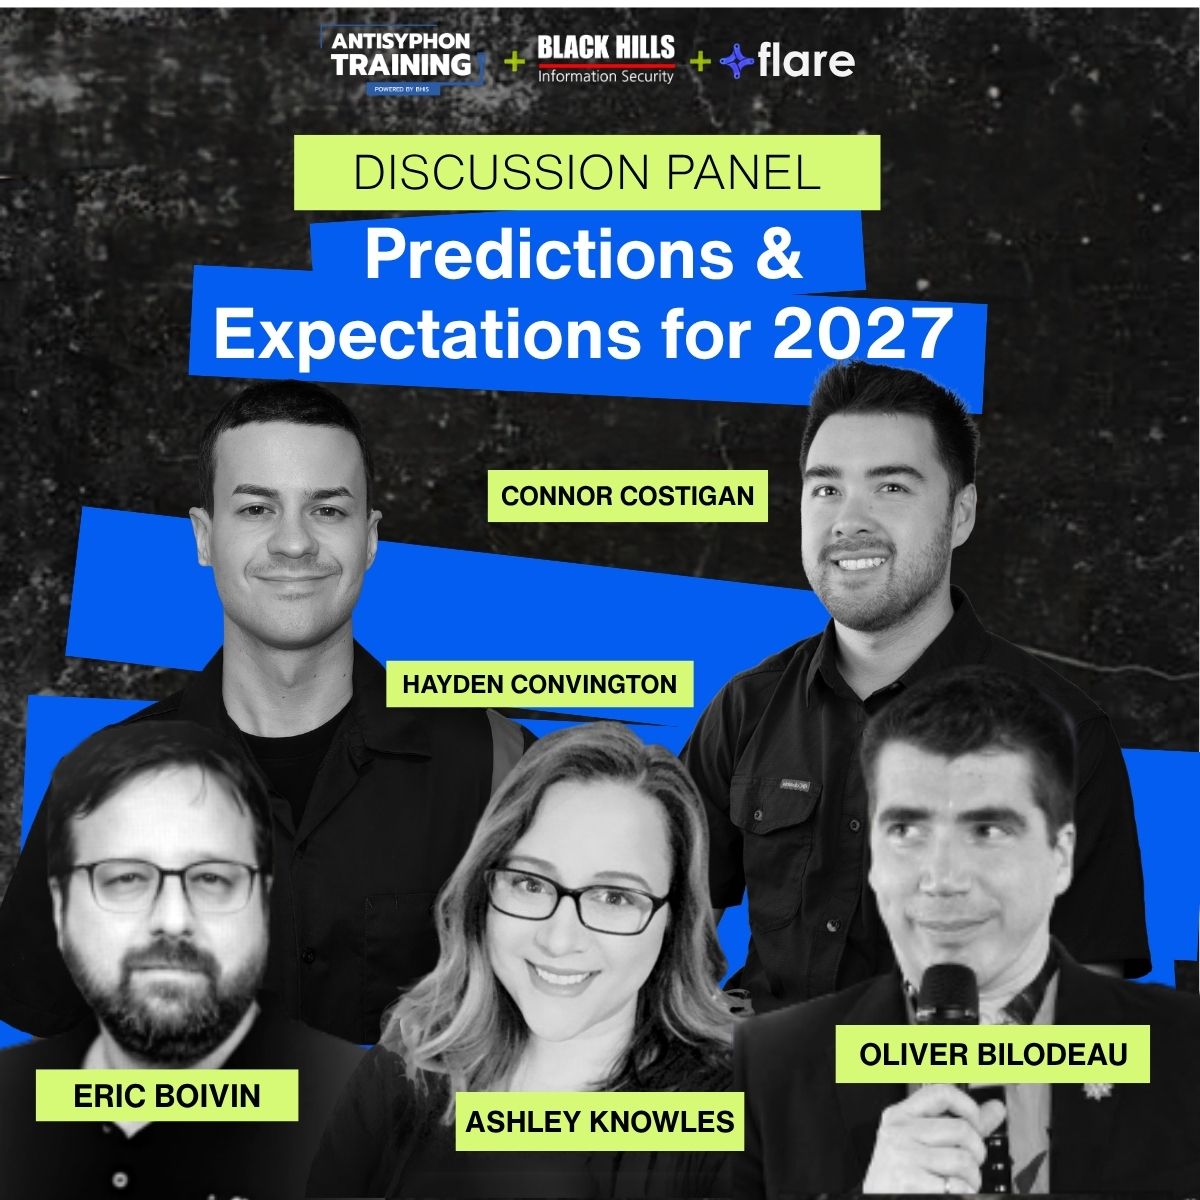
Big Conversations. Real Perspective. Join these experts during What in the Actual Cyber?! 2026 in Review as they cover an AI Review, CISO/Business Leaders Review, and Predictions & Expectations for 2027.
🖱️https://t.co/8fEPTw6MSa
"That’s what makes me uncomfortable. Attackers don’t need to get through the most heavily scrutinized software in your environment. They need a way in. And I think these less supported technologies are going to give them one." - John Strand, Owner, Black Hills Information Security
https://t.co/FbuTe72V4w
Reminder for our lab regulars: your hours don’t stack, so use the 2 you’ve got! ⏰ Spin up your VM and dig into the labs before Friday rolls around again.
https://t.co/nEFDUk1BRP
NEW BHIS | Blog
Learn how to hunt for threats in packet data, network flows, and odd internal traffic, plus Betty’s favorite tools and methods.
Threat Hunting on the Network: An Active Search for Risks on the Wire
by: Betty DuBois
Published: 11/18/2026
Learn more: https://t.co/MNh3Y4YTFc
An employee's inbox is flooded with subscription emails. Seven minutes later, someone claiming to be IT reaches out through Microsoft Teams to help.
On December 2, we're joining Spur Intelligence to examine a real-world investigation involving mail bombing, helpdesk impersonation, and anonymized infrastructure.
Hayden Covington, Associate Director of Security Operations at BHIS, will walk through how investigators connected the evidence and how Spur IP intelligence helped identify suspicious infrastructure that traditional reputation checks missed.
Join us for the investigation and practical lessons for triage and containment.
December 2 | 12 PM ET
Register: https://t.co/H5c9wyHs9r
Where will we be Feb. 17-19, 2027? Right HERE. 👇
Wild West Hackin’ Fest is taking over the Sheraton Denver Downtown Hotel, and there’s a seat with your name on it. Come hack with us.
🖱️https://t.co/hUXBoHfFzJ
Certificate authority DigiCert has disclosed a data breach involving an internal business system that was inadvertently exposed to the internet for more than 16 months following a February 2025 network migration.
John Strand weighed in - “First, there was a breach, but nothing sensitive was affected. Then, there was a breach, but we took care of it. Now we’re hearing that the exposure lasted more than 16 months."
💻https://t.co/iHUHwVbX5B
It's been a crazy year! Now more than ever, we need to capitalize on incident-response "lessons learned" before suffering cybersecurity failures!
Join Patterson Cake in this webcast on Thursday, November 19 at 11 AM (MST) as he looks back at 2026 and outline the top 10, low-effort, high-impact technical “lessons learned” that every business should review and address BEFORE a cybersecurity incident.
https://t.co/U3PSiqDABO
Not sure where to start when it comes to working with a cybersecurity team? At Black Hills Information Security, we make the process simple, approachable, and tailored to your needs.
🤝Get Started Today - https://t.co/SShXZF64HG
An attacker ran as SYSTEM on a user's laptop for twelve minutes through ScreenConnect's hidden Backstage mode, and the user never noticed. The only command we recovered was one leftover line in a PSReadLine history file.
➡️https://t.co/iiFIZeRsam
Poll: what defined security in 2026? ⬇️ Vote in the Comments.
We'll be unpacking the year Dec 9 at What in the Actual Cyber?! 2026 in Review.
https://t.co/8fEPTw6MSa
Just when we thought we had this whole cybersecurity thing figured out, 2026 said, "Hold my energy drink."
What in the Actual Cyber?! 2026 in Review is your chance to cut through the hype with four free hours of risks, rants, and rabbit trails from the Black Hills Information Security crew.
Register ➡️ https://t.co/2mhOGMCALh
One Stolen ConnectWise Credential Reached Nearly 1,000 Microsoft 365 Tenants
“What else could the attackers access? Compromised application credentials can let attackers into customer tenants and give them access to data through Microsoft Graph,” says John Strand, Owner, Black Hills Information Security.
Read the full article ➡️https://t.co/I2B97WD1Py
Have you heard of Free Lab Fridays?
Join Tim Doerges, Lead Developer for Black Hills Information Security, as he takes you through all of the features available TO YOU, FOR FREE on our Free Lab Fridays platform!
👀 Watch the latest: https://t.co/i9KtBSjhXo
NEW BHIS | Blog
One failed login is a typo. Ten in two minutes is someone guessing your passwords. Want to learn how SOC analysts spot the one pattern that screams “intruder” in millions of log entries?
Log Analysis Field Guide: Tips for Spotting Patterns and Red Flags
by: TJ Johnson
Published: 11/11/2026
Learn more: https://t.co/ilDvi71wXy
Want to learn why core security skills matter more than ever in the age of AI... and how they turn AI into a force multiplier?
Core Skills in the Age of AI:
by: John Strand
Published: 11/05/2026
Learn more: https://t.co/fa0XzS03LN
Did you know BHIS isn’t just pentesting? 🤯
From Active SOC and Incident Response to AI security assessments and GRC, we’ve got you covered from first scan to final report!
https://t.co/fAesDMSREs