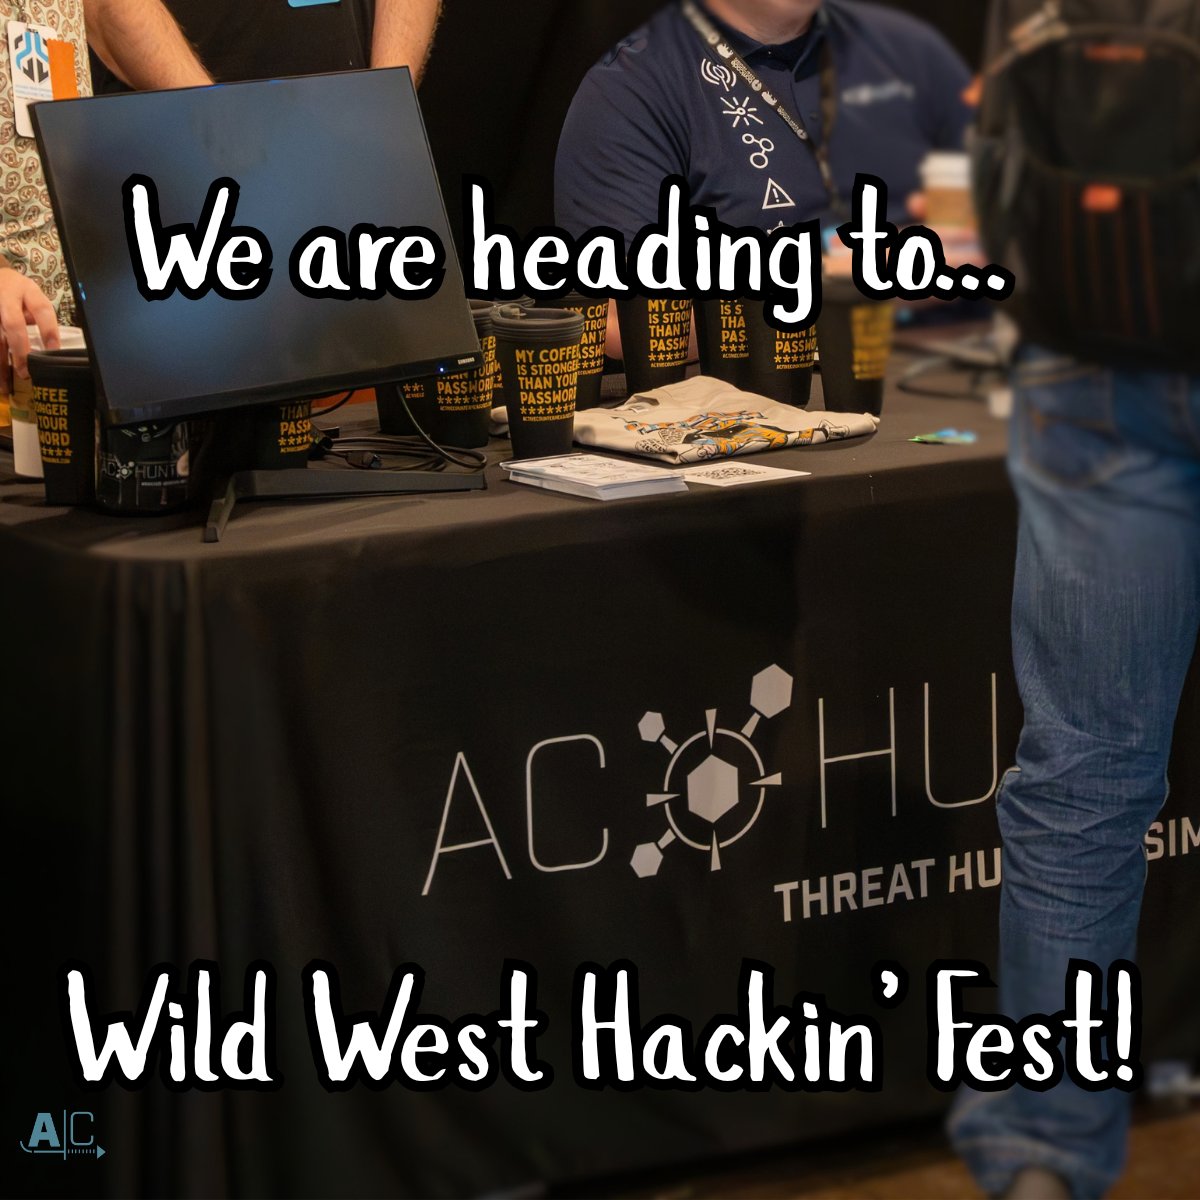
Thanks to everyone who stopped by the Active Countermeasures booth at Wild West Hackin' Fest! We loved chatting threat hunting with you, and we hope you’re rocking your new Threat Hunter shirt (and maybe still trying to land every ring in that water game).
Until next time!
Thanks to our sponsor, Active Counter Measures, for supporting the Threat Hunting Summit and helping defenders improve. Join ACM's lunch hour learning session: https://t.co/7fWcUUklMr
Friendly reminder: The Threat Hunting Summit is free, speakers are ready, and the agenda is packed. Join us June 17 for expert talks and practical insights. Register here: https://t.co/7fWcUUklMr
Detection often relies on consistency. ZetaSwitch relies on the opposite. By pivoting between DNS and HTTP, this C2 creates a moving target for defenders. We simulated the traffic with @faanross to show how to hunt this hybrid threat.
Read more: https://t.co/9IZkKAKmtw
Defenders watch one channel. Numinon C2 uses two. By splitting traffic between HTTP and DNS, it hides in plain sight. We simulated and analyzed the traffic with @faanross to see how it bypasses detection.
Read: https://t.co/y9StAwbx3j
@saidesheikh@BHinfoSecurity Hey there, yes our webcasts are always recorded, you can find them at our YouTube channel, here's the link to the latest one: https://t.co/b91KHOuDU1
Is your DNS traffic hiding active C2? Join @faanross to learn how attackers abuse TXT records to bypass common tunneling detections.
Reminder: Chat is in the BHIS Discord #live-chat for HACK IT credit.
Date: Feb 20
Time: 12:00 PM EST
Register: https://t.co/uDaJ2Wu4RM
A predictable heartbeat is easy to find. Merlin C2 uses data jitter to make its pulse irregular and invisible. @faanross simulated and analyzed the traffic to show why it hides so effectively.
Read: https://t.co/jaDn4UA8R5
IP blocks fail when an attacker has trillions of identities. IPv6 address aliasing turns one host into a ghost. We simulated and analyzed this traffic with @faanross to help you hunt the technique. https://t.co/xU2peTKppv
The ocean is vast. Without a compass, you aren't sailing; you’re drifting.
Network security is the same. Even with the best ship, if you lack a map, you're lost at sea.
Turn MITRE ATT&CK from a bingo card into your roadmap.
New from @faanross: https://t.co/baznxY6GVE
An IcedID loader is often just an open door for ALPHV ransomware. @faanross simulated the attack and analyzed the traffic to pinpoint the pivot. Recognition is the key to defense.
Read here: https://t.co/XkG2ccHk9h
The signal evolved, but the hunt remains. @faanross simulated and analyzed complex C2 beaconing to reveal the unusual ways traffic hides in plain sight. This insight is what turns the tide for defenders.
Read Part 2: https://t.co/BJHM6FmXeq
The adversary hides in the encryption you provide. When DNS goes dark, defenders go blind. @faanross simulated and analyzed the traffic to find the signal.
https://t.co/m4CzXjLX09
Malware doesn't scream; it whispers in a rhythm. @faanross simulated and analyzed C2 traffic to decode these hidden heartbeats. Recognizing the pattern is how you find the breach.
Read here: https://t.co/ER2gvieloH
A clock sync seems harmless until it becomes a backdoor. @faanross explores how Gomesa hides C2 in NTP traffic. We simulated and analyzed this traffic to reveal what defenders often miss.
https://t.co/feqDW6jUtH
An algorithm finds the hash, but it can't find the why. When attackers pivot, they aren't just changing code they're testing your intuition. Automation has a ceiling; human hunting doesn't. Learn why context is the key to the game: https://t.co/SVlGXsOdl5
What happens when DFIR tools are used for harm? Join Episode 6 of Command & Convo this Friday to see how threat actors misuse Velociraptor for C2.
As part of our hunt-it program, join the new chat location here: https://t.co/S3wqIxt3pp
Register here: https://t.co/uQvsrb4OQP
We simulated the traffic to see what your logs won't show. Microsoft Dev Tunnels allow RDP to blend into legitimate streams, bypassing standard blocks. See @faanross's analysis on how to detect this hidden activity:
https://t.co/ybbQ8RDZGK
What happens when legitimate DFIR tools are used for harm? Join Episode 6 of Command & Convo to see how threat actors misuse Velociraptor for C2 and how to hunt for these pivots.
Date: Jan 9 Time: 1:00 PM EST Register: https://t.co/uQvsrb4OQP