CVE-2026-107181 POC | Telegram Desktop Account Takeover
1 Click account takeover by stealing session files.
PoC & technical breakdown: https://t.co/MJIaXku1Cp
Shoutout to @BeakSec for the excellent research and detailed write-up!
#CyberSecurity#CVE#ExploitDev#InfoSec
Android Security Bulletins have been twisted into a way to mislead the public about security. Patches are only listed in the bulletins 2-6 months after they're disclosed to each Android OEM and allowed to be shipped. Patches listed in the September 2026 bulletin were available to ship for months.
Android Security Bulletins are divided into two sections. The first section contains High and Critical severity Android Open Source Project (AOSP) patches backported to older releases. For years already, Low and Moderate severity AOSP patches have required updating to the latest major releases.
The first section is the main portion of the patches and gets provided 2-6 months in advance as security preview patches. The security preview patches are allowed to be shipped right away, which is sensible. The horrific part is delaying disclosure of the vulnerabilities and patches for months.
The security preview patches aren't only for Android projects but rather also include patches to external projects. Some of these external patches are already publicly disclosed while others are not. As one example, there have been non-publicly-disclosed security preview patches for wpa_supplicant.
GrapheneOS provides security preview releases providing early access to all of the security preview patches. It's the only OS quickly shipping all of these patches. A subset of these patches are shipped early by the stock OS on Pixels and Samsung flagships but far from all and it comes weeks later.
In 2026, Google has been completely overwhelmed by the volume of vulnerabilities being discovered by AI models both internally and externally. They recently announced to OEMs that the full set of High and Critical severity patches will only be available through the latest yearly and QPR2 releases.
Their announcement explains the massive number of vulnerabilities discovered by AI models internally will only be patched in the latest major releases. A subset deemed to pose an imminent risk to users will be backported to the most recent releases but not to older releases with security support.
Each Android Security Bulletin also has a 2nd section with listing an extraordinarily small subset of the vulnerabilities patched in the upstream Linux kernel along with a small subset of vulnerabilities patched in drivers/firmware shared by many devices. This is deliberate to keep the bar very low.
Google wants Android users to feel safe due to believing they have the latest privacy and security patches. Therefore, they delay patches being listed in the bulletins for months and don't list a substantial portion of Linux, driver and firmware patches. It's a very low bar so devices can keep up.
Since it's already public from https://t.co/3EX4ZqEkSc -
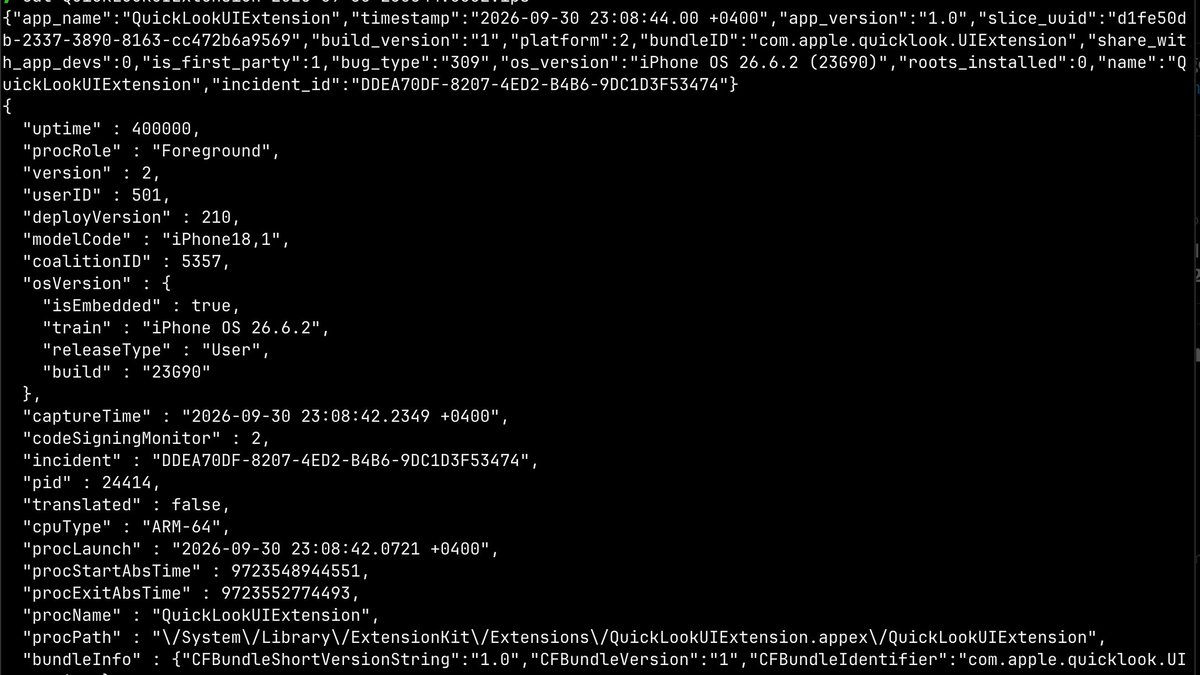
WhatsApp → QuickLook ext → PDFKit → PaperKit → PDFKit → CoreGraphics (aa_cache_render)
Reachable from a crafted PDF/font via the ImageIO/thumbnail path (QuickLook/sips).
My clanker and I did some analysis on the iOS 26.7.1 CoreGraphics patch. As the diff from @blacktop indicates (https://t.co/8ilewkqpRW), some small changes. It likely has to do with glyphs and I got a small PoC crashing Quick Look delivered by a PDF. 1/2
⚡ A VoLTE exploit chain can give attackers full Android kernel access.
The Unisoc chain starts with modem RCE, then lets modem code modify Android kernel memory. It requires attacker-controlled 4G infrastructure and the victim to answer the video call.
No patch is available.
Details: https://t.co/oH0NKZGy3M
Trying to root an Android device without needing the stock firmware by dumping the boot.img and injecting it via Magisk/APatch
#BugBounty#Mobilesecurity#Cybersecurity
https://t.co/C36W3Gu9eZ
reported a chrome fullchain (web -> shell) on pixel 10 to google. got a 9.6 cve (cve-2026-87464) and a fix in chrome.
now they bend the rules and refuse to pay the fullchain bonus bc one of the vulns in the chain was an unpatched nday. total payout: $2.5k. despite cve + shell :|
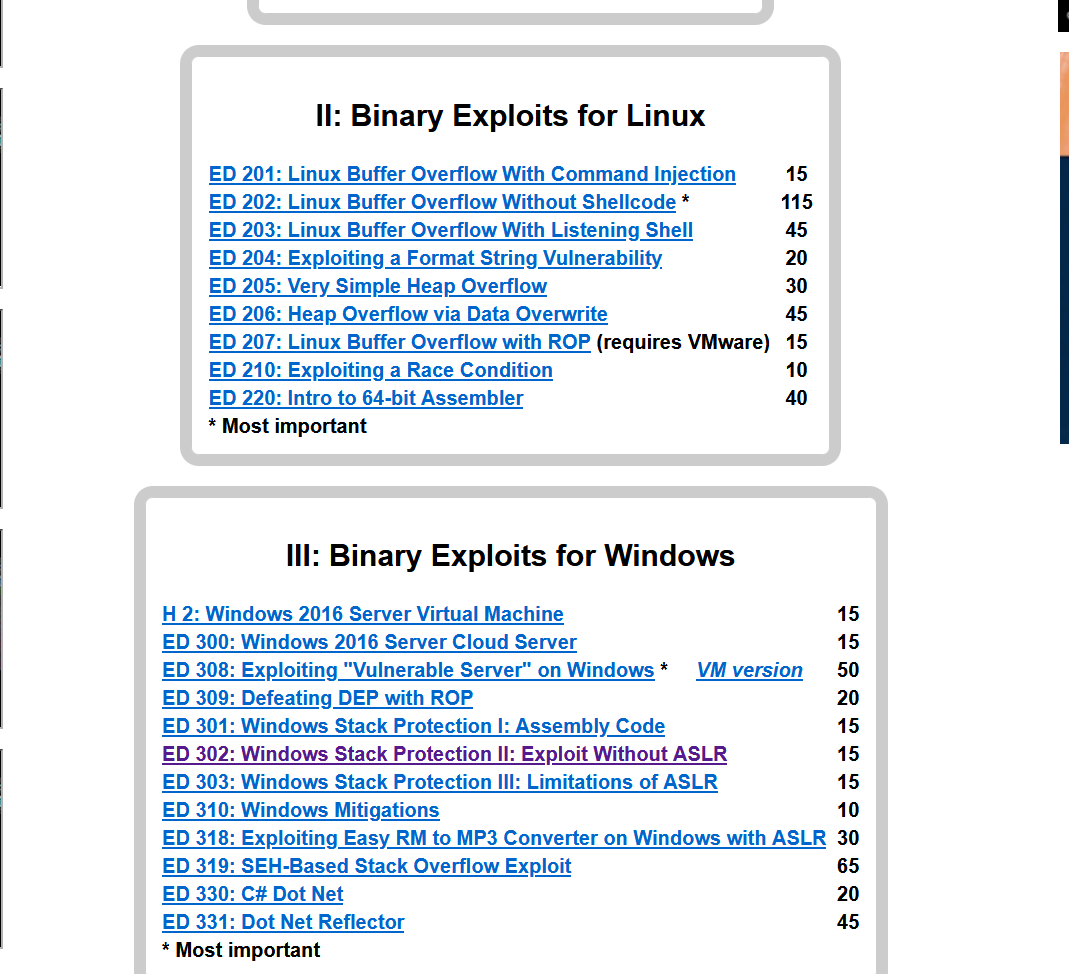
If you're learning exploit development, bookmark this.
A FREE collection of hands-on exploit development tutorials covering:
Linux + Windows buffer overflows
ROP + defeating DEP
ASLR + Windows mitigations
Heap overflows
Format string vulnerabilities
Race conditions
SEH exploitation
x64 assembly
ARM shellcode
iPhone exploitation
Created by @sambowne with @djhardb, @KaitlynGuru and @infosecirvin.
Start here: https://t.co/dpFck4hnwz
Excellent free resource for anyone getting into exploit development, binary exploitation and reverse engineering.
#ExploitDevelopment #ReverseEngineering #Infosec
dangling COM registration. SYSTEM DLL load.
CVE-2026-66804. incomplete fix for Dark Elevator.
CrossDevice CLSID points at a DLL under ProgramData that does not exist.
any user plants it. Forshaw loads it via custom COM marshaling.
Shell Create Object Task starts dllhost as SYSTEM. custom marshal still on.
ICreateObject takes the fake IMarshal. CLSID unmarshals. DLL runs.
credit: James Forshaw / @ProjectZero
https://t.co/WbqOSog2fM
#ExploitDev #WindowsSecurity #InfoSec
Tired of banking apps crying about Developer Options or USB Debugging? 🙄
Geto fixes that 🔥
Hide Dev Options and Debugging modes on a per-app basis—keep your banking apps happy without breaking your dev setup.
👇 Link in reply!
#Android#AndroidDev#Tech#OpenSource#Android #OpenSource #AndroidDev #Tech #Root
Drones have become a powerful force in both modern warfare and cyber-physical operations.
In this advanced #BHEU Training, explore offensive and defensive drone tactics, real-world attack scenarios, and the evolving technologies reshaping the unmanned systems landscape.
Gain hands-on knowledge of one of today's fastest-moving security domains.
🔗 Learn more and register: https://t.co/nfAvWXVbLJ
🔴 Android'in MatroskaExtractor bileşenindeki High seviyeli CVE-2026-28609 out-of-bounds write açığı için çalışan PoC yayınlandı.
Özel hazırlanmış WebM dosyası üzerinden tetiklenebilen açık, Android 14/15/16/16 QPR2 sürümlerini etkiliyor.
PoC, gerçek Android cihaz üzerinde AddressSanitizer ile heap-buffer-overflow tetiklendiğini gösteriyor. PoC şu aşamada RCE sağlamıyor; exploit zincirinin weaponize edildiğini göstermiyor.
https://t.co/fcs9BPQQxU