Sandboxing is now more important than ever.
Here's a guest to host sandbox escape for gVisor release-20260928
This was our planned submission for Wiz zeroday-cloud-2026. Releasing it today because it's now patched in release-20261005
enjoy :)
One attacker controlled image, default docker run --runtime=runsc, no --privileged, no runner -v, no added caps.
Shout out to @Zombiehelp54 and @Wrath_ZA
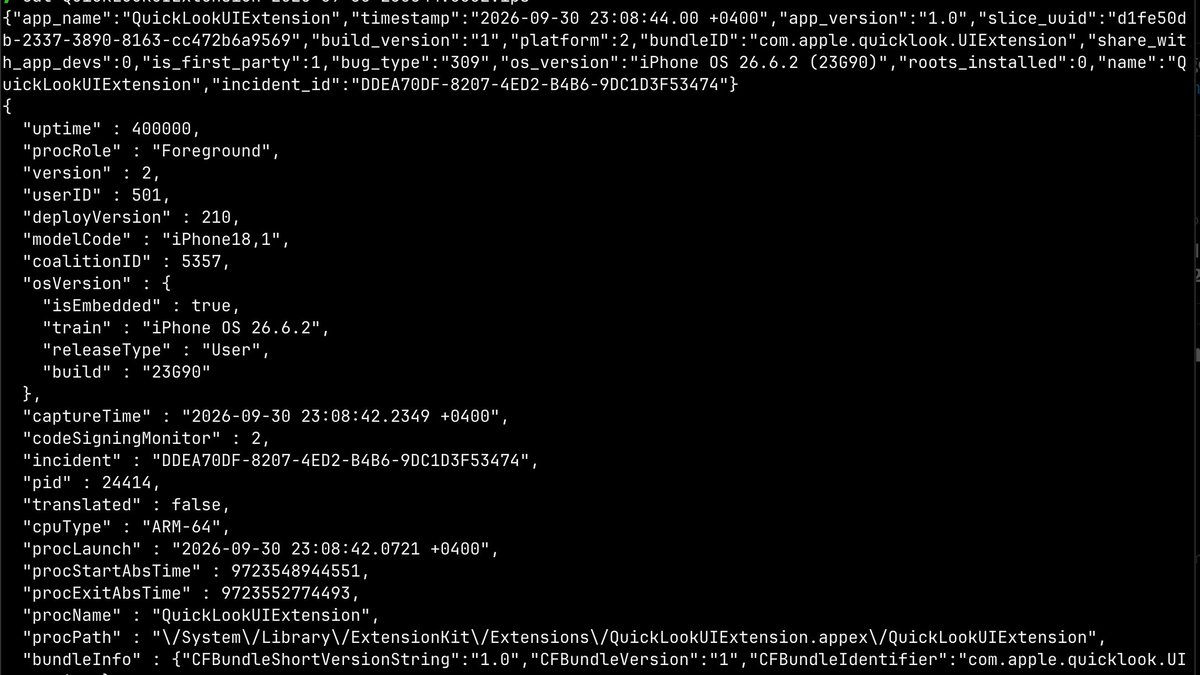
Looks like WhatsApp itself renders the PDF thumbnail (via WAMessageIDGetHighResThumbnailFilePathForMediaType)
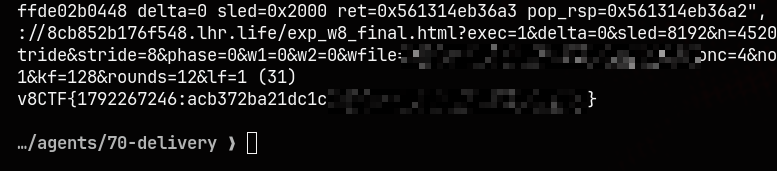
i.e. we have confirmed a live-heap corruption, on iOS WhatsApp (non-MTE) using a single crafted PDF
no arb r/w yet.
Since it's already public from https://t.co/3EX4ZqEkSc -
WhatsApp → QuickLook ext → PDFKit → PaperKit → PDFKit → CoreGraphics (aa_cache_render)
Reachable from a crafted PDF/font via the ImageIO/thumbnail path (QuickLook/sips).
Since it's already public from https://t.co/3EX4ZqEkSc -
WhatsApp → QuickLook ext → PDFKit → PaperKit → PDFKit → CoreGraphics (aa_cache_render)
Reachable from a crafted PDF/font via the ImageIO/thumbnail path (QuickLook/sips).
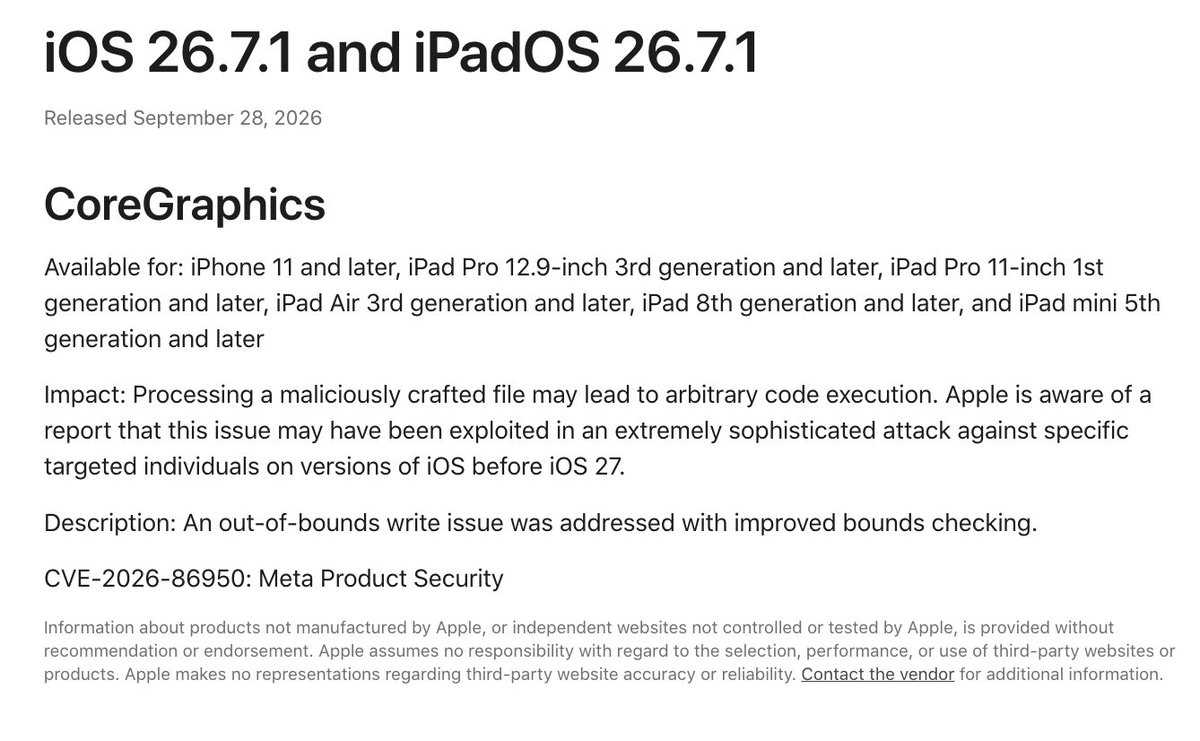
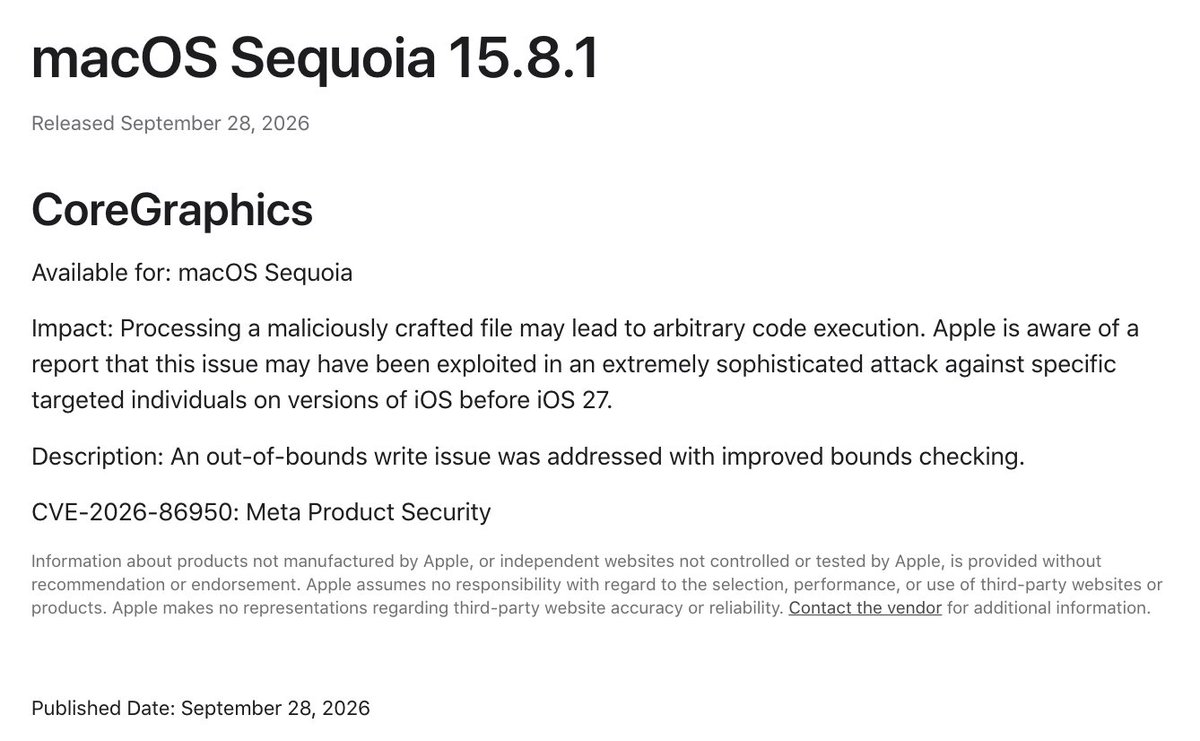
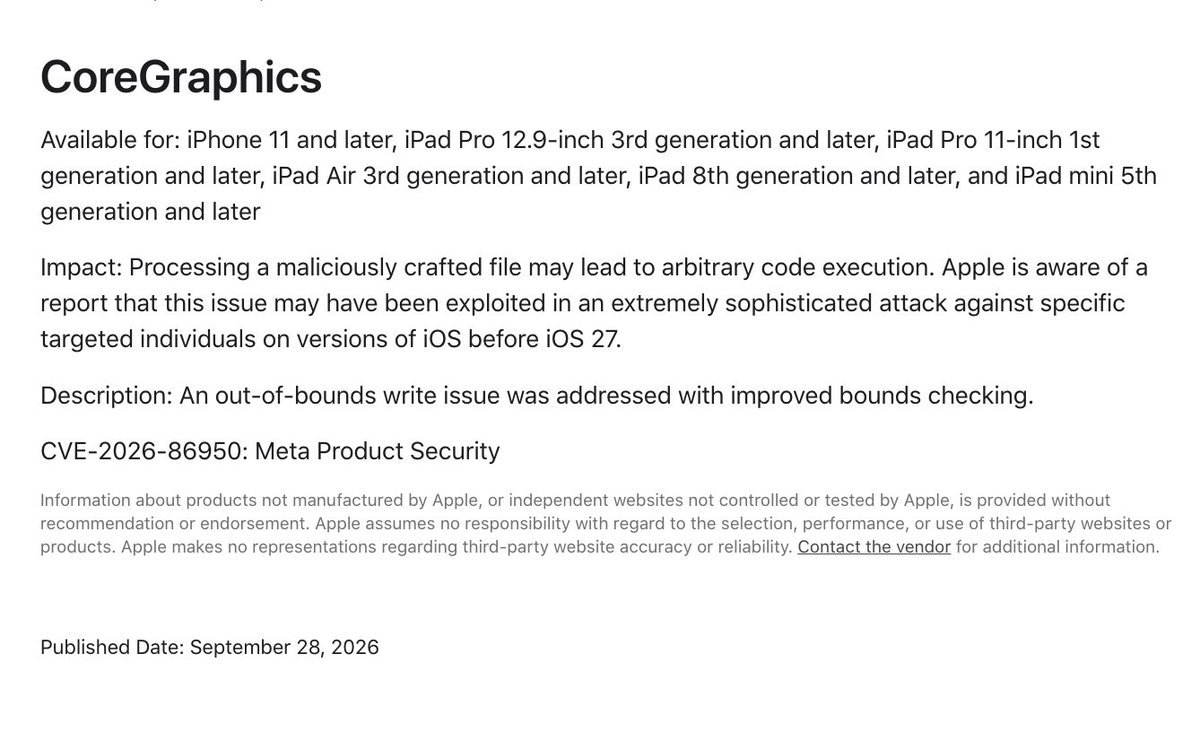
⚡️ 0-Day Alert: Apple CoreGraphics RCE exploited in targeted attacks
CVE-2026-86950: out-of-bounds write in CoreGraphics parsing a maliciously crafted image/PDF, leading to arbitrary code execution.
Both iOS and macOS are vulnerable.
This AV is reachable through a wide variety of iOS native and 3rd party apps that render graphics, such as WhatsApp (first suspect due to report credit), Safari, iMessage, etc.
Zero-click where auto-preview renders the file.
However, the bug alone is not enough to compromise the device, and requires further chaining such as sandbox escape and EoP. These further bugs are not public.
Patched in iOS/iPadOS 26.7.1, macOS Tahoe 26.7.1, macOS Sequoia 15.8.1.
https://t.co/F9ekneBQ2m
Took a minute to write a few words about security & safety as someone who lived through it all at OpenAI. I hope my thoughts help someone out there. https://t.co/gJBf08vJH9
one of my engineers reached out to me about how they struggled to find satisfaction in their work in the age of AI. I asked them if I could publish our brief exchange, and they agreed. I know people are feeling similarly, so maybe they can relate. https://t.co/YbeImE6aId
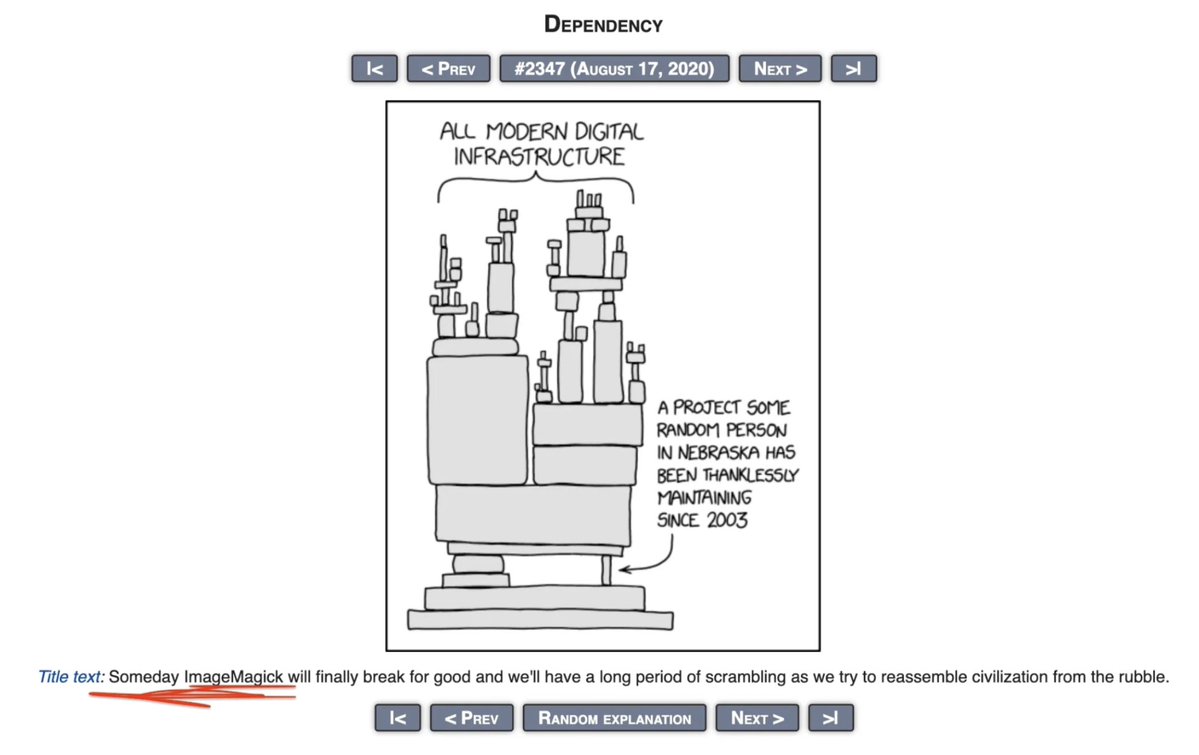
We’re disclosing HEIF Heist, a months-long investigation into libheif that allowed us to hack OpenAI, Slack, Meta, GitHub Ent, Rails, Next.js, ImageMagick, and many more.
It was literally xkcd #234, one obscure image library beneath a huge number of apps. 🧵