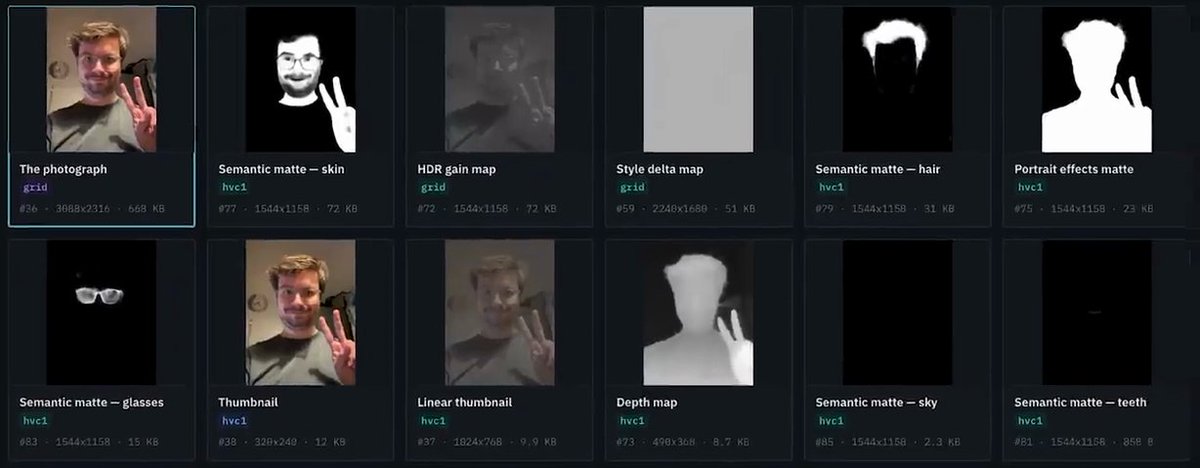
Remember the Heap Buffer Overflow in libheif 1.19.7, which was used by @rootxharsh to hack into OpenAI?
Here is a .heic file from a iPhone photo, which actually contains several images. And the primary image is actually derived from a grid of smaller images. 🧵1/x
Hacktron has reported high-impact vulns to us through our bug bounty program. Now we’re teaming up with @zeyu1337 and the Hacktron crew to hunt for more. https://t.co/XZYPTUzJvV
Two crazy things happened in my life:
1. Got married to the love of my life, surrounded by the people I love most.
2. Partnering with OpenAI. Link below
OpenAI has announced a partnership with Hacktron to investigate vulnerabilities in its systems. Our researchers will work with @OpenAI's engineers to prioritize testing of connections with third-party services, with broader frontier-model access through Daybreak Red.
We're excited to deepen our partnership with OpenAI, combining our offensive security expertise with their frontier models to help secure OpenAI and the broader software ecosystem.
https://t.co/PqWAT5g3W3
Our security researchers built an autonomous cyber vulnerability discovery, exploitation, and patching pipeline.
In a single run with an upcoming cyber model, it validated and generated patches for 948 local privilege escalation vulnerabilities in the Linux kernel at a total API cost of $1.2 million.
I want to share some context on a security incident we discovered on October 30.
First, the most important thing: WorkOS's production systems are secure. No customer platform data was accessed. This incident was isolated to internal GTM systems.
The attack involved ARTEX, an autonomous AI agent framework used to carry out offensive security operations. It's a striking example of how quickly the capabilities of attackers are evolving.
We've contained the incident, brought in independent experts to investigate, and are working through the details.
Security is something we take extremely seriously, and I believe in being transparent when things go wrong. We'll continue to share updates as we learn more.
Full details: https://t.co/6Pt6Nt7kr5
What if you could backdoor Bash, ls, cp, rm, and other GNU software used by millions of systems?
Our research led us to hack GNU Savannah, the infrastructure hosting their source code.
The xz backdoor that never happened 🧵
this blog shows some of the worst bugs claude found, including a zero-click rce on the linux networking stack that roots a server over the network with no creds or interaction, and tens of full rce chains in chrome (recording below is the one in the blog): https://t.co/DHkfR22s94