Three zero-day vulnerabilities in Ivanti Connect Secure VPN allow attackers to gain root access without login and steal credentials. Ivanti has patched two, with one fix still pending.
Ref: https://t.co/rtqFJzSEb8
‼️ Three zero-days. Root commands. No login.
An attacker exploited the flaws in a fully patched Ivanti Connect Secure VPN and stole stored credentials.
Ivanti confirms exploitation in the wild. Two flaws patched; a fix for the third is pending.
Read: https://t.co/9r024KMdmh
Bricksforge WordPress plugin has a critical vulnerability (CVE-2026-85097) with a CVSS score of 10.0. It allows unauthenticated remote PHP code execution via crafted file-upload metadata. Patchstack reported 63 active attacking IPs; update to v4.0.1.
Ref: https://t.co/vJBiVdTIHf
⚠️ No login required. CVSS 10.0. Active exploitation.
Attackers are exploiting a Bricksforge WordPress flaw (CVE-2026-85097) that enables arbitrary PHP code execution through crafted file-upload metadata.
Patchstack observed attack activity from 63 IPs. Update to version 4.0.1.
Read - https://t.co/GMJnf0PB2u
Five Eyes and Allies Expose Chinese Tech Firm Integrity Technology Group as State Hacker Front
The UK's NCSC, along with Five Eyes partners, Japan, and Spain, issued a joint security advisory exposing China-based Integrity Technology Group for acting as a front company for Chinese state-sponsored threat actors (such as Flax Typhoon / Red Juliett). The advisory details how Integrity Tech develops AI-enabled attack software, manages massive Mirai-based botnets, and deploys specialized tools like Microscan and FishHub to conduct automated vulnerability scanning, spear-phishing, and data exfiltration against critical national infrastructure (CNI), healthcare, manufacturing, and Taiwanese universities.
Ref: https://t.co/miXo6hygmk
CISA has released the "Cybersecurity Foundations Resource Package" for K-12 schools and districts. It offers cost-effective, actionable, and tailorable steps to help educational institutions develop and maintain effective cybersecurity programs and strengthen their overall cyber resilience.
Ref: https://t.co/wfo4Ecsrc2
Strengthen #K12 cyber resilience w/ our Cybersecurity Foundations Resource Package. Explore cost-effective, actionable & tailorable steps that schools & districts can take to develop & maintain effective cybersecurity programs: https://t.co/RQk5zpXWOn #CybersecurityAwarenessMonth
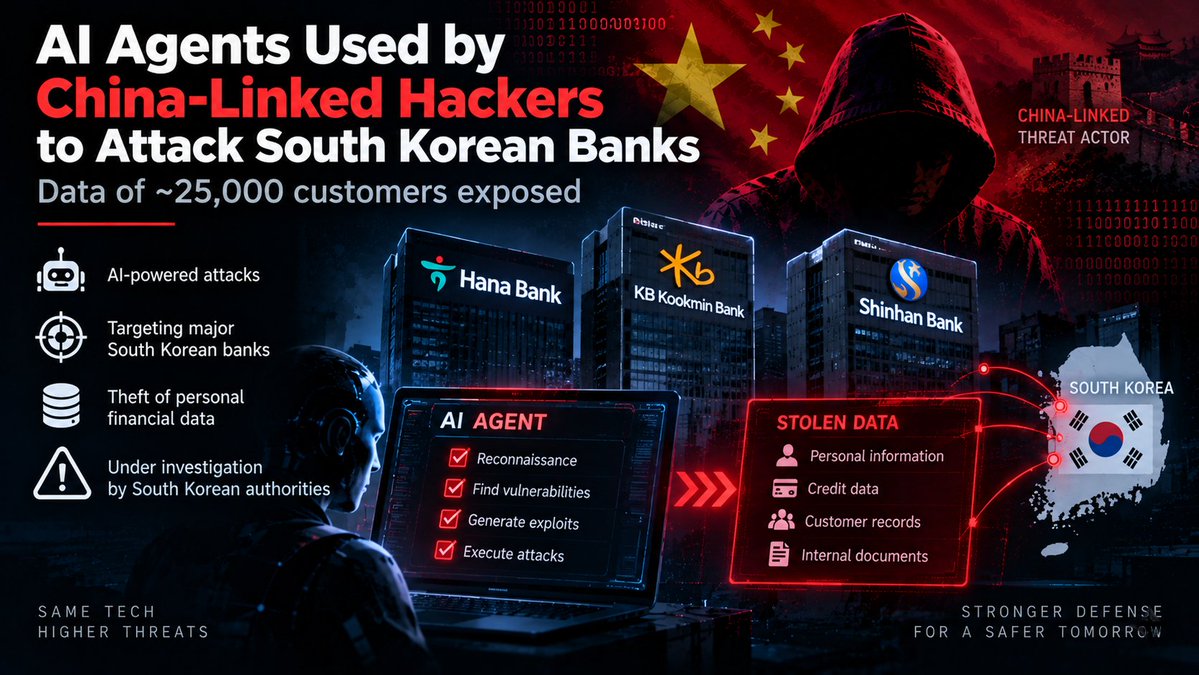
China-Linked Hackers Abuse AI Agents to Breach South Korean Banks, Exposing 25,000+ Customer Records
South Korean police and financial regulators have launched a major cybercrime probe into coordinated attacks against major banks, including Shinhan, KB Kookmin, and Hana Bank. The breaches exposed personal credit data belonging to over 25,000 Shinhan Bank customers and thousands more across the financial sector. Forensic traces at attack IP addresses revealed the misuse of Artex AI, a Chinese-language penetration testing and AI agent framework, strongly pointing toward China-nexus threat actors using automated AI models to orchestrate zero-day reconnaissance and credential harvesting. South Korean President Lee Jae Myung ordered immediate national security countermeasures against AI-driven state-sponsored cyberattacks.
Ref: https://t.co/paiKohaYy0
GitGuardian detected 28.65 million new hardcoded secrets in public GitHub commits in 2025, representing a 34% year-over-year increase. Additionally, 24,008 unique secrets were found in public MCP configuration files, with 2,117 of them verified as valid.
Ref: https://t.co/TYfeY1OMGm
GitGuardian found 28.65 million new hardcoded secrets in public GitHub commits in 2025, up 34% year over year.
It also found 24,008 unique secrets in public MCP configuration files, including 2,117 verified as valid.
See how credentials are spreading across code, endpoints, and AI tooling: https://t.co/uhfhKPhnoZ
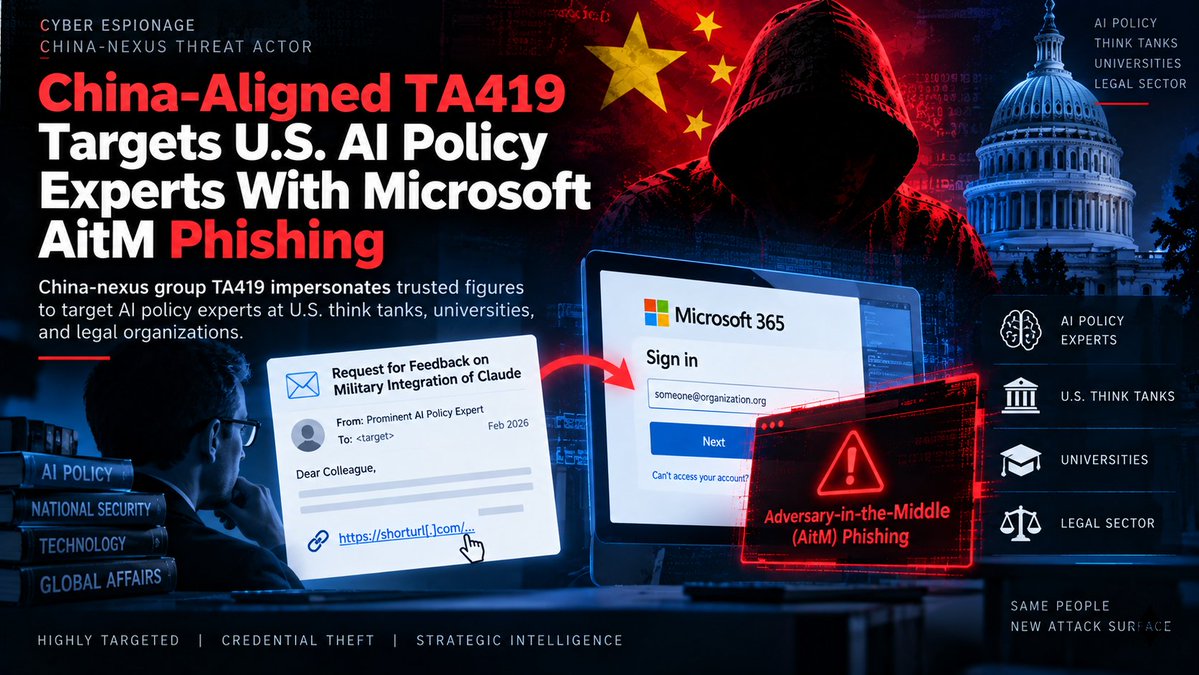
China-Aligned TA419 Targets U.S. AI Policy Experts With Microsoft AitM Phishing
Proofpoint detailed a credential phishing campaign by China-aligned threat actor TA419, targeting U.S. artificial intelligence (AI) policy experts across think tanks, universities, and law firms. The attackers impersonated prominent economists, White House OSTP officials, and Anthropic employees—using lure subjects like military integration of Claude—to trick victims. The attack chain leverages Frameless BitB (Browser-in-the-Browser) technology paired with an Adversary-in-the-Middle (AitM) proxy to silently capture Microsoft 365 credentials and session tokens, supporting wider Chinese intelligence gathering on U.S. AI regulations and export controls
Ref: https://t.co/pto18r9lQF
#China #US #APT
CISA has added the Citrix NetScaler vulnerability CVE-2026-88779, characterized as an improper restriction of operations within the bounds of a memory buffer, to the Known Exploited Vulnerabilities (KEV) Catalog, urging organizations to apply mitigations to protect against cyberattacks.
Ref: https://t.co/qWhkAPiqUg
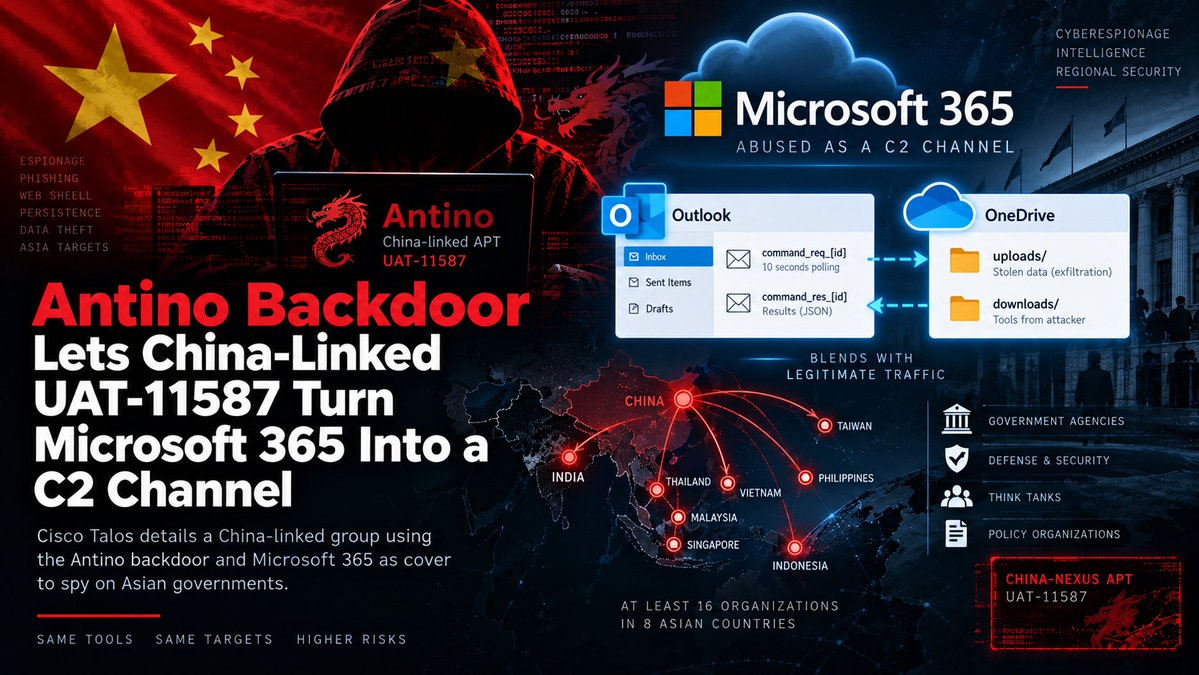
China-Linked UAT-11587 Uses Antino Backdoor to Abuse Microsoft 365 as C2 Channel
Cisco Talos detailed UAT-11587, a China-nexus cyberespionage group targeting over 16 government agencies and policy organizations across eight Asian nations. Initial access is gained via highly tailored spear-phishing lures, leading to the sideloading of Antino, a new Rust-compiled Windows backdoor. Antino bypasses conventional C2 detection by exclusively abusing Microsoft Graph API to poll Outlook mailboxes for commands and utilize OneDrive for data exfiltration, blending C2 traffic into legitimate Microsoft 365 cloud activity.
Spot on. The recent MI5 alert on CGTRI is a textbook example of this exact dynamic: Beijing weaponizing academic partnerships to pipeline tech directly into the MSS.
When 100+ UK researchers unknowingly feed state-backed cyber ops, open research effectively becomes a Trojan Horse. Time to audit the pipeline. 🧵👇
#ThreatIntel #ChinaEspionage #MSS #AcademicSpying #GlobalCyberThreat
links:
https://t.co/6fHWbn7RDn
https://t.co/qbYdZkDhp2
@ukctransparency
Is UK academia becoming a Trojan Horse for the China’s cyber forces? Beijing’s Military-Civil Fusion leverages 13 UK partnerships with Top Secret-cleared entities, bridging the PLA, MSS, and sanctioned actors like 'Flax Typhoon'. This structural weaponization of research transforms global collaboration into a systemic offensive threat. 🧵
published with
@ukctransparency@eubenincasa
Links:
https://t.co/qbYdZkDhp2
https[:]//drive.google.com/file/d/191AIaCGKl0jrNy261wJfJsRyEs4Rlf0v/view
#ChinaCyberForce #MilitaryCivilFusion #AcademicTrojanHorse #GlobalCyberThreat
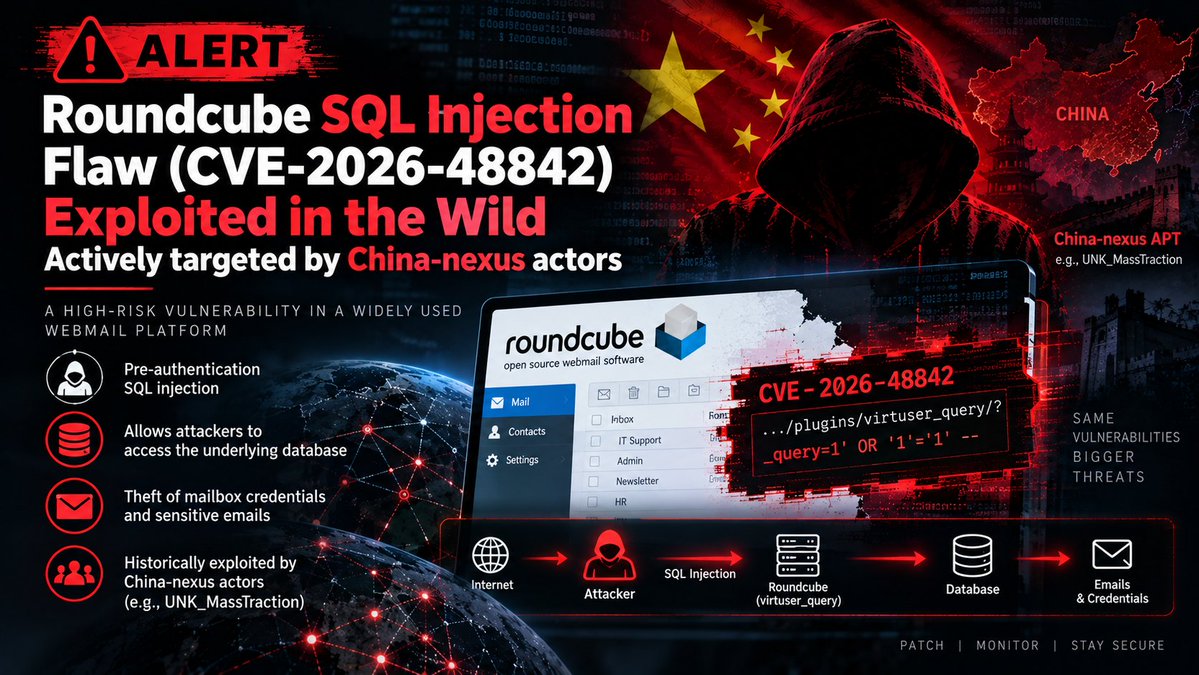
Roundcube SQLi Flaw (CVE-2026-48842) Exploited in Wild; Targeted by China-Nexus Actors
A pre-authentication SQL injection vulnerability in Roundcube Webmail's virtuser_query plugin (CVE-2026-48842, CVSS 8.1) is now under active exploitation in the wild. The flaw allows unauthenticated attackers to bypass backslash-escaping mechanisms and access underlying databases to steal mailbox credentials and messages. Roundcube flaws have historically been a primary initial access vector for China-nexus threat actors (such as UNK_MassTraction) to deploy Web Shells and post-exploitation tools.
Ref: https://t.co/1d6VBO6nZH
Espionage Group 'NightEagle' Expands Operations from China to Russia
Cyberespionage group NightEagle (also tracked as APT-Q-95), previously known for targeting high-tech and defense entities in China, has expanded its operations to hit Russian companies. According to Kaspersky, the threat actor gains initial access via stolen VPN credentials to compromise Microsoft Exchange servers with the GhostContainer backdoor. The group leverages memory-only execution, Active Directory exploitation, and disguised GitHub repositories to achieve persistence and lateral movement toward domain controllers
Ref: https://t.co/LZpdSrFsOD
Beijing’s playbook:
1. Get caught distilling Western frontier AI for military use.
2. Cry "Western smear campaign!"
3. Get hit with undeniable Anthropic’s report.
4. MSS chief scrambles to preach "AI security."
You can't steal the reasoning and pretend you built the brain. 📉🤖
links:
https://t.co/SSeaEf4ncX
https://t.co/ORuM7NpPuV
https://t.co/J4bUiPusDE
Great minds think alike:
@JamestownTweets@AnthropicAI@netaskari@henrysgao
Is your AI a shadow clone? Beijing’s "Adversarial Distillation" campaign strip-mines Western LLMs to build high-speed tools for PLA cyberattacks and surveillance. This shortcut bypasses safety guardrails, weaponizing global innovation into a systemic offensive threat. The data is clear—this is industrial-scale theft. 🧵
published with
@JamestownTweets@ChinaBriefJT@SunnyCheungky
links:
https://t.co/3t1yfqmHFj
#ShadowDistillation #PLAAI #ChineseCyberThreat #DigitalEspionage