I released an article talking about my bug bounty journey, how I ranked 1st in U.S. DoD and how I reached top 100 hackers on @Hacker0x01. Sharing also resources, tips and advices to become a better bug bounty hunter.
https://t.co/epV5rSGwb0
Today @CISAgov released guidance on vulnerability reporting for election administrators. This is a great resource for any election official looking to implement a vulnerability disclosure policy. Read here: https://t.co/550gDAH5Fa
#XSS Interesting Weekend Read:
What’s in an Exploit? An Empirical Analysis of Reflected Server #XSS Exploitation Techniques by Ahmet Salih Buyukkayhan et al.
https://t.co/4zZtFHNfIb
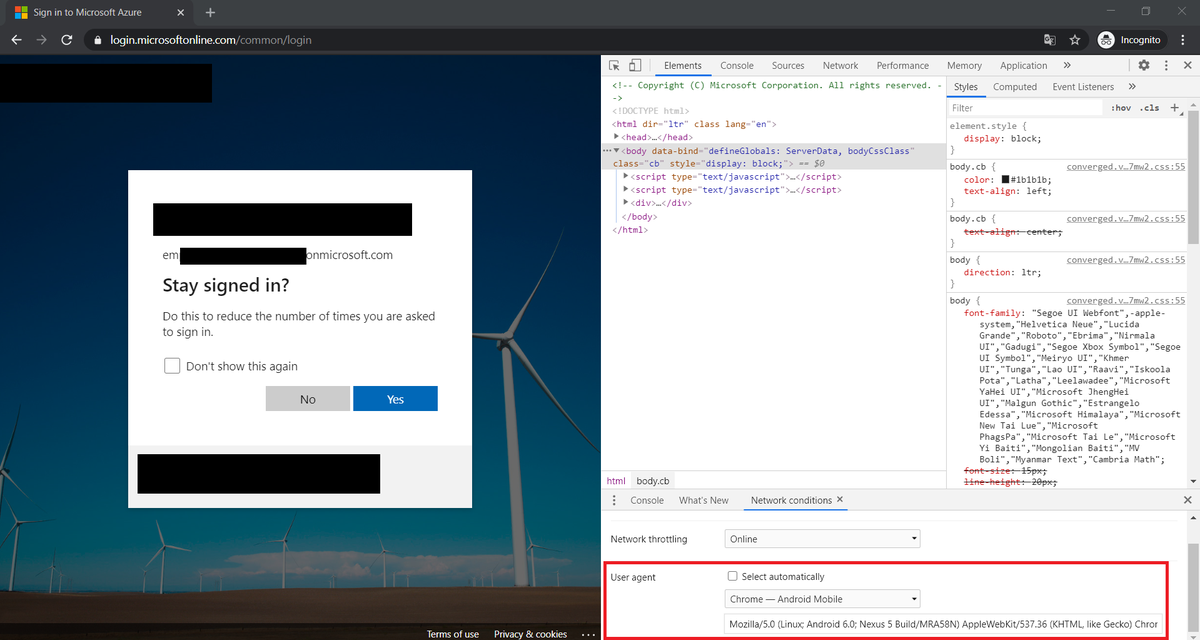
Got clear-text password of a user but #Azure AD enforces 2FA? Try changing the User-Agent string. The 'platform' in Conditional Access policies is determined by User-Agent string of the browser. #RedTeam
I recently discovered a fancy way to execute arbitrary XSS without parenthesses. As far as I am concerned this is a novel technique 😁
https://t.co/K0ebjvpmxq
#javascript#bugbountytips#xss