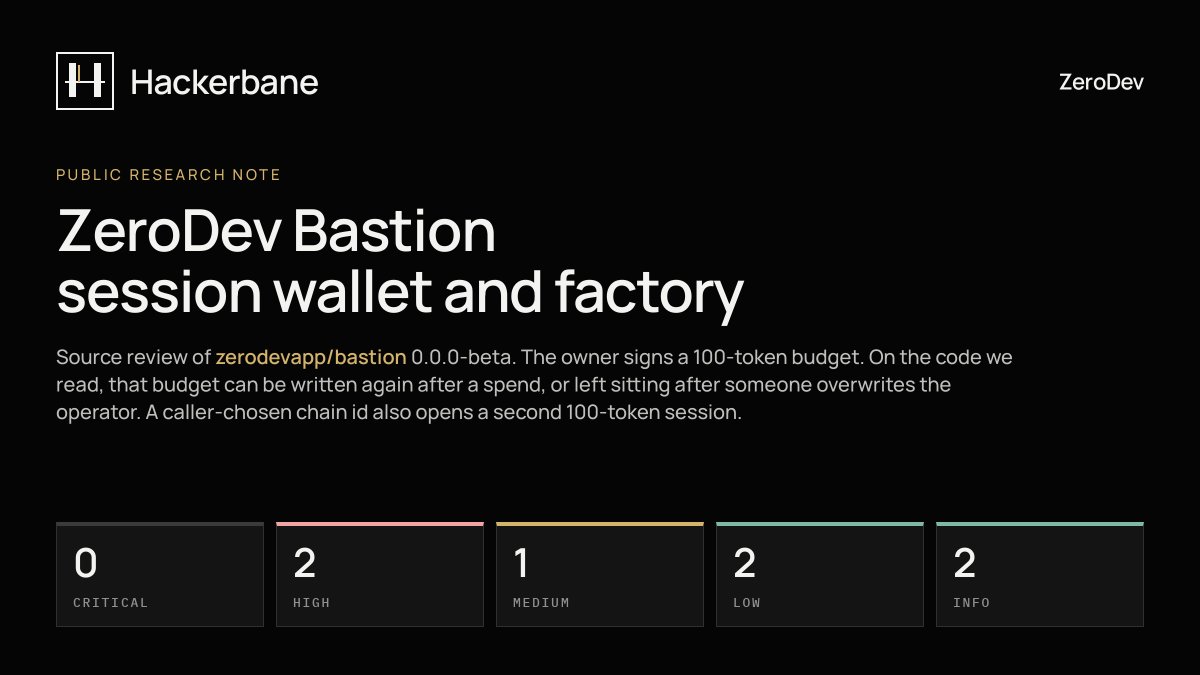
This week our team found high-sev vulnerabilities in ZeroDev's Bastion session wallet. Replaying a signature refills a factory budget that was already spent.
Full report: https://t.co/D9Dk1cFNoG
@Harvesto12 Enough to make it not worth it. I'd say 9/10 genuine findings get ignored, called "known" or "intended", or straight up rejected for no good reason.
This week our team reviewed @Shipfox_HQ. We found four vulnerabilities, one critical.
Communication with the team was excellent, and all findings were resolved within 48 hours.
Full report: https://t.co/z9OsLxRLGB
@0zSchnack Public bug bounties are very low yield now that anyone with a claude sub can join the party unless you have some very sophisticated techniques
We found 2 Critical vulnerabilities in a live token protocol this week. The findings have not been resolved.
100% of the protocol's live TVL is currently at risk, and the team have not yet responded to our report.
Our researcher found 6 high-severity vulnerabilities found in a Web3 bridging platform. Multiple attempts to contact the team via DMs, email and Discord. Still no response.
If you're handling user funds, ignoring security disclosures is unacceptable.
This week our team audited oksolc, the Zig implementation of the Solidity compiler.
Writing a secure and correct compiler code is one of the most technically challenging areas in Computer Science.
full report: https://t.co/DbZRHErlMH
Our lead security researcher has contacted @OpenAI about a vulnerability in ChatGPT, allowing full nudity imagery through the chat UI.
We've notified OpenAI and are withholding reproduction details while the issue is assessed.
More to follow
HACK: Ledger asked CryptoBilis to pause sales and shipments of their hardware wallet.
If you bought a device there in the last 90 days, do not set it up. If you already did, move the funds to a new device with a new seed immediately.