@ykrauq Interesting perspective (as a challenge author!). I agree with you, AI makes CTFs much more accessible, but it definitely has both pros and cons 🙂
Platform Update:
~ Web Challenges: 5 labs dropped
~ Pwn: 1 challenge updated and 2 new ones
~ XP Rebalance & Hint Improvements, UI Polish
~ CTF Thursdays: Starting next week, every Thursday at least one new challenge drops!
Happy Hacking!
#ctf#ctfs#ethicalhacking#cybersecurity
Reversing public #security advisories has been a lot of fun lately. Here's an exploit I've built for CVE-2025-9501 that potentially affects 1+ million #WordPress installations:
https://t.co/PVBnKi0rO8
Wrote an in depth review of the new SANS SEC565 Red Team Operations and Adversary Emulation.
Purpose: Help those figure out if it's for them.. https://t.co/RfgBLHNX3z
PS: If you decide it's your poison, then @Jean_Maes_1994; @jorgeorchilles & Barrett are running it this month
I recently finished up exploits for what I believe to be CVE-2023-20025 and CVE-2023-20026. It's kind of wild that Cisco isn't going to patch these with ~20k internet-facing / affected devices.
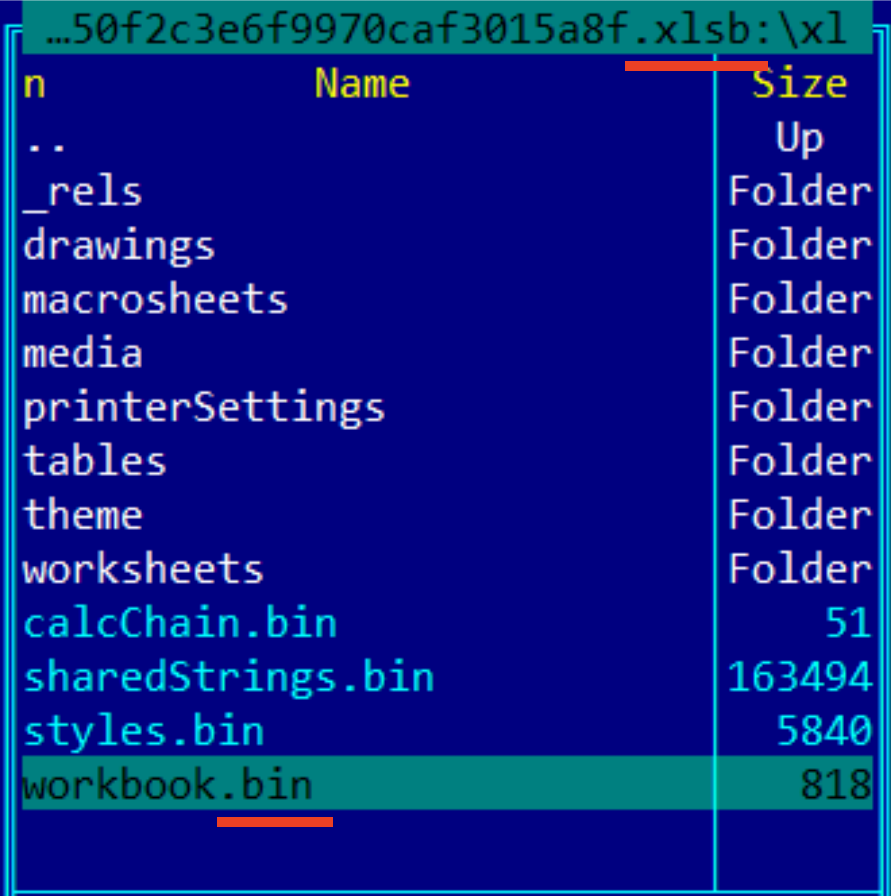
RE tip of the day: In OOXML files, if macros are supported, the last letter of the file extension will be m rather than x (example: .xlsm). If you see inside files with an extension .bin instead of .xml, the sample file extension should end with b (like .xlsb)
#infosec#reversing
A lot of people blaming #Log4j devs about the exploit... I honestly find it pathetic. A lot of people sharing the "Dependency" XKCD post? Maybe appropriate. But this is WAY more appropriate.
You get what you pay for, and if you can, and don't pay enough, YOU are to blame.