I am giving away 1 seat each for our upcoming bootcamps.
Azure Cloud Attacks (CARTP) - 3rd Feb (9:00 AM ET)
Active Directory Attacks (CRTP) - 4th Feb (9:00 AM ET)
Please Reply, Like and Repost to participate. The winners will be announced on Friday 2nd Feb 2024.
https://t.co/BG69lSjBny
#Azure #Redteam #Pentesting
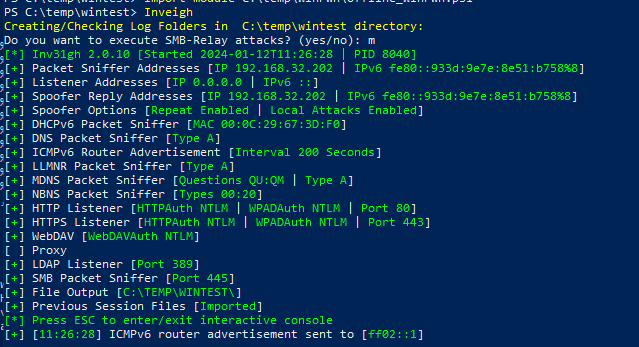
Just updated Rubeus, Seatbelt, Certify, Invoke-Privesccheck in PowersharpPack and WinPwn. It was time again.
Also WinPwn now uses the C# Inveigh version with way more features enabled.👌
🚨 Massive AI Security Release 🚨
@NIST just put out the best AI Security Publication that I've ever seen.
It is 106 pages of deep, technical content. It references real-world practical attacks. In this thread is the link and I'm going to cover a few highlights. 👇
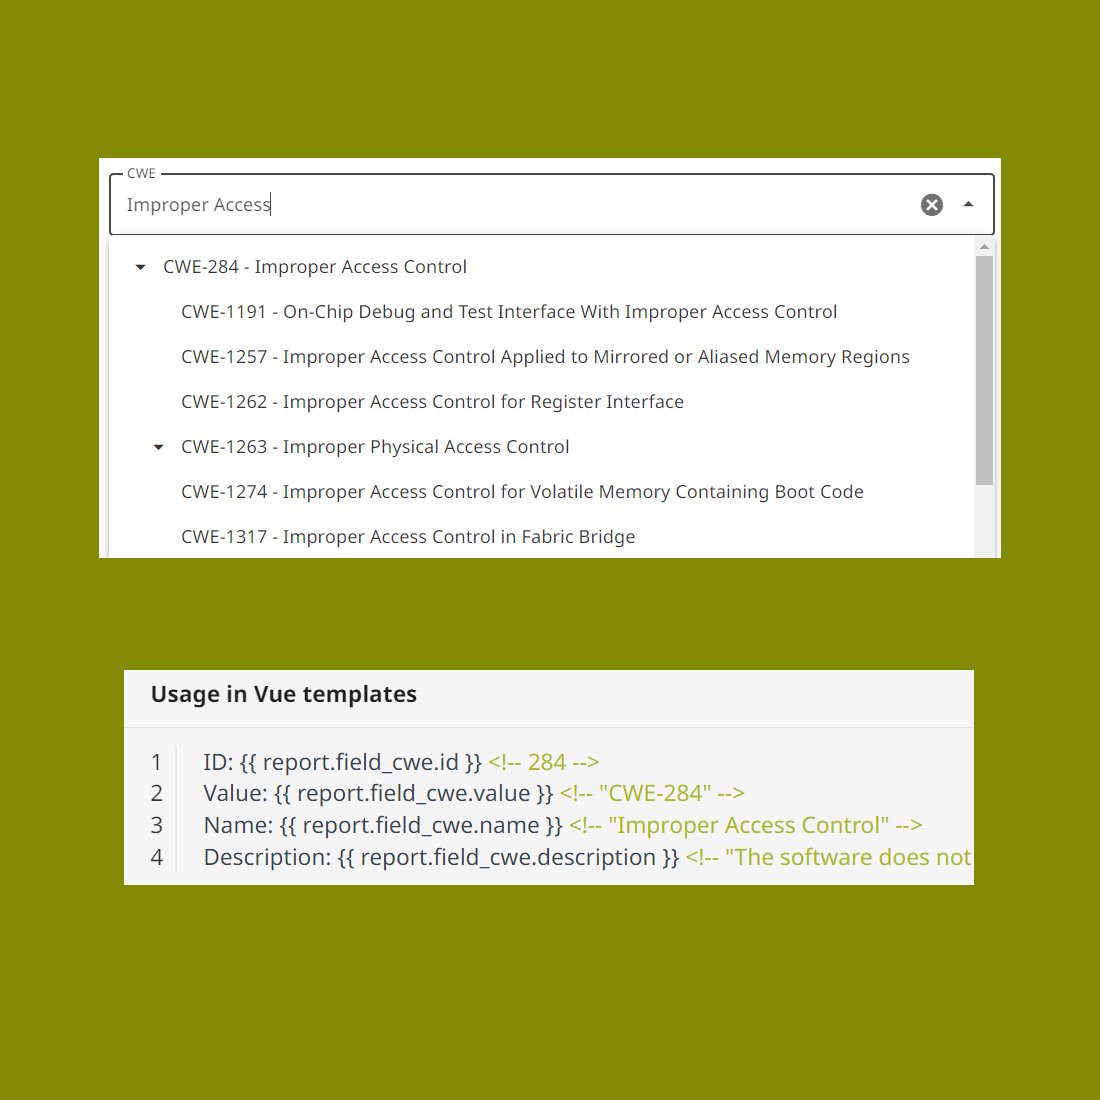
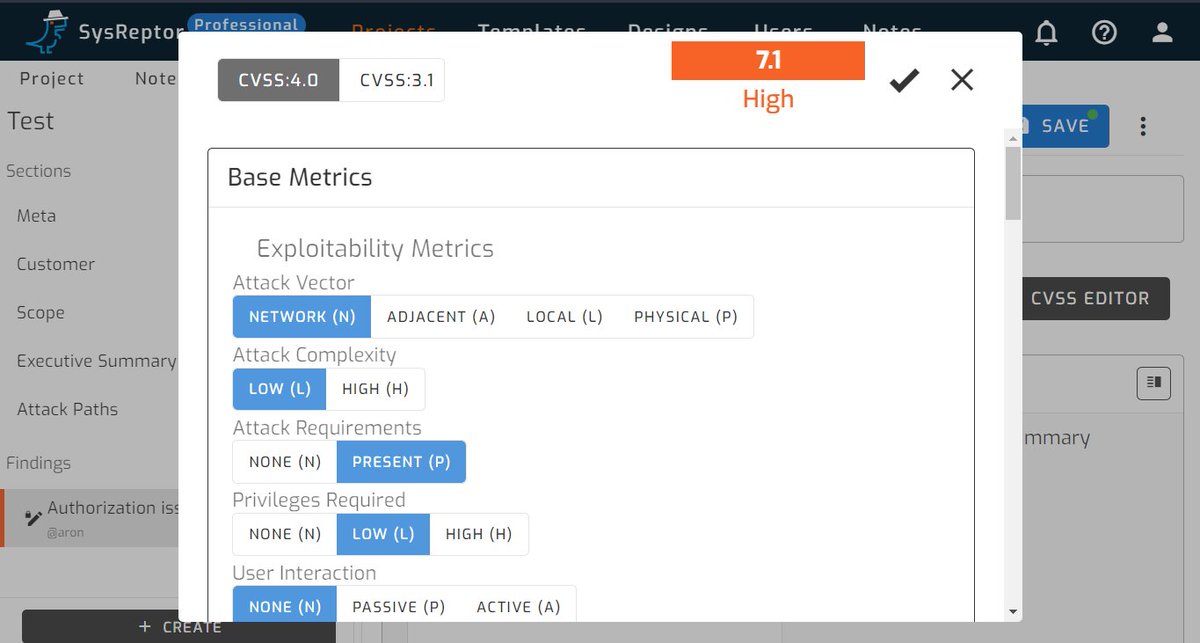
Our last update brought CVSS v4.0 🎉
You can define in your report design, if you want to use v3.1 or v4 (or any of them).
Or to get to know each other: You can add two CVSS fields and enter both.
Swiping more Microsoft 365 session tokens... but with a different technique! Showcasing TokenTactics and the device code phishing trick -- we convert in HTTP cookies, browse the victim's inbox, and earn more access into the cloud environment 😎 https://t.co/RgS9iZ3MCb
‼️ M365 admins ➡️ Did you know there are two types of conditional access policies that can COMPLETELY BLOCK phishing attacks on your users? 👇
I just published a video with heaps of demos showing...
❌ how easy it is for attackers to phish users with main-in-the-middle phishing attacks using the awesome @evilginx app created by @mrgretzky
✅ how to block these phishing attacks using two types of conditional access policies
This is a bit of a longer video than my usual ones.
Please like and share this tweet ➕ subscribe to my YouTube channel if you would like me to make more video explainers like this 🙏
https://t.co/DtzomO75Y4
Democratic nations are slowly rolling back protections against the kinds digital of surveillance that were once limited to despotic regimes.
If passed, Article 25 will allow European govts to spy on encrypted internet traffic.
👇 Check this out 👇
https://t.co/PbgROZqRpO
🗝️A skeleton key attack patches LSASS on the victim's domain controller. This enables the attacker to authenticate as any user with a master password.
#ThreatHunting#DFIR
My @defcon submission is accepted!
Come see my talk 😄
The GitHub Actions Worm: Compromising GitHub repositories through the action dependency tree
#defcon31
GIVING AWAY 5 free coupons to my Offensive Rust course.
Like and retweet this tweet to enter.
5 Winners will be picked up on Tuesday.
this course is packed with malware development with rsut.
https://t.co/t5PsTKYxdD
#infosec#malware#rust#rustlang#redteam#cybersecurity
Just to clarify some points on this:
- This assumes full compromise of the on-premises AD
- The attack applies regardless of whether you actually use Seamless SSO or not
Done, CrackMapExec is now able to decrypt LAPS password thanks to the awesome work of @_zblurx and @BoreanJordan 🎉
If you have a credential that can read laps password, just run a /24 with the option of your choice (lsassy, lsa, dpapi...) and quickly become DA (probably) 👑
🪂