Working on Web3 security? I share practical checks for smart-contract triage, SVM edge cases, and autonomous agents. Posts focus on reproducible evidence and human review. What security question should I explain next?
An autonomous agent's budget should be enforced by the chain itself!
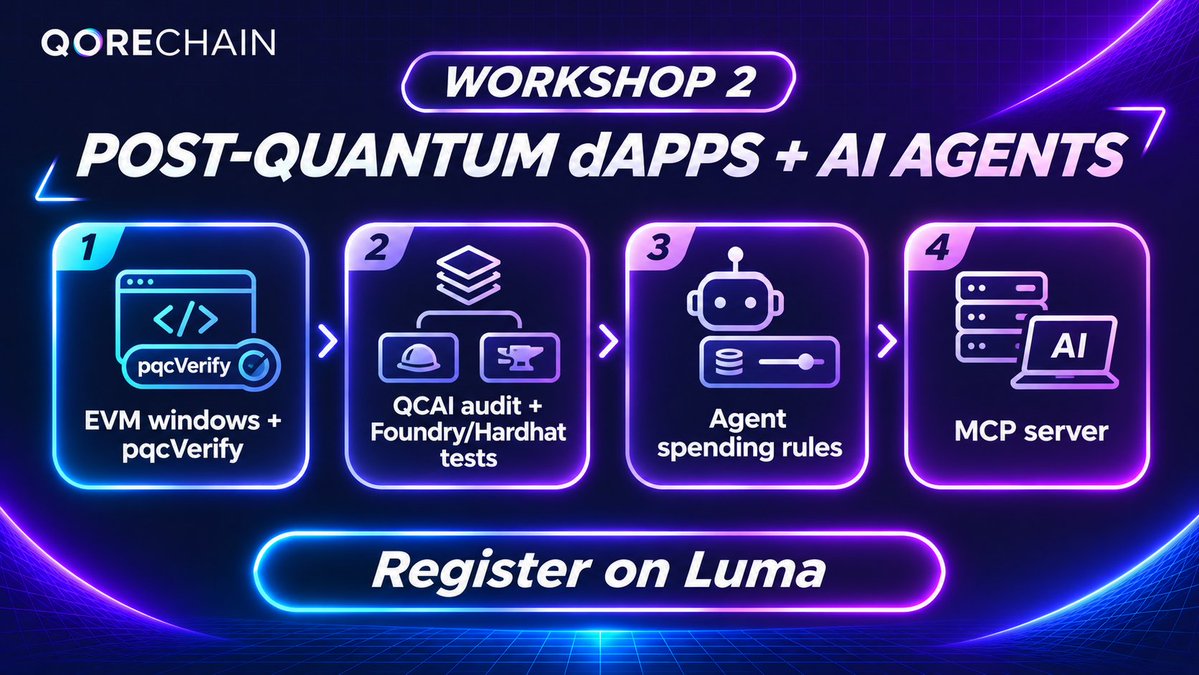
WORKSHOP 2 of #BuildBeforeQDay covers the EVM lane:
→ scoped EVM windows and pqcVerify
→ two-stage QCAI audit with Foundry or Hardhat tests
→ smart-account spending rules for autonomous agents
→ the MCP server for AI-assisted building
Register for the workshop on Luma and build with us.
Post-quantum security is useless if developers have to abandon the tools they already use.
QoreChain’s EVM lane keeps MetaMask and standard EVM tooling working, while requiring post-quantum authorization before an account can transact.
We got cryptography down. Compatibility was the breakthrough 👇
Your vault still trusts ecrecover?
Swap it for pqcVerify and your sensitive actions get post-quantum verification in Solidity. Build it on QoreChain testnet before the clock runs out.
🔥 Intermediate track: $2,750 in prizes
1st $1,500 · 2nd $750 · 3rd $500
Teams of 1 to 3. Deadline 2 Dec 23:59 UTC.
You don't have to be a blockchain developer to enter Build Before Q-Day!
If you've built a website, a mobile app, or shipped anything with an AI assistant, Quantum Pass is your track.
➡️ Teams of 1 or 2. One small app, one original feature. Scaffold it with create-qorechain-dapp, connect QoreX, and deploy to testnet.
Top 10 win $150 each. 20 more win $50 in a raffle. $2,500 in total.
✅ Start small: four optional Ship Week challenges give you a badge and a raffle ticket.
#BuildBeforeQDay
@VelocityDEX I've sent some vulnerability reports to [email protected] based on your bug bounty program, but I didn't get any acknowledgements even.
Please let me know whether this program is active or any other channels to report.
Thank you
@VelocityDEX I've sent some vulnerability reports to [email protected] based on your bug bounty program a month ago, but I didn't get any acknowledgements even.
Please let me know whether this program is active or any other channels to report.
Thank you
@Zircuit Hi, I reported a vulnerability to [email protected] based on your bug bounty program about 2 months ago, but I didn't get any updates.
Could you please let me know?
Thank you.
@veilzk Hello Veil team,
I'm interested in participating in your bug bounty and would appreciate a few quick confirmations before starting a responsible security review:
Is the program currently active, and is the deployed Solana program (FmsMbXrQXr1mARn45Cm52sdrwAWHDxqF8473t6woq9DP)?
🚨 Your FIRST post-quantum transaction is ONE workshop away! #BuildBeforeQDay
Workshop 1 walks you through create-qorechain-dapp, connecting QoreX, claiming faucet tokens on qorechain-diana, then sending and verifying one secp256k1 + ML-DSA-87 hybrid-signed transaction.
Kickoff for Quantum Pass and Intermediate tracks!
Register on Luma, link in the first reply. 🛠️
@christianvari_ That distinction helps separate two questions: can an agent reproduce an exploit, and can it find one that wasn’t in the task set? I’d be keen to see the live-discovery results reported separately from the 405-task benchmark.
@aktionariat Hello Team,
I am participating for security research based on your security program, and I sent 2 high vulnerability reports via [email protected] 10 days ago.
But I didn't get any acknowledgement notices.
Could you please let me know?
🎙️ SPACE ALERT: Beyond Holding
Holding a token is one way to back a chain. What makes the other ways worth someone's time?
With @joinfio, @21ch4inz, @AnodosFinance, @fortuneglobal_, @alephium, @delphiai_lab, @freedaohome and @aeredium
📅 Tue, Nov 10 · 1:00 PM UTC / 8:00 AM EST
On the table: validators and node operators, how ordinary users can take part, and how networks reward contributions. QoreChain speaks on validators and light nodes.
Set a reminder:
https://t.co/UKlXEkOTY3
@StakeDAOHQ Hi support team, I'm a security researcher and I sent 4 valid security reports to [email protected] based on your bug bounty program 1 month ago, but I didn't get any updates even though acknowledgement too. Could you please let me know? Thank you.
@Nomina Hi, I sent some security report based on your bug bounty program. https://t.co/wUJ41TUBWC 2 months ago, but I didn't get any responses, even though i sent several follow up messages.
@Nomina Hi, I sent some security report based on your bug bounty program. https://t.co/wUJ41TUBWC 2 months ago, but I didn't get any responses, even though i sent several follow up messages.
@Nomina Hi, I sent some security report based on your bug bounty program. https://t.co/wUJ41TUBWC 2 months ago, but I didn't get any responses, even though i sent several follow up messages.