

Top Tweets for #BLACKBASTA

Payouts King, the successor to BlackBasta, uses vishing and direct syscalls to bypass EDR and strike global targets. Learn how to defend your enterprise.
#PayoutsKing #Ransomware #CyberSecurity #InfoSec #BlackBasta #ThreatIntelligence #Vishing
https://t.co/yNYxonzPM1


Die Erben von Blackbasta formieren sich neu als „Payouts King“ mit raffinierter Ransomware
#Blackbasta #Cybersecurity #Cybersicherheit #Malware #PayoutsKing #Ransomware #SocialEngineering #ThreatHunting #Vishing @Zscaler @Zscaler_DACH
https://t.co/IBl5RPp5dS

BlueVoyant exposes Blitz Brigantine's new tactics: using email bombing, Microsoft Teams lures, and covert DNS MX tunneling to deploy AOBackdoor.
#BlitzBrigantine #AOBackdoor #CyberSecurity #InfoSec #BlackBasta #DNSTunneling #ThreatIntel
https://t.co/r8r2vAFfqy

Oleg Evgenievich Nefedov, alleged BlackBasta leader, added to EU Most Wanted and INTERPOL Red Notice lists. BlackBasta uses phishing, vulnerability exploits, and double-extortion ransomware. #BlackBasta #Ransomware #Russia
https://t.co/IXplE2FipH

⚠️ Black Basta resurfaces with refined ransomware tactics
Black Basta ransomware has re-emerged with updated tooling, tighter victim targeting, and improved lateral movement techniques, signaling an operational revival after months of reduced activity.
#ransomNews #BlackBasta #ransomware

#BlackBasta: Defense Evasion Capability Embedded in #Ransomware Payload - The vulnerable driver (an NsecSoft NSecKrnl driver) was bundled with the ransomware itself. Read more: https://t.co/0sdyacX6EZ
#NEW - #BlackBasta: Defense Evasion Capability Embedded in #Ransomware Payload - #BYOVD component included in ransomware payload itself, rather than as a separate tool. Read more: https://t.co/0sdyacX6EZ

Federal Agencies Worldwide Hunt for Black Basta Ransomware Leader https://t.co/0XHcLdGDdW #AI #BlackBasta #BlackBastaRansomware
European Authorities Identify Black Basta Suspects as Ransomware Group Collapses https://t.co/oNUzhbehbY #BlackBasta #BlackBastaRansomware #BlackBastaRansomwaregang
Black Basta Under Pressure After Ukraine Germany Enforcement Operation https://t.co/1eZlVcGfGy #BlackBasta #ContiRansomware #CyberExtortion


Ex miembro de Conti, ahora conocido como "Devman", añadido a la lista de buscados de Interpol (actualizado)
#Devman #ransomware #blackBasta #infosec #ciberseguridad #Conti
😆si es el mismo me ha insultado dos veces una por Black Basta otra por Devman
https://t.co/NmJTy6xHqC

Just a friendly reminder that you're free to go source all the leaks surrounding #Lockbit #BlackBasta and a few #DarkWeb Markets... I cannot remember if I added "Dream Market" so if it's not there I'll added it
https://t.co/GKeyhReol8


While researching another topic, I found this in the #BlackBasta leaks. They mention the company in question. Interesting.
It also notes the use of signed .MSI files and powertick, neither of which are mentioned in the ICO UK report 🤔
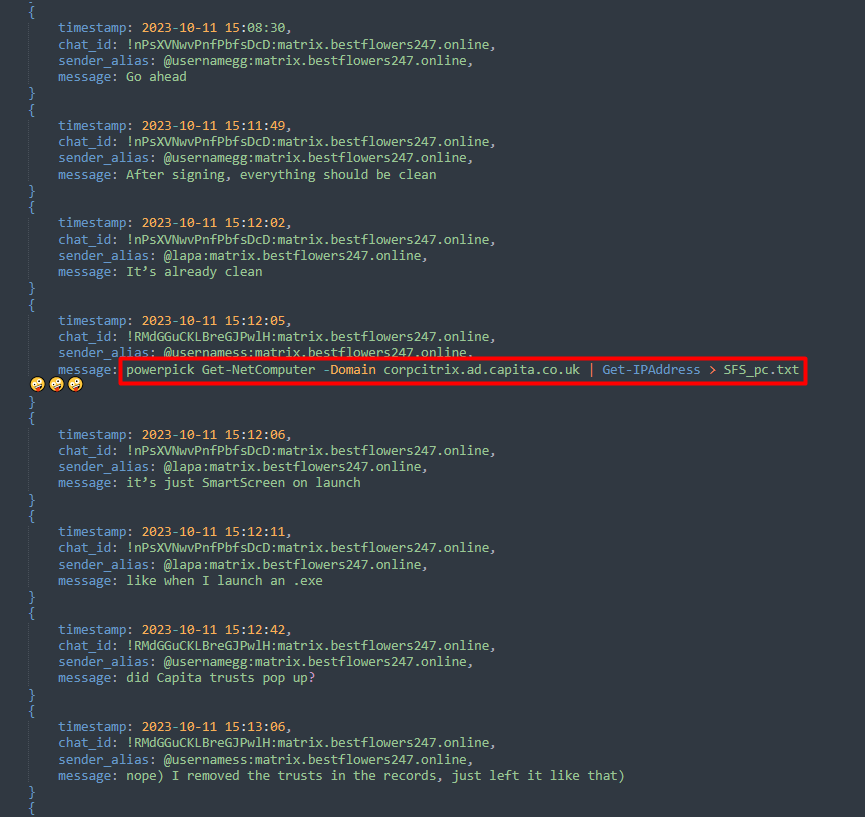

Details about the Capita Breach have been shared via the UK ICO including the Kill Chain:
“jdmb.js” -> Qakbot -> CobaltStrike -> Bloodhound -> SystemBC -> Rclone -> BlackBasta ransomware
https://t.co/bSq1VMyC95
h/t @AlexMartin for finding the report
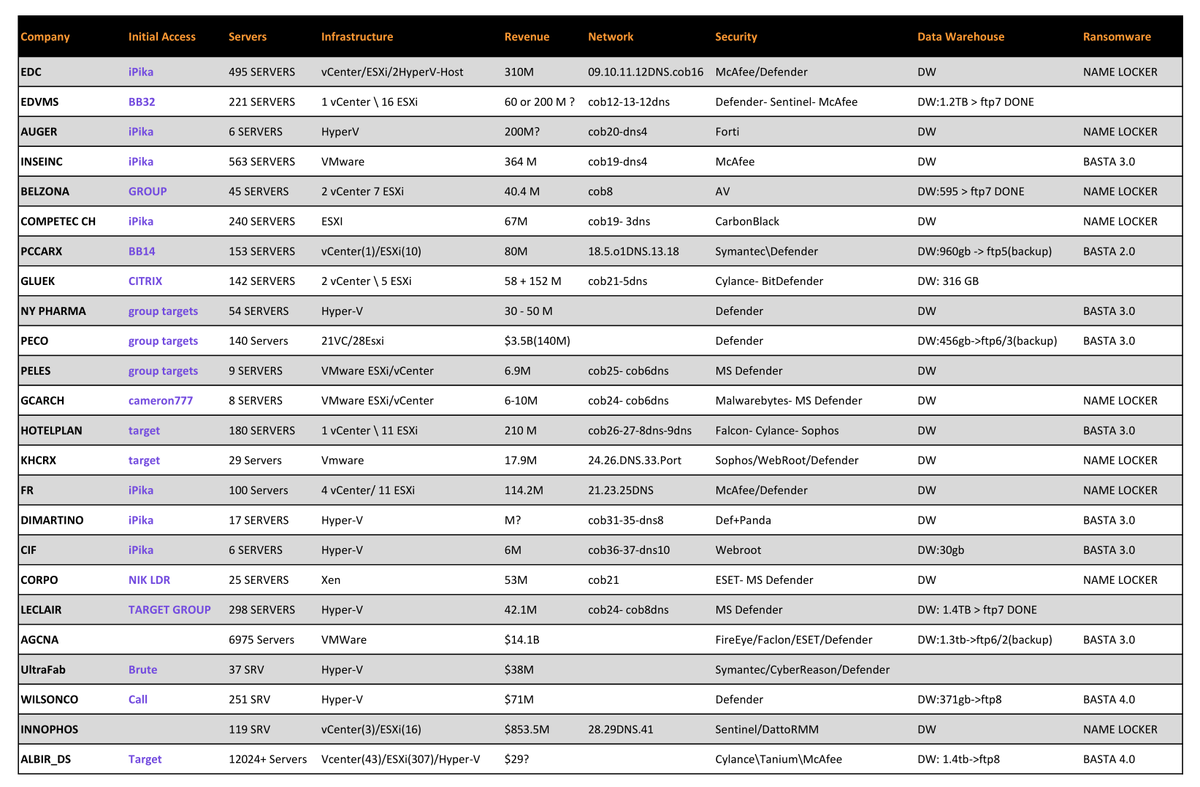
📌 While analyzing the #BlackBasta ransomware leak, I identified a pattern that allowed me to compile a list of organizations that were attacked or compromised between 2023 and 2024.
They documented details such as the initial access vector, which included:
- #Qakbot
- #PikaBot
- NIK LDR (?)
- CITRIX (vulnerabilities)
- Call (social engineering / vishing)
- Brute Force (probably the #BRUTED framework)
- "Cameron777" (IAB) and others.
* #CobaltStrike was also a component that was used in almost all attacks. Let's not forget #IcedID, #DarkGate and #Latrodectus among others.
A worrying and interesting fact is that many of these organizations never made the incident public, which could suggest that they paid the ransom to avoid other repercussions (?) 🤔
All my respect to the community that has always been reporting and warning about each of these malicious campaigns, including the current ones.
[+] https://t.co/PfW9i3cfCf
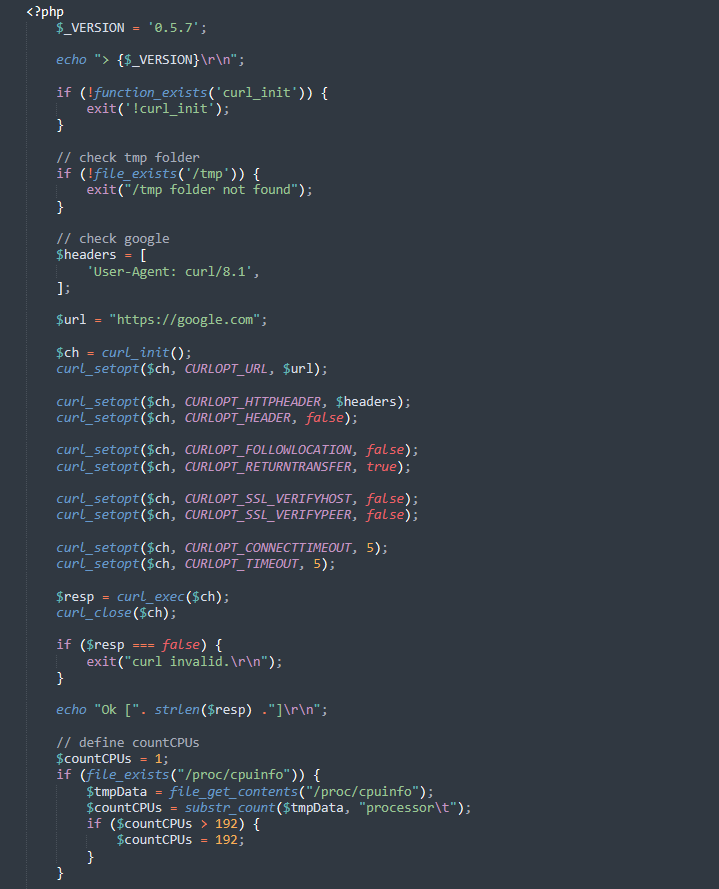
📌 In March 2024 I found a very interesting opendir on IP 2.57.149.237 (mentioned in the EclecticIQ report). An opsec error allowed me to see part of the PHP source code and that's when I realized two things:
1.- It was a tool or framework to perform brute force attacks on VPN devices.
2.- The code had fragments very similar to the PHP proxy scripts used by #TA577 (aka Tramp aka GG) for the distribution of Emotet, Qakbot, Pikabot, etc.
Now, thanks to @EclecticIQ's research, everything fits and I can confirm that what I saw a year ago, was a preliminary or in-development version of #BRUTED. Good work @WhichbufferArda and team! 🦾
/ @Cryptolaemus1


Former Black Basta Members Use Microsoft Teams and Python Scripts in 2025 Attacks https://t.co/qPk3g3tOuw #CyberSecurity #Ransomware #BlackBasta #Phishing #MicrosoftTeams

元Black BastaメンバーがTeamsフィッシング+Python/cURLで金融・建設セクターを攻撃。Quick Assist経由でJava/Python RATとRust SSHローダーを展開。Teamsリンク監視+AnyDesk制限+C2通信用ストレージ監視が急務。#BlackBasta #TeamsPhishing #RAT https://t.co/6w37LanVaq
Black Basta affiliates are now using Teams phishing, email bombing, and Python scripts for persistent network access in 2025 attacks. Threat actors are also leveraging cloud services for command and control. 🚨 #BlackBasta #Python #Japan
https://t.co/7JeZxQnyFy
Hackers Tricking Employees with Fake IT Calls and Email Floods in New Ransomware Scam https://t.co/kzpa79PXpK #BlackBasta #CyberAttacks #GoodSync


Η παραβίαση είναι ανησυχητική, καθώς η ConnectWise παρέχει λογισμικό απομακρυσμένης πρόσβασης και αυτοματοποίησης για εταιρικούς πελάτες, δίνοντας ενδεχομένως στους απατεώνες πρόσβαση σε ένα ευρύ φάσμα εταιρειών. #ConnectWise #BlackBasta
https://t.co/PECYGewJa8

⚠️ Teams, scams & #Ransomware: Inside #BlackBasta’s 2024 #SocialEngineering playbook..
1️⃣ Email bombing ➡️ spoofed helpdesk call
2️⃣ Victim launches Quick Assist
3️⃣ RMM install, M365 creds stolen, data exfil, ransomware 💥
👀 Eye opening breakdown by Partha at #RansomwareSummit

Most Popular Users

Elon Musk 
@elonmusk
240.9M followers

Barack Obama
@barackobama
118.8M followers

Cristiano Ronaldo
@cristiano
114.5M followers

Donald J. Trump
@realdonaldtrump
111.9M followers

Narendra Modi
@narendramodi
107M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.2M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.4M followers

Kim Kardashian
@kimkardashian
70.8M followers

YouTube
@youtube
68.7M followers

Neymar Jr
@neymarjr
66.4M followers

Bill Gates
@billgates
65.2M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.2M followers

CNN
@cnn
61.7M followers

X
@x
60.6M followers