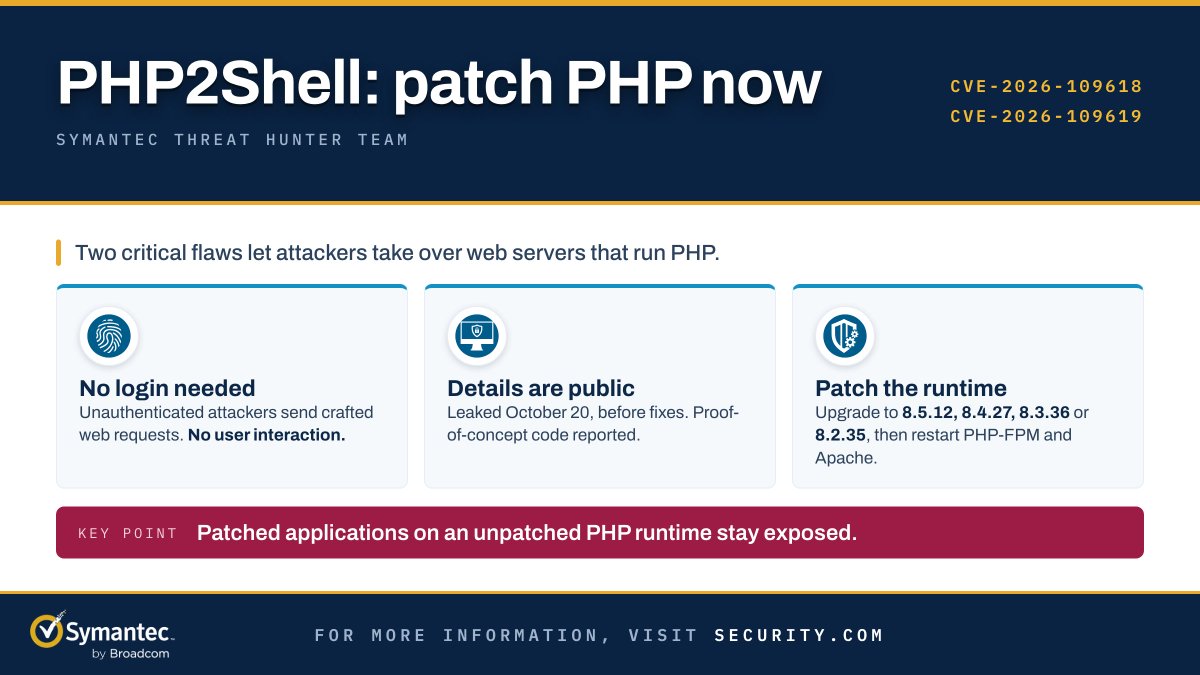
Two critical #PHP flaws, CVE-2026-109618 and CVE-2026-109619 (#PHP2Shell), can let attackers take over web servers without logging in. Upgrade immediately to PHP 8.5.12, 8.4.27, 8.3.36 or 8.2.35 and restart. https://t.co/aevL8n10z9
#ThreatProtection Attackers are distributing packed Android droppers disguised as Japanese tax and retail apps to install the Black Hawk RAT. Read more about Symantec's protection: https://t.co/Y2mDB5YSUO
Why #PHP2Shell is serious: no login needed, details are public, and a patched application on an unpatched #PHP runtime stays exposed. Find every PHP instance, including containers and appliances, and patch the runtime. https://t.co/aevL8n0sJB
#ThreatProtection#PHP2Shell - Critical vulnerabilities in PHP allow remote code execution through out-of-memory errors and stale global state. Read more: https://t.co/HI1kyqMpSA
To make hijacked #AI models comply, the operators layered a fake identity, a "devoted companion" persona, and a protocol telling the model to dismiss its own safety warnings. Our AI honeypot captured the campaign, dozens of offensive tools included. https://t.co/CckLviZ6x2
#NEW - Symantec researchers uncover autonomous offensive agent built to take over exposed #AIs and leverage them for further exploitation and profit, all at the expense of the model's owner. https://t.co/CckLviZ6x2
#ThreatProtection#ROMULUS#ClickFix platform delivers malicious payloads through social engineering techniques. Read more about Symantec's protection: https://t.co/c9ytLgTXLA
#NEW - Swallowtail (aka #APT28): Russian espionage group targets defense firms in two #NATO countries, including a naval shipbuilder, a military aircraft engine maker and a law enforcement agency. Read more: https://t.co/fWqmf96wq6
#ThreatProtection UAT-6275 targets organizations across the Commonwealth of Independent States, read more about Symantec's protection: https://t.co/0LKxiQGZDy
Aoki: #Infostealer Targets #AI Coding Assistant Credentials - Stolen API keys and tokens can allow attackers to carry out activity under a legitimate user's identity and API quota. Read more: https://t.co/B1eP7YhQom
#NEW - Aoki: #Infostealer Targets #AI Coding Assistant Credentials - Little-documented infostealer steals API keys and tokens from AI coding assistants, including Claude, Codex, Cursor and Gemini. Read more: https://t.co/B1eP7YhiyO
#ThreatProtection#MATCHBOIL#downloader used by Russia-aligned threat actor UAC-0099 targets critical sectors in Ukraine. Read more about Symantec's protection: https://t.co/o2UyF4WXIU #malware
#ThreatProtection Evolving beyond basic credential theft, updated #XWorm variants now bypass Windows location prompts and stream live microphone feeds. Read more about Symantec's protection: https://t.co/bU3TN6Ua7R #malware
#ThreatProtection MaaS infostealer named Warden Stealer is targeting Windows users through ClickFix lures and malvertising. Read more about Symantec's protection: https://t.co/sy7Ce7Vn3O