

Top Tweets for #D3FackLoader

An interesting loader that is similar to #D3FackLoader in terms of leveraging Inno Setup's Pascal scripting capabilities to retrieve next stage payloads using an authentication token.
You can hunt for impersonated malicious domains using HOST-BANNER_0_HASH (e36885cbaaf494301ff191f5862f2cb6) provided by awesome folks at @ValidinLLC


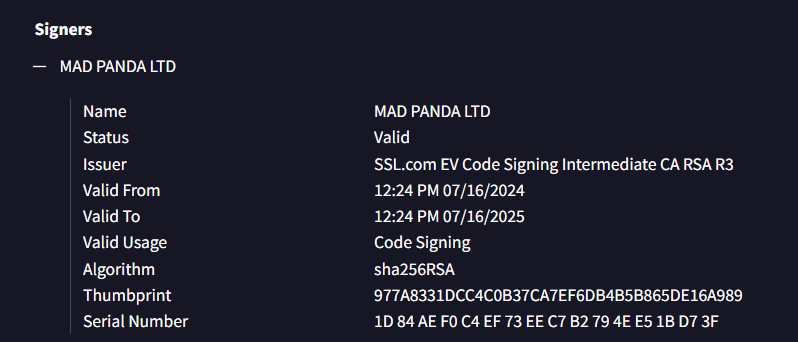
Malicious webpages impersonating legitimate software sites distribute a previously unknown loader. The loader has anti-VM functionality & retrieves payloads through tinyurl[.]com using authentication token and compromised WordPress websites. More info at https://t.co/uSAeH3QDDL
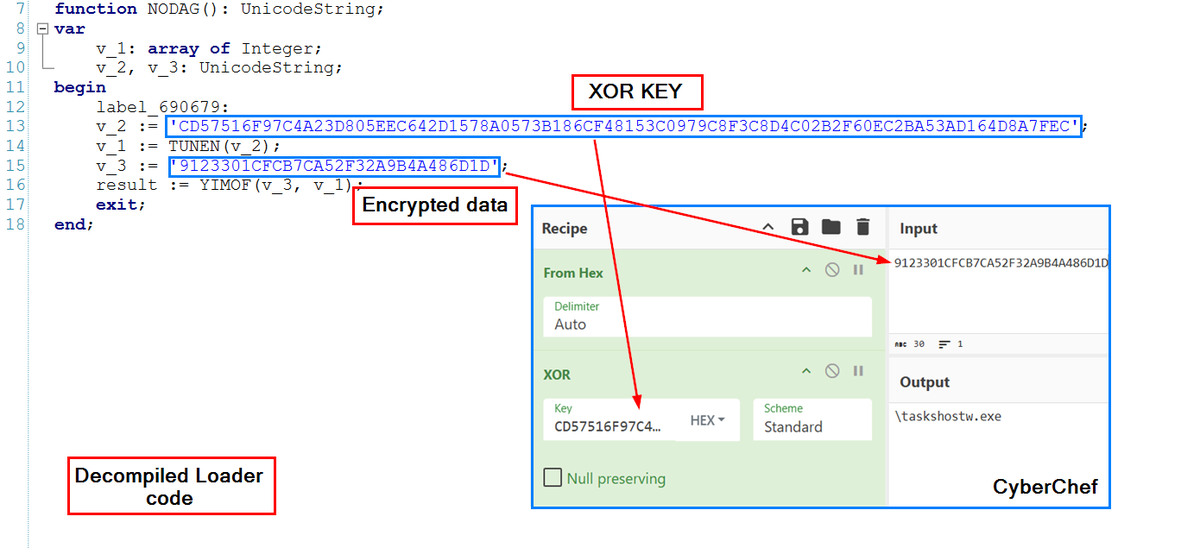


My little piece of work on a MaaS loader, #D3FackLoader 💙 I hope you will enjoy the read.
Link: https://t.co/2cmNdE78P3

It doesn't matter if your payload is FUD or how hard you try to blur out the payload you uploaded to VT. I will still find you and detect you, #D3FackLoader
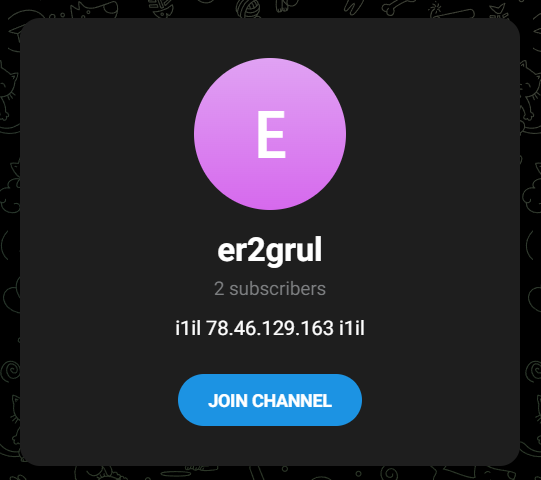
['https://steamcommunity[.]com/profiles/76561199689894251', '\\21[.]txt', '\\21[.]cmd', '\\85[.]zip', '\\855[.]zip', '\\4554[.]cmd', '/manual/225/225[.]zip', 'https://t[.]me/+UfHrjVyCLZ03ODYy', '/manual/225/225']


🦔 📹 New Video: D3fack loader analysis
➡️ Inno Setup pascal script analysis
➡️ string deobfuscation with binary refinery
➡️ JPHP decompilation
Sample was first described by @RussianPanda9xx
https://t.co/J4kB3Lbef2
#MalwareAnalysisForHedgehogs #D3fackLoader
This new loader named d3f@ck has a stage which is JPHP.
Here is how to analyse JPHP
#d3fackloader #d3fack
My little write-up on #D3fackLoader, the lovely MaaS loader from our boy Sergei. Preparing another blog on it, stay tuned 👀
Article: https://t.co/0rfBc5GmgE
@esthreat

Last Seen Hashtags on Sotwe
ensest
Seen from Turkey
MGAI(********)**************** filter:videos
Seen from Turkey
男大
Seen from Japan
ليز
minichat()************+filter:media
Seen from Mexico
creepshot #candid
Seen from United States
minichat((**))*********************************************** filter:native_video
Seen from United States
TheAntiGraham
Seen from Netherlands
TheaterAccessibility
Seen from United States
انجي_الدلوعة
Seen from Egypt
Most Popular Users

Elon Musk 
@elonmusk
241.5M followers

Barack Obama
@barackobama
118.8M followers

Cristiano Ronaldo
@cristiano
114.5M followers

Donald J. Trump
@realdonaldtrump
111.8M followers

Narendra Modi
@narendramodi
107.1M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.3M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.5M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.5M followers

Bill Gates
@billgates
65.3M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.2M followers

CNN
@cnn
61.7M followers

X
@x
60.7M followers