

Top Tweets for #DFIRtip

#DFIRTip if you ever investigate a website breach and all you got is ftp access, you can use this little script to create a basic filesystem timeline using only ftp (https://t.co/HtcihkZr4r). Additionally you can run a web shell scanner like this: https://t.co/Z5fBzhL51U

1/ #DFIRTip: Another example from a real IR case.
We investigated a breached Linux web server where the attackers used https://t.co/YpRUsQdxbT (Impacket Suite) to dump the hashes from the DC (at this point, the TA already had the necessary permissions for this action).
🧵

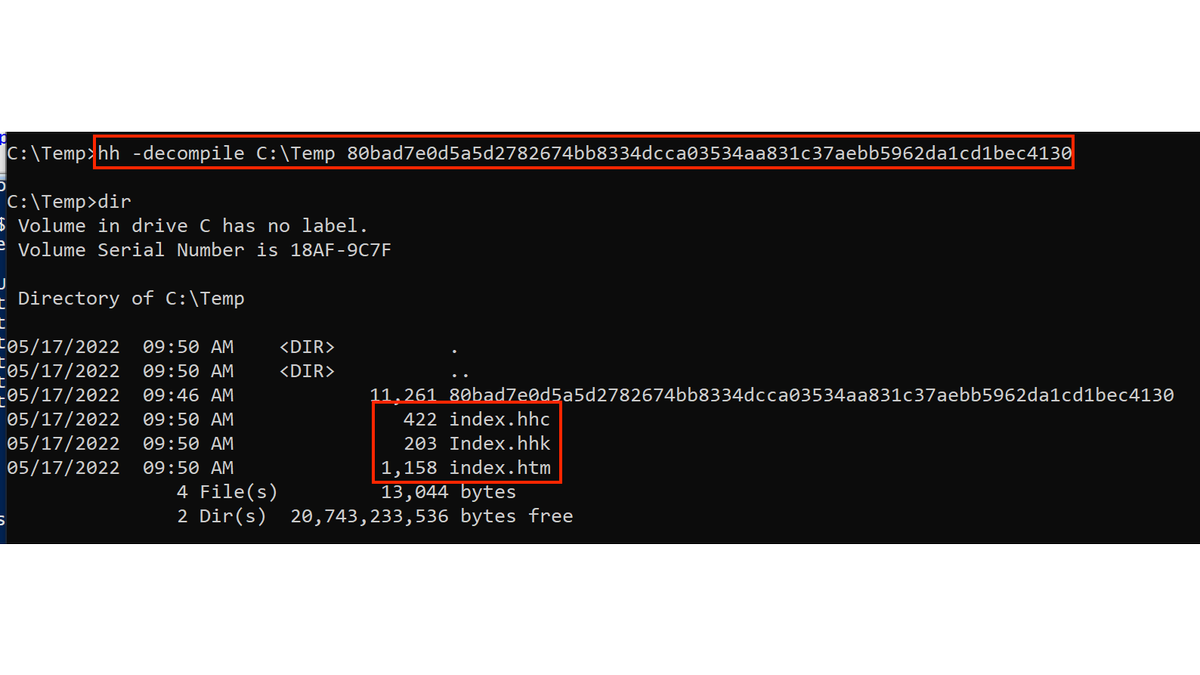
#DFIRTip: A CHM file (Microsoft’s HTML help file format) consists of a number of compiled HTML files.
Decompilation is as easy as
"hh -decompile <Target-Folder> <.chm-file>"

05 Windows Registry - EventLogs | Digital Forensics & Incident Response
الحلقة الخامسة من سلسلة التحقيق الجنائى الرقمى و الاستجابة للحوادث باللغة العربية.
https://t.co/9HcCJbrzis
Slides: https://t.co/Yo8wNWhOw5
#DFIR #dfirtip #امن_المعلومات

A new update was released for Autopsy-RegistryExplorer-plugin. As suggested by @EricRZimmerman , The plugin now supports the analysis of transaction logs thanks to Mr. Eric's tool 'rla.exe'
https://t.co/GXTTN0Z05y
#dfirtip #dfir #cybersecuritytips
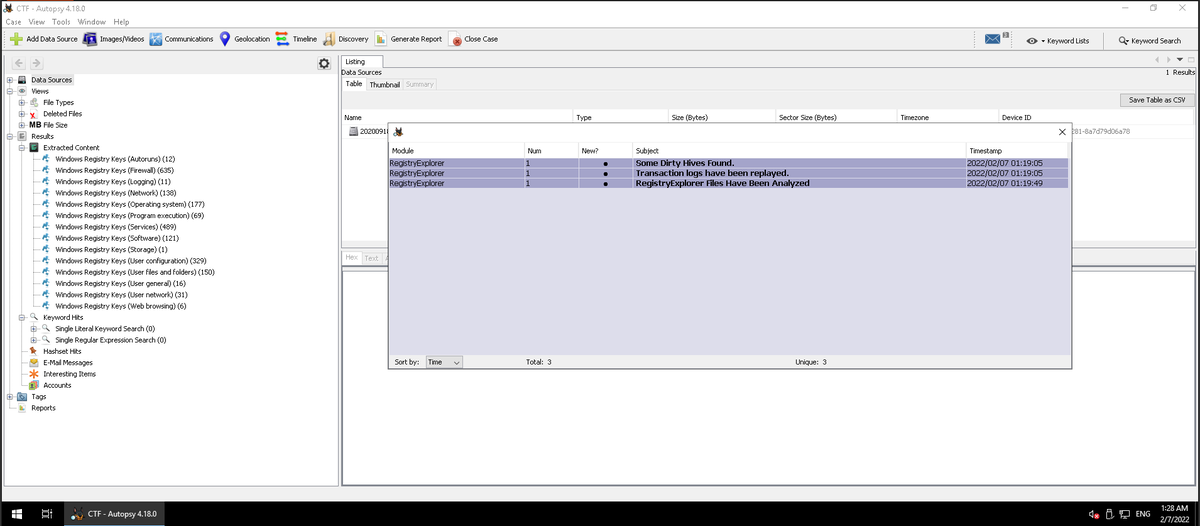
RegistryExplorer: @sleuthkit autopsy module to analyze Registry Hives based on @EricRZimmerman RegistryExplorer's bookmarks
https://t.co/GXTTN0Z05y
Features:
1. Analyze registry hives without loading a full disk image
2. Keys Categorization
#dfirtip #dfirtips #cybersecurity
04 Windows Registry - DFIR | Digital Forensics & Incident Response
الحلقة الرابعة من سلسلة التحقيق الجنائى الرقمى و الاستجابة للحوادث باللغة العربية.
https://t.co/xT67Z5KbxO
#DFIR #dfirtip #امن_المعلومات


#dfirtip #blueteamtips
A friend of mine @yamatosecurity introduced to me his new swiss army knife tool to help us #dfir folks in investigating windows event logs. It was written in PowerShell and can provide tons of stuff + sigma rules integration!
https://t.co/omIDQRJECV
Curious about how #ransomware operators get their overall profit and other shenanigans in the RaaS platform? This research from @NCCGroupInfosec nailed it! https://t.co/RVIkfQVeAy
#dfir #incidentresponse #infosec #dfirtip


#DFIRtip Need to view a location with a different time zone setting on Oxygen Forensic Maps? We have you covered. Set the desired time zone in the Options menu. #DFIR #saferworld

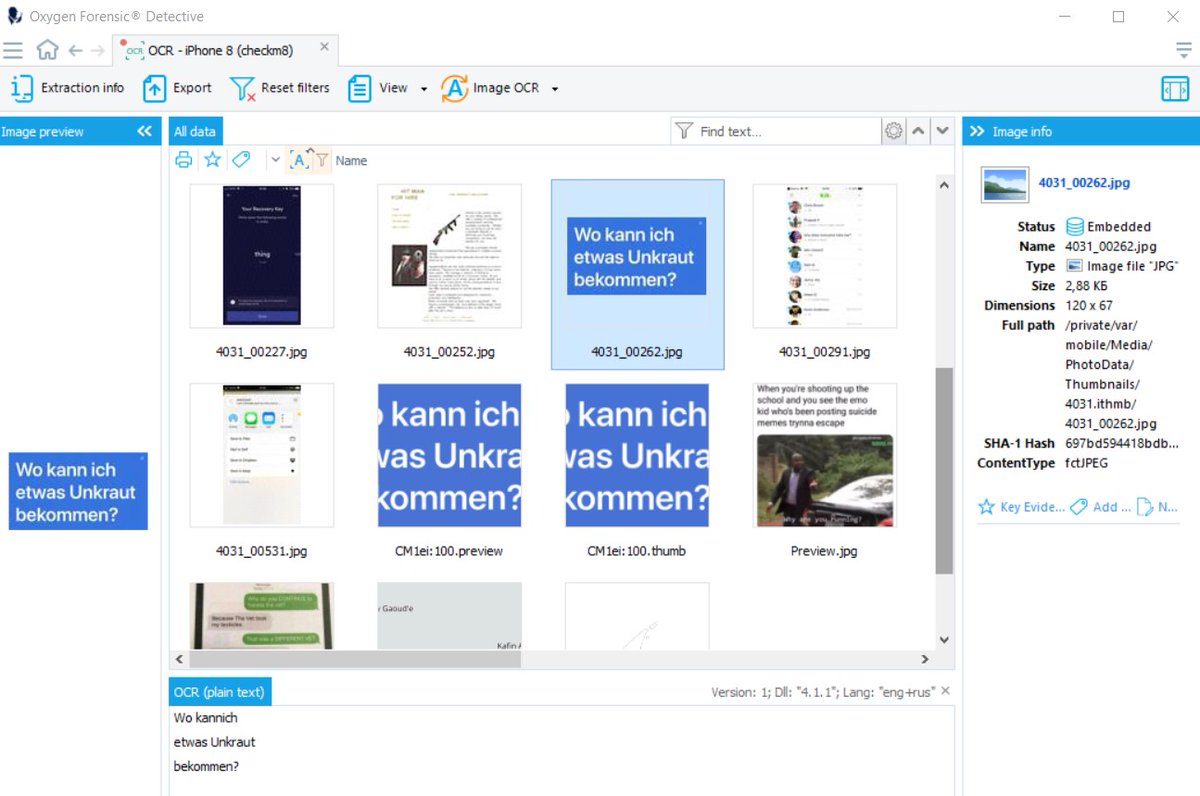
#DFIRtip Did you know that Oxygen Forensic Detective can import and parse over 35 types of backups and images: GrayKey extractions, DAR archives, JTAG images, drone flight logs and images, iTunes, Huawei and Xiaomi backups, Warrant Returns and many others? #DFIR #saferworld



Last Seen Hashtags on Sotwe
nosocialhate
Seen from United States
escolaSalvadorLluch
Seen from United States
minichat
Seen from Japan
ankaraesc
Seen from Turkey
雪羽yuki
Seen from United States
anxiouspanda
Seen from United States
desi #incest
Seen from Spain
ipcam
Seen from United Arab Emirates
nepalikandavideos
vantravesti
Seen from Turkey
Trends for you
Most Popular Users

Elon Musk 
@elonmusk
241.7M followers

Barack Obama
@barackobama
119M followers

Cristiano Ronaldo
@cristiano
114.4M followers

Donald J. Trump
@realdonaldtrump
111.8M followers

Narendra Modi
@narendramodi
107.2M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.4M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
83.9M followers

Lady Gaga
@ladygaga
75.4M followers

Virat Kohli
@imvkohli
73.3M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.3M followers

Bill Gates
@billgates
65.1M followers

Selena Gomez
@selenagomez
63M followers

The Ellen Show
@theellenshow
62.3M followers

CNN
@cnn
61.8M followers

X
@x
60.7M followers