

Top Tweets for #EndToEndEncryption

🔒🚫 End-to-End Encryption Greyed Out? Step by Step Help https://t.co/GjU1bxWfsn #FacebookMessenger #EndToEndEncryption #MessengerEncryption #E2EEncryption


@Meta @WhatsApp @wcathcart — Correction posted.
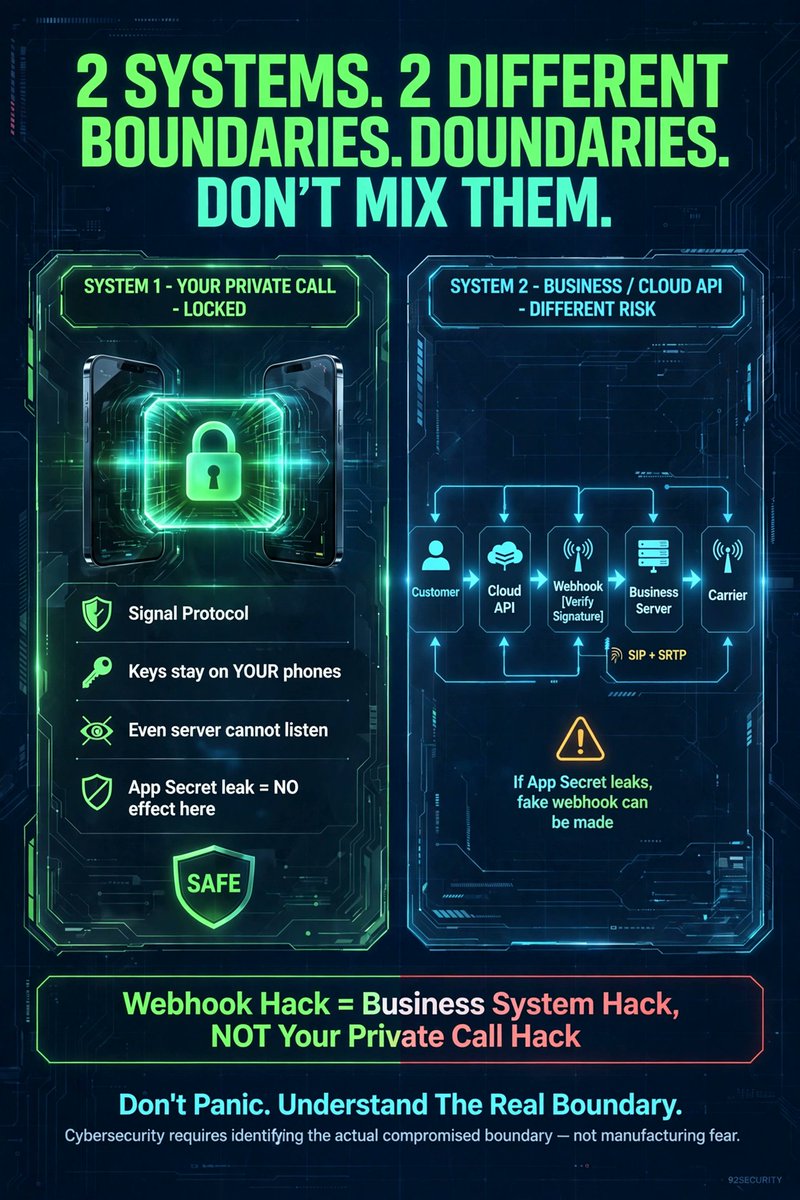
Please review the boundary distinction: Webhook compromise ≠ E2E breach.
TECHINT What/261104
#WhatsAppSecurity #EndToEndEncryption #CyberSecurity
TECHINT | WhatsApp| Webhook | 05 NOV 2026 TRACK ID: What/261104 | CLASSIFICATION: Cybersecurity requires identifying the actual compromised boundary - not manufacturing fear.
Correction to my earlier diagram.
I mixed two systems.
Here is the final corrected version.
92SECURITY | CYBERSECURITY ASSESSMENT
Classification: Conceptual Security Assessment.
Confidence: High for the stated security-boundary
distinctions. Limitation: Not an independent protocol audit or fresh verification of Meta's implementation.
This is a source-based conceptual assessment, not verification of any specific provider deployment.
Scope: WhatsApp Native Calling vs Business Platform / CPaaS.
Focus: Credential compromise, webhook authentication and encryption boundaries.SCOPE
NOTE: The WhatsApp On-Premises Business API reached end of support on 23 October 2025. Meta-hosted Cloud API is now the supported WhatsApp Business Platform messaging API.
Third-party Business Solution Providers may provide additional messaging, orchestration, telephony and media infrastructure; their security boundaries must be assessed separately.
SYSTEM 1 - WhatsApp Native Private Call: This is the free voice/video call for consumers.
It is a separate consumer product and security domain from the Business Platform / CPaaS integrations discussed in
System 2. This distinction does not assert the native calling transport implementation.
Under Meta's documented model, native consumer voice/video calls use end-to-end encryption under the Signal protocol between the participants' devices, with device-generated SRTP master secrets via end-to-end encrypted signalling.
Its media is end-to-end encrypted and the server / relay is not intended to have access to decrypted call content.
I am NOT asserting the exact internal call-key establishment, codec, or transport details as independently verified from authoritative protocol documentation.
The key security distinction is the boundary: Compromise of a Meta App Secret, Business Platform access token, or webhook endpoint does NOT, by itself, compromise the end-to-end encryption of a native WhatsApp call.
Merely opening a random link does not, by itself, break end-to-end encryption.
A phishing link can trick a user into typing a password / OTP, approving a malicious device link, granting permissions, or disclosing session information - but that is user / endpoint compromise, not a break of end-to-end encryption itself.
SYSTEM 2 - WhatsApp Business Platform / CPaaS: Webhooks and API tokens are used in Business Platform integrations. SIP may be present in provider-specific Business Calling / CPaaS deployments.
Cloud API manages encryption keys on behalf of the business and decrypts incoming messages before forwarding; WhatsApp does not treat those business-side communications as end-to-end encrypted in the same sense as native calls.
Meta App Secret compromise is a genuine security risk.
Clarification: Do NOT call the App Secret a dedicated "webhook secret." It is the Meta App Secret used for webhook signature verification.
Meta App Secret compromise = an attacker can generate valid HMAC signatures for attacker-crafted webhook payloads, potentially defeating the receiver's signature-based authenticity checks.
Verification Token = only for subscription challenge, not for authenticating POST events.
Access Token = only for API operations allowed by its permissions.
Flow: Customer -> Meta WhatsApp Cloud API -> HTTPS Webhook + Verify the X-Hub-Signature-256 header against the raw request body with constant-time comparison using App Secret, HMAC-SHA256 of the raw body + Secrets in Secrets Manager, never in .env / Git / Logs -> Business Orchestration (Routing, IVR, Queue) -> [Possible provider-specific Business Calling path]
If Business Calling enabled: Media Gateway -> SIP over TLS + SRTP -> Carrier (Twilio / Vonage / 8x8) -> Agent Desktop.
Note: HMAC validates authenticity and integrity, it does NOT encrypt webhook contents.
Transport relies on HTTPS.
A valid HMAC signature proves only that the payload was signed using the relevant secret.
It does NOT prove that the event is genuine, fresh, unique or authorized.
Receivers should also implement replay protection, event deduplication, and application-level validation.
72h key rotation and per-request token rotation are recommended practices in certain CPaaS environments.
Their suitability depends on the provider and integration.
They are NOT universal Meta requirements.
Business Calling integrations and their precise architecture should be assessed against the relevant provider documentation.Conclusion: Webhook compromise is an infrastructure-security incident.
It is not evidence of a WhatsApp end-to-end encryption breach.
Token theft is not Signal compromise.
Backend compromise is not automatic access to every user's private conversation.
Cybersecurity requires identifying the actual compromised boundary - not manufacturing fear.
#WhatsAppSecurity #EndToEndEncryption #CyberSecurity


Your DMs on UpScrolled are now end-to-end encrypted. Who's the first person you're messaging?
#UpScrolled #Privacy #CommunityFirst #EndToEndEncryption
‼️HUGE ANNOUNCEMENT‼️
End-to-end encrypted messaging is officially here at UpScrolled! 🚀🙌
Your privacy matters, and we are committed to it at UpScrolled.
Download the latest version of UpScrolled from the App Store and check it out!
#UpScrolled #EndToEndEncryption #Privacy

Arattai में Group Chats के लिए End-to-End Encryption आ गया! 🔒
नए ग्रुप में तुरत मिलेगा, पुराने ग्रुप्स में भी धीरे-धीरे रोलआउट होगा। अब ग्रुप चैट्स भी पूरी तरह प्राइवेट!
पूरा अपडेट जानिए 👇
https://t.co/jLOaYkg3D2
#Arattai #EndToEndEncryption #kpgtechnews
@Arattai Arattai में Group Chats के लिए End-to-End Encryption आ गया! 🔒
नए ग्रुप में तुरत मिलेगा, पुराने ग्रुप्स में भी धीरे-धीरे रोलआउट होगा। अब ग्रुप चैट्स भी पूरी तरह प्राइवेट!
पूरा अपडेट जानिए 👇
https://t.co/jLOaYkg3D2
#Arattai #EndToEndEncryption #kpgtechnews

ఇక సరికొత్తగా వాట్సాప్.. ఆండ్రాయిడ్ యూజర్లకు క్రేజీ ఫీచర్
#WhatsApp #WhatsAppUpdate #AndroidUsers #AIAgents #ThirdPartyAI #OpenAI #WhatsAppAI #PrivacyPolicy #TechNews #Meta #EndToEndEncryption #WhatsAppBeta
@WhatsApp @Meta
https://t.co/RfumWvvLrN

2/5: The fight relates to Advanced Data Protection - encryption so secure even Apple can't access it. Apple pulled the service from UK customers in Feb 2025 rather than create backdoors. #DataProtection #Cybersecurity #EndToEndEncryption

link to full blogpost:
https://t.co/bEHMhwT7gM
#EndToEndEncryption #Section230 #censorship #surveillance

Why Privacy-Conscious Users Should Think Twice Before Storing Sensitive Files on Google Drive https://t.co/XgRSxfTiDQ #cloudstoragesecurity #EndtoEndEncryption #GoogleDriveencryption


Privacy isn't just about where your notes are stored - it's about who can access them. With Joplin's End-to-End Encryption, your notes remain protected from unauthorized access, giving you full control over your data.
#Joplin #EndToEndEncryption #DigitalPrivacy #OpenSource


WhatsApp Encryption Comes Under Spotlight Following Federal Allegations https://t.co/oEuthOHYzP #cybersecuritynews #digitalsurveillance #EndToEndEncryption


ఐఫోన్ To ఆండ్రాయిడ్ మెసేజ్లకు
ఎండ్ టు ఎండ్ ఎన్క్రిప్షన్
#etvdigital #apple #google #EndToEndEncryption


So... can WhatsApp suddenly read your chats now?
A lot of people are confused about the new privacy claims online. Watch this to know what’s actually going on.
Video: @efeemena
#WhatsApp #Privacy
#EndToEndEncryption #factcheck

Google, Apple bring end-to-end encryption to RCS messaging
https://t.co/pe8hTiMM95
#Google #Apple #RCSMessaging #EndToEndEncryption #TechNews #iOS #Android #Privacy #MessagingApps #CyberSecurity
@Google @Apple

ఇన్స్టాగ్రామ్ చాటింగ్ల
ఎండ్ టూ ఎండ్ ఎన్క్రిప్షన్కు ఎండ్కార్డ్
#Instagram #EndToEndEncryption #etvdigital

ఇన్స్టాగ్రామ్ చాటింగ్ల
ఎండ్ టూ ఎండ్ ఎన్క్రిప్షన్కు ఎండ్కార్డ్
#Instagram #EndToEndEncryption #etvdigital


Instagram ने हटवलं End-to-End एन्क्रिप्शन; तुमचे पर्सनल चॅट वाचू शकणार कंपनी, हॅकर्ससाठी मार्ग मोकळा
#instagram #latestupdates #endtoendencryption #sakalnews
https://t.co/Q9oOiNCt7I

Meta has rolled back end-to-end encryption for Instagram direct messages, allowing access to message content, images, videos and voice notes, a move praised by child safety groups but criticized by privacy advocates.
#Meta #Instagram #Privacy #EndToEndEncryption #CyberSecurity #SocialMedia #PakistanTV

Last Seen Hashtags on Sotwe
Trends for you
Most Popular Users

Elon Musk 
@elonmusk
241M followers

Barack Obama
@barackobama
118.8M followers

Cristiano Ronaldo
@cristiano
114.5M followers

Donald J. Trump
@realdonaldtrump
111.9M followers

Narendra Modi
@narendramodi
107M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.2M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.4M followers

Kim Kardashian
@kimkardashian
70.8M followers

YouTube
@youtube
68.7M followers

Neymar Jr
@neymarjr
66.4M followers

Bill Gates
@billgates
65.2M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.2M followers

CNN
@cnn
61.7M followers

X
@x
60.6M followers