Top Tweets for #MALicious
Lost your #votingright in the #SIRprocess , get back your vote by filling #form6 or if you are a victim of #malicious #form7 deletion, reply to notice.
It's simpler now after the agitation by #GenZ and @RahulGandhi petition in #SupremeCourt.
#gyaneshkumar has become softer https://t.co/PdsmyRI4Wk
#Trump officials scrutinized #Omar in 2019. They didn’t find #citizenship issues. - @washingtonpost
“[@IlhanMN] is now facing an #inquiry over some of the same #allegations #investigators previously deemed not worth pursuing.”
#Malicious #prosecution!
https://t.co/LeLiSFhlG4.
First sample of Ledger Nano X arrived clean... now waiting for the next one incoming from #MediaWorld #MediaMarkt 🤞🏻🙈🙉🙊
In case you wonder how to check yours for #Malicious #Hardware #Implants👇
#HardwareForsensics #CertifiedHardwareHacker
Free crypto DMs are never free. 🎣 If it sounds too good to be true, it’s bait. Slow down, check the sender, and don’t click.
#Web3 #Crypto #Malicious #CyberSecurity

#Stop #visiting #shady #converter #sites #packed with #malicious #popups 🚫💻
#Get 200+ #blazing-fast #calculators, #encoders & #file #utilities on #Cloudflare #Workers for $1 #lifetime:
https://t.co/LzqqQanjzH
#ToolMint #WebDev #BuildInPublic #IndieDev
#LibreOffice and #OpenOffice #Flaws Let #Malicious #Spreadsheets Run #Code Without #Macro #Warnings https://t.co/zWCelQowvp
Brilliant! 🏆 "Good or #Selfless actions
generate positive results (good karma);
harmful or #malicious actions generate
#Negative results (BAD karma)! When
he stuffs up, always 'blames' others and
takes NO #responsibility! 😡 Agree? 🙋♂️
🎯Cr @lvhothead2483 ⤵️ #VoteBlue 💙

Host: redsun[.]live
Read the full report, with the loader chain and indicators (free signup) 👇
https://t.co/GiRKAoJsKs
Thanks @malwrhunterteam for the find: https://t.co/zBumMo8yQl
#malicious #opendir
Opendir: https://redsun[.]live/
🤷♂️
![malwrhunterteam's tweet photo. Opendir: https://redsun[.]live/
🤷♂️ https://t.co/rKbnlAUP8L](https://pbs.twimg.com/media/HUGMGp7XUAAGWg5.png)
@AshutoshRanka @deepakbaliyan90 @PoliceRajasthan Who will take responsibility for these #malicious and #lies spread about assault by @abhijeet_dipke #CJP?? @PoliceRajasthan @RajCMO @jawaharbedam Please take cognizance of these posts!!

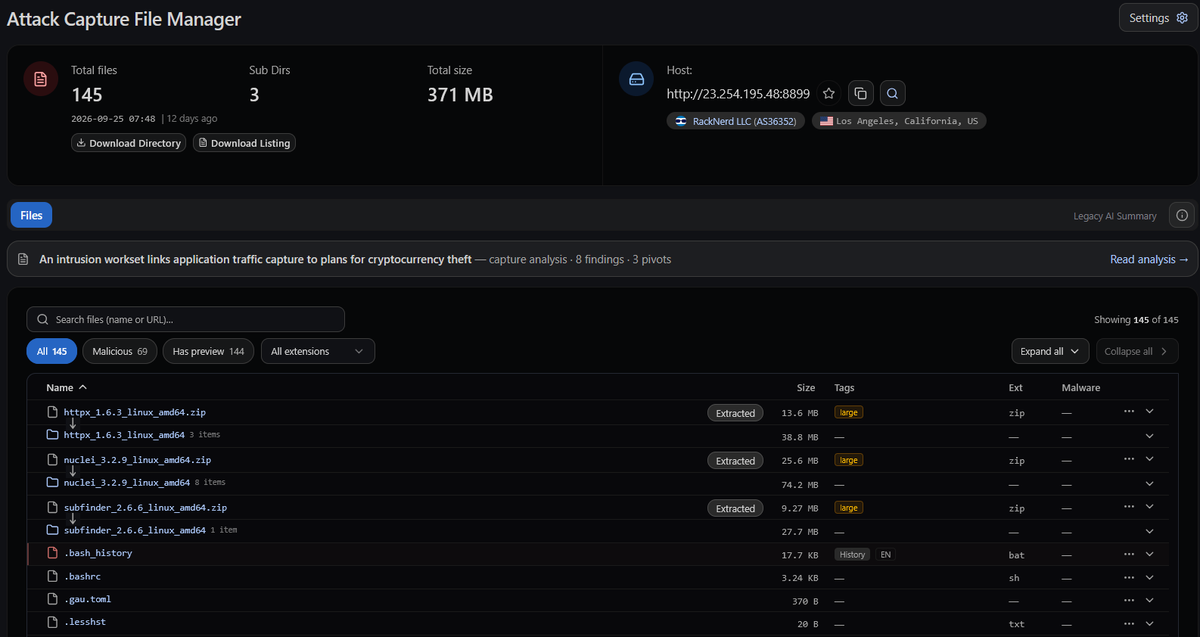
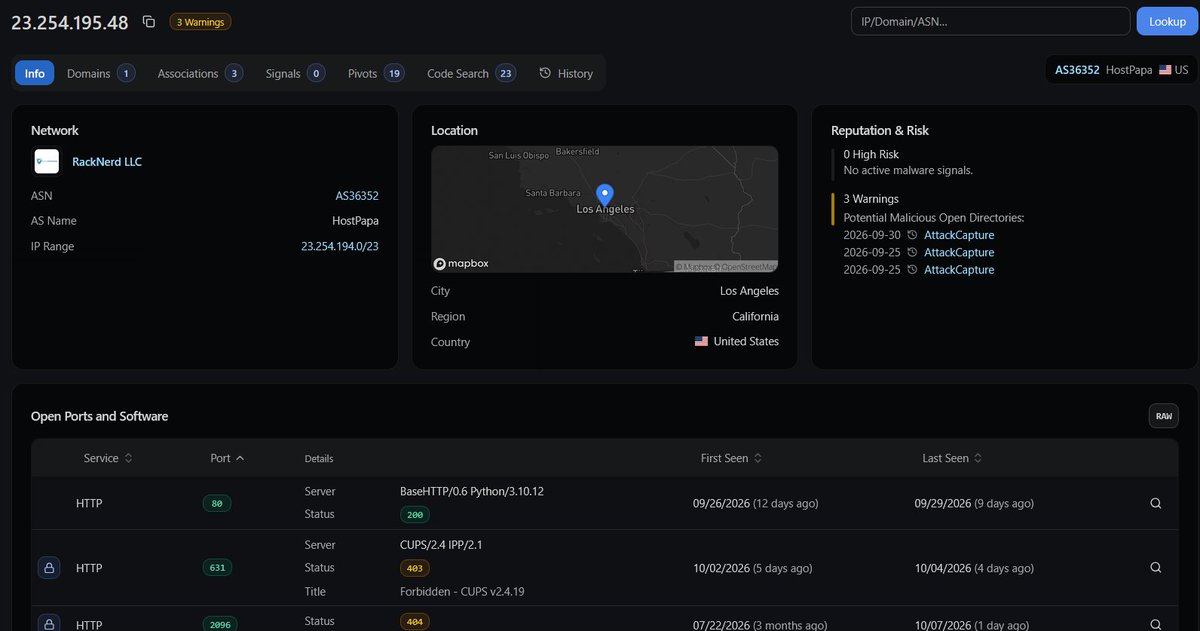
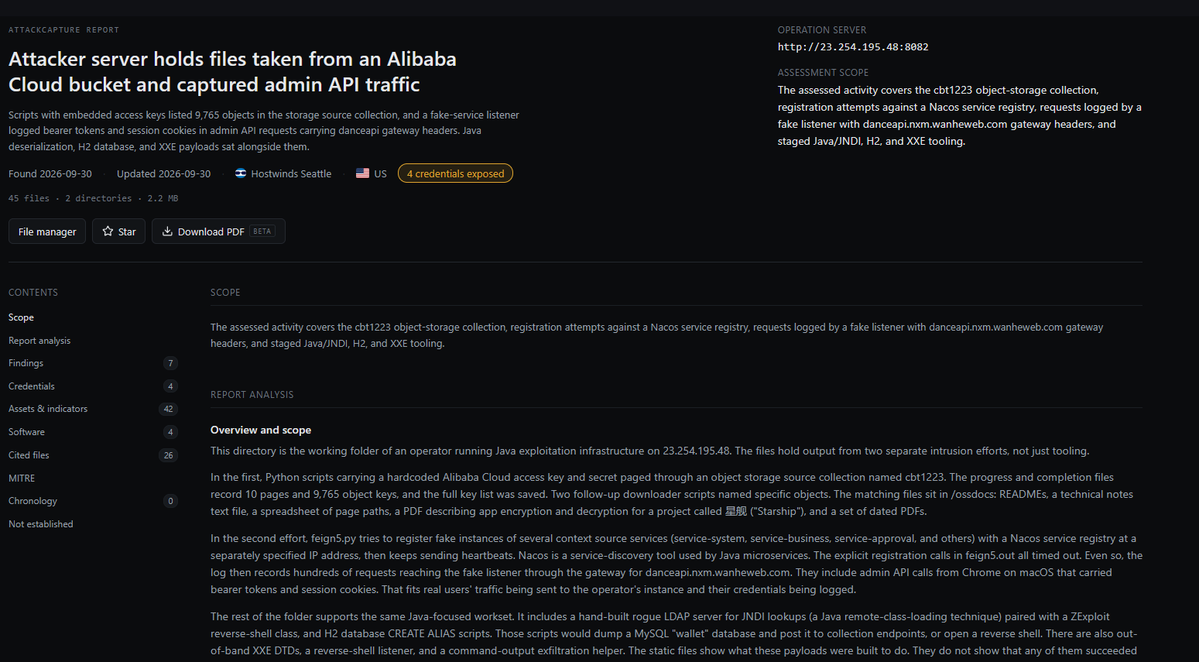
⚠️ #malicious #opendir on 23.254.195[.]48
AttackCapture URL: https://t.co/DijpevaumH
Found by @BlinkzSec https://t.co/6wTVepx6if
https://t.co/aojFWxKETZ shows three opendir on 23.254.195[.]48 (RackNerd/HostPapa)
:8082 https://t.co/NVZSf0pAmC
- Alibaba OSS bucket enumerated (9,765 keys pulled), jndi/ldap rogue server staged with a reverse shell class, h2 scripts built to dump a MySQL "wallet" db, fake nacos listener logging real bearer tokens and cookies.
:8099 https://t.co/o0g0dddsDT
- Custom Go beacon compiled for Linux and Windows, full remote access kit (shell, file transfer, screenshots, socks5, persistence, self-delete), checks in to:8443
:8899 https://t.co/390BzMKnpm
- Same fake listener grabbing creds, operator notes claiming nacos access tied to a Chenzhou tourism target, wallet theft scripts (dump/decrypt/sweep), 3 cracked SSH passwords, beacon served 18 times
![Huntio's tweet photo. ⚠️ #malicious #opendir on 23.254.195[.]48
AttackCapture URL: https://t.co/DijpevaumH
Found by @BlinkzSec https://t.co/6wTVepx6if
https://t.co/aojFWxKETZ shows three opendir on 23.254.195[.]48 (RackNerd/HostPapa)
:8082 https://t.co/NVZSf0pAmC
- Alibaba OSS bucket enumerated (9,765 keys pulled), jndi/ldap rogue server staged with a reverse shell class, h2 scripts built to dump a MySQL "wallet" db, fake nacos listener logging real bearer tokens and cookies.
:8099 https://t.co/o0g0dddsDT
- Custom Go beacon compiled for Linux and Windows, full remote access kit (shell, file transfer, screenshots, socks5, persistence, self-delete), checks in to:8443
:8899 https://t.co/390BzMKnpm
- Same fake listener grabbing creds, operator notes claiming nacos access tied to a Chenzhou tourism target, wallet theft scripts (dump/decrypt/sweep), 3 cracked SSH passwords, beacon served 18 times](https://pbs.twimg.com/media/HUHaL3jW0AAeCkv.png)
found by drewfink👇
https://t.co/Q9SOKdxqJC

TRIUMPH - A Destiny 2 PK titan burgertage/edit
GR2H guardians! Kill your local final warning user!
#EVIL #GR2H #DIDDY #MALICIOUS #Destiny2
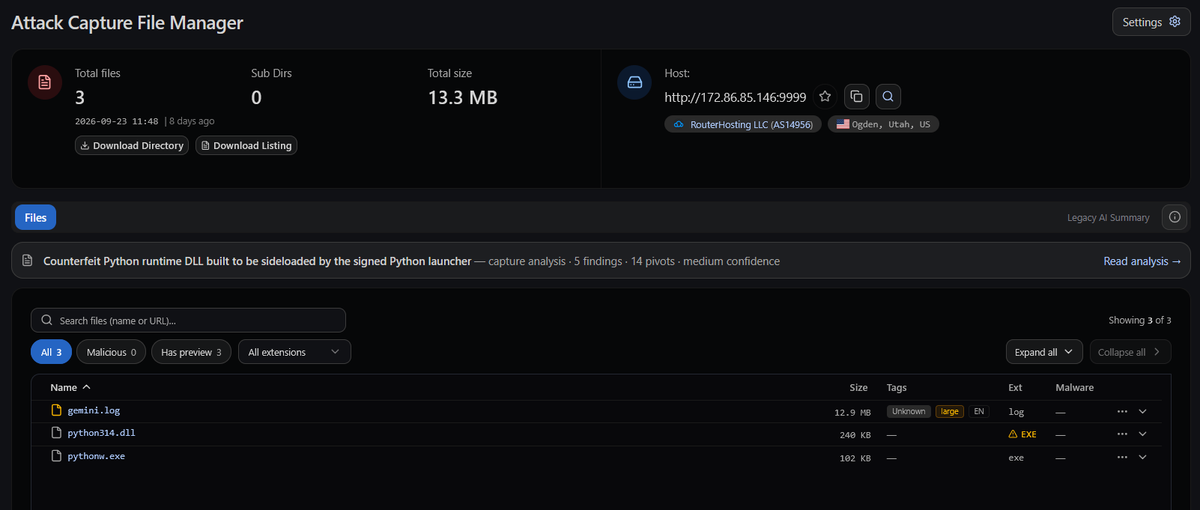
⚠️ #malicious #opendir hosted at 172.86.85.146[:]9999
AttackCapture URL: https://t.co/q7UL6QDZEs
Found by @malwrhunterteam https://t.co/hTBXBiorsp
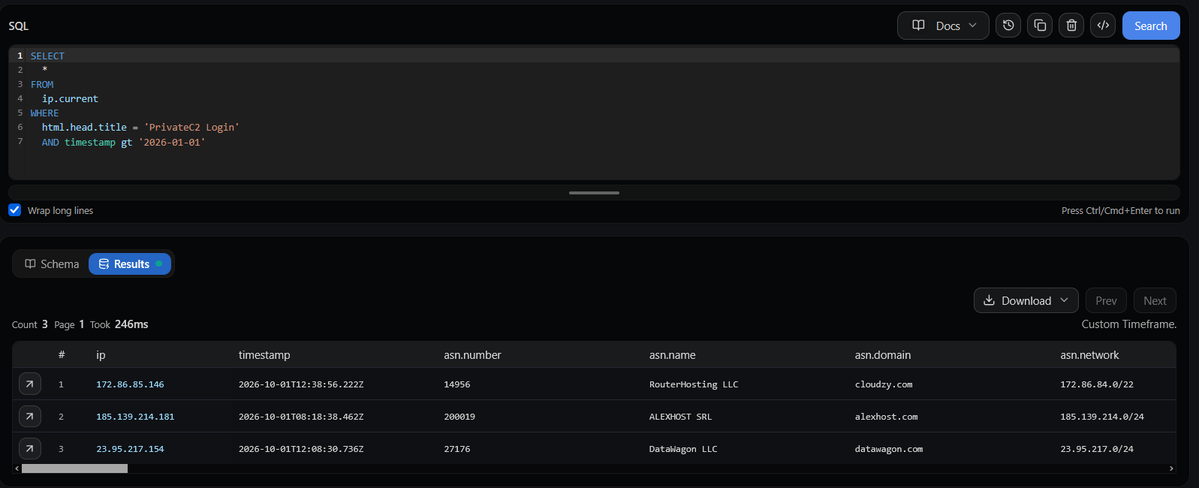
1/ Flagged via AttackCapture: 172.86.85[.]146 (RouterHosting LLC / cloudzy[.]com, AS14956, Ogden, UT) runs a "PrivateC2 Login" panel on :5173 and an exposed n8n workflow-automation instance on :5678.
2/ An open dir on :9999 (nginx/1.24.0) holds pythonw.exe + python314.dll (a PyInstaller runtime pair) plus a 12.9MB gemini.log that's pure high-entropy binary - not a readable log, likely a packed/encrypted payload.
3/ HuntSQL pivot on html.head.title = 'PrivateC2 Login' since Jan 2026 turns up 2 more hosts running the same panel:
• 185.139.214[.]181 (ALEXHOST SRL) - plain HTTP, no MFA, basic build
• 23.95.217[.]154 (DataWagon LLC) - a Windows box (RDP :3389, SMB :445) running a newer build with MFA + SSO/OIDC login
4/ Same C2 panel, 3 hosts, 3 different providers, and a visibly iterating codebase.
![Huntio's tweet photo. ⚠️ #malicious #opendir hosted at 172.86.85.146[:]9999
AttackCapture URL: https://t.co/q7UL6QDZEs
Found by @malwrhunterteam https://t.co/hTBXBiorsp
1/ Flagged via AttackCapture: 172.86.85[.]146 (RouterHosting LLC / cloudzy[.]com, AS14956, Ogden, UT) runs a "PrivateC2 Login" panel on :5173 and an exposed n8n workflow-automation instance on :5678.
2/ An open dir on :9999 (nginx/1.24.0) holds pythonw.exe + python314.dll (a PyInstaller runtime pair) plus a 12.9MB gemini.log that's pure high-entropy binary - not a readable log, likely a packed/encrypted payload.
3/ HuntSQL pivot on html.head.title = 'PrivateC2 Login' since Jan 2026 turns up 2 more hosts running the same panel:
• 185.139.214[.]181 (ALEXHOST SRL) - plain HTTP, no MFA, basic build
• 23.95.217[.]154 (DataWagon LLC) - a Windows box (RDP :3389, SMB :445) running a newer build with MFA + SSO/OIDC login
4/ Same C2 panel, 3 hosts, 3 different providers, and a visibly iterating codebase.](https://pbs.twimg.com/media/HTj9kyTXcAAZyoZ.png)
Some opendir: http://172.86.85[.]146:9999/
🤔
🤷♂️
![malwrhunterteam's tweet photo. Some opendir: http://172.86.85[.]146:9999/
🤔
🤷♂️ https://t.co/0eT1eR6Ll0](https://pbs.twimg.com/media/HSwcq9bWgAAAKJo.png)
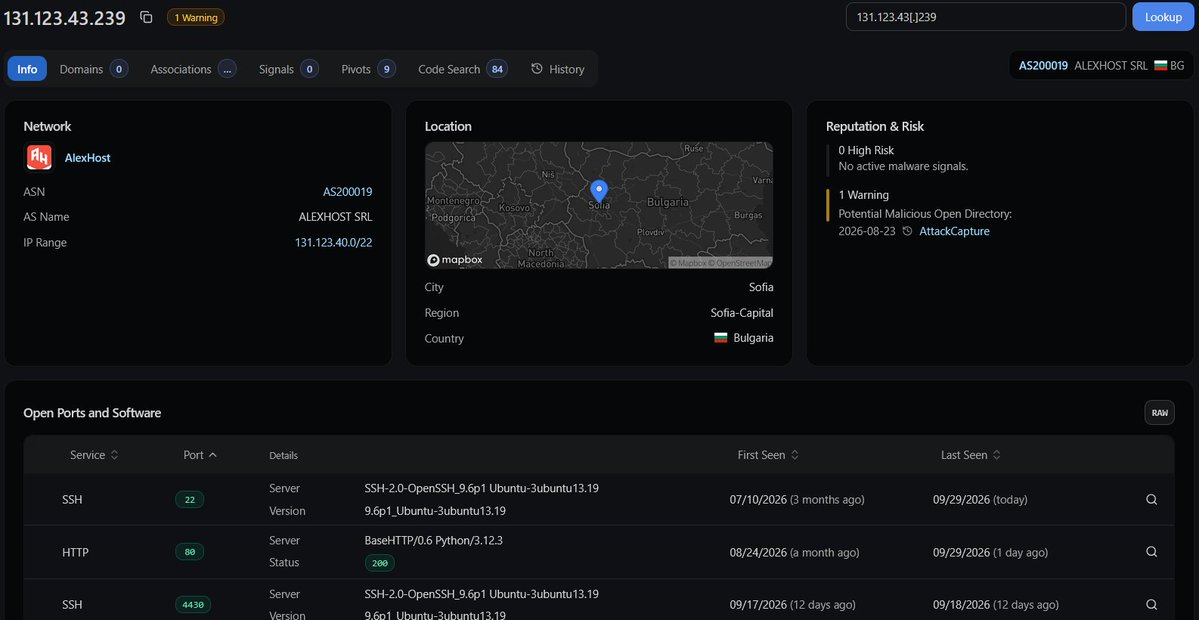
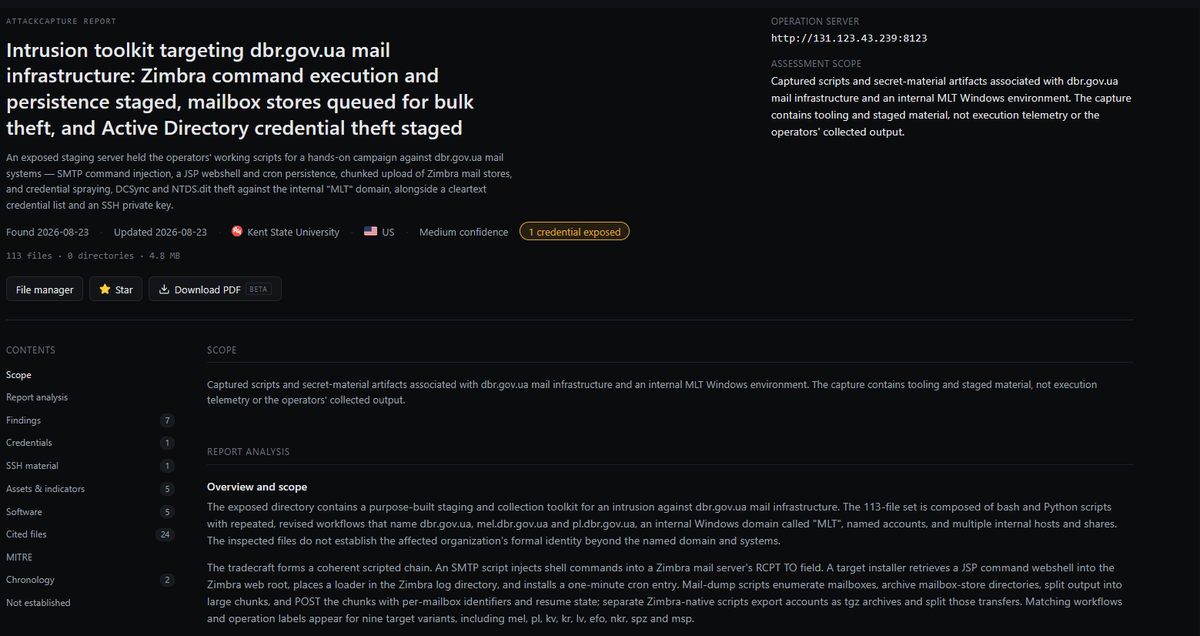
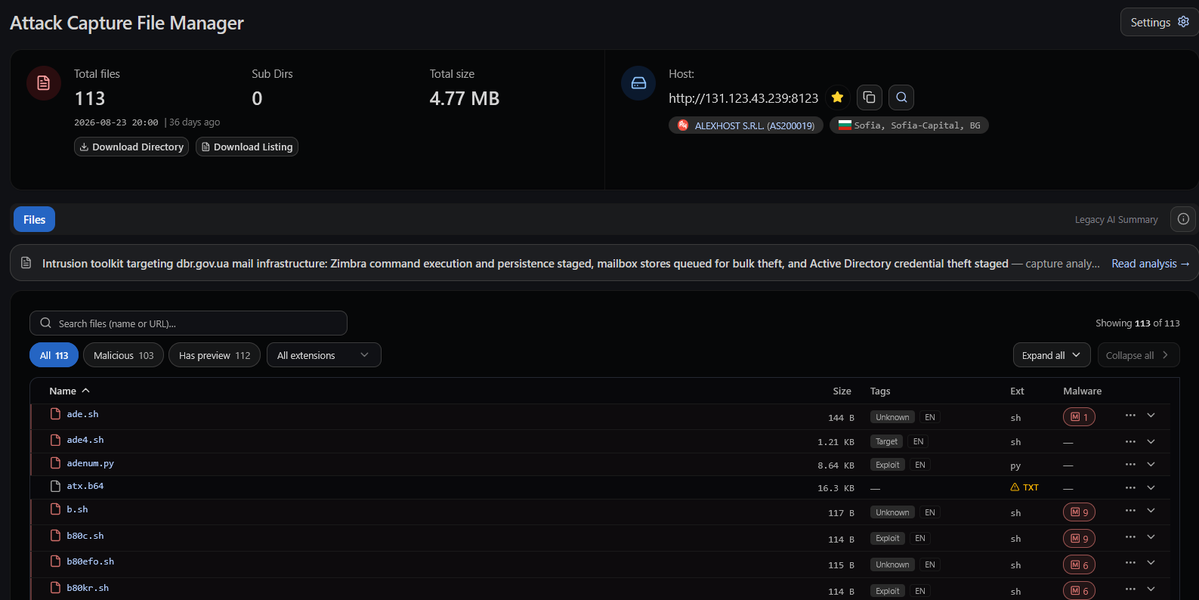
👿 #malicious #opendir hosted on 131.123.43.239[:]8123
AttackCapture URL: https://t.co/3msozYgsoQ
Found by @malwrhunterteam https://t.co/P2bOLFiKaP
This open dir is hosted at AlexHost SRL (AS200019), Sofia BG. Captured 2026-08-23, 113 files / 4.8MB, 103 tagged malicious.
What we found:
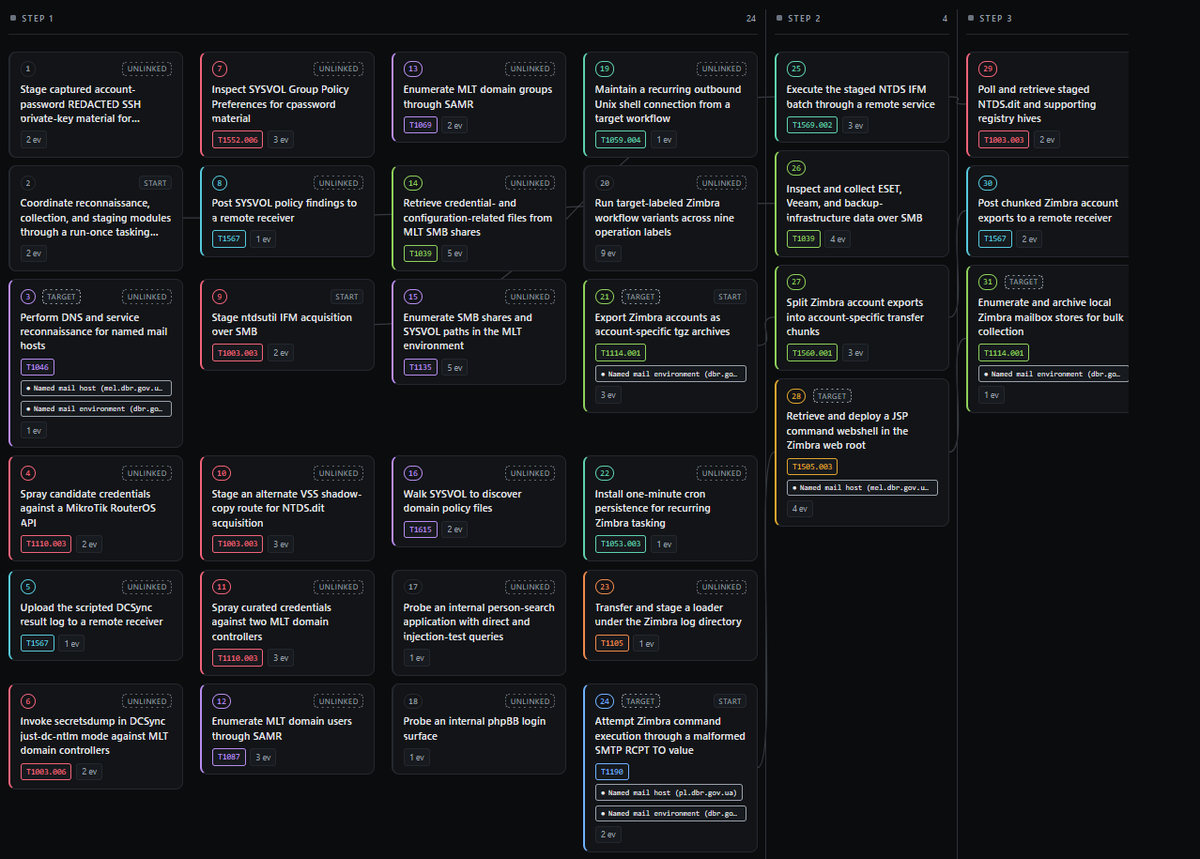
- Staging server for a hands-on campaign against dbr[.]gov[.]ua Zimbra mail infrastructure
-SMTP RCPT TO command injection + JSP webshell drop + 1-min cron persistence scripted out
- Two resumable mailbox dump workflows (zmmailbox tgz export + raw store archive), chunked POST exfil, 9 target variants (mel, pl, kv, kr, lv, efo, nkr, spz, msp)
- MLT Windows domain: credential spray, SAMR/SMB enum, SYSVOL/GPP hunt, DCSync + ntdsutil IFM + VSS shadow copy all staged for NTDS.dit
- 69-line cleartext cred list and an SSH private key just sitting in the dir alongside the tooling
![Huntio's tweet photo. 👿 #malicious #opendir hosted on 131.123.43.239[:]8123
AttackCapture URL: https://t.co/3msozYgsoQ
Found by @malwrhunterteam https://t.co/P2bOLFiKaP
This open dir is hosted at AlexHost SRL (AS200019), Sofia BG. Captured 2026-08-23, 113 files / 4.8MB, 103 tagged malicious.
What we found:
- Staging server for a hands-on campaign against dbr[.]gov[.]ua Zimbra mail infrastructure
-SMTP RCPT TO command injection + JSP webshell drop + 1-min cron persistence scripted out
- Two resumable mailbox dump workflows (zmmailbox tgz export + raw store archive), chunked POST exfil, 9 target variants (mel, pl, kv, kr, lv, efo, nkr, spz, msp)
- MLT Windows domain: credential spray, SAMR/SMB enum, SYSVOL/GPP hunt, DCSync + ntdsutil IFM + VSS shadow copy all staged for NTDS.dit
- 69-line cleartext cred list and an SSH private key just sitting in the dir alongside the tooling](https://pbs.twimg.com/media/HTeoSsjWUAA9Bbg.png)
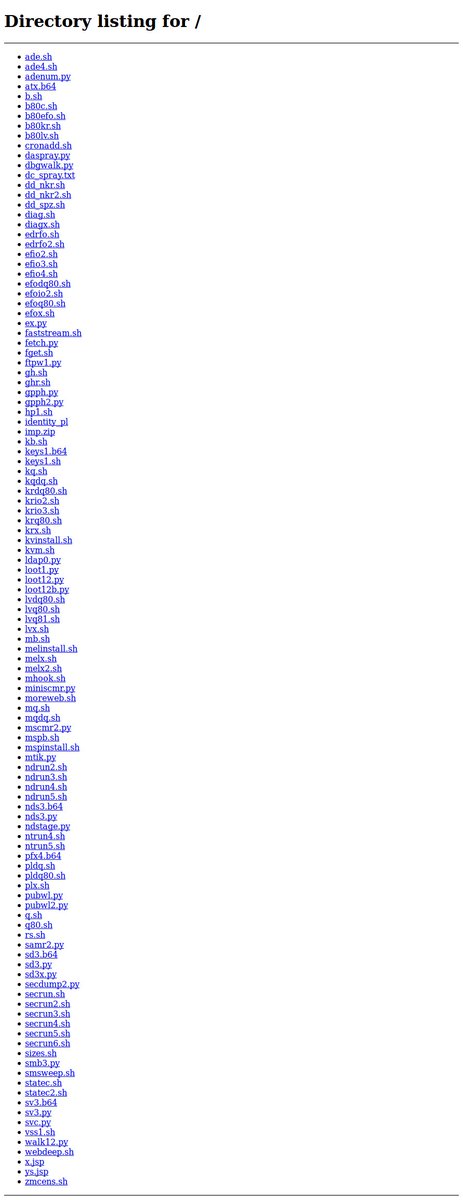
Opendir: http://131.123.43[.]239:8123/
🤷♂️
![malwrhunterteam's tweet photo. Opendir: http://131.123.43[.]239:8123/
🤷♂️ https://t.co/ZLeSBjKk2C](https://pbs.twimg.com/media/HTXovFhXMAAjyIm.jpg)
feeling #malicious
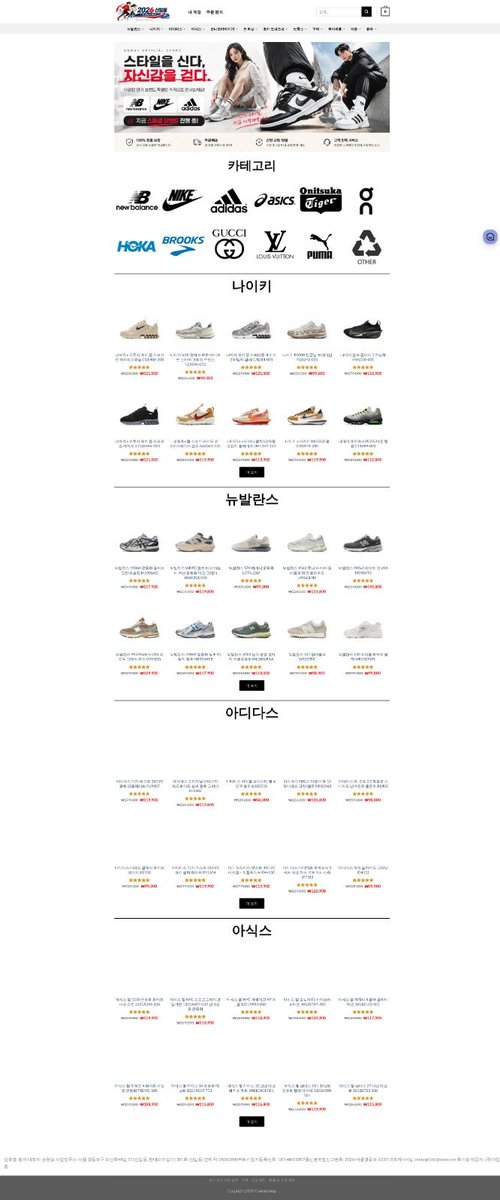
VT relations on that IP surfaced seoui[.]shop. Flagged #malicious by security vendors. Title reads "및 핫 셀링". Looks like a #Korean shoe store.
Resolves to 119.28.163[.]147
![_AkatsukiLegion's tweet photo. VT relations on that IP surfaced seoui[.]shop. Flagged #malicious by security vendors. Title reads "및 핫 셀링". Looks like a #Korean shoe store.
Resolves to 119.28.163[.]147 https://t.co/yasqrT9xKq](https://pbs.twimg.com/media/HS5GnTObcAA58Vt.jpg)
Reported
hxxps[://]entry-code-cdn[.]codes
(but also a good demo of using network protection in defender!)
(this was done on purpose)
#Malicious #URL #WebSiteCompromise #SupplyChain
![UK_Daniel_Card's tweet photo. Reported
hxxps[://]entry-code-cdn[.]codes
(but also a good demo of using network protection in defender!)
(this was done on purpose)
#Malicious #URL #WebSiteCompromise #SupplyChain https://t.co/L8JS5LhWt4](https://pbs.twimg.com/media/HSuUrjmW8AAxBIH.jpg)
Reporting from @BleepinComputer uncovers #malicious @npmjs #NPM packages bypassing install-script defenses at runtime.
Software #SupplyChains face heightened threats as #adversaries🦹♂️ exploit developer dependencies.
Defenders must rethink runtime #monitoring immediately. 🛡️ #CyberSecurity #AppSec #Hackers
https://t.co/GGgzPzgbem

Malicious npm packages evade install-script defenses at runtime
https://t.co/lYGecJc7xU
Last Seen Hashtags on Sotwe
candyfavours
Seen from United States
velvetbarstools
Seen from United States
BMWBerlinmarathon2018
Seen from United States
malluthund
Seen from India
cpk
Seen from United States
dfosouthchatra
Seen from United States
istanbulesc
Seen from Turkey
TBT9
Seen from France
eventschairs
Seen from United States
hijab mom
Seen from Turkey
Most Popular Users

Elon Musk 
@elonmusk
241.5M followers

Barack Obama 
@barackobama
118.8M followers

Cristiano Ronaldo 
@cristiano
114.6M followers

Donald J. Trump 
@realdonaldtrump
111.8M followers

Narendra Modi 
@narendramodi
107.1M followers

Rihanna 
@rihanna
98.7M followers

NASA 
@nasa
92.3M followers

Justin Bieber 
@justinbieber
91.8M followers

KATY PERRY 
@katyperry
90.1M followers

Taylor Swift 
@taylorswift13
84M followers

Lady Gaga 
@ladygaga
75.5M followers

Virat Kohli 
@imvkohli
73.5M followers

Kim Kardashian 
@kimkardashian
70.9M followers

YouTube 
@youtube
68.8M followers

Neymar Jr 
@neymarjr
66.5M followers

Bill Gates 
@billgates
65.3M followers

Selena Gomez 
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.2M followers

CNN 
@cnn
61.7M followers

X 
@x
60.7M followers


![Huntio's tweet photo. ⚠️ #malicious #opendir on 23.254.195[.]48
AttackCapture URL: https://t.co/DijpevaumH
Found by @BlinkzSec https://t.co/6wTVepx6if
https://t.co/aojFWxKETZ shows three opendir on 23.254.195[.]48 (RackNerd/HostPapa)
:8082 https://t.co/NVZSf0pAmC
- Alibaba OSS bucket enumerated (9,765 keys pulled), jndi/ldap rogue server staged with a reverse shell class, h2 scripts built to dump a MySQL "wallet" db, fake nacos listener logging real bearer tokens and cookies.
:8099 https://t.co/o0g0dddsDT
- Custom Go beacon compiled for Linux and Windows, full remote access kit (shell, file transfer, screenshots, socks5, persistence, self-delete), checks in to:8443
:8899 https://t.co/390BzMKnpm
- Same fake listener grabbing creds, operator notes claiming nacos access tied to a Chenzhou tourism target, wallet theft scripts (dump/decrypt/sweep), 3 cracked SSH passwords, beacon served 18 times](https://pbs.twimg.com/media/HUHaL3gW0AAVHGw.png)
![Huntio's tweet photo. ⚠️ #malicious #opendir on 23.254.195[.]48
AttackCapture URL: https://t.co/DijpevaumH
Found by @BlinkzSec https://t.co/6wTVepx6if
https://t.co/aojFWxKETZ shows three opendir on 23.254.195[.]48 (RackNerd/HostPapa)
:8082 https://t.co/NVZSf0pAmC
- Alibaba OSS bucket enumerated (9,765 keys pulled), jndi/ldap rogue server staged with a reverse shell class, h2 scripts built to dump a MySQL "wallet" db, fake nacos listener logging real bearer tokens and cookies.
:8099 https://t.co/o0g0dddsDT
- Custom Go beacon compiled for Linux and Windows, full remote access kit (shell, file transfer, screenshots, socks5, persistence, self-delete), checks in to:8443
:8899 https://t.co/390BzMKnpm
- Same fake listener grabbing creds, operator notes claiming nacos access tied to a Chenzhou tourism target, wallet theft scripts (dump/decrypt/sweep), 3 cracked SSH passwords, beacon served 18 times](https://pbs.twimg.com/media/HUHaL3eXMAA-3Wo.jpg)


![Huntio's tweet photo. ⚠️ #malicious #opendir hosted at 172.86.85.146[:]9999
AttackCapture URL: https://t.co/q7UL6QDZEs
Found by @malwrhunterteam https://t.co/hTBXBiorsp
1/ Flagged via AttackCapture: 172.86.85[.]146 (RouterHosting LLC / cloudzy[.]com, AS14956, Ogden, UT) runs a "PrivateC2 Login" panel on :5173 and an exposed n8n workflow-automation instance on :5678.
2/ An open dir on :9999 (nginx/1.24.0) holds pythonw.exe + python314.dll (a PyInstaller runtime pair) plus a 12.9MB gemini.log that's pure high-entropy binary - not a readable log, likely a packed/encrypted payload.
3/ HuntSQL pivot on html.head.title = 'PrivateC2 Login' since Jan 2026 turns up 2 more hosts running the same panel:
• 185.139.214[.]181 (ALEXHOST SRL) - plain HTTP, no MFA, basic build
• 23.95.217[.]154 (DataWagon LLC) - a Windows box (RDP :3389, SMB :445) running a newer build with MFA + SSO/OIDC login
4/ Same C2 panel, 3 hosts, 3 different providers, and a visibly iterating codebase.](https://pbs.twimg.com/media/HTj9kyTW8AAqsUA.jpg)
![Huntio's tweet photo. ⚠️ #malicious #opendir hosted at 172.86.85.146[:]9999
AttackCapture URL: https://t.co/q7UL6QDZEs
Found by @malwrhunterteam https://t.co/hTBXBiorsp
1/ Flagged via AttackCapture: 172.86.85[.]146 (RouterHosting LLC / cloudzy[.]com, AS14956, Ogden, UT) runs a "PrivateC2 Login" panel on :5173 and an exposed n8n workflow-automation instance on :5678.
2/ An open dir on :9999 (nginx/1.24.0) holds pythonw.exe + python314.dll (a PyInstaller runtime pair) plus a 12.9MB gemini.log that's pure high-entropy binary - not a readable log, likely a packed/encrypted payload.
3/ HuntSQL pivot on html.head.title = 'PrivateC2 Login' since Jan 2026 turns up 2 more hosts running the same panel:
• 185.139.214[.]181 (ALEXHOST SRL) - plain HTTP, no MFA, basic build
• 23.95.217[.]154 (DataWagon LLC) - a Windows box (RDP :3389, SMB :445) running a newer build with MFA + SSO/OIDC login
4/ Same C2 panel, 3 hosts, 3 different providers, and a visibly iterating codebase.](https://pbs.twimg.com/media/HTj9kyQXwAA48Rw.png)
![Huntio's tweet photo. 👿 #malicious #opendir hosted on 131.123.43.239[:]8123
AttackCapture URL: https://t.co/3msozYgsoQ
Found by @malwrhunterteam https://t.co/P2bOLFiKaP
This open dir is hosted at AlexHost SRL (AS200019), Sofia BG. Captured 2026-08-23, 113 files / 4.8MB, 103 tagged malicious.
What we found:
- Staging server for a hands-on campaign against dbr[.]gov[.]ua Zimbra mail infrastructure
-SMTP RCPT TO command injection + JSP webshell drop + 1-min cron persistence scripted out
- Two resumable mailbox dump workflows (zmmailbox tgz export + raw store archive), chunked POST exfil, 9 target variants (mel, pl, kv, kr, lv, efo, nkr, spz, msp)
- MLT Windows domain: credential spray, SAMR/SMB enum, SYSVOL/GPP hunt, DCSync + ntdsutil IFM + VSS shadow copy all staged for NTDS.dit
- 69-line cleartext cred list and an SSH private key just sitting in the dir alongside the tooling](https://pbs.twimg.com/media/HTeoSsEW4AI0Vdp.png)
![Huntio's tweet photo. 👿 #malicious #opendir hosted on 131.123.43.239[:]8123
AttackCapture URL: https://t.co/3msozYgsoQ
Found by @malwrhunterteam https://t.co/P2bOLFiKaP
This open dir is hosted at AlexHost SRL (AS200019), Sofia BG. Captured 2026-08-23, 113 files / 4.8MB, 103 tagged malicious.
What we found:
- Staging server for a hands-on campaign against dbr[.]gov[.]ua Zimbra mail infrastructure
-SMTP RCPT TO command injection + JSP webshell drop + 1-min cron persistence scripted out
- Two resumable mailbox dump workflows (zmmailbox tgz export + raw store archive), chunked POST exfil, 9 target variants (mel, pl, kv, kr, lv, efo, nkr, spz, msp)
- MLT Windows domain: credential spray, SAMR/SMB enum, SYSVOL/GPP hunt, DCSync + ntdsutil IFM + VSS shadow copy all staged for NTDS.dit
- 69-line cleartext cred list and an SSH private key just sitting in the dir alongside the tooling](https://pbs.twimg.com/media/HTeoSsBWAAEJKGL.jpg)
![Huntio's tweet photo. 👿 #malicious #opendir hosted on 131.123.43.239[:]8123
AttackCapture URL: https://t.co/3msozYgsoQ
Found by @malwrhunterteam https://t.co/P2bOLFiKaP
This open dir is hosted at AlexHost SRL (AS200019), Sofia BG. Captured 2026-08-23, 113 files / 4.8MB, 103 tagged malicious.
What we found:
- Staging server for a hands-on campaign against dbr[.]gov[.]ua Zimbra mail infrastructure
-SMTP RCPT TO command injection + JSP webshell drop + 1-min cron persistence scripted out
- Two resumable mailbox dump workflows (zmmailbox tgz export + raw store archive), chunked POST exfil, 9 target variants (mel, pl, kv, kr, lv, efo, nkr, spz, msp)
- MLT Windows domain: credential spray, SAMR/SMB enum, SYSVOL/GPP hunt, DCSync + ntdsutil IFM + VSS shadow copy all staged for NTDS.dit
- 69-line cleartext cred list and an SSH private key just sitting in the dir alongside the tooling](https://pbs.twimg.com/media/HTeoSr-XYAIvXiJ.png)


![_AkatsukiLegion's tweet photo. VT relations on that IP surfaced seoui[.]shop. Flagged #malicious by security vendors. Title reads "및 핫 셀링". Looks like a #Korean shoe store.
Resolves to 119.28.163[.]147 https://t.co/yasqrT9xKq](https://pbs.twimg.com/media/HS5Gl28asAEU6Ct.jpg)

![UK_Daniel_Card's tweet photo. Reported
hxxps[://]entry-code-cdn[.]codes
(but also a good demo of using network protection in defender!)
(this was done on purpose)
#Malicious #URL #WebSiteCompromise #SupplyChain https://t.co/L8JS5LhWt4](https://pbs.twimg.com/media/HSuUfUqXwAAk2RM.jpg)