

Top Tweets for #NETSCALER

Citrix flags a NetScaler SAML authentication issue as patched NetScaler appliances reboot after CVE-2026-88771 attacks. Check your config.
#Citrix #NetScaler #SAML #CVE202688771 #CVE202688772 #ZeroDay #Vulnerability
https://t.co/bzs5TqJeXo

A GitHub repository for the Citrix NetScaler exploitation activity associated with CVE-2026-88771 and CVE-2026-88772.
https://t.co/Dt5JYLEtMw
#Netscaler #CVE #Citrix #exploits #ioc #threatintel #Threathunting #CTI #cybernews #ioa


We are tracking rumors + honeypot activity relating to a new vulnerability affecting Citrix appliances, acknowledged just now in a Citrix blog.
It is currently unclear whether this is “DoS via bad patch" or "another bad vuln in SAML config'd appliances"
Our hearts 💔

#netscaler if you are using ICA Gateway with SAML https://t.co/Aj8giqSblM you better contact Citrix, not sure how critical it is...
So all security researchers that are looking into the latest #netscaler vulnerability, let me explain. For many #netscaler deployments is used for ICA Proxy that provides remote access to Citrix VDI. AAA is often used to provide SAML authentication in front of the ICA Proxy

Patched NetScalers rebooting today: a SAML exploit tries to drop a persistent kit and crashes them trying. Using SAML? Call Citrix for the workaround.
Free checker v1.10 finds the kit, the crashes, backdoor admins, 58 IPs:
https://t.co/fGlD4MZeiI
#NetScaler
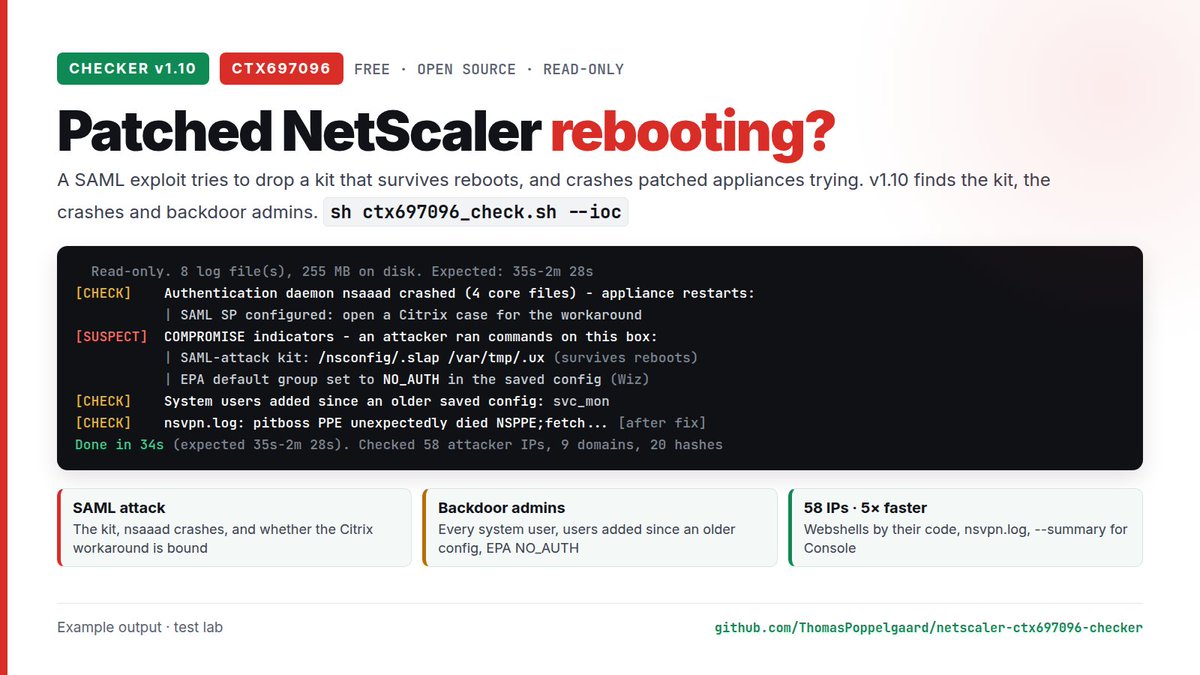


NCSC-FI says it outright: patching won't remove an attacker who's already inside. On NetScaler, hunt what the patch doesn't touch: webshells, cron jobs, superusers besides nsroot. @_POPPELGAARD's checker covers most of it, and v1.10 adds the superuser list. #NetScaler

🚨 BREAKING: Finland's cyber agency reports several intrusions through the Citrix NetScaler zero-days.
NCSC-FI has contacted the owners of hundreds of NetScaler instances in Finland and warns that patching alone will not remove an attacker who is already inside.
CVE-2026-88771 allows command execution without authentication.



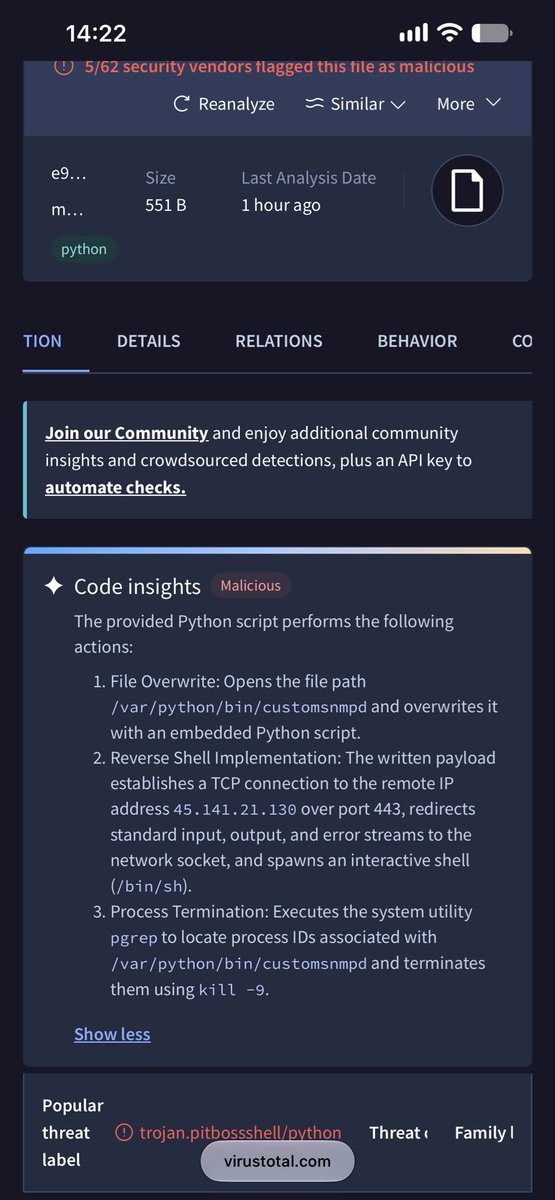

Citrix NetScaler CVE-2026-88772 was exploited for at least 24 days before Citrix disclosed and fixed the zero-day.
IOCs (6):
e9fe43968c6c0955300e3bc4d7fb0b05a18570b4733aaf4f5c6f7f09be5a242c
+5 more
Full set: https://t.co/0QNritnSTX

#Citrix #NetScaler #Post_Exploitation #Payload Creates #Superuser, Maps #Web_Shell to #CSS-Like URLs
https://t.co/9SvN7wPPi8


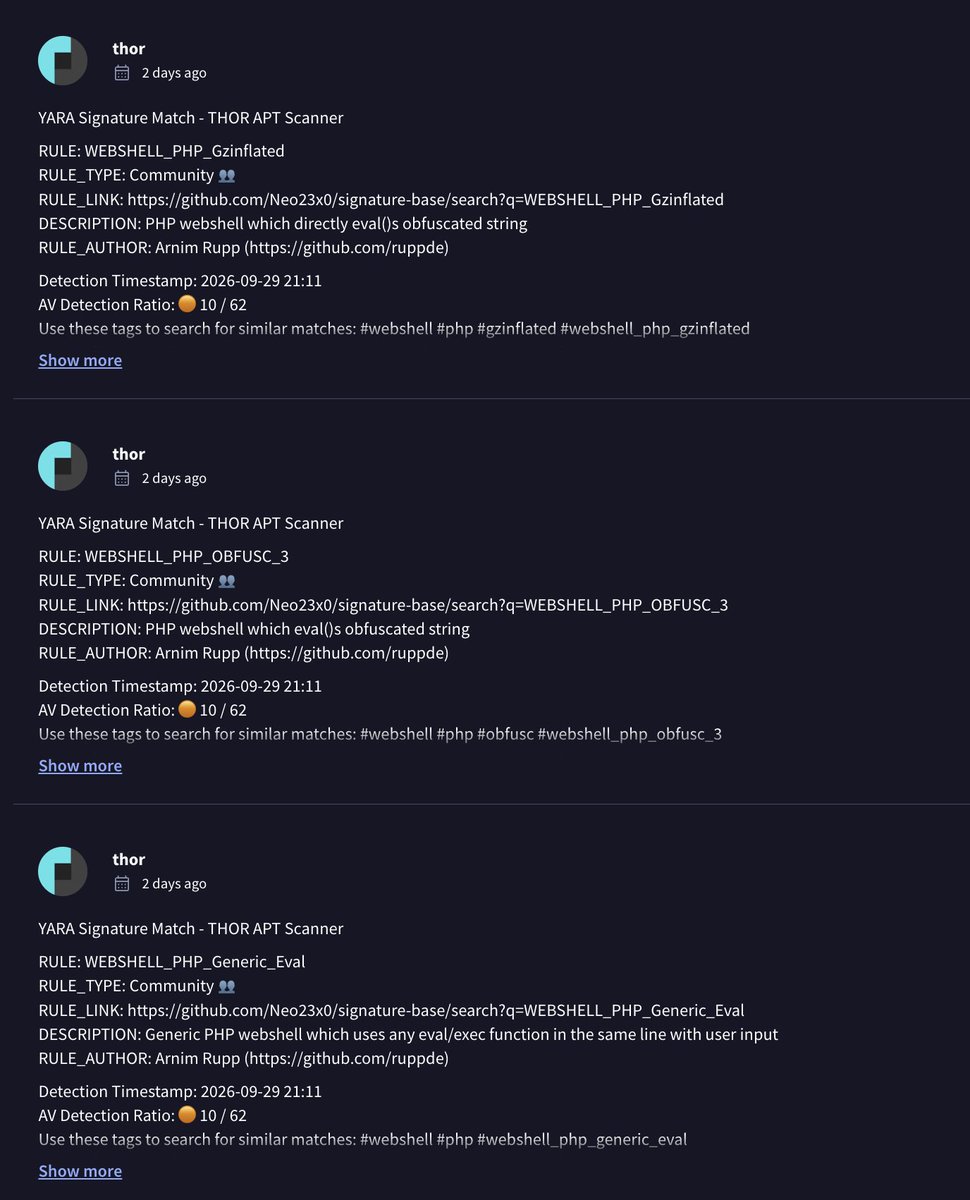
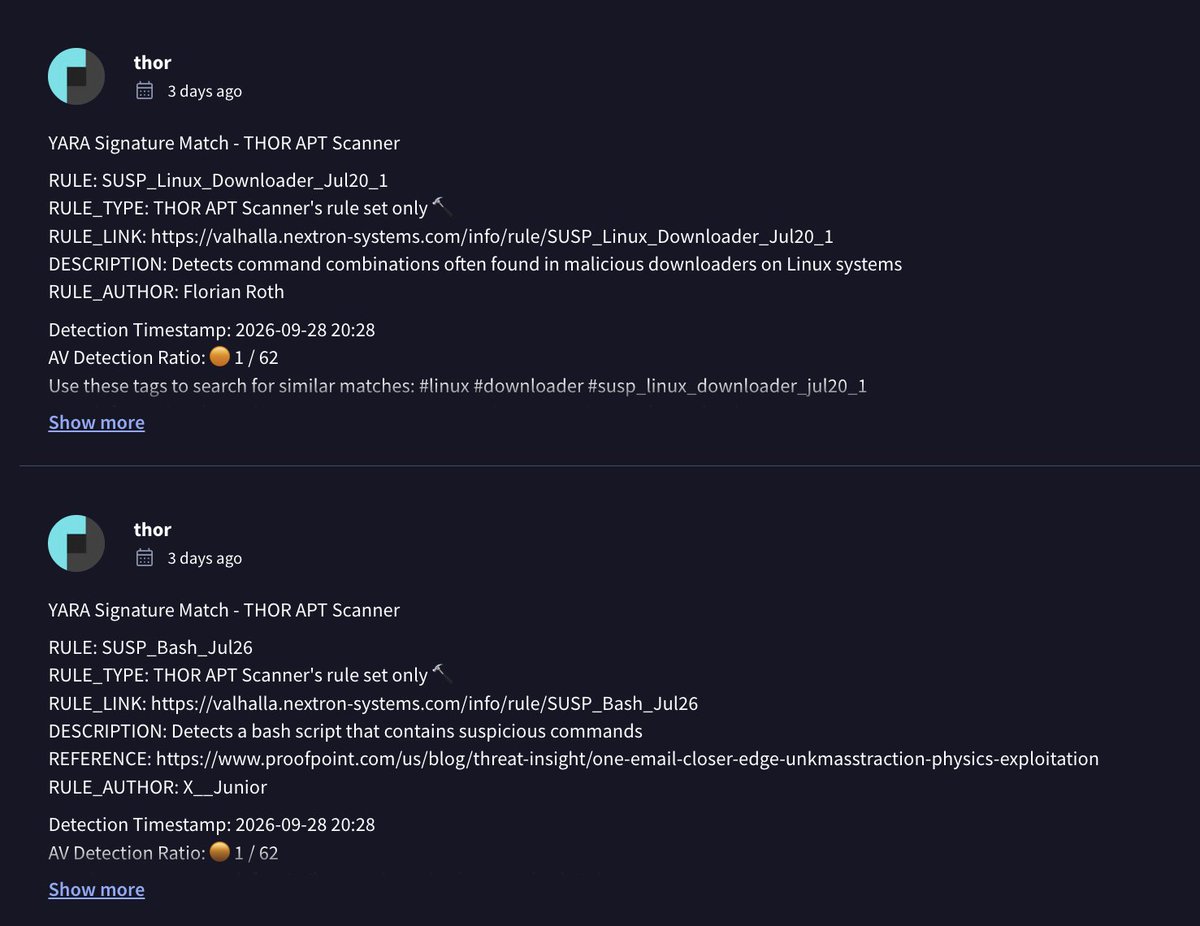
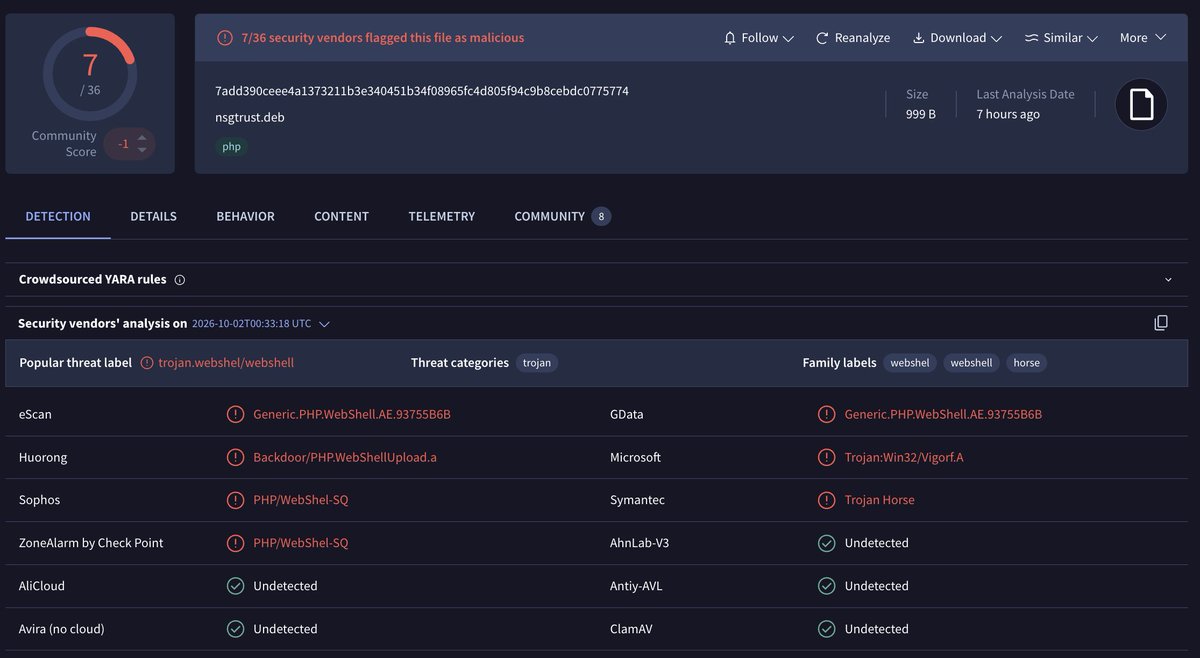
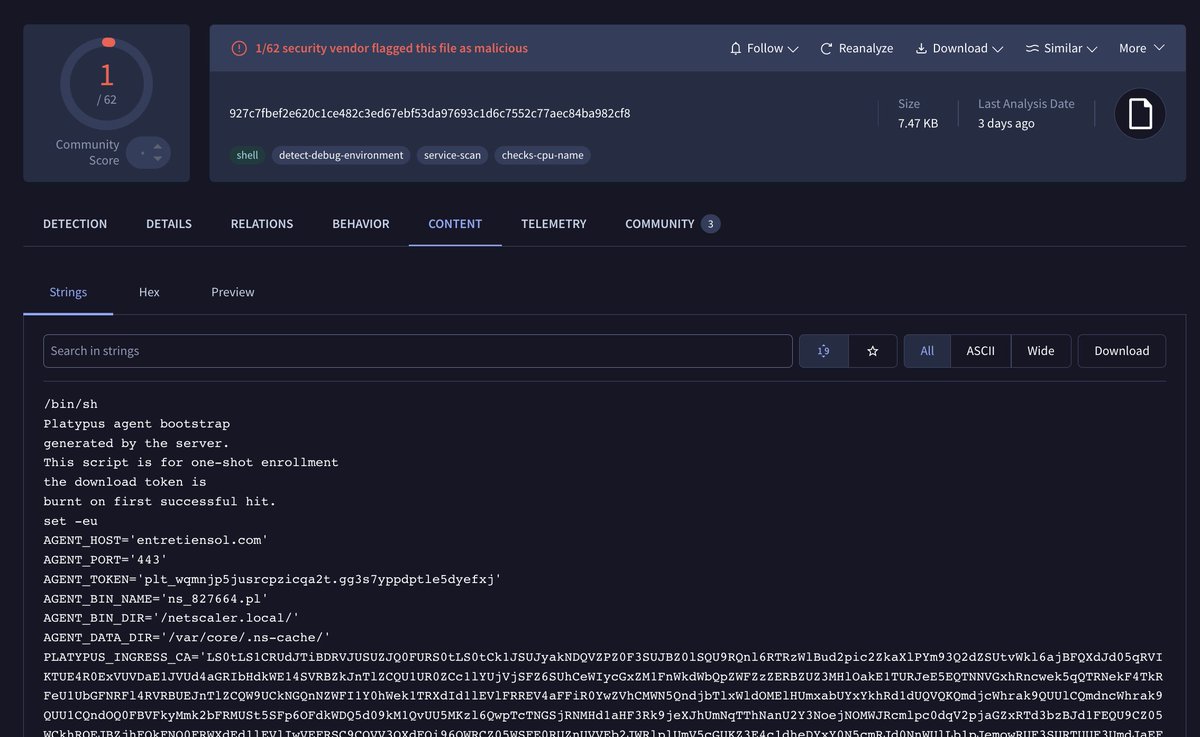
We examined artifacts left behind by attackers during the recent Citrix #NetScaler compromises. Many were already covered by existing generic THOR rules, including rules we've shipped for years.
One script matched SUSP_Linux_Downloader_Jul20_1. That rule dates back to 2020, more than six years ago(!). The script also matched SUSP_Bash_Jul26.
The recovered webshells matched these existing generic rules:
- SUSP_WEBSHELL_PHP_Encoded_Jun21_1
- SUSP_Eval_Base64_Indicators_Feb22_1
- EXT_WEBSHELL_PHP_Generic_Eval
- EXT_WEBSHELL_PHP_OBFUSC_3
- EXT_WEBSHELL_PHP_Generic
- EXT_WEBSHELL_PHP_Gzinflated
- EXT_WEBSHELL_PHP_Dynamic_Big
Some of those webshell rules are in THOR Lite, too (EXT_*)
This is POST-EXPLOITATION DETECTION. We didn't need to know which zero-day got the attacker in to recognize what they left behind.
A scan could have flagged these artifacts from day one, before the exploited vulnerabilities were public. The rules were already there.
Scan your edge devices regularly. Daily, where practical. Use THOR via SSHFS or scheduled file collection for THOR Thunderstorm.
Don't wait for the next advisory to start looking
Why THOR detects what others miss
https://t.co/EbtVt3al8E

For the last two days, our Research Team has been looking into the recently disclosed Citrix NetScaler vulnerabilities CVE-2026-88771 and CVE-2026-88772 and building detection coverage to help identify compromised systems.
The new THOR Preview signature set currently includes:
- EXPL_CVE_2026_88772_POC_Sep26
Detects artifacts related to the public CVE-2026-88772 PoC
- LOG_SUSP_EXPL_CVE_2026_88771_Sep26
Detects potential CVE-2026-88771 exploitation traces in NetScaler logs
- WEBSHELL_CSS_PassThrough_Sep26
Detects the PHP webshell pattern observed in the post-exploitation activity reported by GreyNoise
We also released a new IOC set:
- NetScaler ADC suspicious file artifacts
It contains filesystem indicators derived from the Citrix IOC scanner script and covers suspicious PHP/XHTML files and other unusual artifacts in NetScaler web directories.
The Preview signatures are already available with:
./thor-util update --sigdev
We’ll keep adding signatures as new technical details become available from public research and from information shared with us by partners and customers.
Details:
https://t.co/3JZKTSWgXG
And if you’re wondering how to actually scan a NetScaler appliance with THOR: we documented a remote scanning approach using SSHFS a few years ago, which still applies here:
https://t.co/Q4NWOZxAWL

Researchers say some organisations may still face unauthorised access after patching NetScaler devices, with attackers using scripts and reverse shells post-exploit. #NetScaler #CyberSecurity #InfoSec #UKTech https://t.co/3ePqlRXZVh

Alerta ISD N.° 188-2026-CNSD: vulnerabilidad crítica de día cero en Citrix NetScaler que permite acceso root y despliegue de web shells.
https://t.co/Dzz9oVpPJT
#Ciberseguridad #CNSD #Citrix #NetScaler #ZeroDay


Aktiv ausgenutzte Netscaler-Lücken - Arctic Wolf analysiert die Aktivitäten der Angreifer
@AWNetworks #ArcticWolf #Cybersecurity #Cybersicherheit #IncidentResponse #IndicatorsofCompromise #Netscaler #Schwachstelle
https://t.co/UAen0yoFcZ

Two NetScaler zero-days. CVSS 9.5 each. Exploited weeks before a patch existed. 🚨
Patching closes the door. It does not show who was already inside.
The 7 steps from patch to closure 👉 https://t.co/fQAZyxtcGw
#NetScaler #ZeroDay

NetScaler backdoor persists after patching. WHIPSHOT webshell hides as CSS on 50,277 appliances. Block 45.141.21.130. Forensic checklist: https://t.co/3HJdq1Sbg1 #CVE202688771 #NetScaler

🚨 CVE-2026-88772: NetScaler attacks go beyond initial access.
Mandiant observed attackers using WHIPSHOT web shells and SLAPSHOT tunneling malware after gaining pre-auth root access.
Patching may not remove persistence or stolen credentials.
#ThreatIntel #NetScaler

Attackers are exploiting NetScaler zero-days CVE-2026-88771 and CVE-2026-88772 for root-level network access. Patch ADC and Gateway now: https://t.co/3vcnh2jGeP #CyberSecurity #NetScaler #ZeroDay
https://t.co/3vcnh2jGeP
Last Seen Hashtags on Sotwe
izmirtravesti
Seen from Turkey
BAYFALL1
Seen from United States
ifşa anne
Seen from Turkey
RanthamborePhysioSummit
Seen from United States
nsfwtwt
Seen from United States
tweetmuna
Seen from United States
chriscotter
Seen from United Kingdom
beurette renoi
Seen from Belgium
สวิงกิ้งเมีย
Seen from Thailand
سـكـــسًْ
Seen from Saudi Arabia
Most Popular Users

Elon Musk 
@elonmusk
241.7M followers

Barack Obama
@barackobama
119M followers

Cristiano Ronaldo
@cristiano
114.5M followers

Donald J. Trump
@realdonaldtrump
111.9M followers

Narendra Modi
@narendramodi
107.2M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.4M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.5M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.5M followers

Bill Gates
@billgates
65.2M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.3M followers

CNN
@cnn
61.8M followers

X
@x
60.7M followers