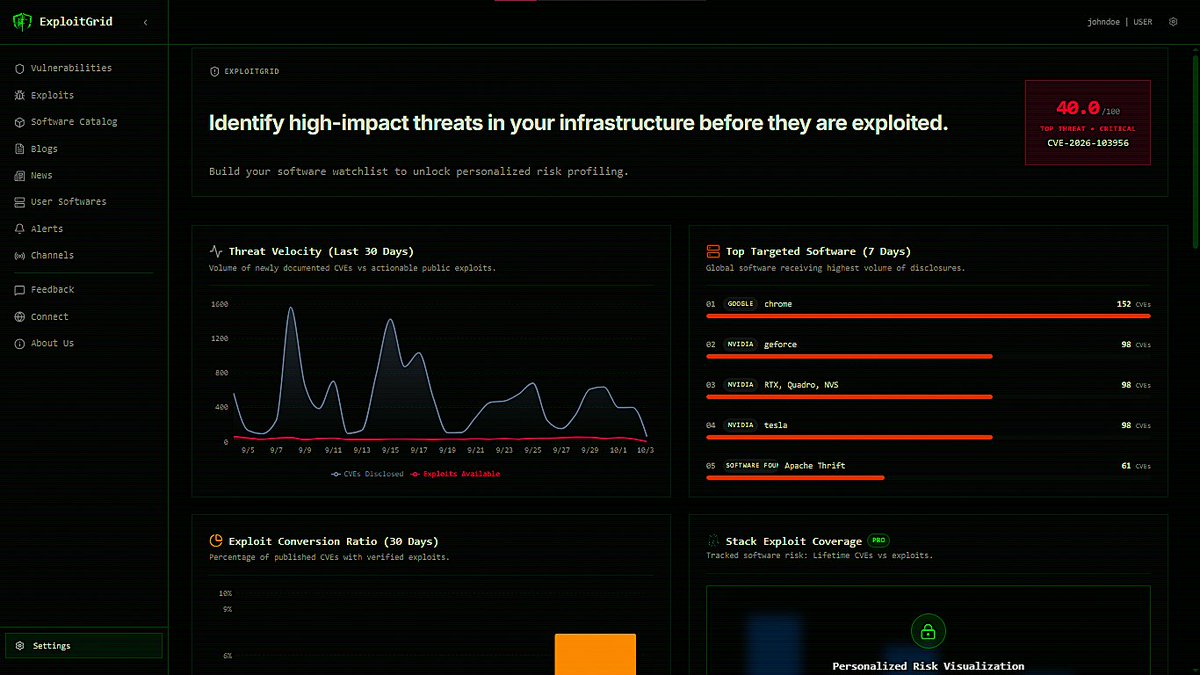
Introducing ExploitGrid.
New vulnerabilities and exploits appear every day. The challenge isn't finding them. It's knowing what matters, what's being exploited, and what needs attention first.
We built ExploitGrid for that.
🧵 Here's what we offer:
🚨 As if PHP2Shell wasn't enough for one day... now GitLab.
CVE-2026-110264 (CVSS 10.0) could allow unauthenticated RCE on self-managed GitLab servers, potentially affecting 12 years of releases, back to 2014.
Patches are available. Update immediately!
https://t.co/PMrlgsdu3t
🚨 AI-assisted cyberattacks are moving beyond experiments.
Microsoft reports Storm-0940 used AI agents for reconnaissance and abuse of trusted access across hundreds of organizations.
AI speeds up attacks. Existing access makes them harder to detect.
🔎 https://t.co/3IVcXRYho9
🚨 Five Apache bugs landed at CVSS 10 today, four of them in Traffic Server alone. Mercury (mljar), which was a CVSS 10 unauth RCE two days ago, now has a public RCE exploit.
Here’s what hit the feed 👇
🚨 PHP2Shell activity predates disclosure.
AWS reports a honeypot recorded an attempt on Oct 17, four days before disclosure on Oct 21.
Investigate suspicious activity from Oct 17 onward and patch to a fixed PHP version.
Patching alone isn’t enough.
🔎 https://t.co/3IVcXRYho9
Affected versions span Java SE 8, 11, 17, 21, 25 and 27, plus specified GraalVM releases. Check Oracle’s advisory for the exact affected builds and remediation guidance: https://t.co/DtHaePOSiw
🚨 Oracle Java CVE-2026-91403: a critical JSSE flaw enables unauthenticated network attacks on data confidentiality and integrity.
CVSS 9.1. No public exploit found. ExploitGrid: 36.4/100 Medium.
Update affected Java and GraalVM versions.
🔎 https://t.co/3IVcXRYho9
Some more updates, https://t.co/dQQj7UzpuT , implements chain_e, which was first reported from jackalsyn. This works on a lab for the patched releases. Verify on your end always under a lab env.
A TLS certificate’s private key was reportedly as weak as the number 4.
The eMudhra incident shows how flawed key generation can undermine trust in digital certificates and enable forged identities.
Trust starts with secure key generation.
🔎 https://t.co/3IVcXRYho9
⚠️ GitLab CVE-2026-112212: an unauthenticated attacker could poison a shared OAuth/OIDC discovery cache under certain conditions, redirecting authentication flows to an attacker-controlled server.
Review patched GitLab releases.
🔎 https://t.co/3IVcXRYho9
➕ +584 more threats tracked today.
Explore the full threat feed and mitigation details on ExploitGrid.
🔗 https://t.co/3IVcXRYho9
Disclaimer: Informational, defensive security monitoring only.