

Top Tweets for #RansomwareSpotlight

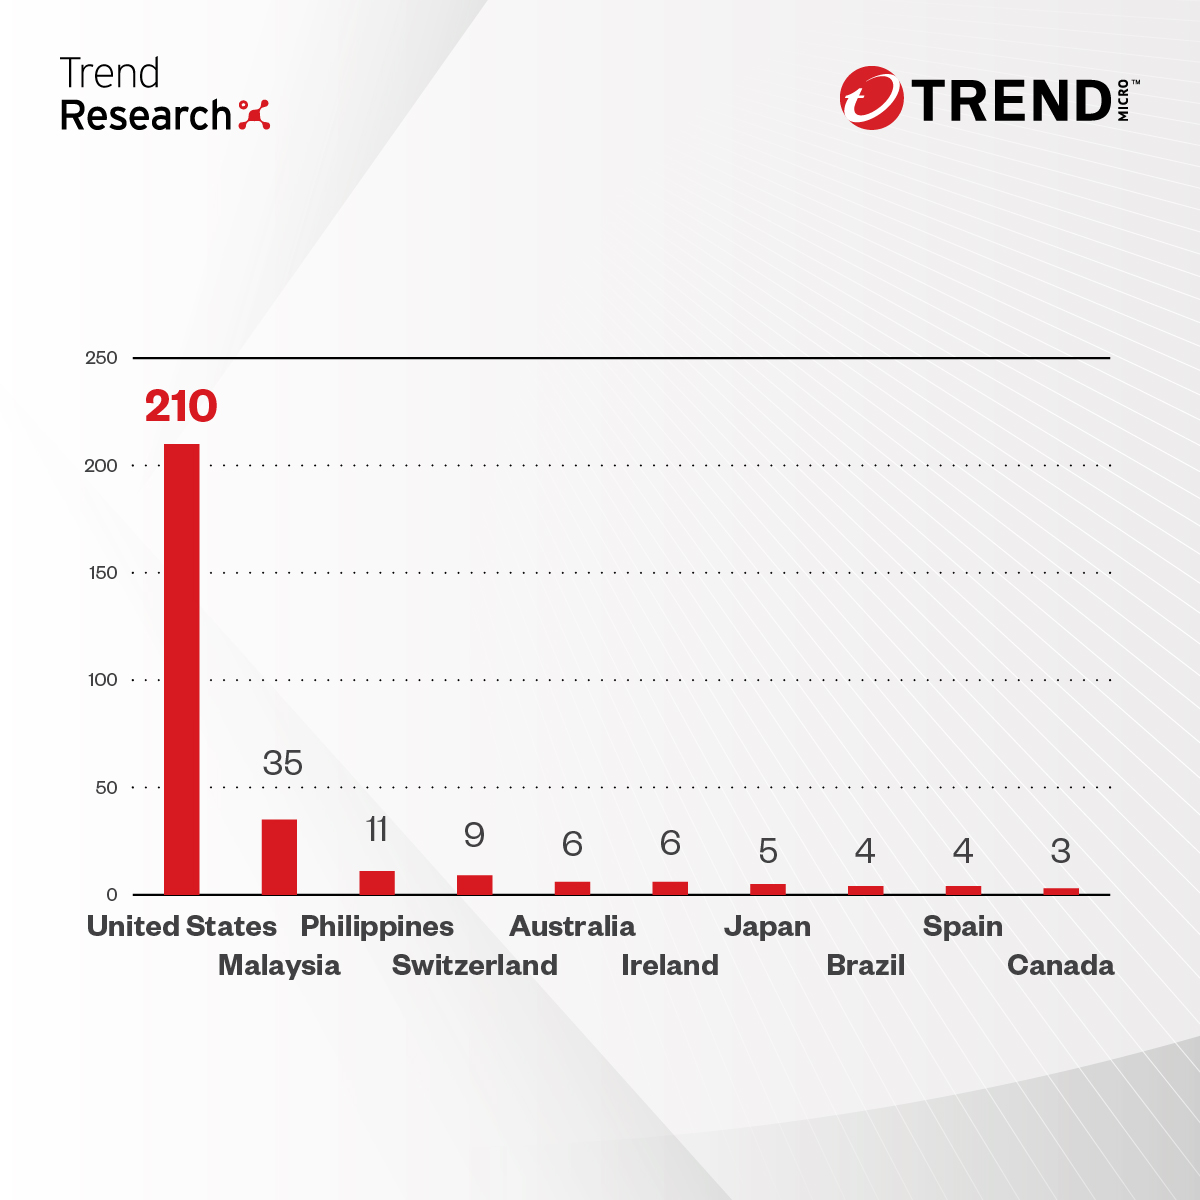
Our #RansomwareSpotlight reveals that RansomHub predominantly targets small businesses within North America, especially in the United States.
Read more about this #ransomware: ⬇️ https://t.co/uMx5QrGvVG
Our #RansomwareSpotlight reveals that RansomHub predominantly targets small businesses within North America, especially in the United States.
Read more about this #ransomware: ⬇️ https://t.co/uMx5QrGvVG

Despite aggressive tactics, RansomHub selectively avoids non-profits and CIS regions, highlighting a unique ethical boundary. Their affiliate program, offering 90% of ransoms, further incentivizes participation.
Find out more in our #RansomwareSpotlight: https://t.co/uMx5QrGvVG
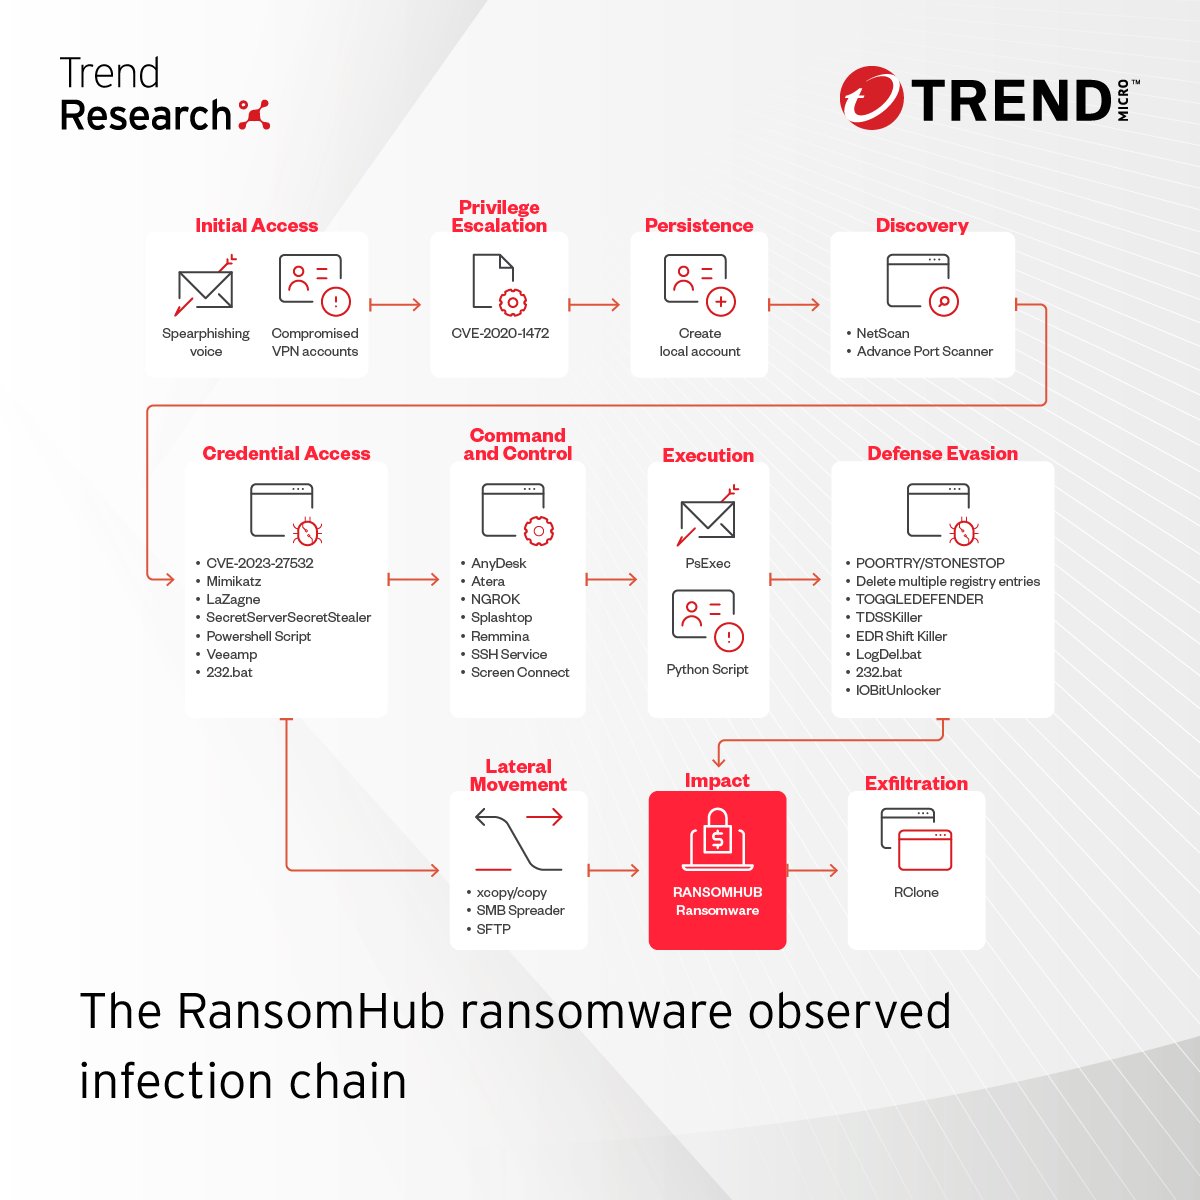
In our #RansomwareSpotlight, RansomHub highlights technical prowess by using GoLang for Windows/Linux and C++ for ESXi servers, indicating a sophisticated cross-platform threat. Understand these capabilities and their security challenges.
Learn more: https://t.co/uMx5QrGvVG

RansomHub exploits weaknesses in cloud storage, particularly targeting misconfigured Amazon S3 instances, to threaten data leaks and extort providers.
Learn more in our #RansomwareSpotlight: ⬇️ https://t.co/uMx5QrGvVG

In our #RansomwareSpotlight, RansomHub demonstrates a diverse victimology, with notable frequency in targeting the Information Technology sector.
Learn more about RansomHub's impact across industries in our report: ⬇️ https://t.co/uMx5QrGvVG
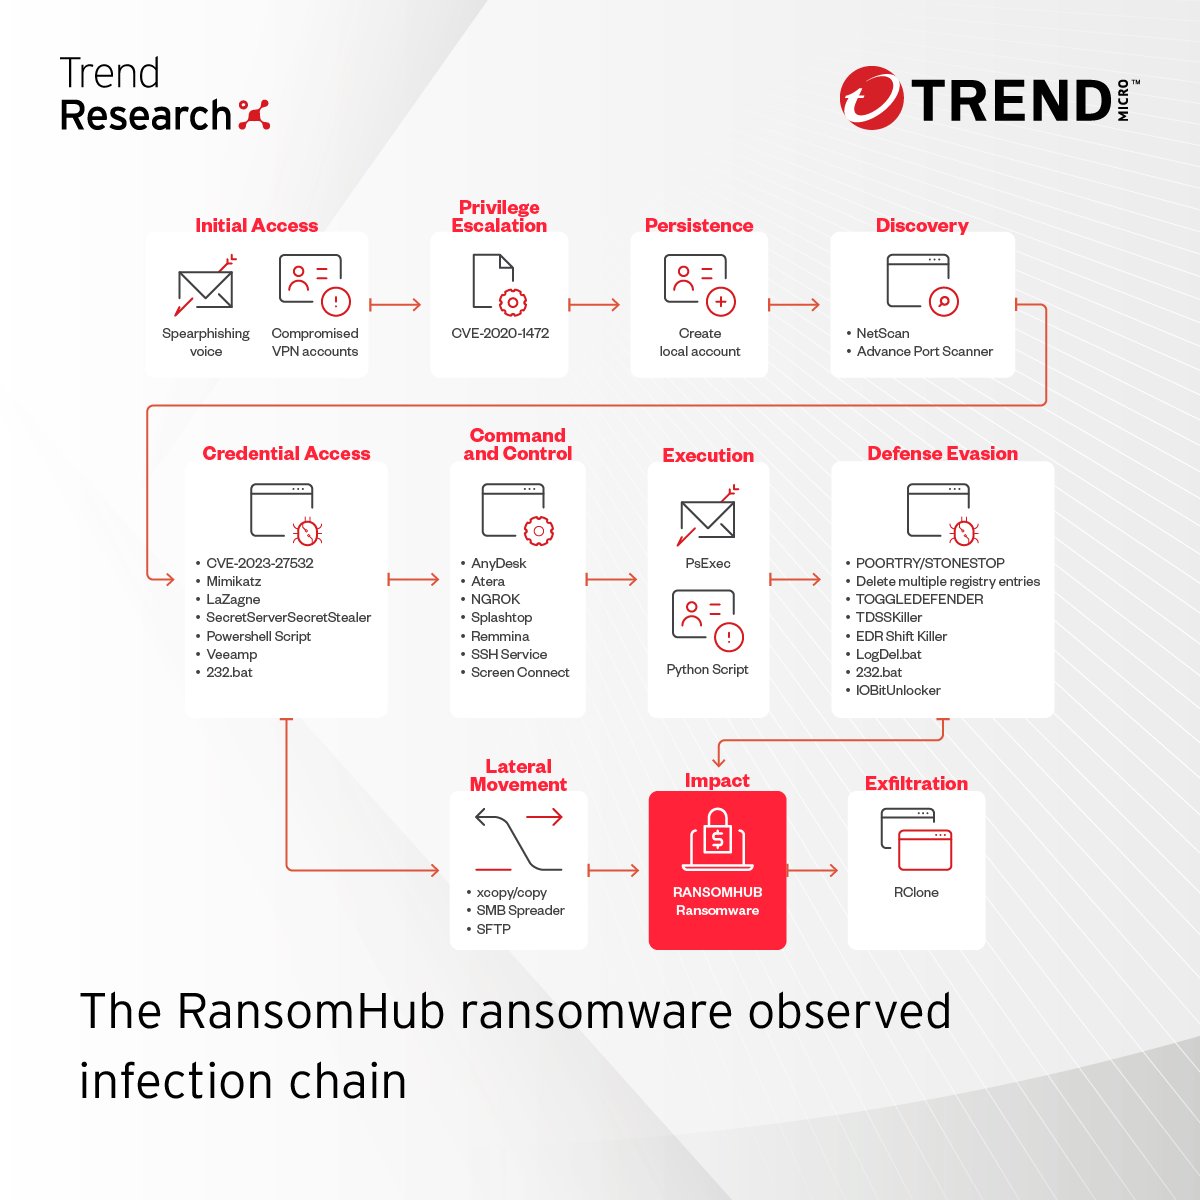
In our #RansomwareSpotlight, RansomHub demonstrates a diverse victimology, with notable frequency in targeting the Information Technology sector.
Learn more about RansomHub's impact across industries in our report: ⬇️ https://t.co/uMx5QrGvVG

Our #RansomwareSpotlight reveals that RansomHub predominantly targets small businesses within North America, especially in the United States.
Learn more about this ransomware: ⬇️ https://t.co/uMx5QrGvVG
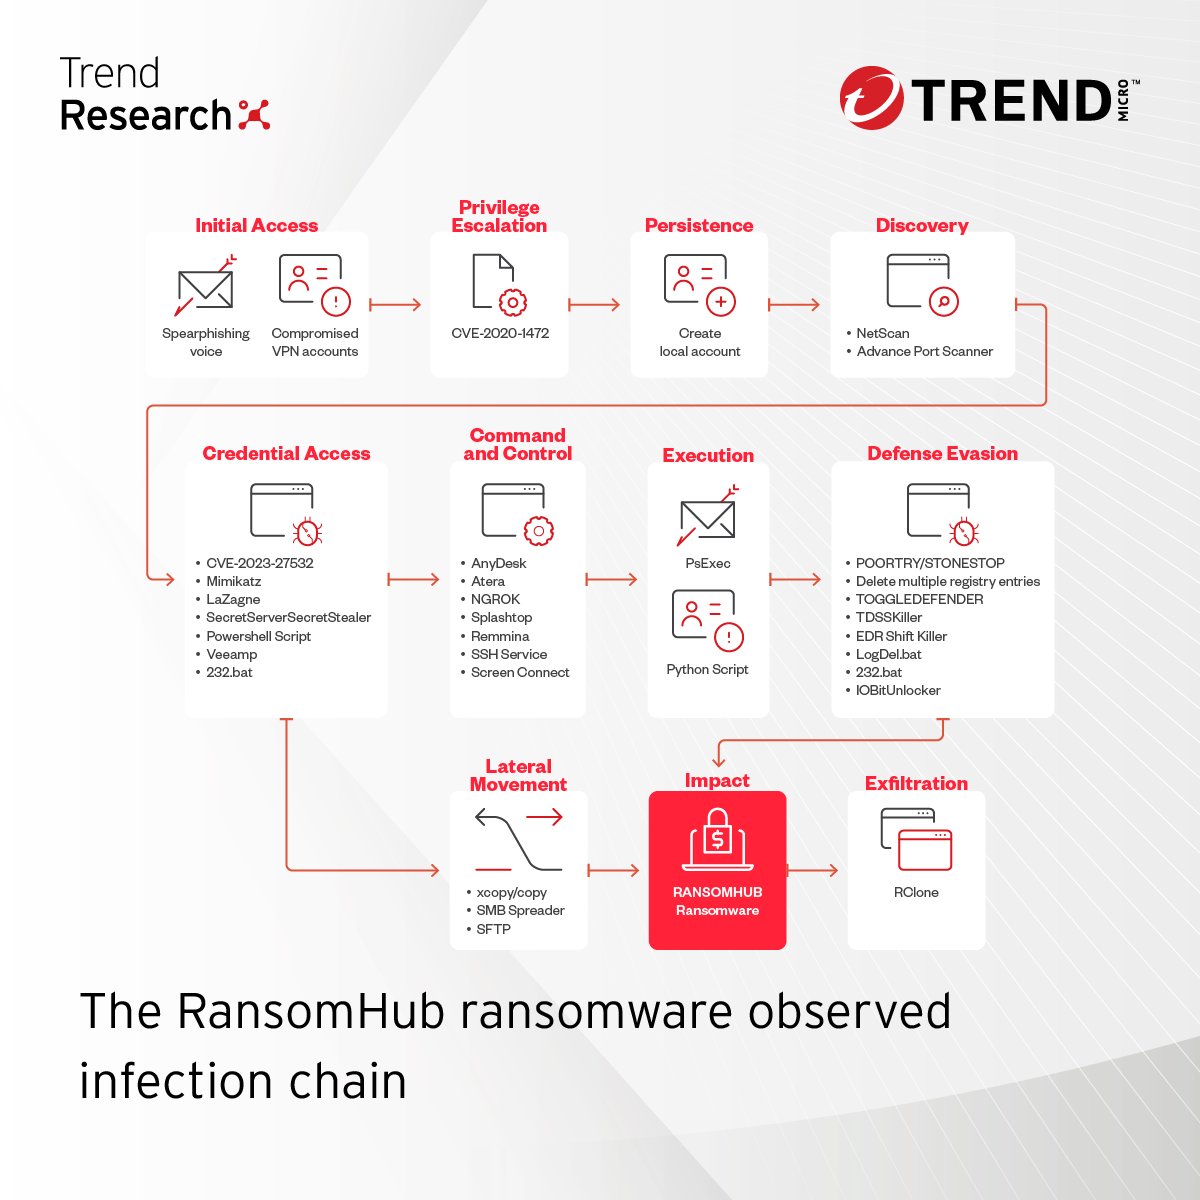
Our #RansomwareSpotlight report details how INC ransomware leverages tools like HackTool.Win32.ProcTerminator.A for defense evasion and deploys new methods to terminate victims' system processes.
Learn how these tactics work: ⬇️ https://t.co/JTGic4ZgLB
Our #RansomwareSpotlight report details how INC ransomware leverages tools like HackTool.Win32.ProcTerminator.A for defense evasion and deploys new methods to terminate victims' system processes.
Learn how these tactics work: ⬇️ https://t.co/JTGic4ZgLB
INC Ransomware targets victims via phishing and uses valid credentials from Initial Access Brokers. Stay vigilant with the insights found in our #RansomwareSpotlight.
Click here to read more about the INC ransomware:⬇️ https://t.co/JTGic4ZgLB
Threat actors behind INC #ransomware use purchased, valid account credentials typically acquired through Initial Access Brokers.
Discover more about INC ransomware’s tactics in our #RansomwareSpotlight:⬇️ https://t.co/JTGic4ZgLB
INC Ransomware targets victims via phishing and uses valid credentials from Initial Access Brokers. Stay vigilant with the insights found in our #RansomwareSpotlight.
Click here to read more about INC ransomware:⬇️ https://t.co/JTGic4ZgLB
Our #RansomwareSpotlight report details how INC #ransomware leverages tools like HackTool.Win32.ProcTerminator.A for defense evasion and deploys new methods to terminate victims' system processes.
Learn how these tactics work:⬇️ https://t.co/JTGic4ZgLB

#INCRansomware evolves rapidly by leveraging vulnerabilities in Netscaler ADC & Gateway for initial access.
Our latest #RansomwareSpotlight provides valuable insights into this evolving threat: https://t.co/Nbobv4W3k6

INC Ransomware targets victims via phishing and uses valid credentials from Initial Access Brokers. Stay vigilant with the insights found in our #RansomwareSpotlight.
Stay in the loop and read more about INC ransomware here: https://t.co/xYdiQhL6ND
Threat actors behind INC #ransomware use purchased, valid account credentials typically acquired through Initial Access Brokers. They have also targeted victims via phishing in their early attacks.
Learn more from our #RansomwareSpotlight:⬇️ https://t.co/JTGic4ZgLB
The INC Ransomware targets victims via phishing and uses valid credentials from Initial Access Brokers. Stay vigilant with the insights found in our #RansomwareSpotlight.
Stay in the loop and read more about the INC Ransomware here:⬇️ https://t.co/JTGic4ZgLB
#RansomwareSpotlight: INC ransomware positions its double extortion scheme in the guise of “safeguarding the reputation” of its victims to pressure them into paying a ransom.
Find out what organizations need to know: https://t.co/cU1JsLj1Ha
Cybercriminals behind INC #ransomware have primarily targeted healthcare organizations but have also extended attacks to academia, nonprofits, and religious groups in the community sector.
Discover more in our #RansomwareSpotlight:
https://t.co/jCrr3YnfyA
Most Popular Users

Elon Musk 
@elonmusk
241.5M followers

Barack Obama
@barackobama
118.8M followers

Cristiano Ronaldo
@cristiano
114.5M followers

Donald J. Trump
@realdonaldtrump
111.8M followers

Narendra Modi
@narendramodi
107.1M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.3M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.5M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.5M followers

Bill Gates
@billgates
65.3M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.2M followers

CNN
@cnn
61.7M followers

X
@x
60.7M followers