

Top Tweets for #RustPack

Rumour has it that Jonas Lykkegaard's self-delete technique doesn't work on Windows 11 anymore. Well, the original proof of concept (PoC) does not, but slight modifications bring this technique back to Win11!😎
With #RustPack, you can easily generate self-deleting executables or DLLs. The following video showcases a DLL being executed from rundll32.exe and deleting itself while the process continues to run. 🔥 Of course, this also works for DLL sideloads.
Having problems generating payloads yourself? Don't have time for proper evasion? Your loaders get flagged regularly? We've got you covered — contact us at info[at]https://t.co/7A5FxNExvF 👍
The Ruy-Lopez technique sometimes helps a lot with evasion. The technique was published and open sourced by our founder @Shitsecure two years ago. In #RustPack version 1.3.1 we added a custom, non-public version of this technique that is much more OPSec safe than the public version.
The original release only allowed spawn/inject, which is relatively limited. If you wanted to stay in your local process or sideload binary, you could not use it. In RustPack you can use Ruy-Lopez for local execution AND spawn/inject for both executables and DLL payloads. And it will prevent userland EDR DLLs from loading on top of amsi.dll. 🤠
For a few months now, all Sliver payloads have been flagged by many vendors because of the built-in AMSI patch bypass. Most people stuck to modifying the sliver source to get rid of these detections. Well, if amsi.dll is never loaded at all, the patch won't happen either, and you can get rid of this detection just by using the Ruy-Lopez technique. 💡
The following video shows how to pack a Sliver executable with RustPack to get a fully functional connection without any detections. 🔥
And this is just a small use case. A fully interactive Powershell runspace with all amsi related DLLs blocked and no userland hook DLLs sounds great too, right? Easy to build with RustPack in a few seconds. Execute all those Powershell scripts like it's many years before 2025. 🥳
#RedTeam #Pentest #OST #Malware #Maldev
#RustPack version 1.3.0 has been released today. This version includes (again) minor changes to the final payload metadata to remove various potential IoCs. 🔥🔥
For example, most packers use some kind of string based encoding to reduce entropy, such as the well-known UUID, MAC, IPv4 endings. Or custom words. However, having a large amount of strings in a binary can also be considered suspicious, so this release now uses a different encoding that looks like legitimate code instead of strings. 💡
You can never have enough alternatives to bypass AMSI or ETW? With this release, we have reached the point where new techniques should not be needed for some time. We have added three new AMSI bypass techniques and two more ETW bypasses in this release. This makes a total of 7 different AMSI bypasses and 5 ETW bypasses. Of course, we provide our customers with information on which bypass to use against which vendor. Multiple of those bypasses are not used by any public open source tools by now, ensuring long term coverage without detections. If any of these bypasses get flagged by behaviour, we usually also adjust them for the next release so that it's usable again. 😎
One of the newly added AMSI bypasses is a customized Ruy-Lopez version, which not only prevents AMSI related DLLs from loading into a process but which on top also prevents userland hooking DLLs from loading. You will therefore not only get rid of AMSI based detections but also don't have to worry about userland hooks in that process anymore. 🥳
From this release on, all executables and DLLs by default use random metadata information, such as copy right information, productversion and so on. Executables are also shipped with random different Icons, which also reduces overall suspicion. But Operators can now also clone any other files metadata or Icons, so that executables can look like PDF-files or whatever else you prefer to use.
Interested in buying RustPack or getting more information? Contact us via info[at]https://t.co/7A5FxNExvF !
#Pentest #RedTeam #OST
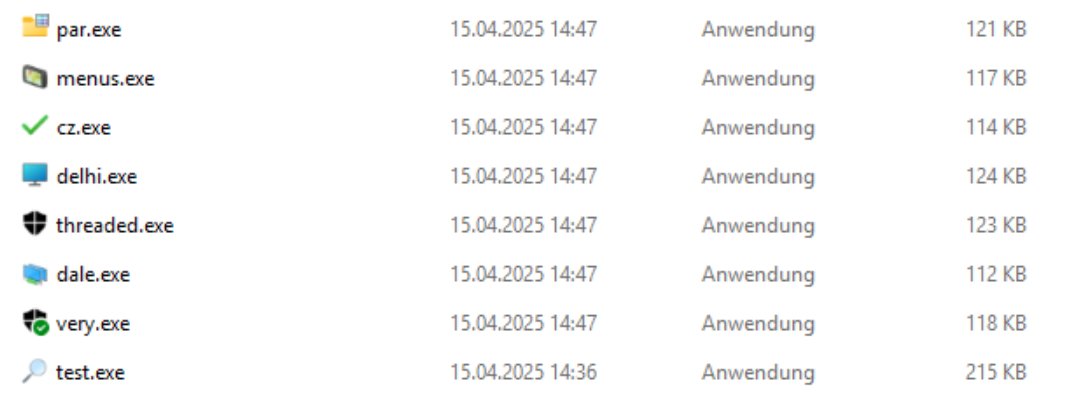
#RustPack Version 1.2.0 is now released for our customers. The biggest change was to add full DInvoke support for all payloads. The import table now won't show the Windows APIs being used anymore, instead by default random non malicious imports are added in here to make payloads look more benign. This was in the very end like a re-write of all existing code.
Besides from that one new AMSI bypass alternative was added on top of the existing ones. All of them work fine against most EDRs but it's always good to have options. 🙃
On top one new OpSec safe injection technique was integrated, in combination with the existing options it will be hard to flag your payload - even with ETWti data. 🤠
More info here:
https://t.co/2J0hCLkbvz
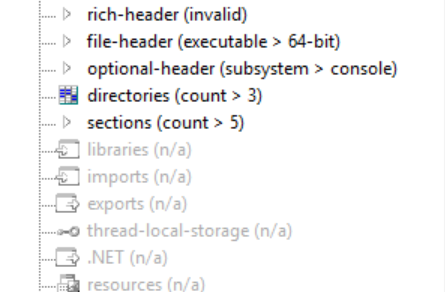
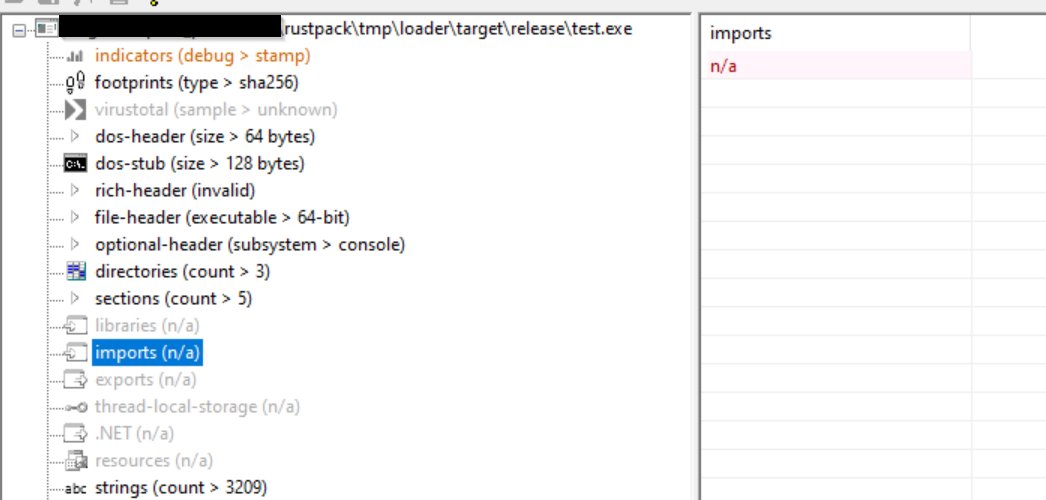
The next version of #RustPack will not expose any of it's used imports anymore 🔥🔥🔥
Instead, there will be random friendly looking imports for each payload. Only if the operators really want to they can still go for zero imports. Just because it's possible.🙂
The simplest use case for #RustPack: Packing shellcode into an unsigned executable. RustPack is an Windows executable, which can be used offline. It takes the input file (in this case Havoc shellcode) and builds an executable output format, which will decrypt and execute the shellcode on runtime.
Although we don't recommend using unsigned executables, they will still work fine against most classic AV vendors and some EDR's. Perfectly fine for a Pentest, better not when detections matter. As you can see, there is a warning system that tells operators that they should adjust the options to make the payload more OPsec safe. If you don't see a warning - that's the way to go. But OPsec considerations can also be found in our RustPack DOCS. 💡
Operators can place the output executable on their target host and execute it to retrieve the Command & Control connection. 🔥
In our case, we enumerate our current user using the built-in whoami module, check for open windows using an open source BOF and finally enumerate the AMSI provider DLLs using Seatbelt. 😎
🔥🔥The first new #RustPack version 1.1 was just sent to our customers. 🔥🔥
________________________
Changes include:
- A killdate can now be set, after that date payloads won't fire anymore
- The operator can specify the host binary, in which the payload will fire. It will only fire there, nice for DLL Sideloading or targeted COM Hijacking
- Optional option to only execute the payload once at the same time. Also viable for Sideloading or COM Hijacking to not get multiple C2 connections at once
- New non public ETW patching offsets
- Service binary output format, so that custom executables for Lateral Movement or persistence can be used
- Now there is also RustPack DOCS, a guide for each feature plus OPSec recommendations from our side🚨
________________________
More information about RustPack at https://t.co/h37e1ok21e!
Directly want to get into contact? E-Mail us via:
inquiry[at]msecops[dot]de
Another super handy feature for Pentesters is the interactive Powershell. Whenever you have a project where you have interactive access to a desktop environment, you may want to stick to the offensive Powershell tooling.
In this case, #RustPack can generate an executable for you that runs an interactive Powershell runspace *after* bypassing AMSI and ETW via the option of your choice. Since these two are typically the main detection vectors for offensive Powershell or .NET tradecraft, you are free to run the tools of your choice as you would in a normal Powershell. You don't have to worry about detection and can focus on simulating the attack + showing the worst case impact.
Constrained language mode active - not a problem here it's bypassed with the custom runspace.
This is definitely a time saver for your projects! 🔥 😎
#Pentest #RedTeam #Powershell
One more cool thing about #RustPack is, that you can create DLLs, which still return console output to the Operator.
This can be used, to for example execute C# binaries from within rundll32.exe or other processes - still getting the file output as usual. 🔥
So for Pentesters that don't use a C2 this can be used as alternative to running executables. Unsigned executables are much more flagged anyway nowadays and are not recommended to be used from us.
Or if you dont want to burn your C2 connection, drop a RustPack packed payload to disk and let it run standalone. 😎
Interested? Contact us via info[at]msecops[dot]de !
Entropy based detections are not a problem at all for #RustPack. All payloads by default end up in a normal to low overall entropy value. And the operator can on top choose between alternative payload encoding options. 😎
Alternatively, you can de-couple the encrypted payload from the final payload to retrieve/decrypt it on runtime.

Last Seen Hashtags on Sotwe
ebonyhotwife
Seen from Netherlands
monkeyapp
Seen from United States
incest #family #porn
CaughtOnCamera
Seen from Netherlands
live tango
Seen from Pakistan
aishortdrama
Seen from Malaysia
eşdeğişimi
Seen from Turkey
coser
Seen from Japan
snapchat()
Seen from Brazil
spankingdiscipline
Seen from Greece
Trends for you
Most Popular Users

Elon Musk 
@elonmusk
241.5M followers

Barack Obama
@barackobama
118.8M followers

Cristiano Ronaldo
@cristiano
114.5M followers

Donald J. Trump
@realdonaldtrump
111.8M followers

Narendra Modi
@narendramodi
107.1M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.3M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.5M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.5M followers

Bill Gates
@billgates
65.3M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.2M followers

CNN
@cnn
61.7M followers

X
@x
60.7M followers