

Top Tweets for #Windowsforensics

🔍 Malware survived a reboot.
Scheduled task? Service? Registry autorun? WMI subscription?
Persistence has many forms.
📚 Mastering Windows Incident Response
🎃 20% off Oct 23–31
HALLOWEEN26
https://t.co/kGYzR9IKHQ
#WindowsForensics #DFIR

#digitalforensics #computerforensics #Orionforensics #cyberforensics #Cybersecurity #Windowsforensics #IncidentResponse Orion provides a range of in-house digital forensics /Cyber Security training courses for investigators, auditors, IT staff, managers and legal teams.

🚨 Why did WINWORD.EXE launch PowerShell?
Parent-child process relationships can reveal suspicious execution.
Context matters.
📚 Mastering Windows Incident Response
20% off Oct 23–31
HALLOWEEN26
https://t.co/kGYzR9IcSi
#WindowsForensics
🖥️ The Windows Registry isn't just configuration data.
It can reveal user activity, persistence and valuable forensic clues.
Know where to look.
📚 Mastering Windows Incident Response
20% off Oct 23–31
HALLOWEEN26
https://t.co/kGYzR9IKHQ
#WindowsForensics
🔍 Malware deleted? Evidence may remain.
Prefetch, Amcache, Event Logs and Registry artifacts can help reconstruct Windows activity.
📚 Mastering Windows Incident Response
🎃 20% off Oct 23–31
HALLOWEEN26
https://t.co/kGYzR9IcSi
#WindowsForensics #DFIR

Don’t miss out, master Windows & Linux forensics! 💻🐧
The Dual-OS Masterpass (CCDFA & CCLFA) is extended until month’s end.
Secure your edge now!
🔗 https://t.co/c8hsqbdsTQ
#DigitalForensics #DFIR #CyberSecurity #CCDFA #CCLFA #Cyber5W #LinuxForensics #WindowsForensics

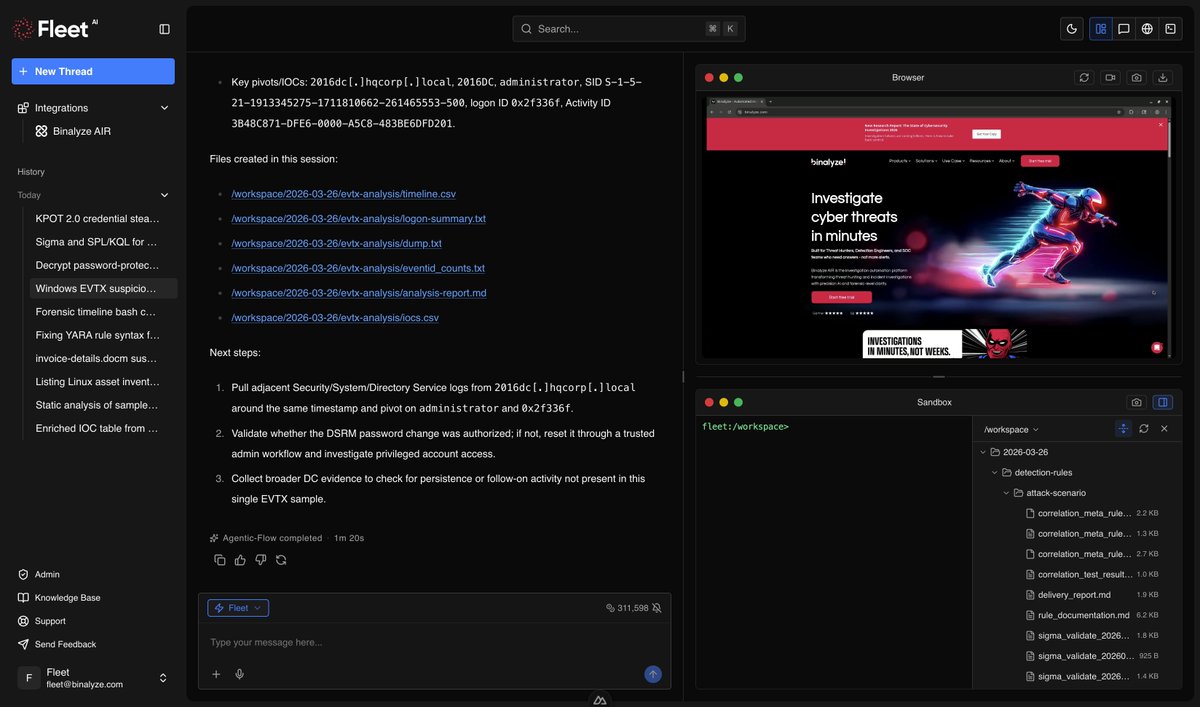
Drowning in EVTX data? Upload to Fleet and instantly surface authentication, escalation, and lateral movement events, risk-prioritized and timeline-ordered. Investigate smarter: https://t.co/qOVfTzSsrv #DFIR #WindowsForensics #ThreatHunting #IR #EDR #XDR #BlueTeam



A New #DFIR Peer-reviewed article has been published on @DFIRReview by "Is that Windows Notepad window really empty?" by Christopher Eng.
#WindowsForensics #DigitalForensics
https://t.co/U0xDiZ4uiO

Windows Forensics - Beginner-Friendly Overview
Windows Forensics focuses on the collection, preservation, and analysis of digital evidence from Windows systems following security incidents or cybercrime activity.
#WindowsForensics
#CyberSecurity
#IncidentResponse


🖥️ Windows Forensics — What Happened on This System?
#WindowsForensics
#DFIR
#CyberSecurity
#IncidentResponse
#DigitalForensics
#InfoSec
#BlueTeam

🚨 New Writeup Alert! 🚨
"Digital Forensics-[Ali Hadi — Mystery Hacked System Case]" by whoami is now live on IW!
Check it out here: https://t.co/S2ptZ2Y8zk
#digitalforensics #cybersecurity #incidentresponse #dfir #windowsforensics

KAPE: el framework que redefine el triage forense en minutos https://t.co/hWUK0ROOy3
#DFIR #DigitalForensics #ForensicTriage #MemoryForensics #WindowsForensics #DiskForensics #MalwareAnalysis #ArtifactAnalysis #IncidentResponse #ThreatHunting #ThreatDetection #ForensicTools

Worked through Windows Event Logs on @TryHackMe. Now I can map events to actions, filter noise, and find the signals that matter. #WindowsForensics #BlueTeam #SecurityOps

Sysmon on @TryHackMe changed how I see Windows events. Learning to trace processes, tune configs, and connect the dots finally made forensics click. #Sysmon #BlueTeam #WindowsForensics


⚠️ Disclaimer:
For educational and authorized use only. Always perform forensic analysis in a controlled, legal environment.
#WindowsForensics #DFIR #IncidentResponse #BlueTeamOps #CyberSecurity #MemoryForensics #RegistryAnalysis #SOCAnalyst #InfoSecTools #EducationOnly

Even if a shortcut sat idle on the desktop, Windows knows 👀
Just like the {F4E57C4B-2036-45F0-A9AB-443BCFE33D9F} key tracks what’s used (and what isn’t)…
Let your week track effort, not just intention.
💥 Take action.
📊 Leave artifacts.
#DFIR #WindowsForensics #CyberSecurity #MotivationMonday #BlueTeam #ThreatHunting
Disclaimer: This content is for educational and awareness purposes only. Always conduct forensic analysis in authorized and ethical contexts.
#WindowsForensics #DigitalForensics #CyberSecurityTraining #InfoSec #IncidentResponse #BlueTeam #ForensicAnalysis #EducationOnly #DFIR
🔍 Learn how to trace Windows program execution using artifacts like Prefetch, ShimCache & AmCache, and more.
🎯 Enroll in "Investigating Windows Program Executions" by Cyber5W:
👉 https://t.co/WwUGAxUgtf
#C5W #DFIR #DigitalForensics #WindowsForensics #CyberSecurity


Whether you’re a student, IT admin, or beginner in DFIR:
Always ask—who used this system before me?
And if someone’s missing, ask why?
#DigitalForensics #WindowsForensics #CyberAwareness #DFIR #Infosec
📢 Join our Windows Forensics Bootcamp – Live Training on May 15–16!
Learn hands-on skills in log analysis, registry forensics & more.
🎯 Instructor-led & interactive.
🔗 https://t.co/DCrfPrAXV2
#C5W #DFIR #WindowsForensics #CyberSecurity

Last Seen Hashtags on Sotwe
Unexpected
Seen from Turkey
mommy
Seen from India
minichat () filter:native_video
Seen from Ukraine
anxiouspanda
Seen from United States
minichat
marochienne filter:native_video
Seen from Netherlands
หาดใหญ่นัดเยด
Seen from Thailand
anxiouspandaa
Seen from United States
扮孕
Seen from United States
minichat video*
Seen from United States
Most Popular Users

Elon Musk 
@elonmusk
241.5M followers

Barack Obama
@barackobama
118.8M followers

Cristiano Ronaldo
@cristiano
114.5M followers

Donald J. Trump
@realdonaldtrump
111.8M followers

Narendra Modi
@narendramodi
107.1M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.3M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.5M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.5M followers

Bill Gates
@billgates
65.3M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.2M followers

CNN
@cnn
61.7M followers

X
@x
60.7M followers