Top Tweets for #cinoshi
@crep1x Some weeks ago I spottet a/this #Cinoshi campaign in the wild, distributed via #SmokeLoader.
You can find my findings here:
https://t.co/lBazqqu8BE
ThreatActors continue to amaze me.
#SmokeLoader -> Telegram Bio -> unidentified #Loader / #Stealer -> #CryptoMiner + #Ransomware + #RedLine
Triage:
https://t.co/d4cKdAL7QK
The initial bin dropped by #SmokeLoader is an unidentified Loader/Stealer :
hxxps://transfer.sh/get/oFBAuC/MavrodiBlack%202.exe
it first reaches out to:
hxxp://t.me/cinoshibot
from the bio, it gets the C2:
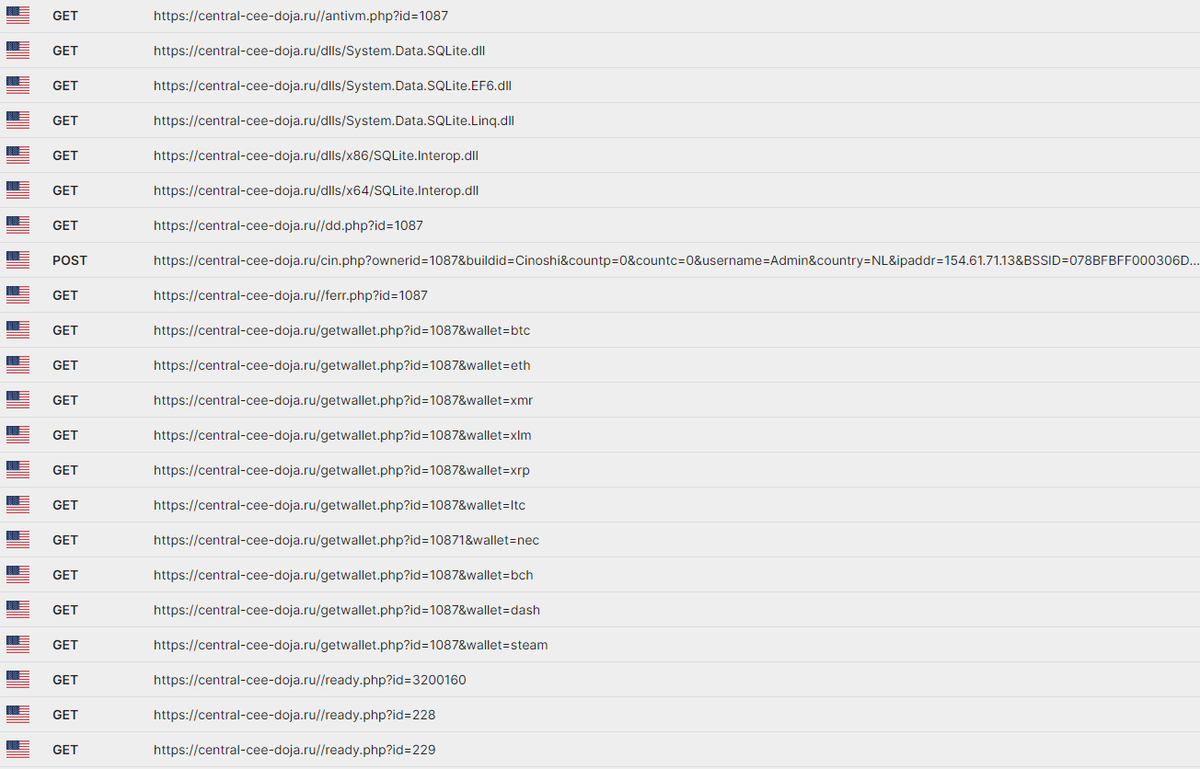
hxxps://central-cee-doja.ru
It then continuously reaches out to this address via different endpoints (see image below)
After successfully executing it loads 3 additional binaries:
1) hxxps://github.com/holdthismoney/icona/raw/main/version32.exe
2)
hxxps://github.com/MavrodiBlack/sturdy-potato/raw/main/MavrodiBlack.exe
3)
hxxps://transfer.sh/get/L0fiUE/[@]MavrodiBlack_alice.exe (without [])
1) loads a #CryptoMiner mining on hashvault[.]pro
(With extra feature of a reliable BlueScreen through pagefault error on Win10)
https://t.co/VOxtzfp4Fo
2) is a #Ransomware with some pretty cool animations. (Intezer: #GlobeImposter )
Actor: #JumperHacks
DecryptionKey via: t[.]me/Imthepassword
https://t.co/zqaN7Pv5qb
3) is #RedLine #Stealer with C2: 37.220.87[.]13:48790
@ET_Labs for detection rules on this noisy Stealer/Loader (maybe you also know what this is)
![Gi7w0rm's tweet photo. ThreatActors continue to amaze me.
#SmokeLoader -> Telegram Bio -> unidentified #Loader / #Stealer -> #CryptoMiner + #Ransomware + #RedLine
Triage:
https://t.co/d4cKdAL7QK
The initial bin dropped by #SmokeLoader is an unidentified Loader/Stealer :
hxxps://transfer.sh/get/oFBAuC/MavrodiBlack%202.exe
it first reaches out to:
hxxp://t.me/cinoshibot
from the bio, it gets the C2:
hxxps://central-cee-doja.ru
It then continuously reaches out to this address via different endpoints (see image below)
After successfully executing it loads 3 additional binaries:
1) hxxps://github.com/holdthismoney/icona/raw/main/version32.exe
2)
hxxps://github.com/MavrodiBlack/sturdy-potato/raw/main/MavrodiBlack.exe
3)
hxxps://transfer.sh/get/L0fiUE/[@]MavrodiBlack_alice.exe (without [])
1) loads a #CryptoMiner mining on hashvault[.]pro
(With extra feature of a reliable BlueScreen through pagefault error on Win10)
https://t.co/VOxtzfp4Fo
2) is a #Ransomware with some pretty cool animations. (Intezer: #GlobeImposter )
Actor: #JumperHacks
DecryptionKey via: t[.]me/Imthepassword
https://t.co/zqaN7Pv5qb
3) is #RedLine #Stealer with C2: 37.220.87[.]13:48790
@ET_Labs for detection rules on this noisy Stealer/Loader (maybe you also know what this is)](https://pbs.twimg.com/media/FwQHnHlXgAM-2Dt.jpg)
Cinoshi Stealer
bf39239f0b1526c68de99294e9c8ef5f
C2 : anaida.evisyn[.]lol
buildid=rocket
#CinoshiStealer #Stealer #IOC
![suyog41's tweet photo. Cinoshi Stealer
bf39239f0b1526c68de99294e9c8ef5f
C2 : anaida.evisyn[.]lol
buildid=rocket
#CinoshiStealer #Stealer #IOC https://t.co/93TfAyLXQa](https://pbs.twimg.com/media/FqxzdUoXsAEoUuG.jpg)
#ThreatProtection #Cinoshi #Malware-as-a-Service (#MaaS), read more about Symantec's protection: https://t.co/TnlO8gqtJB
Last Seen Hashtags on Sotwe
pasdevideo
Seen from United States
hijo mom
Seen from Chile
Ephrum
Seen from United States
minichat()**************** filter:videos since:2026-09-10
Seen from United States
freak
Seen from United States
anxiouspanda
Seen from Turkey
anxiouspanda (************************) filter:videos
anxiouspanda #minichat #snapchat
Seen from New Zealand
สุราษฎร์ธานี
Seen from Thailand
incestoconmama #madreehijo
Most Popular Users

Elon Musk 
@elonmusk
241.5M followers

Barack Obama 
@barackobama
118.9M followers

Cristiano Ronaldo 
@cristiano
114.6M followers

Donald J. Trump 
@realdonaldtrump
111.8M followers

Narendra Modi 
@narendramodi
107.1M followers

Rihanna 
@rihanna
98.7M followers

NASA 
@nasa
92.3M followers

Justin Bieber 
@justinbieber
91.8M followers

KATY PERRY 
@katyperry
90.1M followers

Taylor Swift 
@taylorswift13
84M followers

Lady Gaga 
@ladygaga
75.5M followers

Virat Kohli 
@imvkohli
73.5M followers

Kim Kardashian 
@kimkardashian
70.9M followers

YouTube 
@youtube
68.8M followers

Neymar Jr 
@neymarjr
66.6M followers

Bill Gates 
@billgates
65.3M followers

Selena Gomez 
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.2M followers

CNN 
@cnn
61.7M followers

X 
@x
60.7M followers

![Gi7w0rm's tweet photo. ThreatActors continue to amaze me.
#SmokeLoader -> Telegram Bio -> unidentified #Loader / #Stealer -> #CryptoMiner + #Ransomware + #RedLine
Triage:
https://t.co/d4cKdAL7QK
The initial bin dropped by #SmokeLoader is an unidentified Loader/Stealer :
hxxps://transfer.sh/get/oFBAuC/MavrodiBlack%202.exe
it first reaches out to:
hxxp://t.me/cinoshibot
from the bio, it gets the C2:
hxxps://central-cee-doja.ru
It then continuously reaches out to this address via different endpoints (see image below)
After successfully executing it loads 3 additional binaries:
1) hxxps://github.com/holdthismoney/icona/raw/main/version32.exe
2)
hxxps://github.com/MavrodiBlack/sturdy-potato/raw/main/MavrodiBlack.exe
3)
hxxps://transfer.sh/get/L0fiUE/[@]MavrodiBlack_alice.exe (without [])
1) loads a #CryptoMiner mining on hashvault[.]pro
(With extra feature of a reliable BlueScreen through pagefault error on Win10)
https://t.co/VOxtzfp4Fo
2) is a #Ransomware with some pretty cool animations. (Intezer: #GlobeImposter )
Actor: #JumperHacks
DecryptionKey via: t[.]me/Imthepassword
https://t.co/zqaN7Pv5qb
3) is #RedLine #Stealer with C2: 37.220.87[.]13:48790
@ET_Labs for detection rules on this noisy Stealer/Loader (maybe you also know what this is)](https://pbs.twimg.com/media/FwQHnGnXgAUWkn8.jpg)
![Gi7w0rm's tweet photo. ThreatActors continue to amaze me.
#SmokeLoader -> Telegram Bio -> unidentified #Loader / #Stealer -> #CryptoMiner + #Ransomware + #RedLine
Triage:
https://t.co/d4cKdAL7QK
The initial bin dropped by #SmokeLoader is an unidentified Loader/Stealer :
hxxps://transfer.sh/get/oFBAuC/MavrodiBlack%202.exe
it first reaches out to:
hxxp://t.me/cinoshibot
from the bio, it gets the C2:
hxxps://central-cee-doja.ru
It then continuously reaches out to this address via different endpoints (see image below)
After successfully executing it loads 3 additional binaries:
1) hxxps://github.com/holdthismoney/icona/raw/main/version32.exe
2)
hxxps://github.com/MavrodiBlack/sturdy-potato/raw/main/MavrodiBlack.exe
3)
hxxps://transfer.sh/get/L0fiUE/[@]MavrodiBlack_alice.exe (without [])
1) loads a #CryptoMiner mining on hashvault[.]pro
(With extra feature of a reliable BlueScreen through pagefault error on Win10)
https://t.co/VOxtzfp4Fo
2) is a #Ransomware with some pretty cool animations. (Intezer: #GlobeImposter )
Actor: #JumperHacks
DecryptionKey via: t[.]me/Imthepassword
https://t.co/zqaN7Pv5qb
3) is #RedLine #Stealer with C2: 37.220.87[.]13:48790
@ET_Labs for detection rules on this noisy Stealer/Loader (maybe you also know what this is)](https://pbs.twimg.com/media/FwQHnFRXoAICGSJ.jpg)
![Gi7w0rm's tweet photo. ThreatActors continue to amaze me.
#SmokeLoader -> Telegram Bio -> unidentified #Loader / #Stealer -> #CryptoMiner + #Ransomware + #RedLine
Triage:
https://t.co/d4cKdAL7QK
The initial bin dropped by #SmokeLoader is an unidentified Loader/Stealer :
hxxps://transfer.sh/get/oFBAuC/MavrodiBlack%202.exe
it first reaches out to:
hxxp://t.me/cinoshibot
from the bio, it gets the C2:
hxxps://central-cee-doja.ru
It then continuously reaches out to this address via different endpoints (see image below)
After successfully executing it loads 3 additional binaries:
1) hxxps://github.com/holdthismoney/icona/raw/main/version32.exe
2)
hxxps://github.com/MavrodiBlack/sturdy-potato/raw/main/MavrodiBlack.exe
3)
hxxps://transfer.sh/get/L0fiUE/[@]MavrodiBlack_alice.exe (without [])
1) loads a #CryptoMiner mining on hashvault[.]pro
(With extra feature of a reliable BlueScreen through pagefault error on Win10)
https://t.co/VOxtzfp4Fo
2) is a #Ransomware with some pretty cool animations. (Intezer: #GlobeImposter )
Actor: #JumperHacks
DecryptionKey via: t[.]me/Imthepassword
https://t.co/zqaN7Pv5qb
3) is #RedLine #Stealer with C2: 37.220.87[.]13:48790
@ET_Labs for detection rules on this noisy Stealer/Loader (maybe you also know what this is)](https://pbs.twimg.com/media/FwQHnE8WAAMKwXs.png)

![crep1x's tweet photo. #Cinoshi stealer uses a Telegram channel as a Dead Drop Resolver (DDR), just like #Vidar stealer
DDR: hxxps://t.]me/cinoshibot
C2: hxxps://central-cee-doja.]ru/
The number of samples communicating with the DDR suggests that the malware is rather well distributed. https://t.co/zKPDfR0oxf](https://pbs.twimg.com/media/Fx36WLiWAAA8W3G.jpg)
![crep1x's tweet photo. #Cinoshi stealer uses a Telegram channel as a Dead Drop Resolver (DDR), just like #Vidar stealer
DDR: hxxps://t.]me/cinoshibot
C2: hxxps://central-cee-doja.]ru/
The number of samples communicating with the DDR suggests that the malware is rather well distributed. https://t.co/zKPDfR0oxf](https://pbs.twimg.com/media/Fx36TuLWcAA1JZ4.jpg)

![suyog41's tweet photo. Cinoshi Stealer
bf39239f0b1526c68de99294e9c8ef5f
C2 : anaida.evisyn[.]lol
buildid=rocket
#CinoshiStealer #Stealer #IOC https://t.co/93TfAyLXQa](https://pbs.twimg.com/media/FqxzdNuWYAYMpva.png)
![suyog41's tweet photo. Cinoshi Stealer
bf39239f0b1526c68de99294e9c8ef5f
C2 : anaida.evisyn[.]lol
buildid=rocket
#CinoshiStealer #Stealer #IOC https://t.co/93TfAyLXQa](https://pbs.twimg.com/media/FqxzdIoXwAAYXp-.png)