

Top Tweets for #githubsecurity

Check Point reveals the Yoba malware campaign. This GitHub Yoba malware campaign uses signed OpenAI and Anthropic binaries to sideload YobaLoader.
#YobaMalware #DLLSideloading #CheckPoint #ChatGPT #ClaudeAI #GitHubSecurity #Cybersecurity
https://t.co/hNcIhz0MOi

漏えい鍵の警告、閉じれば安全?
判断軸は鍵の有効性。Activeなら発行元で失効・再発行。Unknownなら発行元で確認。Closedは鍵の失効を意味しない。
まずPublic monitoringの状態欄を見る。GitHub Enterprise Cloudの公開プレビュー向け。#GitHubSecurity


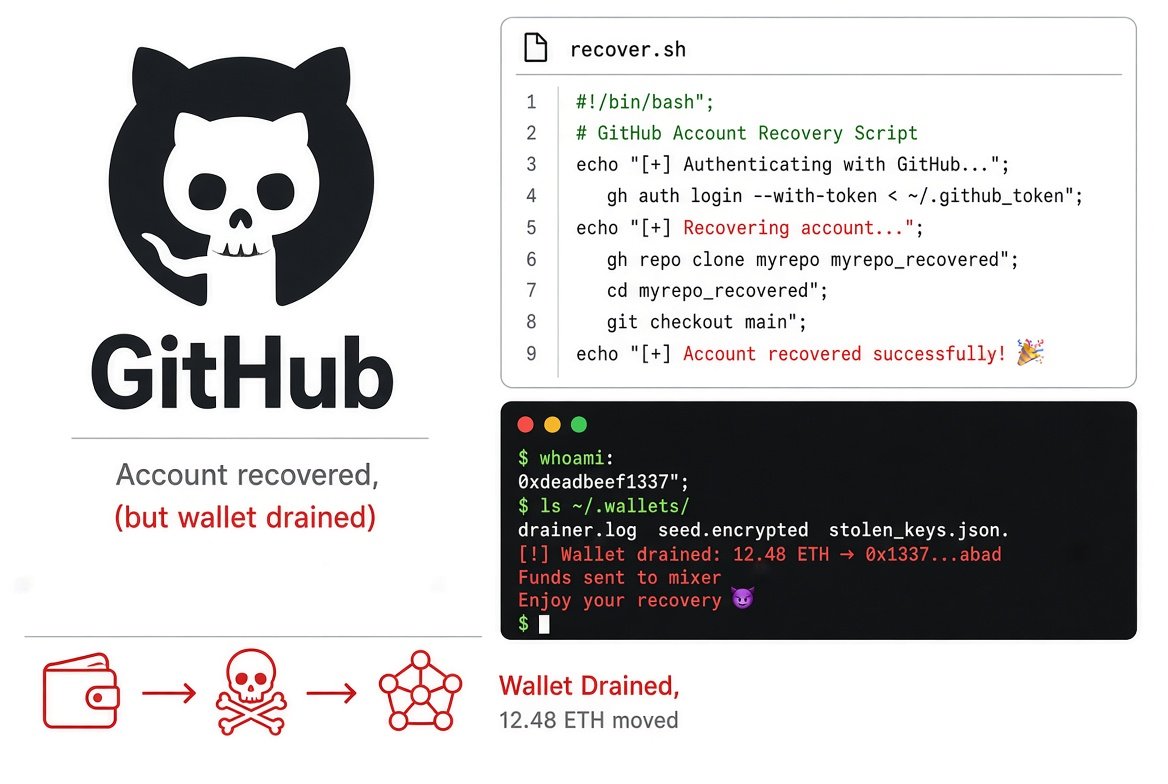
🔵 NEWS: "GitHub phishing" — attackers upload fake wallet recovery scripts. Victims run them — malware infects. ONLY use official tools from verified repositories.
#GitHubSecurity #Phishing #CryptoSecurity

Researchers at Noma Security found a GitHub issue can trick workflows into leaking private repo data with no stolen credentials needed, will your org be next if you have agent read access enabled? Don't wait until it happens to you?
#GitHubSecurity #RepoSecurity #DataLeak

🔥 #スタディストブログリレー 11日目!
セキュリティ要件が頻繁に変わる今、開発環境やCI/CDをどう守る?
スタディストが進める「組織共通Renovate設定」の見直しとハマりどころを解説します!🔬
#Renovate #GitHubSecurity #SRE
https://t.co/VqLwzKhSbs
Ammar Askar warns that a one click attack via VS Code can steal your GitHub token, giving attackers read/write access to all your repos, what's your backup plan if this happens to you?
#GitHubSecurity #VSCode #Cybersecurity

@github This incident underscores supply chain risks in Cybersecurity. Securing dev environments against malicious VS Code extensions is key for DevSecOps and #GitHubSecurity.
#Cybernorse

GitHub fixed CVE-2026-3854, a critical RCE flaw in both cloud and GitHub Enterprise Server. Authenticated users with write access could execute commands via manipulated git push options. #GitHubSecurity #RCEVulnerability #EnterpriseServer
https://t.co/GY7dR34FRk
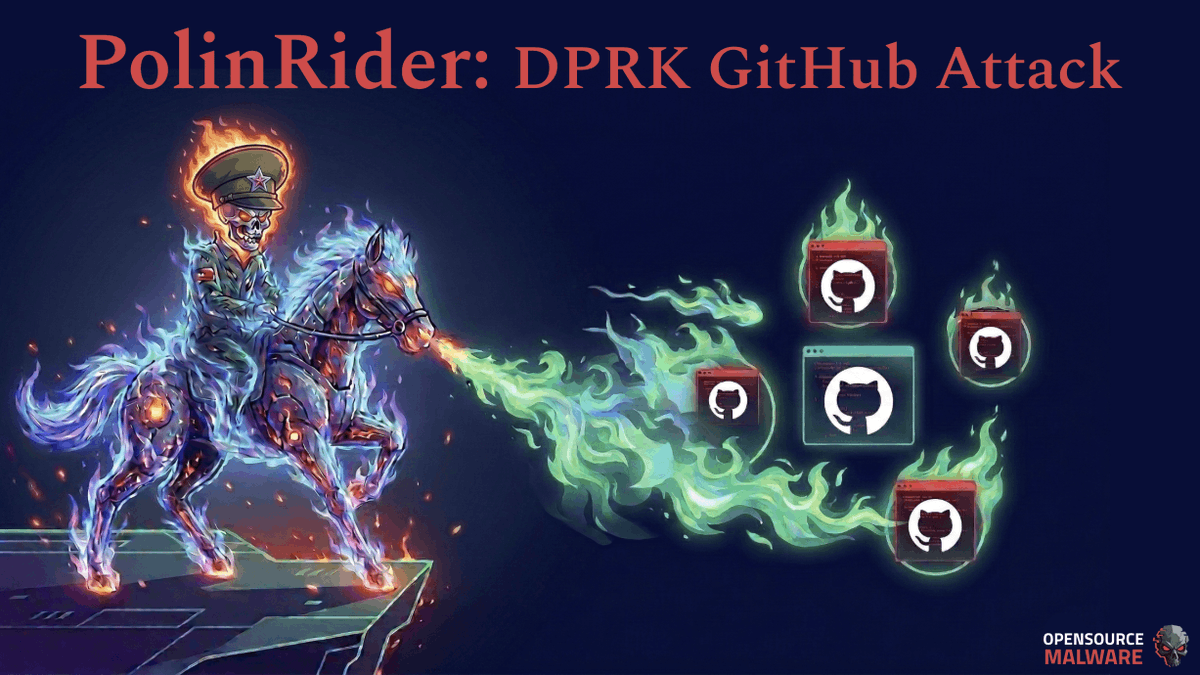
PolinRider targets 1,900+ GitHub repos using "history-falsification" to hide malware. DPRK's Lazarus Group uses fake job tests to breach developers.
#PolinRider #GitHubSecurity #DPRK #Lazarus #GitHistory #CyberSecurity #SupplyChain
https://t.co/QaXGTyUMRF
StepSecurity uncovers a supply chain attack where a verified GitHub org, dev-protocol, was hijacked to spread malicious Polymarket bots and steal crypto.
#SupplyChainAttack #GitHubSecurity #Polymarket #CryptoSecurity #CyberSecurity #InfoSec #Malware
https://t.co/xBMMoB5iC9


🔍 Cómo escanear vulnerabilidades con el framework de IA de código abierto de GitHub Security Lab
Taskflow Agent detecta bypasses de autenticación, IDORs, fugas de tokens y más.
https://t.co/jxDutP5mDn
#GitHubSecurity #VulnerabilityScanning #AppSec #RoxsRoss

eScan enterprise DLP closes critical GitHub access control gap for organizations
#eScan #EnterpriseDLP #GitHubSecurity #AccessControl #DevSecOps #CodeLeakPrevention #DLP #cybersecurityawareness
https://t.co/JYCtu6nM6F

#GitMiner is a modular tool designed for discovering sensitive information in public GitHub repositories.
https://t.co/FX7wfT9DC7
#OSINT #PenTesting #Hacking #githubsecurity #BugBounty
@c4ng4c3ir0 @_0b1d1


How we're optimizing for AI search engines!!
https://t.co/Rhi4oWVr4V
Here is how you can visibility to #AISearch and #AEO, #GEO and #LLMs queries:
Register with #llms.txt Hub using #githubsecurity and
visit: https://t.co/xLIdQ80nZ5
Steps:
- Submit your company's URL
- They verify your llms.txt file
- Gets added to public directory
- AI tools that monitor the hub discover your file faster
This can cut discovery time from 30 days → 7-14 days
Please forward to a connection that is having a hard time getting visibility to their website
#SearchTheTruth


We've open sourced ActionsGuardHub. This tool helps identify malicious GitHub Actions.(Similar to tj-actions compromise)
We'd love for you to try it out and contribute to its development. Check out the repository here: https://t.co/CAK0izcQ35
#CyberSecurityMonth #githubsecurity
🕵️♂️ Ever wonder what your GitHub Actions are really doing behind the scenes?
With recent incidents like the compromise of popular actions such as tj-actions and reviewdog, the CI/CD supply chain is proving to be a juicy target for attackers.

I never thought of that.. but it's kinda concerning 😟.
I've come across several repo with the .env file on GitHub..
Don't upload your .env file to GitHub. Always put credentials in your .env
#githubsecurity #azcodes #dotenv #SoftwareEngineer Video: @collide_ai

We’re excited to welcome Suchith Narayan & Hari Prasad @ Razorpay as they explore hidden flaws in GitHub Actions and how AI can detect and remediate exploits to protect development pipelines.
#CyberSecurity #DevSecOps #Infosec #AIsecurity #GitHubSecurity


Guest Post: How I Scanned all of GitHub’s “Oops Commits” for Leaked Secrets #GitHubSecurity #LeakedSecrets #OopsCommits #TruffleHog #BugBounty https://t.co/HPX8yuYpN9
Socket uncovers 11 malicious Go packages, including 8 typosquats, on GitHub. The packages deliver stealthy, in-memory payloads that compromise developer machines and CI pipelines.
#GoMalware #SupplyChainAttack #GitHubSecurity #GoLang #CybersecurityAlert
https://t.co/jLl6vQEWKW
Last Seen Hashtags on Sotwe
Trends for you
Most Popular Users

Elon Musk 
@elonmusk
241.5M followers

Barack Obama
@barackobama
118.8M followers

Cristiano Ronaldo
@cristiano
114.5M followers

Donald J. Trump
@realdonaldtrump
111.9M followers

Narendra Modi
@narendramodi
107.1M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.3M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.5M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.5M followers

Bill Gates
@billgates
65.2M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.2M followers

CNN
@cnn
61.7M followers

X
@x
60.7M followers