

Top Tweets for #optimjack

Having SRI would stop OPTIMJACK. Something mostly rate as INFORMATIONAL. Try this challenge to learn how to use it in your frontend. #optimjack

Malicious code injected into Optimizely reached 178 websites via its CDN, which lacked an integrity check.
SRI makes browsers refuse a script that fails its hash.
Our CSP challenge is inspired by this. Can you fix the bug?
#Optimizely #OPTMJACK #SupplyChainAttack


Only 15% had CSP strict enough to block it. Audit Project JS, enforce strict CSP, rotate tokens.
#OPTIMJACK #SupplyChain #Optimizely #CyberSecurity #infosec

Zoom, BBC & 175+ sites served Optimizely CDN JS—zero internal breach.
▸ 188 Project JS snippets hit (1688360[.]cc)
▸ Crypto-clipper, skimmer & iOS kits
▸ Lock CSP
Read: https://t.co/dKemMiBe0O
#sh3llc0d3 #shellcode #SupplyChain #OPTIMJACK

7/7 What happened, and 6 checks to run immediately
https://t.co/FVRP3VFg0G #OPTIMJACK #Magecart #WebSecurity
3/7 What it did: a #Magecart skimmer copied card numbers, expiry dates and CVVs from checkout forms. It also swapped crypto wallet addresses, grabbed cookies and screenshots, and hit iPhones with exploit kits. #CardSkimming #OPTIMJACK
1/7 On Nov 16, #Optimizely's A/B testing script started stealing card numbers and crypto from visitors to 178 companies' websites. Those companies weren't hacked. Their vendor was. Here's why that matters. 🧵 #OPTIMJACK #SupplyChainAttack

An A/B testing script stole card numbers on 178 companies' sites for ~16 hours. Security let it run because it came from an approved vendor, #Optimizely. #OPTIMJACK Our view: judge a script by what it does, not where it comes from. #Magecart #PCIDSS https://t.co/FVRP3VFg0G


Neben CNN, BBC, Zoom, Salesforce, GitLab, IKEA, HSBC, Equifax, Air France-KLM, Ledger und Peacock. Auch die eigene Hauptseite und Anmeldeseite des Anbieters enthielt den Code. Einige Forscher nennen die Kampagne #OPTIMJACK .
https://t.co/p4IKgzaQ8l


178 orgs. 1 hacked CDN. 17 hrs.
OPTIMJACK hit BBC, CNN, Zoom, Salesforce via Optimizely's CDN - card skimmers, crypto clippers, iOS exploit, all from a trusted script.
Check Optimizely snippet for "1688360" today.
https://t.co/LnC0olEOo7 #CyberSecurity #OPTIMJACK

OPTIMJACK: a third-party script loader slips wallet swappers and card skimmers onto CNN and Zoom. https://t.co/k4H99nK88z #ThreatIntel #html2canvas #OPTIMJACK #SupplyChain

#Companies spend millions hardening servers, networks and identity systems. #OPTIMJACK bypassed all of it without touching any of it. The attacker did not need to breach #HSBC or #Zoom; they only needed to breach something that HSBC and Zoom trusted. https://t.co/u3ME8sC6jG

💳 Watch your bank and card statements for small charges you don't recognize
🔐 If you entered card details on a big site Monday, call your bank and get a new card number
Stay alert. Stay ready. Stay united. 🇺🇸
#SITREP #CyberSecurity #OPTIMJACK

#OPTIMJACK: #BBC, #CNN and #Zoom Among Targets of Optimizely Script Hijacking
https://t.co/5KAUKs1Ts7
#securityaffairs #hacking #malware #eskimmer
@reporturi
Optimizely's CDN served a card skimmer and crypto clipper to CNN, BBC and Zoom visitors. https://t.co/rJ7SHzAKg1 #ThreatIntel #Coruna #DarkSword #OPTIMJACK

🚨 Cyber Security Alert!
Dangerous malware has reportedly been found on the websites of 178+ major companies in the OPTIMJACK cyber attack. Websites like CNN, BBC, Zoom, Salesforce, and IKEA are also reported to be affected.
#CyberAttack #OPTIMJACK #CyberSecurity

#OPTIMJACK
暴露了一个容易忽视的问题:你打开的可以是真实网站,地址正确,也有 HTTPS
但页面加载的第三方脚本���可能带有恶意代码。
网站可信,不代表它加载的每一项依赖始终可信。
#optimjack 😂
1/10 OPTIMJACK exposed a gap between trusting a website and trusting everything it loads. A legitimate URL and HTTPS can coexist with malicious third-party JavaScript running inside the page.
2/10 Optimizely confirmed that an Experimentation flaw allowed malicious JavaScript in customer projects. It says the flaw is fixed and injected code removed. That is containment, not proof that earlier visits caused no harm.
3/10 Report URI found 188 infected snippets associated with 178 organizations. Those are different units, not visitor counts. Imported scripts can act within the host page; a trusted delivery domain does not make their contents safe.
4/10 Researchers reported address swapping, card-form skimming and mobile payload delivery. A copied crypto address can be replaced before payment. Keep script delivery, data theft and successful device compromise separate.
5/10 Page scripts cannot simply read your entire phone. Cross-origin payment fields and HttpOnly cookies create useful boundaries. Neither makes the whole page safe. Attacker wallet inflows also need attribution before being called victim losses.
6/10 Before signing, check the full destination, network and amount against an independently verified source. On hardware wallets, check the device screen too. A correct test transfer does not verify the destination of your next transfer.
7/10 Update your OS and browser. If exposed, review relevant transfers, card activity and sessions. Contact providers through official channels about anomalies. Visiting a listed site alone does not establish that your wallet keys or device were compromised.
8/10 Site owners: remove unnecessary scripts from login and payment pages. Inventory the rest, restrict publishing access, require strong authentication and review changes. Monitor content changes and unexpected destinations. Test an emergency disable switch.
9/10 Enforce CSP; Report-Only only reports. Use SRI for reviewed, pinned assets; it does not automatically cover later loads. Restricting data destinations cannot stop every local page change. Preserve evidence while containing exposure.
10/10 For every third-party script: what can it read, what can it change, and how quickly can you stop it?
Sources (Nov 17, 2026):
Optimizely incident
Report URI research

One compromised Optimizely script turned trusted websites into theft tools. If you copy-paste wallet addresses, read this before your next transfer.
#Crypto #Cybersecurity #Optimjack
https://t.co/eLFUfsuFON

As predicted, November 17. This is BIG. 🚨
A major supply-chain cyberattack has hit 178 organisations worldwide, including BBC, CNN, Fox News, Zoom, HSBC, Salesforce, IKEA, Equifax, Ledger and Air France-KLM.
The attack, dubbed #Optimjack, exploited Optimizely Web to inject malicious JavaScript into trusted websites.
And the payload was frightening:
🔴 Stole payment card details
🔴 Replaced copied cryptocurrency wallet addresses
🔴 Stole browser cookies and screenshots
🔴 Targeted iPhones and iPads using Coruna and DarkSword exploit kits
Researchers identified 188 compromised scripts after examining 1,611 Optimizely snippets.
Banking and financial services were the worst-hit sector, with 32 organisations affected.
The important distinction: these were compromised website scripts, not necessarily breaches of the companies' internal networks.
Most malicious scripts had been removed by late November 16, according to Report URI.
But here's the bigger concern:
If we cannot trust the third-party services powering the websites we visit, how safe are we online?
Full investigation: https://t.co/nHt5olpWVK

🚨 Ataque de #malaware en cadena de suministro #OPTIMJACK capaz de robar información financiera y desviar #criptomonedas afecto sitios web mediante scripts maliciosos alojados en la plataforma #Optimizely Aunque el código malicioso fue borrado se desconocen sus alcances 🤯

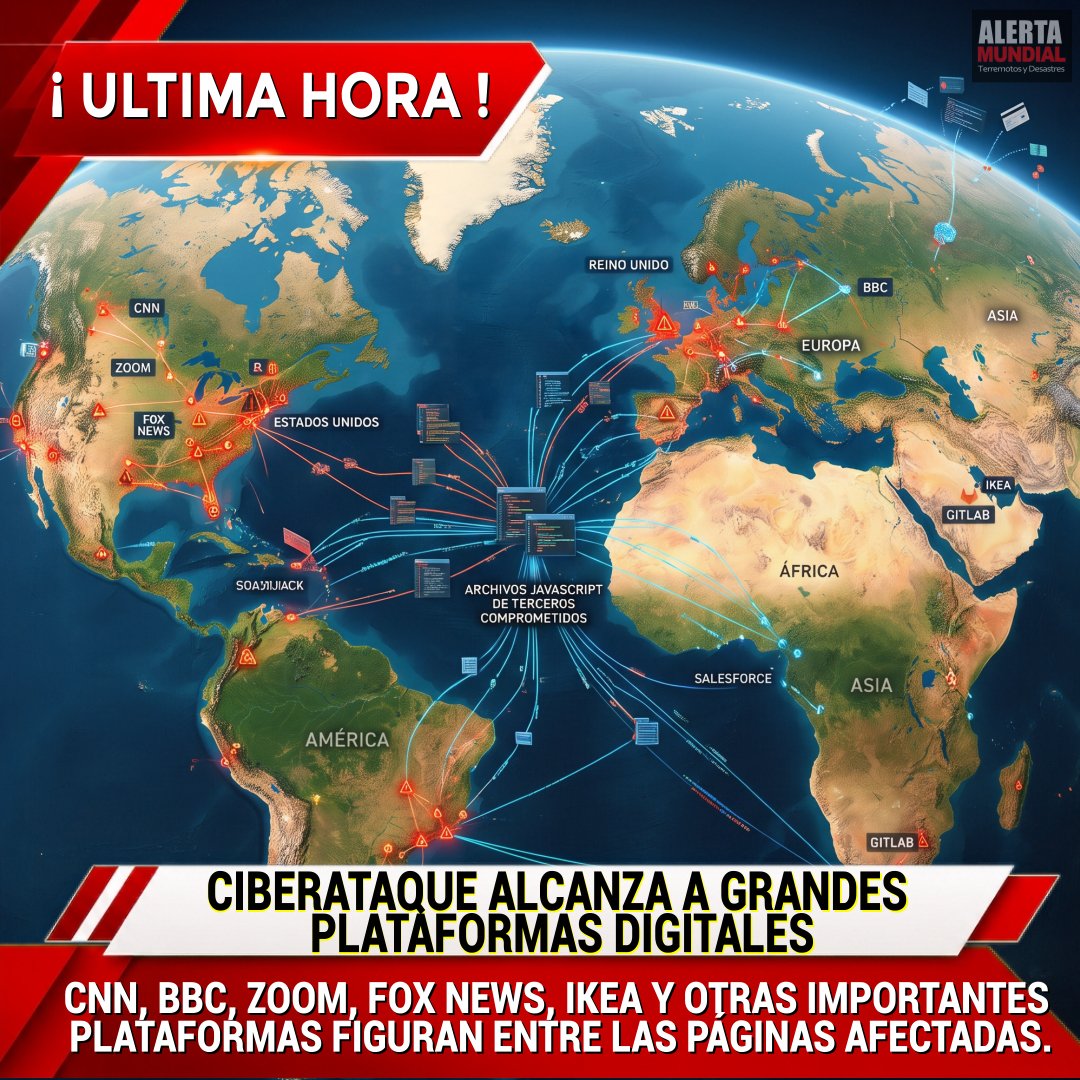
🌐 186 SITIOS WEB DE IMPORTANTES EMPRESAS Y MEDIOS FUERON COMPROMETIDOS POR CIBERATAQUE
Este lunes 16 de noviembre de 2026, investigadores de ciberseguridad identificaron una campaña maliciosa denominada OPTIMJACK que comprometió componentes informáticos utilizados por al menos 186 sitios web. Entre las páginas afectadas figuran CNN, BBC, Fox News, Zoom, Salesforce, GitLab, IKEA y otras plataformas internacionales.
El ataque aprovechó archivos de JavaScript asociados a herramientas de terceros utilizadas por estas páginas para personalizar sus contenidos y servicios. La presencia de código malicioso en esos componentes permitió que visitantes de sitios legítimos pudieran quedar expuestos a funciones diseñadas para robar información financiera, capturar datos de navegación y sustituir direcciones de billeteras de criptomonedas.
La investigación identificó 188 archivos infectados pertenecientes a 178 organizaciones. Aunque durante la noche del 16 de noviembre se había eliminado prácticamente todo el código comprometido, los investigadores todavía desconocían cuántos visitantes pudieron resultar afectados y qué cantidad de información personal fue sustraída.
Last Seen Hashtags on Sotwe
Kitchen hairy
Seen from France
bursatravesti
Seen from Turkey
madre
Seen from Brazil
anxiouspanda()******************************* filter:native_video
Seen from Turkey
niktounsi
brosis
Seen from United States
hotwife
Seen from Indonesia
고영희
Seen from Korea
siliconedoll
Seen from United States
sissyitalia
Seen from Italy
Most Popular Users

Elon Musk 
@elonmusk
240.5M followers

Barack Obama
@barackobama
118.7M followers

Cristiano Ronaldo
@cristiano
114.4M followers

Donald J. Trump
@realdonaldtrump
111.8M followers

Narendra Modi
@narendramodi
107M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.2M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.4M followers

Kim Kardashian
@kimkardashian
70.8M followers

YouTube
@youtube
68.7M followers

Neymar Jr
@neymarjr
66.4M followers

Bill Gates
@billgates
65.2M followers

Selena Gomez
@selenagomez
63M followers

The Ellen Show
@theellenshow
62.1M followers

CNN
@cnn
61.7M followers

X
@x
60.6M followers