Top Tweets for #rdpwrap
#JavaSTRRAT #Ransomware #RDPWrap #Malware #Cyberrime #CyberAttack #CyberSecurity
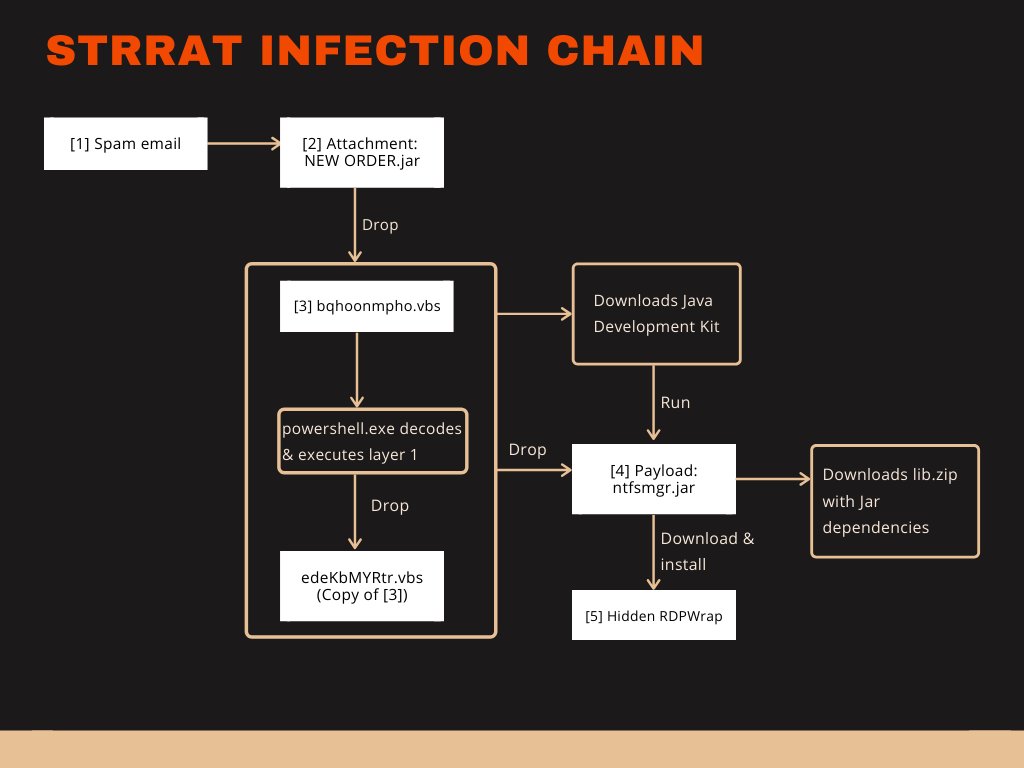
This Java based malware installs RDPWrap, steals credentials, logs keystrokes and remote controls Windows systems. It may soon be capable to infect without Java installed.
https://t.co/xmAr6Z6Gw9

Blog article: Java ☕️ based RAT named STRRAT installs RDPWrap and has a ransomware module (".crimson" ext.)
🦔🦔🦔
➡️https://t.co/EQwqgIUs1V
#Java #RAT #STRRAT #RDPWrap #ransomware #crimson #GDATATechblog @GDATA
2019-05-10: #MegaCortex #Ransomware Additional IOCs Released by @SophosLabs |
https://t.co/0rqP6yuPG5 ✔️
It is notable that "PRO-STO, TOV" cert name was part of many malware
incl #RDPWrap -> #CobaltStrike Payload
As discovered by @malwrhunterteam 👍
e.g https://t.co/rvCXXzaGmu

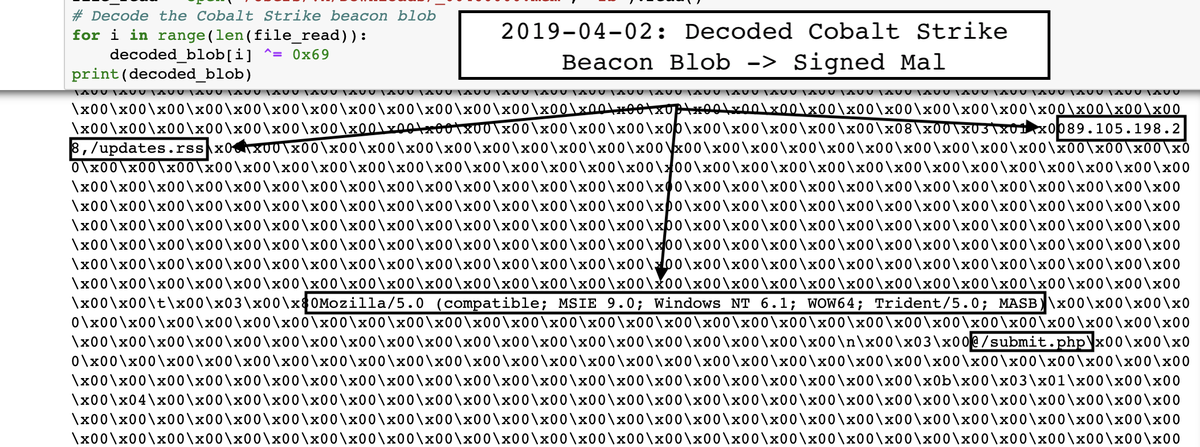
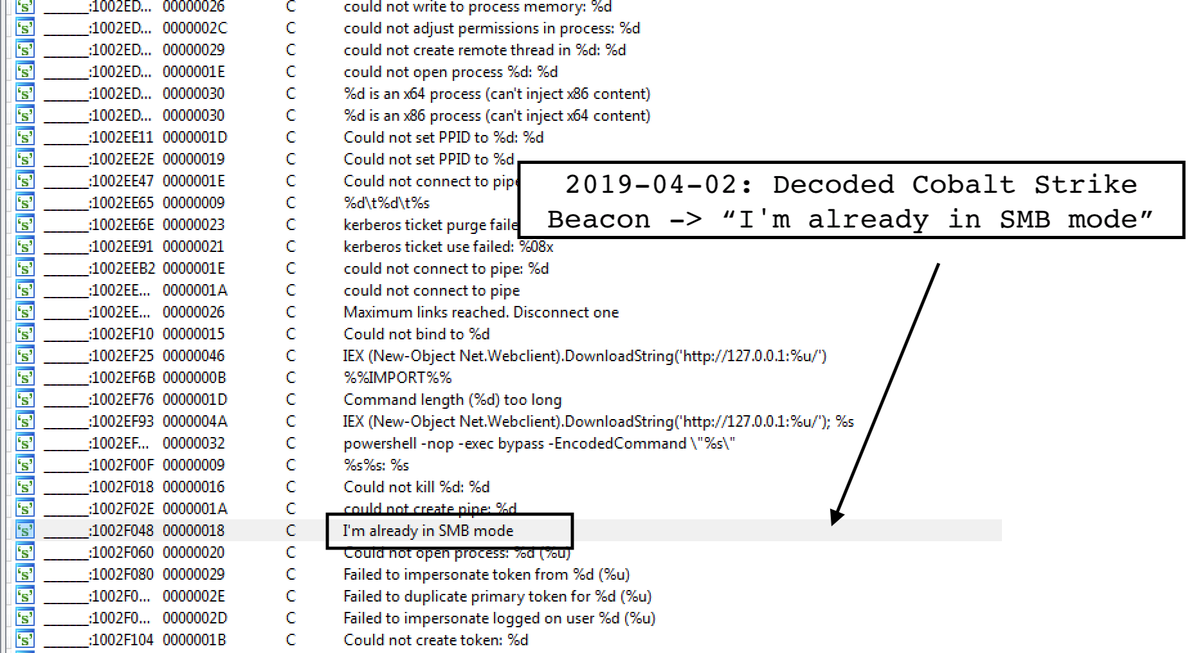
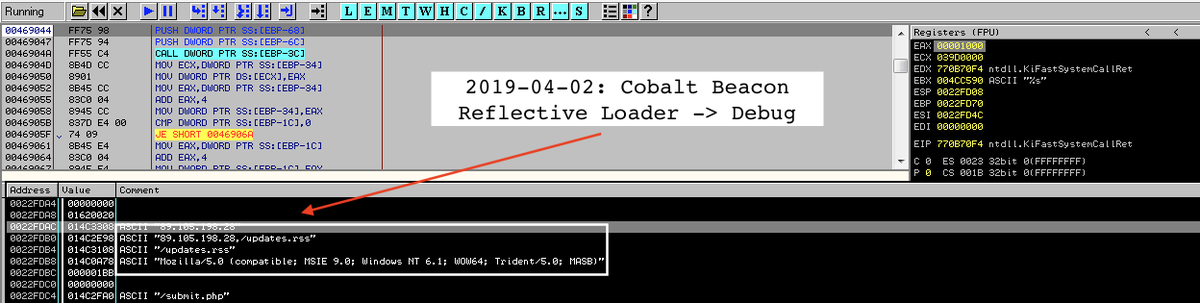
2019-04-02: Signed #Malware Loader -> Reflective #CobaltStrike Beacon
h/t @malwrhunterteam
Signed "PRO-STO, TOV" as #RDWRap Malware Chain Before 🧐 | Sectigo
C2: 89.105.198[.]28/updates.rss | command.php
🔦"I'm already in SMB mode"
😉Decoded XOR 0x69 / Unpacked First-Stage 🛡️
![VK_Intel's tweet photo. 2019-04-02: Signed #Malware Loader -> Reflective #CobaltStrike Beacon
h/t @malwrhunterteam
Signed "PRO-STO, TOV" as #RDWRap Malware Chain Before 🧐 | Sectigo
C2: 89.105.198[.]28/updates.rss | command.php
🔦"I'm already in SMB mode"
😉Decoded XOR 0x69 / Unpacked First-Stage 🛡️ https://t.co/pn3tjEms8y](https://pbs.twimg.com/media/D3IaiMoWsAE4YaI.png)
2019-03-30: Signed #Malware -> #RDPWrap Concurrent Session/Browser Stealer via #PowerShell & SSH Tunnel 🧐
h/t @malwrhunterteam 👍
Digital Certificate: "PRO-STO, TOV" | Sectigo
Payload URL: ref345[.]icu
🛡️Pushed my RE Notebook & IOCs in #MISP #JSON/CSV
https://t.co/zZbWRle3s7
![VK_Intel's tweet photo. 2019-03-30: Signed #Malware -> #RDPWrap Concurrent Session/Browser Stealer via #PowerShell & SSH Tunnel 🧐
h/t @malwrhunterteam 👍
Digital Certificate: "PRO-STO, TOV" | Sectigo
Payload URL: ref345[.]icu
🛡️Pushed my RE Notebook & IOCs in #MISP #JSON/CSV
https://t.co/zZbWRle3s7 https://t.co/jXk9JVKr8i](https://pbs.twimg.com/media/D29qundX4AAfwhZ.jpg)
Last Seen Hashtags on Sotwe
vazouvideo
Seen from Germany
minichat
Seen from Argentina
ipcam
拳交
Seen from Singapore
minichatt ()()()()()********************************************* filter:videos
Seen from Portugal
painful anal
Brosis(***) +filter:native_video since:2026-03-30
Seen from Germany
bops #joi
Seen from United Kingdom
MVSales
Seen from Saudi Arabia
chinese #porn
Seen from Indonesia
Trends for you
Most Popular Users

Elon Musk 
@elonmusk
241.5M followers

Barack Obama 
@barackobama
118.8M followers

Cristiano Ronaldo 
@cristiano
114.5M followers

Donald J. Trump 
@realdonaldtrump
111.9M followers

Narendra Modi 
@narendramodi
107.1M followers

Rihanna 
@rihanna
98.7M followers

NASA 
@nasa
92.3M followers

Justin Bieber 
@justinbieber
91.8M followers

KATY PERRY 
@katyperry
90M followers

Taylor Swift 
@taylorswift13
84M followers

Lady Gaga 
@ladygaga
75.5M followers

Virat Kohli 
@imvkohli
73.5M followers

Kim Kardashian 
@kimkardashian
70.9M followers

YouTube 
@youtube
68.8M followers

Neymar Jr 
@neymarjr
66.5M followers

Bill Gates 
@billgates
65.3M followers

Selena Gomez 
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.2M followers

CNN 
@cnn
61.7M followers

X 
@x
60.7M followers


![VK_Intel's tweet photo. 2019-04-02: Signed #Malware Loader -> Reflective #CobaltStrike Beacon
h/t @malwrhunterteam
Signed "PRO-STO, TOV" as #RDWRap Malware Chain Before 🧐 | Sectigo
C2: 89.105.198[.]28/updates.rss | command.php
🔦"I'm already in SMB mode"
😉Decoded XOR 0x69 / Unpacked First-Stage 🛡️ https://t.co/pn3tjEms8y](https://pbs.twimg.com/media/D3IagfqXgAAOVYH.png)
![VK_Intel's tweet photo. 2019-04-02: Signed #Malware Loader -> Reflective #CobaltStrike Beacon
h/t @malwrhunterteam
Signed "PRO-STO, TOV" as #RDWRap Malware Chain Before 🧐 | Sectigo
C2: 89.105.198[.]28/updates.rss | command.php
🔦"I'm already in SMB mode"
😉Decoded XOR 0x69 / Unpacked First-Stage 🛡️ https://t.co/pn3tjEms8y](https://pbs.twimg.com/media/D3IaewFXQAEiJF0.png)
![VK_Intel's tweet photo. 2019-03-30: Signed #Malware -> #RDPWrap Concurrent Session/Browser Stealer via #PowerShell & SSH Tunnel 🧐
h/t @malwrhunterteam 👍
Digital Certificate: "PRO-STO, TOV" | Sectigo
Payload URL: ref345[.]icu
🛡️Pushed my RE Notebook & IOCs in #MISP #JSON/CSV
https://t.co/zZbWRle3s7 https://t.co/jXk9JVKr8i](https://pbs.twimg.com/media/D29quAQXQAA0lBc.png)
![VK_Intel's tweet photo. 2019-03-30: Signed #Malware -> #RDPWrap Concurrent Session/Browser Stealer via #PowerShell & SSH Tunnel 🧐
h/t @malwrhunterteam 👍
Digital Certificate: "PRO-STO, TOV" | Sectigo
Payload URL: ref345[.]icu
🛡️Pushed my RE Notebook & IOCs in #MISP #JSON/CSV
https://t.co/zZbWRle3s7 https://t.co/jXk9JVKr8i](https://pbs.twimg.com/media/D29qsiYWsAAhQSz.png)

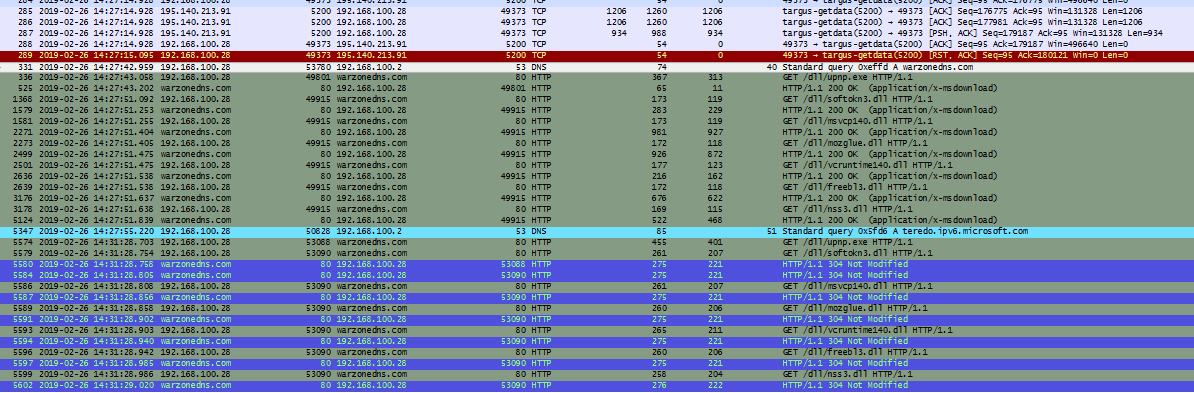
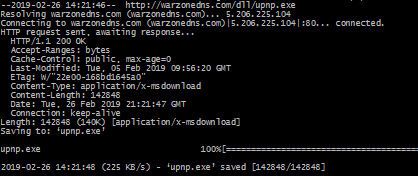
![James_inthe_box's tweet photo. #avamaria via #malspam, drops a curious helper at:
warzonedns[.]com/dll/upnp.exe
to enable 3389 in the firewall via netsh
uses #uacme and #rdpwrap
https://t.co/juT85usEGS
https://t.co/TzILFrSFp1
https://t.co/pOqCmnoQcL
c2's: 195.140.213[.]91
warzonedns[.]com https://t.co/4NqAfq9HFy](https://pbs.twimg.com/media/D0XMi4UUUAI9Pjl.png)
![James_inthe_box's tweet photo. #avamaria via #malspam, drops a curious helper at:
warzonedns[.]com/dll/upnp.exe
to enable 3389 in the firewall via netsh
uses #uacme and #rdpwrap
https://t.co/juT85usEGS
https://t.co/TzILFrSFp1
https://t.co/pOqCmnoQcL
c2's: 195.140.213[.]91
warzonedns[.]com https://t.co/4NqAfq9HFy](https://pbs.twimg.com/media/D0XMejCVsAAtcju.png)