

Top Tweets for #sinobi

10/21本日の入荷です☺️
#ウマ娘プリティーダービーうまむすめし 8巻
#ウマ娘プリティーダービースターブロッサム 7巻
#Sinobi 4巻 完結‼️
#これってハラスメントですか? 5巻
#デスレスブライド 1巻
#DINER 27巻
#ミナミザスーパーエボリューション 4巻
#終の退魔師 27巻

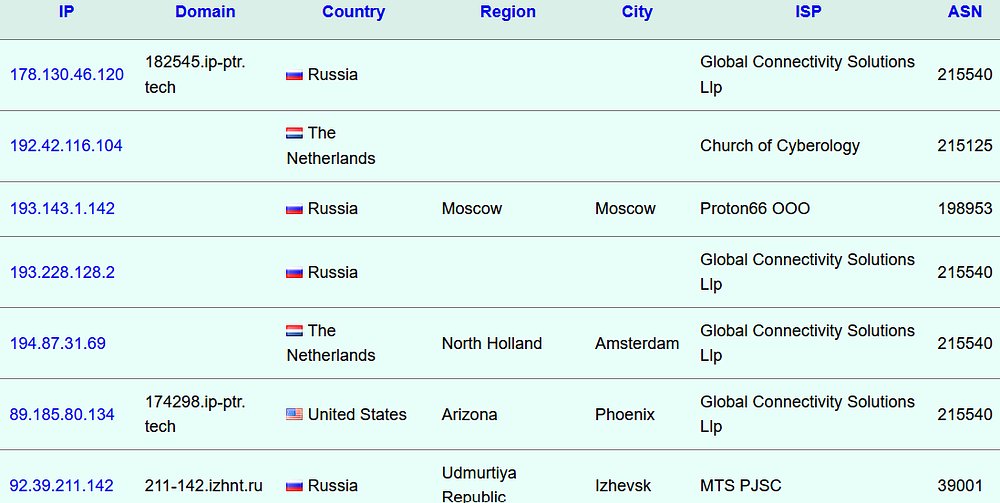
#THEGENTLEMEN #ransomware sticks to GLOBAL CONNECTIVITY SOLUTIONS🇬🇧
194.87.31.69🇳🇱
178.130.46.120🇷🇺
193.228.128.2🇷🇺
192.42.116.104🇳🇱
89.185.80.134🇺🇸
92.39.211.142🇷🇺
193.143.1.142🇷🇺
It's abused by #Akira, #Sinobi, #Tycoon2FA!
#security #infosec #malware #OSINT #darkweb #TOR

#HongKong #CyberThreat Landscape 2025–26. #CYFIRMA's latest intelligence assessment reveals a sharp rise in #ransomware, state-aligned #espionage, cloud abuse, and #datatheft operations targeting Hong Kong. Ransomware groups like #RansomHouse, #Cl0p, #Sinobi, & advanced #APTs such as #SaltTyphoon,
#LotusPanda, #PlushDaemon, #APT41, & #TropicTrooper continue to drive high-impact activity across #finance, #telecom, #manufacturing, & critical infrastructure. #Cybersecurity #Threatintel
https://t.co/puoJ1aHrte


⋱ メタスコア90の超高評価✨ ⋰
⏰3/7(土)10:00
🎮#SHINOBI 復讐の斬撃
https://t.co/EfZLj7xHRI
┈┈┈┈┈┈┈┈┈┈┈┈┈┈┈┈┈┈
忍の技で爽快に敵を斬りまくれ!!
2Dアクションは初心者だけど…反射神経なら任せてください!
#PR #えらべるセガアトラス


#Sinobi, please be kind to users. Format your numbers.
Numbers without dots are just tiny puzzles nobody asked for. #Ransomware #UX #geoplin


Actor: #sinobi
Victim: Asian Heart Institute
Date: 2026-01-21 19:48:00 UTC+3
According to #DarkWeb #Ransomware activity detected by the ThreatMon Threat Intelligence Team. The “#sinobi” Ransomware group has added Asian Heart Institute to its victims.
Actor: #sinobi
Victim: ShuBee
Date: 2026-01-21 19:03:46 UTC+3
According to #DarkWeb #Ransomware activity detected by the ThreatMon Threat Intelligence Team. The “#sinobi” Ransomware group has added ShuBee to its victims.

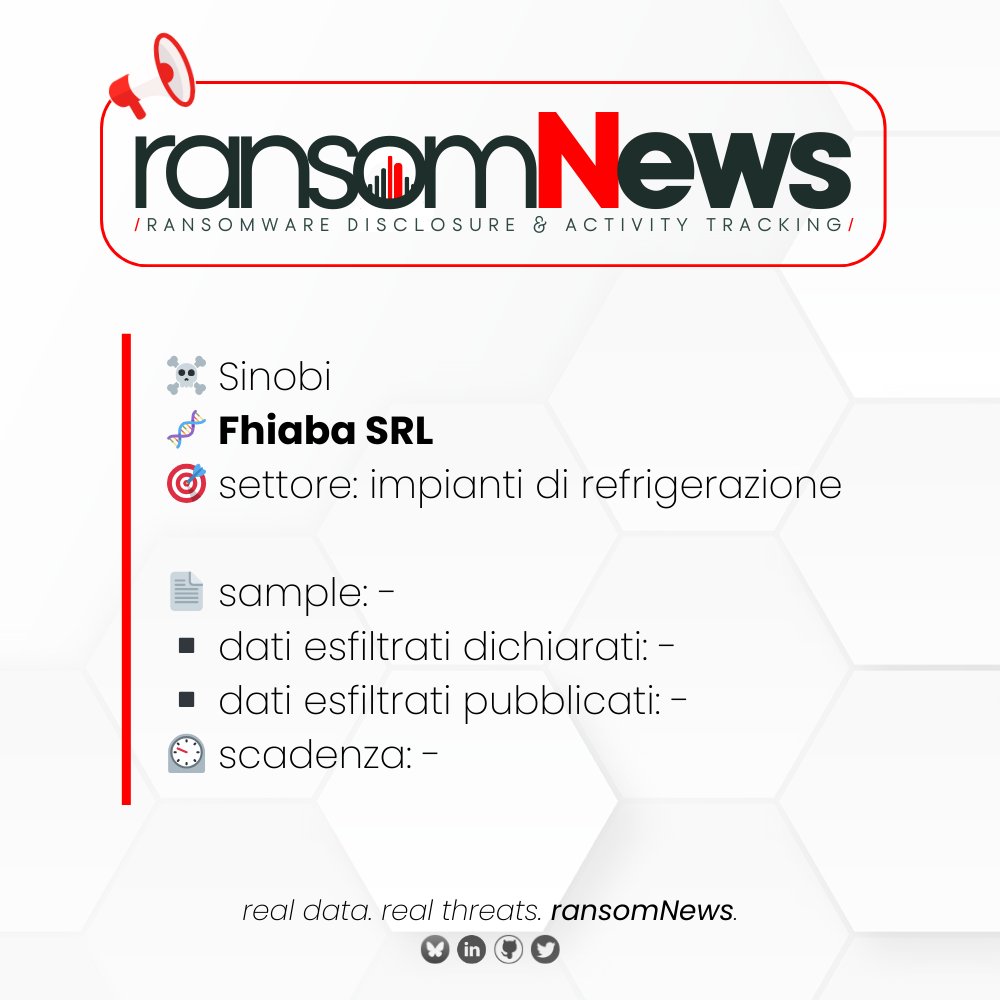
🚨 nuova rivendicazione #ransomware Italia 🚨
🏴☠️ gruppo #Sinobi
🧬 Fhiaba SRL | Azzano Decimo (PN)
🎯 settore: impianti di refrigerazione
🔗 https://t.co/ABhw5HYBwr
🗓️ 19 dicembre 2025
📄 sample: -
▪️ dati esfiltrati dichiarati: -
▪️ dati esfiltrati pubblicati: -
⏲️ scadenza: -
#ransomNews #security #infosec
Actor: #sinobi
Victim: Optimum Window Manufacturing
Date: 2025-12-18 21:29:40 UTC+3
According to #DarkWeb #Ransomware activity detected by the ThreatMon Threat Intelligence Team. The “#sinobi” Ransomware group has added Optimum Window Manufacturing to its victims.
Actor: #sinobi
Victim: Lawrence Family Jewish Community Center
Date: 2025-12-18 21:29:58 UTC+3
According to #DarkWeb #Ransomware activity detected by the ThreatMon Threat Intelligence Team. The “#sinobi” Ransomware group has added Lawrence Family Jewish Community Center to its victims.
🚨 nuova rivendicazione #ransomware Italia 🚨
🏴☠️ gruppo #Sinobi
🧬 Aircond SRL | Roma
🎯 settore: impianti idraulici, riscaldamento e climatizzazione
🔗 -
🗓️ 17 dicembre 2025
📄 sample: -
▪️ dati esfiltrati dichiarati: -
▪️ dati esfiltrati pubblicati: -
⏲️ scadenza: -
#ransomNews #security #infosec


#Sinobi is the newest reminder that mid-market ≠ safe.
🚨 8-week surge to global activity
🚨 SonicWall SSL VPN exploitation
🚨 Anti-recovery cryptography
🚨 U.S. victims dominate (92%)
Break down their tools, lineage, and targets ⬇️ #cybersecurity #ransomware https://t.co/NkSihWisjJ

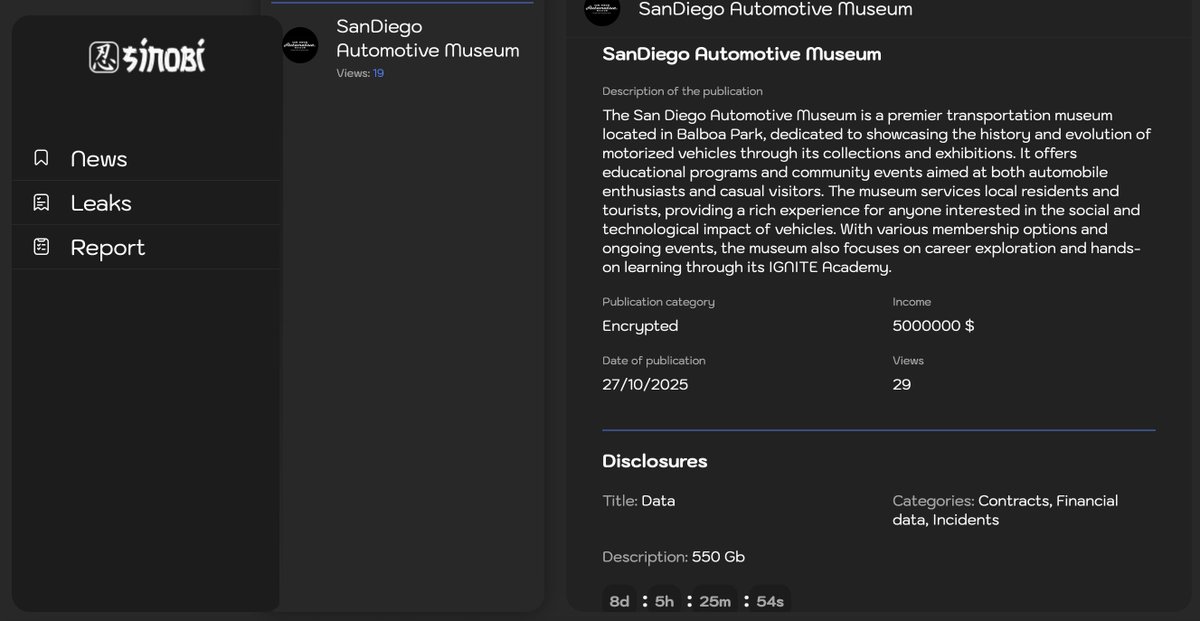
El grupo #Sinobi #ransomware habría #hackeado a San Diego Automotive Museum (@SDAutoMuseum), con sede en #SanDiego, #California 🇺🇸, es un museo de automóviles y motocicletas...
Mas ℹ️ en #VenariX ➡️ https://t.co/OW9Te2XdwS
#CyberAttack #museum #infosec #CyberSec #History
🚨 nuova rivendicazione #ransomware Italia 🚨
🏴☠️ gruppo #Sinobi
🧬 Tecnomarket SNC | Rubiera (RE)
🎯 settore: arredamento
🔗 https://t.co/pEl5eIk4kg
🗓️ 08 ottobre 2025
📄 sample: -
▪️ dati esfiltrati dichiarati: -
▪️ dati esfiltrati pubblicati: 7.50GB
⏲️ scadenza: -
#ransomNews #security #infosec

El grupo #Sinobi #ransomware ha listado en su blog a #Termotasajero (https://t.co/0wSE2cm5Hg), es una empresa #colombiana 🇨🇴 de energía, genera y comercializa electricidad...
@Superservicios
@comisioncreg
Monitorea este incidente en #VenariX ➡️ https://t.co/OW9Te2XdwS
#ciberataque #Colombia #Bogota #infosec #CyberSec #energia #electricidad #CyberAttack #Colgener


New blog on #Sinobi ransomware! They used an MSP's compromised SonicWall SSL VPN creds for initial access. Decryption is impossible w/o the attacker's private key, unless of course you hooked CryptGenRandom😜
https://t.co/fHphAm8ldy


#DoYouKnowAdversary
Explore our Healthcare Sector Intelligence for the 4th week of August 2025:
Ransomware groups like #Sinobi, #Qilin, #Global, and #Beast are increasingly targeting #healthcare organizations. These attacks affect countries like the United States, the United Kingdom, Australia, and Denmark. Sinobi stands out as the most active ransomware group, significantly outpacing the other three ransomware families.
• Gains access by exploiting software vulnerabilities
• Encrypted critical data for impact, demanding #ransom for decryption
Strengthen your defenses with LOVI’s Threat Intelligence and stay ahead of emerging threats.
🔗 Visit LOVI on recent ransomware trends: https://t.co/CHGLyD4jMA
#CyberThreatIntelligence #HealthcareSecurity #LOVI #MitreATTACK #HIPAA #CyberResilience #TTPs #CyberSecurity #VulnerCP_2_CP_9 #CTI #OSINT #InternalDefacement #abilityIntelligence #Infosec #ThreatInformedDefense

#DoYouKnowAdversary
Ransomware Alert!
#Sinobi ransomware, first identified in late June 2025, has since impacted victims across Asia and North America in multiple sectors. It is a ransomware family that encrypts files to deny access, modifies the desktop wallpaper, drops a ransom note named README.txt, and appends the .SINOBI extension to encrypted files.
Leverage our #ThreatIntelligence to anticipate attack patterns, strengthen defenses, and refine response strategies.
🔗 For more information, Visit #LOVI: https://t.co/Us7MOPBl1e
#CyberThreatIntelligence #MalwareCampaign #MitreAttack #TTPs #CyberSecurity #VulnerabilityIntelligence #Infosec #OSINT #ThreatInformedDefense #CTI #Ransomware


🚨 #Ransomware gang #Sinobi added 22 new victims to its data leak site:
🇺🇸 - all 22 are US organizations
🏭 - 7 manufacturers
🏥 - 4 healthcare companies
One company, Pittsburgh Gastroenterology Associates, is currently experiencing technical issues.
https://t.co/I6XilsV1OO

Actor : sinobi
Victim : Hana Financial
Date : 2025-07-05 19:23:41 UTC +3
According to #DarkWeb #Ransomware activity detected by the ThreatMon Threat Intelligence Team. The “#sinobi” Ransomware group has added Hana Financial to its victims.
Last Seen Hashtags on Sotwe
Most Popular Users

Elon Musk 
@elonmusk
241.5M followers

Barack Obama
@barackobama
118.8M followers

Cristiano Ronaldo
@cristiano
114.5M followers

Donald J. Trump
@realdonaldtrump
111.8M followers

Narendra Modi
@narendramodi
107.1M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.3M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.5M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.5M followers

Bill Gates
@billgates
65.3M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.2M followers

CNN
@cnn
61.7M followers

X
@x
60.7M followers