

Top Tweets for #vulnerABILITY

درجة CVSS 10.0 لثغرة في GitLab تتيح تنفيذ تعليمات عن بُعد عبر CI/CD. إن كنت تدير خوادم ذاتية الإدارة، فالثغرة حرجة وتتطلب تحديثاً فورياً لتجنب الاختراق.
#ثغرة_أمنية #Vulnerability


Tuesday's CVE Brief is live:
🔴 5 actively exploited
🟠 51 critical
🟡 107 high priority
Stay protected → https://t.co/Ykh4Hv37ol
#cybersecurity #infosec #CVE #vulnerability


GitLab admins urged to patch critical RCE flaw (CVE-2026-97229) - https://t.co/j2QKKsKrpP - @joaxcar - #GitLab #Vulnerability #CVE #Cybersecurity #CyberSecurityNews #SecurityNews
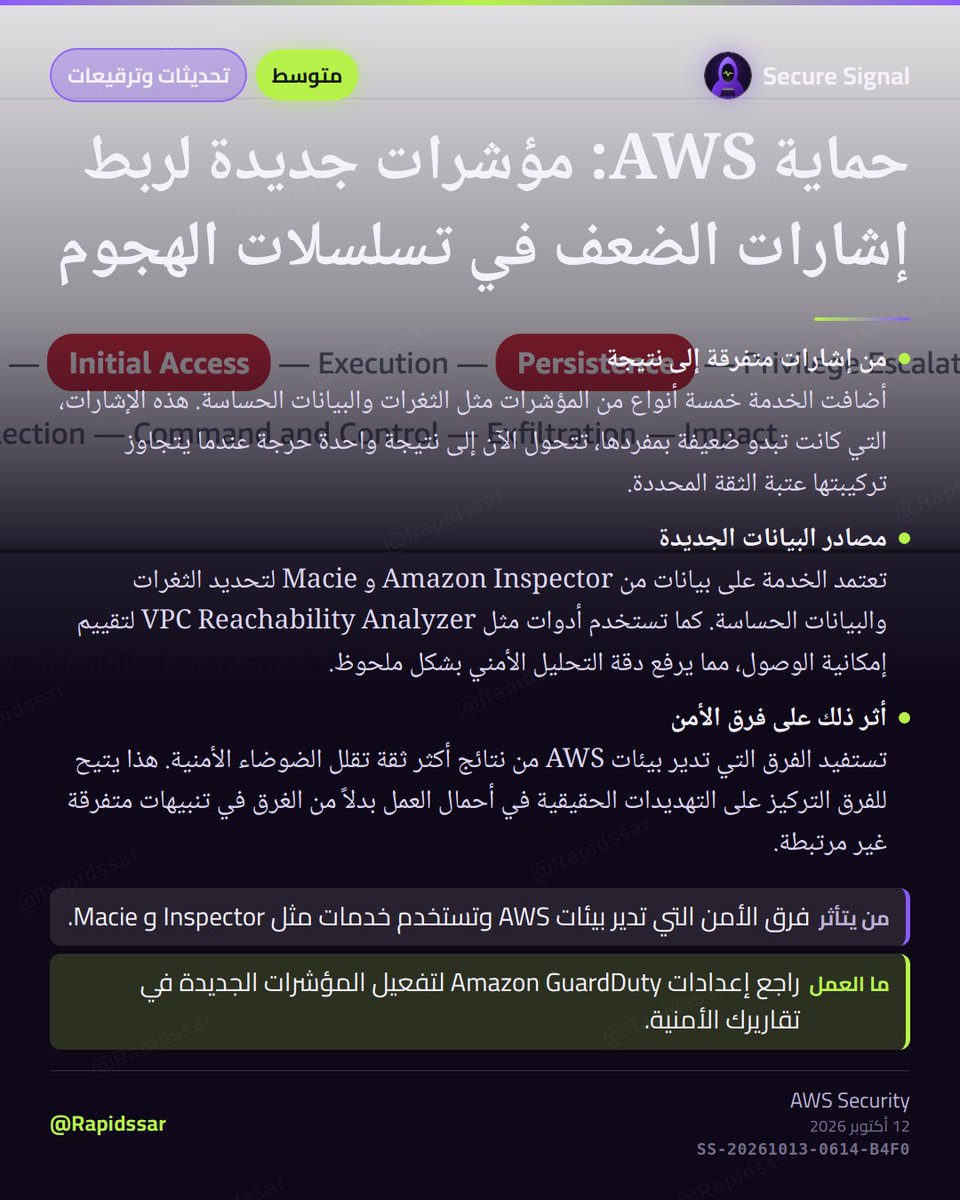
تم إضافة خمس مؤشرات جديدة في Amazon GuardDuty لتحسين اكتشاف الهجمات من خلال دمج بيانات من Inspector و Macie، مما يساعد فرق الأمن على التركيز على التهديدات الحقيقية.
#ثغرة_أمنية #Vulnerability

Brave in public, broken in private. The unseen struggles behind the strongest facades. #MentalHealth #Vulnerability

Security researchers have identified active exploitation of CVE-2026-85097, a severe vulnerability in the Bricksforge plugin for WordPress that allows unauthenticated attackers to upload malicious files and execute PHP code on vulnerable websites.
#Cybersecurity #vulnerability


🚨 HIGH SEVERITY: CVE-2025-62590 in Oracle VM VirtualBox (CVSS 8.2)
Affected: v7.1.12 & 7.2.2
Impact: Complete VM takeover with scope change to additional products
Requires: High privileges, local access
Patch immediately!
#CVE #Vulnerability #PatchNow

🚨 HIGH SEVERITY: CVE-2025-62589 (CVSS 8.2)
Oracle VM VirtualBox Core vulnerability in v7.1.12 & v7.2.2. Easily exploitable by privileged attackers for complete system takeover with scope change impact.
Patch immediately.
#CVE #Vulnerability #PatchNow

🚨 HIGH: CVE-2025-62588 (CVSS 8.2) affects Oracle VM VirtualBox 7.1.12 & 7.2.2. Easily exploitable local vulnerability enables privileged attacker takeover with scope change impact. Patch immediately. #CVE #Vulnerability #PatchNow #ThreatIntel #DFIR

🚨 HIGH: CVE-2025-62587 - Oracle VM VirtualBox Core vulnerability (CVSS 8.2). Affects v7.1.12 & 7.2.2. Easily exploitable, enables full system takeover with scope change. Patch immediately. #CVE #Vulnerability #PatchNow #ThreatIntel


High CVSS 8.7 CVE-2026-78355 impacts OTRS. Organizations using this ticketing system should assess their exposure and apply available patches. https://t.co/Lk9NStbKaq
via NVD Recent High CVSS
#CyberSecurity #InfoSec #Vulnerability #AI #MachineLearning
MikroTik RouterOS WinBox has a CVSS 8.8 auth vulnerability (CVE-2026-103903). Review low-priv accounts and apply updates promptly. https://t.co/oO89l5J8pD
via NVD Recent High CVSS
#CyberSecurity #InfoSec #Vulnerability #AI #MachineLearning
OTRS token issue (CVE-2026-78357, CVSS 9.1): Existing JWTs remain valid after user deactivation or password change. Review instances if in use. https://t.co/dvUIolTkIn
via NVD Recent High CVSS
#CyberSecurity #InfoSec #Vulnerability #AI #MachineLearning
OTRS Community Edition 6 and earlier has a CVSS 9.4 auth issue (CVE-2026-93582). Review deployments and apply updates. https://t.co/RLeGu1s5CD
via NVD Recent High CVSS
#CyberSecurity #InfoSec #Vulnerability #AI #MachineLearning
🚨 CRITICAL: CVE-2025-62481 (CVSS 9.8) - Oracle E-Business Suite Marketing vulnerable to unauthenticated takeover via HTTP. Affects v12.2.3-12.2.14. No authentication required. Patch immediately. #CVE #Vulnerability #PatchNow #ThreatIntel


Discover how recent Hikvision camera attacks in Ukraine exploit the CVE-2021-36260 vulnerability for potential remote surveillance. Learn how to secure IoT.
#Hikvision #CyberSecurity #Ukraine #Vulnerability #IoT
https://t.co/9Vv8W3a597
🚨 HIGH: CVE-2026-98023 (CVSS 7.8)
Linux kernel VXLAN flaw allows list corruption via dynamic FDB entries w/ nexthop IDs. Race condition in softirq context can lead to use-after-free.
Patch immediately.
#CVE #Vulnerability #PatchNow
🚨 HIGH: CVE-2026-98017 (CVSS 7.8)
Linux kernel use-after-free in net/sched qdisc handling. Local attackers with low privs can achieve code execution.
Patch immediately.
#CVE #Vulnerability #PatchNow #Linux

🚨 HIGH: CVE-2026-98002 - Linux kernel IOMMU/AMD flaw (CVSS 7.8)
Ineffective error check in nested domain allocation allows invalid host domain ID usage. Affects AMD IOMMU subsystem.
Patch immediately.
#CVE #Vulnerability #PatchNow

🚨 HIGH: CVE-2026-97991 (CVSS 7.8) - Linux kernel vdpa_sim_blk vulnerability allows out-of-bounds read/write via invalid sector offsets. Patch immediately. #CVE #Vulnerability #PatchNow #ThreatIntel

Last Seen Hashtags on Sotwe
Most Popular Users

Elon Musk 
@elonmusk
241.5M followers

Barack Obama
@barackobama
118.9M followers

Cristiano Ronaldo
@cristiano
114.6M followers

Donald J. Trump
@realdonaldtrump
111.8M followers

Narendra Modi
@narendramodi
107.1M followers

Rihanna
@rihanna
98.7M followers

NASA
@nasa
92.3M followers

Justin Bieber
@justinbieber
91.8M followers

KATY PERRY
@katyperry
90.1M followers

Taylor Swift
@taylorswift13
84M followers

Lady Gaga
@ladygaga
75.5M followers

Virat Kohli
@imvkohli
73.5M followers

Kim Kardashian
@kimkardashian
70.9M followers

YouTube
@youtube
68.8M followers

Neymar Jr
@neymarjr
66.6M followers

Bill Gates
@billgates
65.3M followers

Selena Gomez
@selenagomez
63.1M followers

The Ellen Show
@theellenshow
62.2M followers

CNN
@cnn
61.8M followers

X
@x
60.7M followers