We’re supercharging Copilot on Windows with Hybrid Intelligence.
With your permission, Copilot can tap into the context on your PC, take action for you, and use local models when it makes sense, giving you more capability while helping your tokens go further.
This is a perfect example of why you should set these policy settings
- DisableLocalAdminMerge
- QuickScanIncludeExclusions
For MDE onboarded devices, always enable Full remediation on device groups (PassiveRemediation)
And App Control always works regardless of exclusions ;)
🛠️ Rolling out Microsoft 365 Copilot?
A great Copilot experience starts with the right configuration. This guide highlights key settings that can improve adoption, governance, and day to day usability across your organization.
Get the specs. 👉 https://t.co/SaMh0tO5Dc
#Microsoft365Copilot #ITAdmins #EnterpriseIT
Please share this live hacking video with your loved ones so they can see just how easy it is to fake caller ID (and even clone a voice) to demand money or data over a scam phone call.
I’m hoping this demo helps even 1 person shut down a hacking attempt.
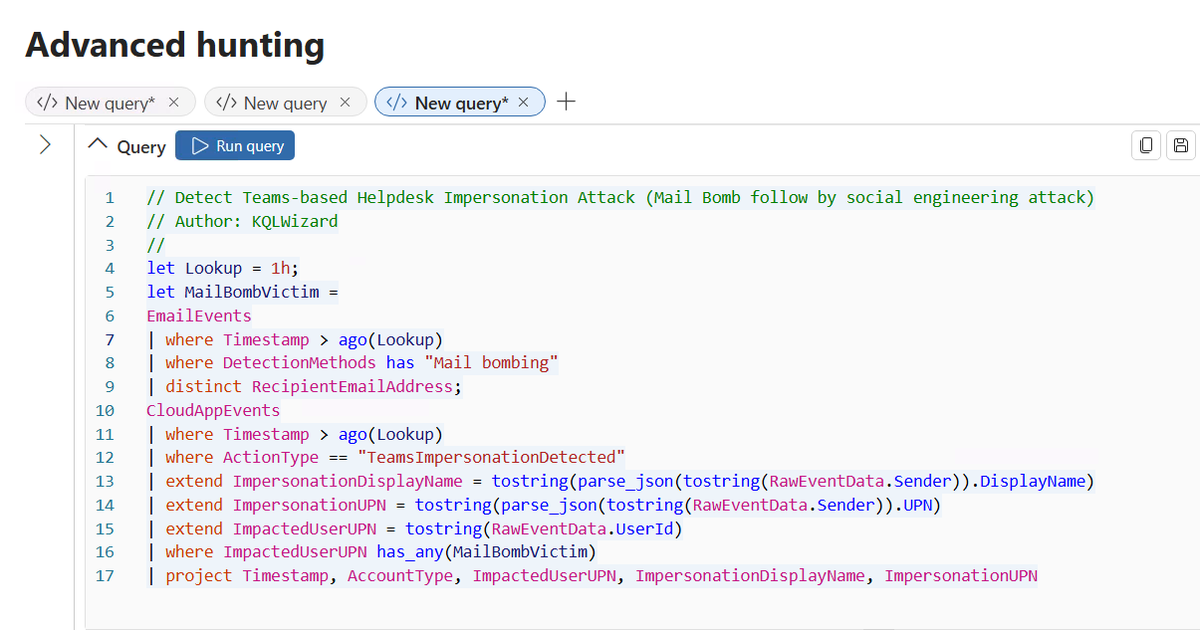
🎯𝗗𝗲𝘁𝗲𝗰𝘁 𝗧𝗲𝗮𝗺𝘀-𝗕𝗮𝘀𝗲𝗱 𝗛𝗲𝗹𝗽𝗱𝗲𝘀𝗸 𝗜𝗺𝗽𝗲𝗿𝘀𝗼𝗻𝗮𝘁𝗶𝗼𝗻 𝗔𝘁𝘁𝗮𝗰𝗸𝘀
I have chained the following two detection signals across separate Microsoft Defender XDR schemas to create a 𝗵𝗶𝗴𝗵-𝗳𝗶𝗱𝗲𝗹𝗶𝘁𝘆 𝗱𝗲𝘁𝗲𝗰𝘁𝗶𝗼𝗻 for Teams-based Helpdesk Impersonation attacks:
• 𝙳𝚎𝚝𝚎𝚌𝚝𝚒𝚘𝚗𝙼𝚎𝚝𝚑𝚘𝚍𝚜 contains "𝗠𝗮𝗶𝗹 𝗯𝗼𝗺𝗯𝗶𝗻𝗴"
• 𝙰𝚌𝚝𝚒𝚘𝚗𝚃𝚢𝚙𝚎 == "𝚃𝚎𝚊𝚖𝚜𝙸𝚖𝚙𝚎𝚛𝚜𝚘𝚗𝚊𝚝𝚒𝚘𝚗𝙳𝚎𝚝𝚎𝚌𝚝𝚎𝚍"
By chaining these signals together, defenders can identify adversaries who combine email flooding techniques with Microsoft Teams helpdesk impersonation attempts, significantly reducing false positives and improving detection accuracy.
This approach provides security teams with a more reliable way to detect and investigate this increasingly common social engineering attack technique.
https://t.co/jQD0re5Jaa
#TeamsImpersonation #SocialEngineeringAttack
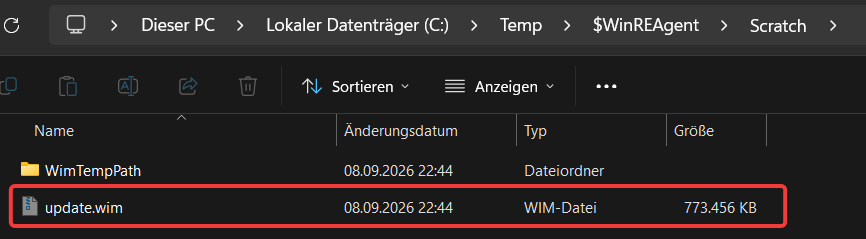
📢 PSA #Windows Update September 2026 warning: Following MS latest recommendation for the WinRE partition size is about 750MB. If your WinRE partition is smaller, Windows Update will attempt to resize the partition, which may result in failure. Be aware :)
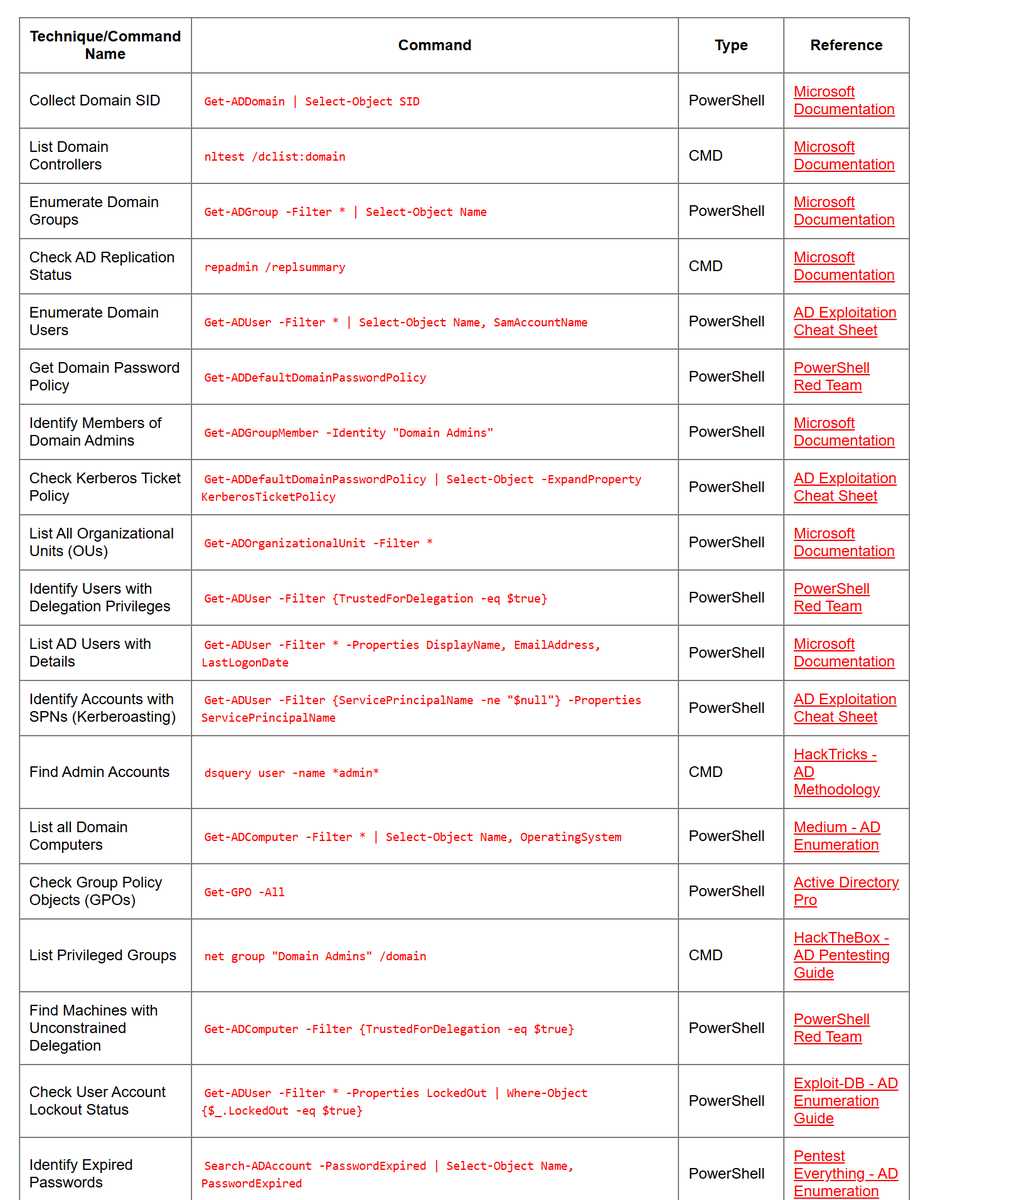
🚨 LOLAD — ACTIVE DIRECTORY ATTACK & ENUMERATION CHEAT SHEET 🔥
🔥 Telegram: https://t.co/upuP8k8ckB
✴️ Twitter: https://t.co/Za7rYILz6E
Working with Active Directory? 🏢⚔️
This is a massive collection of AD commands, techniques and resources for authorized Red Team and security testing.
🔥 Explore:
🔎 AD Enumeration
👥 Users & Groups
💻 Domain Computers
🏢 Domain Controllers
🌐 Forests & Trusts
🔐 Kerberos & SPNs
🎫 Delegation
🛡️ ACL Enumeration
📜 GPO Enumeration
🔑 Credential Techniques
⚔️ Lateral Movement
🧩 Fileless Techniques
⚡ PowerView & PowerUp
💥 Impacket & Mimikatz
🎯 Pass-the-Hash / Pass-the-Ticket
👑 DCSync & Ticket Attacks
💡 The real value?
Instead of memorizing isolated commands, build a structured AD methodology:
ENUMERATE → IDENTIFY WEAKNESSES → VALIDATE → ESCALATE → MOVE → DOCUMENT
🔗 LOLAD:
https://t.co/s1g3bFqaxr
📌 Bookmark this for your next authorized AD lab or assessment.
⚠️ Use offensive techniques only in environments where you have explicit authorization.
♻️ REPOST & SHARE with the Active Directory community!
#ActiveDirectory #ADSecurity #RedTeam #Pentesting #CyberSecurity #Kerberos #PowerShell #Mimikatz #Impacket #EthicalHacking
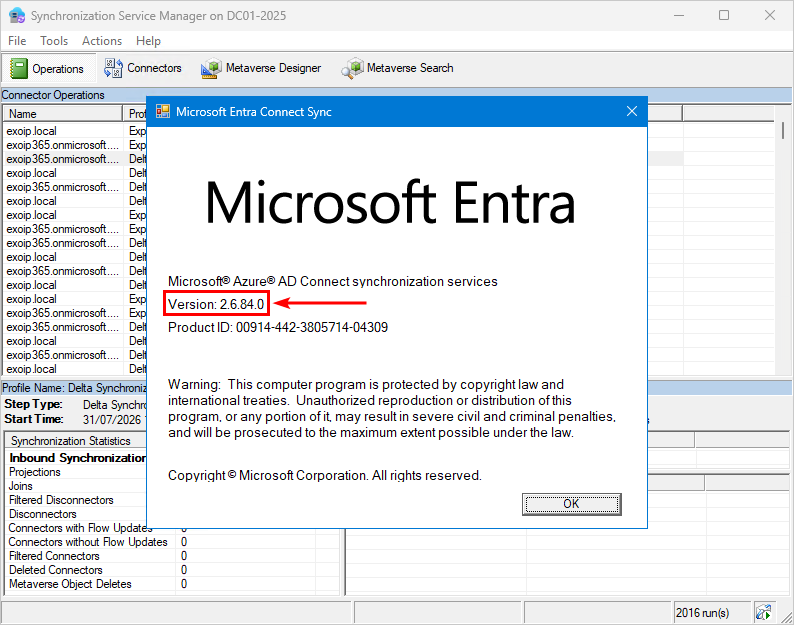
Microsoft Entra Connect Sync upgrade required before September 30, 2026!
All synchronization services in Microsoft Entra Connect Sync will STOP working on September 30, 2026 if you're not on at least version 2.5.79.0.
In May 2025, Microsoft released this version with a back-end service change that hardens its services. Upgrade before this deadline to avoid any service disruption.
Microsoft strongly recommends upgrading to the latest available version 2.6.84.0, rather than only meeting the minimum version requirement.
Version 2.6.84.0 includes security fixes and is the current recommended release.
If you're unable to upgrade before the deadline, all synchronization services will FAIL until you upgrade.
The Microsoft Entra Connect Sync .msi installation file is exclusively available on Microsoft Entra Admin Center.
Make sure you meet the minimum requirements, including .NET Framework 4.7.2 and TLS 1.2.
Learn more:
- https://t.co/Uwzw2y49F7
- https://t.co/3VTk4fO9ko
#Microsoft365 #EntraID #EntraConnect #Cybersecurity
Microsoft just removed wmic.exe from Windows 11. Not disabled - gone. Old scripts calling it (batch files, GPO logon scripts, ConfigMgr task sequences) will fail with zero warning. 🧵
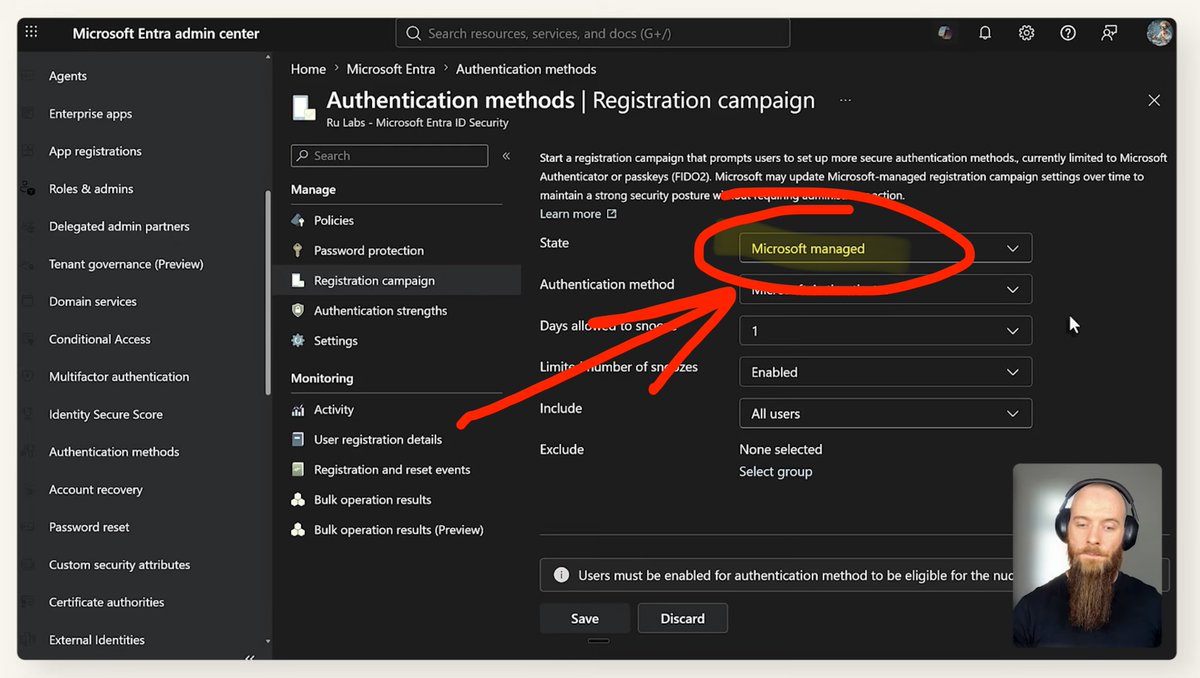
Well, Microsoft has announced the death of #SMS and #Voice authentication methods in #MSEntra. Go turn on #Passkeys right? No big deal?! right? right? Oh, it's not that easy, and it is a big deal! Today, I am releasing my guide that explains what Passkeys are, how to set up the infrastructure around it, and how to get started. Read on for more!
https://t.co/Z6XjZU0L8R
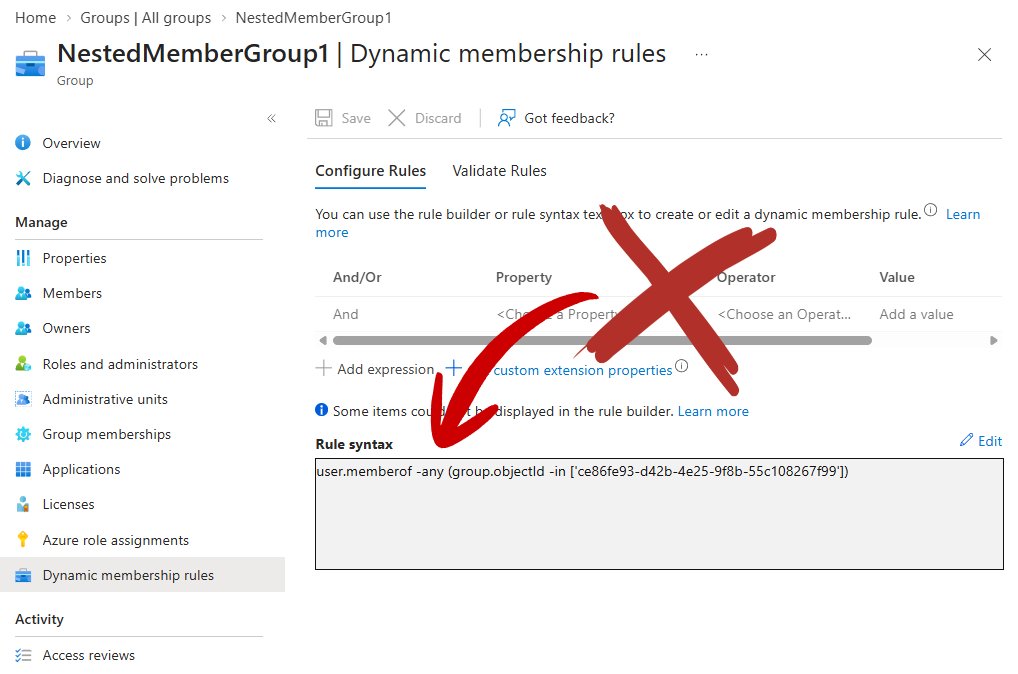
The 𝐌𝐞𝐦𝐛𝐞𝐫𝐎𝐟 𝐫𝐮𝐥𝐞 for dynamic groups in Microsoft Entra will very soon stop working! Read more here > https://t.co/zd7l8Qs8xd
However, this isn't just for groups. It will also impact anyone using the MemberOf rule operator in the following resources:
• Dynamic membership groups
• Dynamic administrative units (AUs)
• Entitlement management auto-assignment policies
• Platforms and services
• Microsoft Entra ID
• Microsoft Entra Groups
• Microsoft Entra Administrative Units
• Microsoft Entra Entitlement Management
For some resources, policies using MemberOf will first be quarantined from 27 October 2026 which will stop any processing. Then after November 3, 2026, any group memberships will stay in their last known state.
#Microsoft #Entra #News
Your Windows Server 2019/2022/2025 clients are reporting 0 required updates while older servers scan fine, you've likely hit SCCM error 0x80244007, a WSUS max prerequisites limit.
We break down the WU_E_PT_SOAPCLIENT_SOAPFAULT cause and the config fix:
https://t.co/0RUrvemcq1
Just updated my Defender for Endpoint/Defender for Business feature comparison by OS.
Main changes:
• AI agent capabilities in preview
• Device response actions, Defender deployment tool, ASR support/licensing
• Fixed it so row headers stay when you scroll down
Check it out: https://t.co/tLEOgQyVA6
New video: Entra is deprecating built-in SMS + voice MFA. I like it, but there are a ton of orgs this is going to generate a ton of work for.
• Key dates and deadlines
• Passkeys becoming the default
• Who's affected + how to find them
• Full walkthrough
WATCH: https://t.co/eYa3vt56mU
⚙️ Microsoft 365 Copilot Chat now supports organization-created prompts. Access curated prompts built by your admins to help generate faster and more tailored responses.
See how it works: https://t.co/YhpHJY9rQa
#Microsoft365#Microsoft365Copilot
🛠️ Rolling out Microsoft 365 Copilot? This Microsoft Learn guide covers recommended configuration settings to help IT admins optimize setup and support a smoother deployment.
Read more: https://t.co/sRvL9Nhn8U
#Microsoft365Copilot#ITAdmins#EnterpriseIT
NEW Security Recommendation: Block outbound network connections from Microsoft HTML Application Host (mshta.exe)!
𝐈𝐧𝐭𝐫𝐨𝐝𝐮𝐜𝐭𝐢𝐨𝐧:
To help organizations strengthen endpoint security and reduce exposure to common attack techniques, Microsoft introduces a new Microsoft Secure Score recommendation in Microsoft Defender for Endpoint (MDE).
This recommendation focuses on blocking outbound traffic from mshta.exe, a legitimate Windows binary that is frequently abused by attackers to execute malicious scripts.
Implementing this recommendation helps reduce risk from living-off-the-land binary (LOLBIN) attacks and improves your overall security posture.
𝐖𝐡𝐞𝐧 𝐭𝐡𝐢𝐬 𝐰𝐢𝐥𝐥 𝐡𝐚𝐩𝐩𝐞𝐧:
- Public Preview: Rollout begins late March 2026 and is expected to complete by early April 2026.
- General Availability (Worldwide): Rollout begins late March 2026 and is expected to complete by late May 2026.
𝐇𝐨𝐰 𝐭𝐡𝐢𝐬 𝐚𝐟𝐟𝐞𝐜𝐭𝐬 𝐲𝐨𝐮𝐫 𝐨𝐫𝐠𝐚𝐧𝐢𝐳𝐚𝐭𝐢𝐨𝐧:
Admins managing Microsoft Defender for Endpoint and Microsoft Secure Score.
𝐖𝐡𝐚𝐭 𝐰𝐢𝐥𝐥 𝐡𝐚𝐩𝐩𝐞𝐧:
- A new Secure Score recommendation titled "Block outbound traffic from mshta.exe" will appear in Microsoft Secure Score.
- Secure Score points will reflect whether this recommendation is implemented.
- The recommendation is not enabled by default and requires admin action to implement.
- There is no direct user experience change unless your organization enforces the configuration.
𝐖𝐡𝐲 𝐭𝐡𝐢𝐬 𝐦𝐚𝐭𝐭𝐞𝐫𝐬:
- mshta.exe is commonly abused by attackers to download and execute malicious payloads from remote sources.
- Blocking outbound traffic from this binary reduces attack surface and aligns with modern endpoint hardening best practices.
𝐖𝐡𝐚𝐭 𝐲𝐨𝐮 𝐜𝐚𝐧 𝐝𝐨 𝐭𝐨 𝐩𝐫𝐞𝐩𝐚𝐫𝐞:
- Review the new recommendation in Microsoft Secure Score once available.
- Evaluate potential line of business or scripting dependencies before enforcement.
- Implement the recommended configuration to improve your organization’s security posture.
- Communicate these changes to your security and endpoint management teams.
#Microsoft365 #Defender #Cybersecurity
Most break-glass accounts won’t work when you actually need them with No testing. No monitoring. Wrong setup.
I wrote a practical guide to designing, securing & monitoring emergency access in Microsoft Entra 👇
https://t.co/rDxTmBv7RB
#AzureAD#Entra#CyberSecurity#MVPBuzz
🚨 M365 Connector for Claude: Who’s Accessing Your Workloads?
Using the Defender XDR GraphAPIAuditEvents schema, I built a KQL query to list Entra users accessing Microsoft 365 workloads via the Claude connector and the specific workloads they touch. Once enabled, this connector allows Claude to directly access SharePoint, OneDrive, Outlook, and Teams — a powerful capability that demands governance oversight.
For defenders, this query provides actionable visibility into who is using the connector and what information they are accessing, helping SecOps teams monitor adoption pressure, enforce governance policies, and ensure connector risks are managed before they escalate.
KQL Code:
https://t.co/dasERAFZdd
#Cybersecurity #M365ConnectorClaude #Entra #Governance