@Raspberry_Pi Not sure that a frustrating product shortage is the best meme opportunity — am more interested in hearing about what the RPi foundation is doing to scale and make more hardware available?
@JohnCantrell97 Seems pointless. There's better options.
If you're going to memorise a few words or resort to brute forcing, might as well be a passphrase.
You could keep seedphrase physical, passphrase digital.
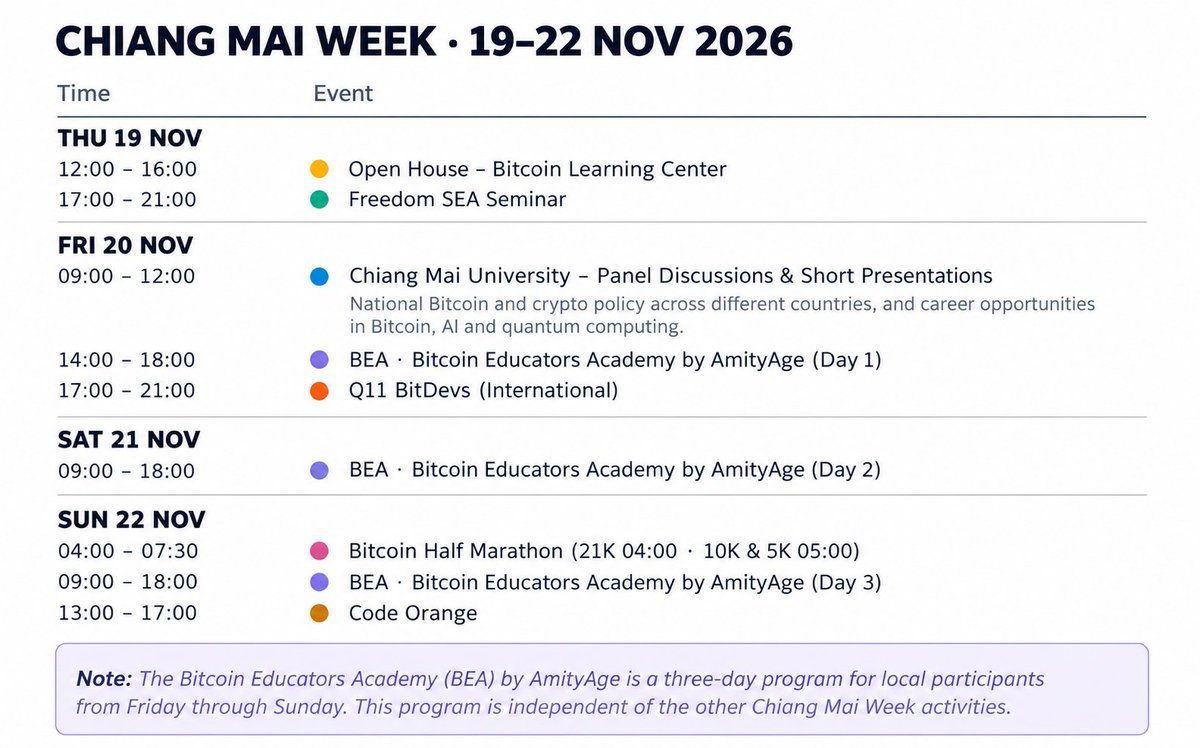
Freedom Southeast Asia is six weeks out. We’re renting the movie theatre again this year. 12 nations from across the region coming together to kick off an action packed weekend. https://t.co/bU5hDv6EbJ
Full post-mortem of the September 19 attack, and a 50% bounty — up to 3.3 BTC — on the stolen funds:
https://t.co/8iRFY7Q13G
Bounty terms:
https://t.co/aF8d2L29Kv
On Saturday September 19 an attacker used a flaw in our admin tools to take over 35 Blink accounts and withdraw about 6.61 BTC from 24 of them. A customer called one of our engineers at 11:39 UTC. Fifteen minutes later the whole custodial service was off. By that evening the hole was closed and the service was back. By Thursday September 24 every affected customer had their exact balance back, in bitcoin and in dollars, paid for by Blink's shareholders. No customer bears any loss.
This was our fault. Not Bitcoin's, not our users'. To the 22 customers whose bitcoin was taken, and to the 3,817 people whose account details were looked up: we are sorry.
How it happened:
From October 2023 until that Saturday, anyone with a free Blink account and a web browser could give themselves the powers of our support staff: change the email or phone on any account, log in as that customer, raise their limits. Three unremarkable mistakes in how our admin tools checked permissions, stacked on top of each other, in code we inherited.
The whole team was busy moving tens of thousands of users to self-custody under new regulation. Monitoring built to catch outages didn't catch an administrator doing things no administrator should.
What it didn't touch:
The money came out of our hot wallet. Most customer funds sit in multi-signature cold storage that nothing in our admin tools can reach. Non-custodial accounts were never in play: we don't hold those keys.
What the attacker saw:
They also read the details of 3,817 other accounts, in some cases a phone number or email address. Not names, not IDs, not addresses, not passwords, not seed phrases. We wrote to every holder we could reach, saying exactly what was seen.
What stopped them:
Two-factor authentication. The attacker logged in to nine accounts that had it on and tried eighteen times to move money. Zero loss.
None of the 24 drained accounts had it on. If you take one thing from this post: Settings → Security and Privacy → Two-factor authentication. Then turn it on for your email too.
What we changed:
The flaw was fixed the same day and a third layer added two days later. The admin tools are off the public internet. The functions that change a customer's email or phone are switched off for everyone while we redesign them. All customer API keys were revoked.
The hot wallet now holds a fraction of what it did. Security fixes are developed privately and published once deployed; the code stays open source. A standing security reporting channel is live, with rewards of up to 0.1 BTC for critical findings.
Where the money is:
Some still sits where it was withdrawn to. About 5 BTC has gone through a cross-chain swap service; a small amount reached an exchange that is cooperating.
Criminal complaints are filed in El Salvador and Próspera, the regulators are notified, and we have traced the funds continuously. We are not expecting the money back.
So we are putting a 50% bounty on it.
Whoever provides the information that leads to a recovery gets 25% of what is recovered. Another 25% of anything recovered goes to Bitcoin Beach, Bitcoin Ekasi, Afribit Kibera and the circular economies they choose. No cap, no end date, paid only out of funds that actually come back. Write to [email protected].
We would far rather have spent this money on grassroots Bitcoin adoption than lost it to a thief. Shame on the attacker.
One more thing:
Ignore any email or SMS about this incident that contains a link: we contacted affected users only through messages in the Blink app. We will never ask for your PIN, password, seed phrase or a login code.
The full post-mortem has the timeline, the technical detail for anyone running code derived from ours, and the bounty terms (links at the top).
Little known fact:
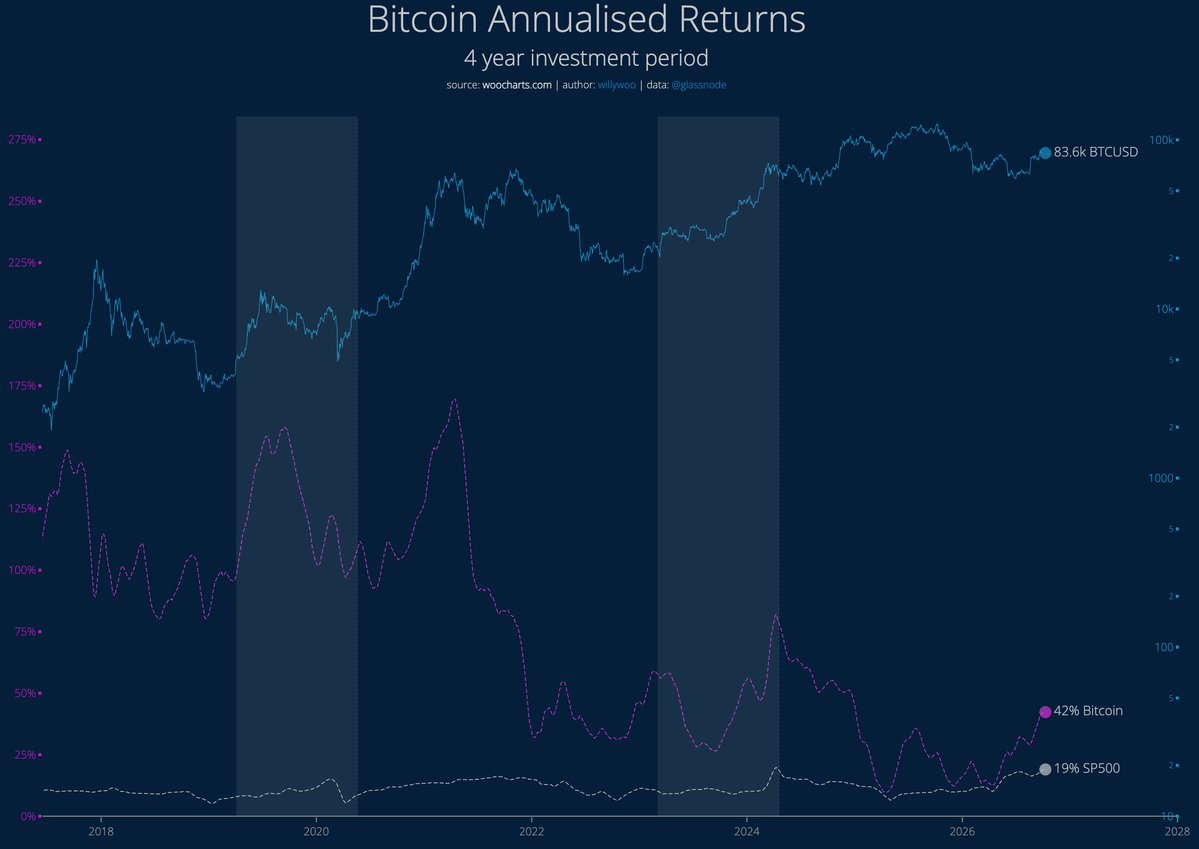
BTC has NEVER been beaten by stocks over a 4 year investment duration. Even if you bought the top.
In fact, at 42% CAGR, BTC beats the undisputed champion of hedge funds, Renaissance Technologies, who delivered 39% to their investors.
@JimmyKostro@mononautical@psacramento_x That's fun!
I have a minimum fee set on my node GUI so it filters out all the transactions unlikely to be mined soon - it usually leaves ~5000 transactions from the 100k.
Adoption will not come through shitcoins.
Adoption will not come through ETFs.
Adoption will not come through nation-states.
Adoption will only come through individuals making the choice to store their value in Bitcoin.