I’m documenting my journey from learning the fundamentals to building real security projects.
If you’re into:
🛡️ Cybersecurity
🔵 Blue Team / SOC
🔴 Red Team
🐍 Python
🌐 Networking
💻 Tech
Drop a follow and let’s connect.
I’d love to meet more people building and learning here.
I’m documenting my journey from learning the fundamentals to building real security projects.
If you’re into:
🛡️ Cybersecurity
🔵 Blue Team / SOC
🔴 Red Team
🐍 Python
🌐 Networking
💻 Tech
Drop a follow and let’s connect.
I’d love to meet more people building and learning here.
Day 15/180 🌐
TCP: “I’ll make sure every packet arrives safely.” 😤📦
UDP: “Just send it bro, we’ll see what happens.” 😂💨
TCP = Reliable
UDP = Fast
Networking is basically choosing between “Are you sure?” and “Send it!” 😂
#ITStudent#Networking#TCP#UDP
Module 01 of 30
Learned the foundation: Red vs Blue vs Purple Team, the attack lifecycle (Recon → Enumeration → ... → Reporting), and why authorization — not skill — is what actually defines Red Teaming.
Practical lab: recon on my own machine
[https://t.co/xXB2Sro7MQ]
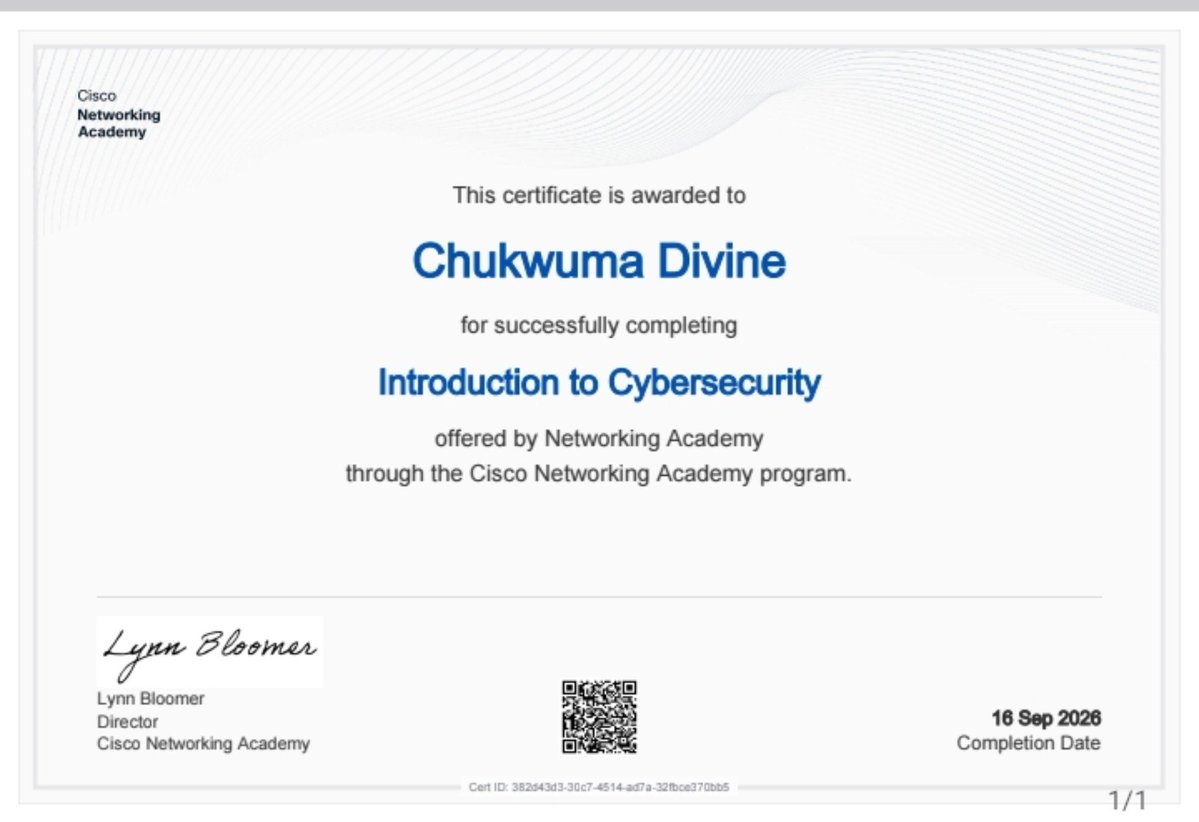
Just completed the Cisco Networking Academy – Introduction to Cybersecurity course 🛡️🎓
Another step forward in my cybersecurity journey.
Learning → Practicing → Documenting → Improving.
And we’re still going. 🚀
@cyber_razz A PIN unlock is significantly more secure than a pattern
Here are two reasons why:
Combinations: A 6-digit PIN offers 1M possibilities. Patterns max out much lower.
Smudge trail: Patterns leave a continuous oily line on your screen showing the exact path. PIN taps overlap.
Module 03 done: OSINT Fundamentals 🔴
Ran a passive recon exercise on a real fintech company — job postings, tech-stack aggregators, public API docs. No systems touched, purely public sources.
Lesson: a "clean" OSINT result is still a result.
[https://t.co/xXB2Sro7MQ]
Module 02 done: Attack Surface & Threat Modeling 🔴
Big lesson — an open port isn't the same as an exposed port. Combined netstat findings with firewall policy and found my "risky" ports were actually protected by default-block rules.
[https://t.co/xXB2Sro7MQ]
Starting a new journey: Red Team Roadmap 🔴
Learning how attackers actually think, so I can defend even better.
Recon, exploitation, privilege escalation, Active Directory, full Red Team sims — all documented as I go.
Write ups and findings 👇👇
[https://t.co/xXB2Sro7MQ]