@AlexEdgerton The Mission S is a mid-engine supercar concept sitting above the 911, not a Cayenne with a different badge.
Expecting a big floating tablet in it is like complaining your race bike doesn’t have cupholders and a heated seat.
🚨 In 2026, a 'remind me later' click is an invite for hackers. ❌ Global authorities now use a strict 14-day rule for critical patches. 🛡️ Enable auto-updates today to close the window on automated exploits before they find you. ✨ #CyberSecurity#ZeroTrust#StaySafe#InfoSec
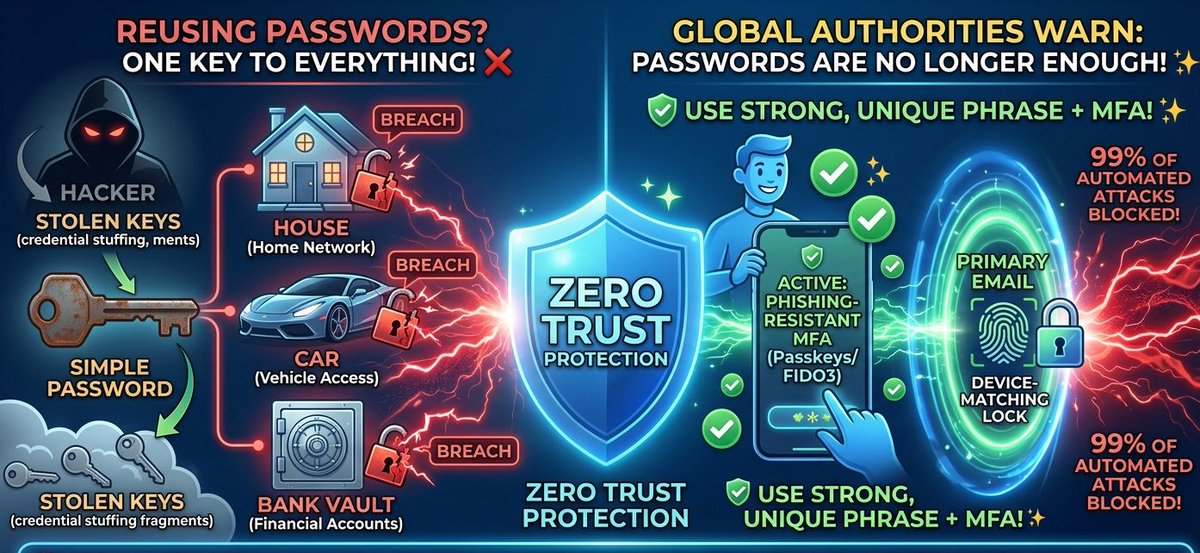
❌ Reusing passwords is like using one key for your house, car, and bank vault. 🛡️ Use a strong, UNIQUE phrase for your primary email and activate phishing-resistant MFA (Passkeys/FIDO3) to stop 99% of automated attacks. ✨ #CyberSecurity2026#ZeroTrust#MFA#InfoSec#StaySafe
🚨 In 2026, scammers don't just hack—they pretend to be people you trust. 🏥💼 If a message feels urgent, STOP. Verify the request through a separate, trusted channel before clicking. 🛡️✨ #OnlineSafety#ZeroTrust#Verify#CyberSecurity#StaySafe
🚨 Reusing passwords is like using one key for your house, car, and bank vault. ❌ Hackers only need to steal it once. 🛡️ Use a strong, UNIQUE phrase for your primary email and get a password manager for the rest! ✨ #OnlineSafety#Privacy#CyberSecurity#InfoSec#StaySafe
Global authorities warn: a simple password is no longer enough. ❌ Phishing-Resistant MFA (Passkeys/Authenticator apps) stops 99% of automated attacks. 🛡️ Don't wait for a breach; activate your highest security settings today! #CyberSecurity#ZeroTrust#MFA#InfoSec#StaySafe
🚨 Alerts spike for a massive phishing campaign hitting healthcare, legal & finance. 🏥 Scammers use fake 'invoice' & 'urgent update' emails to steal credentials. ❌ Don't trust the link; double-check the source and stay secure! 🛡️✨ #Phishing#ZeroTrust#CyberSecurity#InfoSec
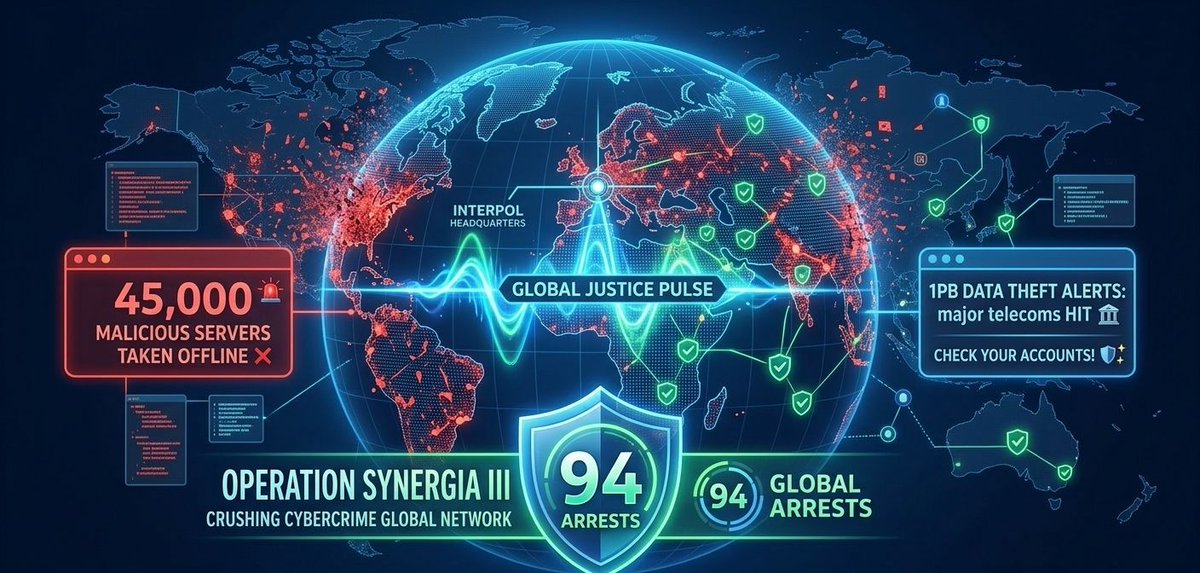
🚨 Interpol’s 'Operation Synergia III' just crushed 45,000 malicious servers & led to 94 arrests worldwide! 👏 Meanwhile, a massive 1PB data theft is hitting major telecoms—check your accounts! ❌ Don't be the weak link; rotate your keys. 🛡️#OnlineSafety#Privacy#CyberSecurity
Digital update! 🚨 Alerts are spiking for automated 'recon' scripts targeting open cloud databases—secure your configs! 🛠️ Meanwhile, the world officially shifts to the FIDO3 standard today, making passwords obsolete. ❌ Authenticate your access, not a phrase! #CyberSecurity
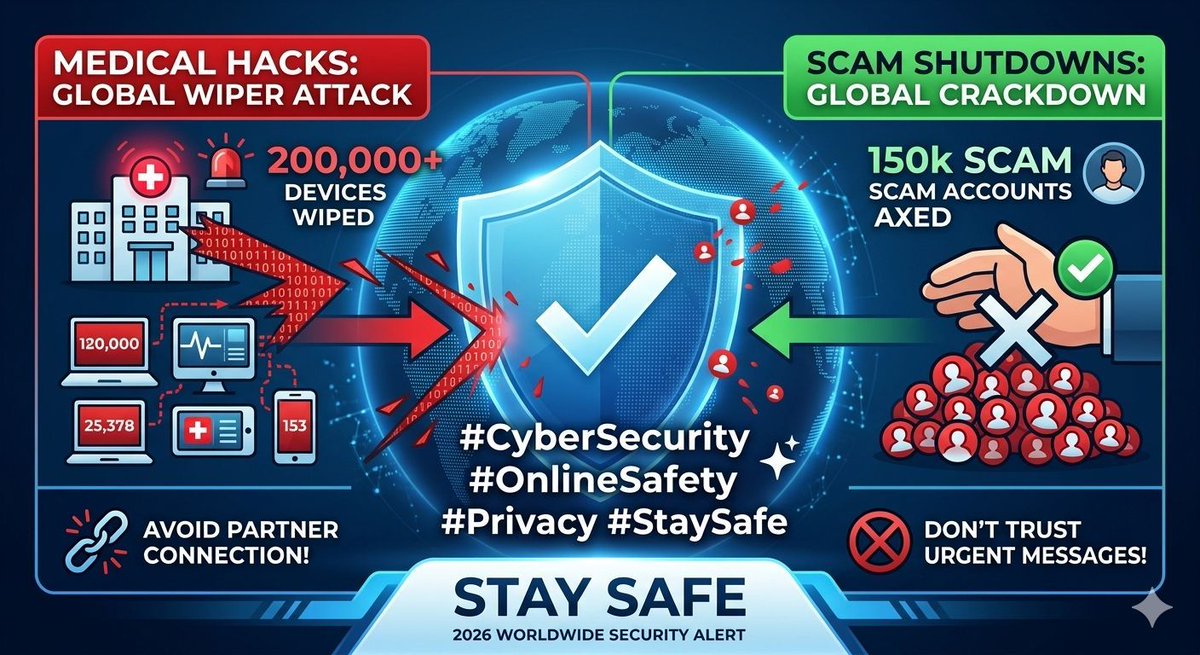
A massive hack has wiped 200,000+ devices at a top medical firm—avoid connecting if you’re a partner. 🏥 Meanwhile, 150k scam accounts were just axed in a huge global bust! ❌ Don't trust 'urgent' messages or unknown code. 🛡️✨ #OnlineSafety#Privacy#CyberSecurity#StaySafe
Global update! 🚨 Alerts spike for supply chain 'spillover' from regional conflicts. Meanwhile, a surge in 'ClickFix' scams tricks users into running rogue code—don't trust 'repair' pop-ups! ❌ Secure your core & verify partners.🛡️✨ #CyberSecurity#InfoSec#ZeroTrust#StaySafe
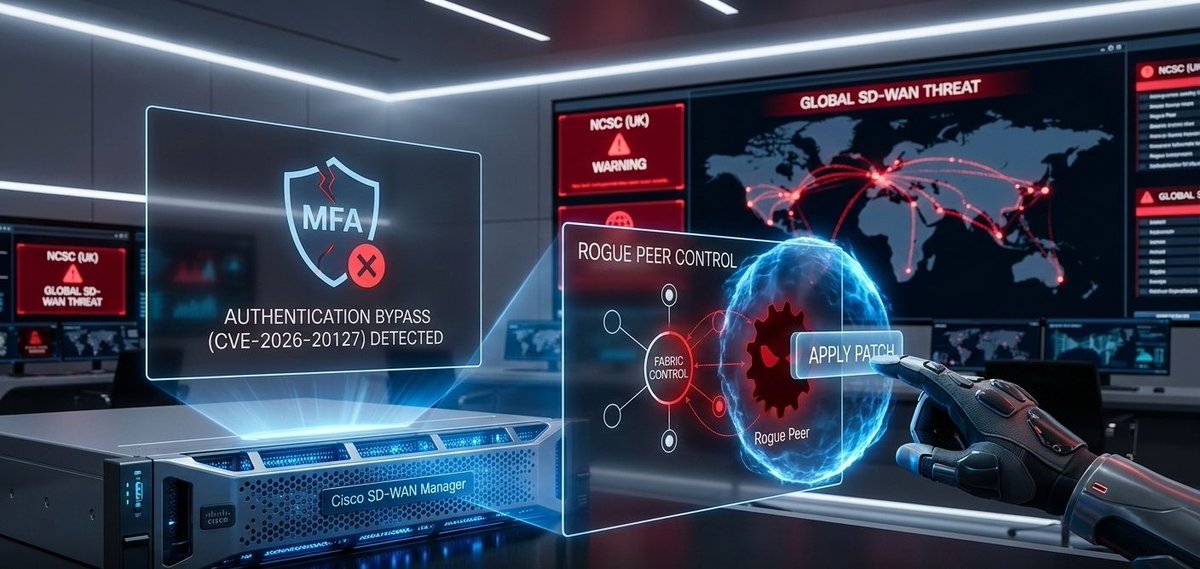
Stop relying only on MFA! 🚨 @NCSC_CH & partners confirm that active MFA bypass exploits (CVE-2026-20127) are targeting Cisco SD-WAN peering. Don’t just 'allow' access; rigorous device and peer verification is now mandatory. Harden your network fabric! 🛠️✨ #CyberSecurity
The threat window has collapsed to <29 minutes between vulnerability and exploit. Prepare for the 'Monday Morning Sprint.' Your 'Zero Trust' model must assume breach is already happening. Prioritize visibility over prevention this week 🦅. #CyberSecurity#NCSC#InfoSec#R
Data isn’t just being stolen; it's being poisoned! NIST warns that Adversarial Machine Learning (AML) is the new front. Securing training data is now as critical as securing endpoints. Identity is the first line of defense in the AI age 👤✨. #AI#InfoSec#CyberSecurity
🚨 @NCSC (UK) & allied partners warn of active root-level exploits on Cisco SD-WAN (CVE-2026-20127). Attackers are bypassing MFA & creating 'rogue peers' to control entire fabrics. Harden your edge & patch immediately! 🛠️✨ #NCSC#CyberSecurity#InfoSec#SDWAN#ZeroTrust
Global update! 🚨 @NCSC_CH warns of 'ClickFix' scams: don’t run 'repair' code in your command line! ❌ Meanwhile, a major subcontractor leak has exposed 38M records. Keep it simple: don’t trust unexpected pop-ups & verify every sender. #OnlineSafety#CyberSecurity#NCSC#Privacy
With so much AI and digital noise, true connection is a premium. Today, let's keep it simple: rebuild digital trust! Focus on easy verification, authentic voices, and reliable communication. Secure your data, but don't overcomplicate it. Sometimes, the best patch is common sense!
Global update! 🚨 @NCSC (UK) warns of Middle East cyber spillover affecting supply chains. Meanwhile, @ASCGovAU & allied partners flag active root-level exploits on Cisco SD-WAN (CVE-2026-20127). Infrastructure is the target—harden your edge now! #NCSC#CyberSecurity#InfoSec
Exactis has leaked 230M comprehensive digital profiles! This isn't just login data; it's behaviors & interests, now fueling ultra-targeted AI social engineering. Data is the new weapon. Strengthen your employees' resistance to personalized phishing today! #CyberSecurity
Comunicações entre o Controle de Tráfego Aéreo de Santa Maria, Açores, e um grupo de 4 bombardeiros furtivos B2 Spirit que irão ser reabastecidos em voo dentro de 20 minutos. O call sign dos B2 é PETRO41. Originalmente o controlador atribui-lhes um bloco de altitudes entre FL220 (22 mil pés) e FL240 mas PETRO41 pede um bloco maior entre FL220 e FL270. Os B2 são aviões subsónicos não detetáveis por radar que voam normalmente a altitudes superiores a FL400 (40 mil pés) mas têm que descer para altitudes mais baixas, tipicamente entre FL220 e FL290, para serem reabastecidos em voo. Estes aviões estão baseados no Missouri, Estados Unidos, e fazem a viagem de ida e volta até ao Irão em cerca de 36 horas de voo consecutivas incluindo a missão de ataque ao solo e múltiplos reabastecimentos. Podem transportar bombas especialmente concebidas para destruição de bunkers. Com agradecimentos ao @RuiPinto_FL