We're publishing our most detailed threat intelligence report to date.
It covers how people tried to misuse Claude—for cyberattacks, influence operations, surveillance, biology, and building weapons—and how we found and stopped them.
We disrupted every operation in the report, and used the lessons from them to strengthen our safeguards. Where appropriate, we also shared what we found with authorities and other AI companies.
These cases are not typical: we’re highlighting some of the most sophisticated misuse we’ve seen. But they’re especially important to discuss, because they show us where AI misuse is headed, where our safeguards work, and where they need to improve.
We’re publishing this report so others can spot the same activity on their own platforms, and so we can give the public a clearer view of how emerging threats develop.
Read the report: https://t.co/0EJUnYEgfz
When building defense strategies, our team contributes to 3️⃣ key areas — intelligence gathering, analysis, and innovation & continuous improvement. See how we work across teams from the research phase to implementing practical customer solutions. https://t.co/6fFQymDoJv
Given the news of SVB, I want to offer some reassurance to our clients: Wealthsimple doesn't have deposits or liabilities with SVB. You can learn more about the coverage we offer to keep your money safe here: https://t.co/ajp8lve1UW
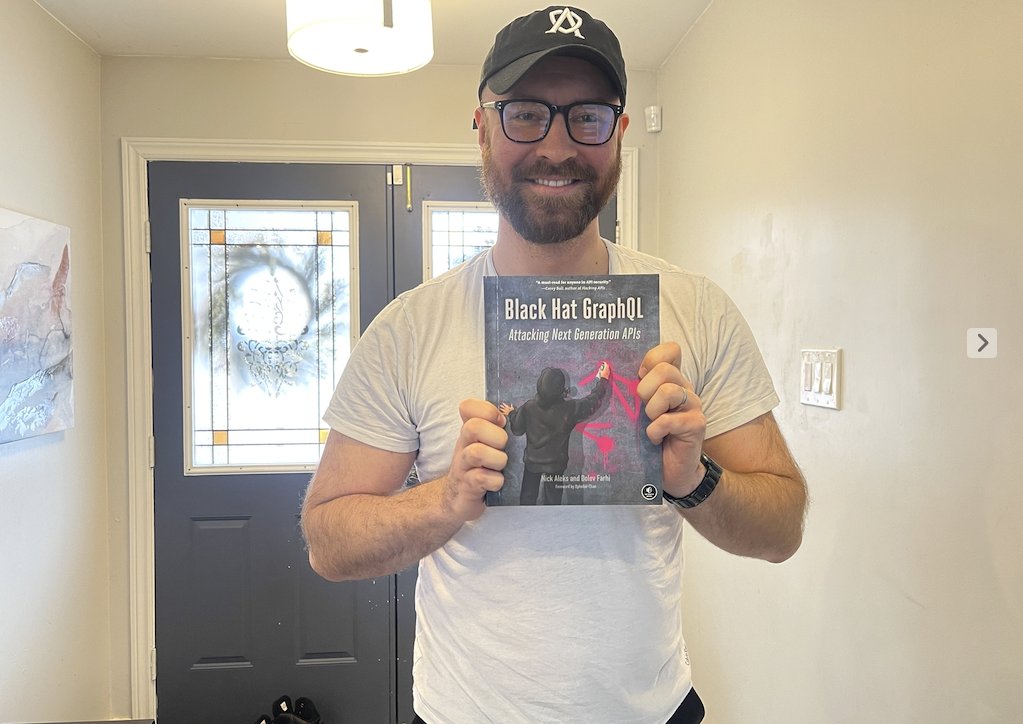
Just received my copy of Black Hat GraphQL and I couldn't be more proud! 📚🚀 This has been a labor of love, and I'm so grateful to finally hold it in my hands. Thank you to everyone who supported @dolevfarhi and I along the way! #GraphQL#hacking#cybersecurity#author
Microsoft researchers investigated an attack where threat actors deployed malicious OAuth applications on compromised cloud tenants and installed a malicious inbound connector to use Exchange servers for spreading spam. Get details and protection guidance: https://t.co/jVM7GBQMVO
GitHub is investigating the Tweet published Wed, Aug. 3, 2022:
* No repositories were compromised
* Malicious code was posted to cloned repositories, not the repositories themselves
* The clones were quarantined and there was no evident compromise of GitHub or maintainer accounts
Black Hat GraphQL is now available on Kobo, Apple Books, Kindle and more. Use the code PREORDER for a 25% discount on the early access version at https://t.co/sIrViWPkeg #GraphQL#security
Antivirus giant Norton 360 has installed a cryptocurrency mining program on users PCs, but says the service that enables the miner is opt-in. Users report miner is hard to remove. Customer reactions range from unease/disbelief to "dude, where's my crypto?" https://t.co/RJKZMfInSW
Wanna learn about reverse engineering? @mytechnotalent cooked up this amazing training with > 180 lessons covering x86, x64, arm, arm64 with practical exercises using gdb and r2! https://t.co/7AkP5alxGP