⚠️ Security Alert | Protect Yourself Against iOS Vulnerabilities
Exploiting this type of vulnerability usually requires specific conditions, such as installing a malicious app. There’s no need for alarm, but we recommend taking these precautions:
🔄 Keep iOS and your wallet app up to date with official releases.
🔗 Review your installed apps and remove any you don’t recognize or trust. Avoid suspicious links.
🔐 Keep your recovery phrase and private keys confidential. Never take screenshots of them or store them online.
🔑 Use a long, unique password for your wallet to add another layer of protection.
🛡️ For larger holdings, consider using an imKey hardware wallet @imKeyOfficial to keep your private keys separate from your everyday phone.
Security isn’t a one-time fix. Good habits are essential to protecting your assets.
🚨 SlowMist TI Alert: iOS sandbox escape 0day PoC “worse_query” disclosed 🚨
A public PoC for a sandbox escape 0day, worse_query, targets iOS 26.0–26.7.2 and iOS 27.2. It is the successor to bad_query. 📱
⚠️ This is a container sandbox escape, not a jailbreak. It breaks the assumption that apps can’t see each other: a malicious app that successfully exploits it can reach system paths and read or modify other apps’ data.
💸 The bug does not steal assets by itself. The real risk starts when a user installs an app from an untrusted source, such as a sideloaded IPA. If a wallet stores its seed phrase, keystore or WebView cache in plaintext locally, a malicious app could read it.
🛡️ Recommendations:
🔸 Don’t install IPAs or apps from unknown sources
🔸 Keep iOS up to date and install Apple’s fix as soon as one is released
🔸 Wallet developers: don’t store sensitive data in plaintext locally
🔸 If you installed an untrusted app on a device holding wallets, treat it as risky and consider moving assets to a new wallet created on a clean device
🔗 https://t.co/sIP4hX85TR
imToken × Lido Staking Campaign Is Live!
Explore ETH staking with imToken and @lidofinance, and discover more ways to participate in the Ethereum ecosystem.
A limited-time campaign designed to make your staking journey even more rewarding.
Nov 9, 16:00 – Dec 9, 16:00 (UTC+8)
👉 https://t.co/iyKSN7QDMV
imToken does not integrate Web3Auth or offer wallet creation through social logins like Google or Apple. As such, imToken is not affected by this incident.
Social logins have made Web3 more accessible. But when it comes to convenience and security, we've always prioritized putting users in control of their own private keys.
This has always been a deliberate choice at imToken, and it's a principle we'll continue to stand by.
We’re aware of a security issue affecting Web3Auth’s services used by some third parties.
We have temporarily paused the embedded wallet service. After an initial investigation, we’ve found no evidence that MetaMask users are impacted.
imToken & @LidoFinance are teaming up to boost your rewards!
💰 A $10,000 pool goes live next week.
The boost changes over time, so the sooner you join, the higher rewards you get.
Stay tuned!
⚠️ Early this morning, a security incident affected a Binance hot wallet. On-chain analysis indicates that the attack involved EIP-7702 delegation. The exact cause and scope of the impact have yet to be confirmed.
A year ago, the imToken security team examined the risks of malicious EIP-7702 authorizations in Issue 39 of its Monthly Security Report and urged users to safeguard control of their accounts.
🔐 For security reasons, imToken currently does not support initiating EIP-7702 delegation, reducing the risk of users inadvertently signing a malicious authorization.
Security reminders:
• Treat unfamiliar signing and authorization requests with caution.
• Avoid using untrusted wallets or extensions for EIP-7702 delegation.
• Keep your recovery phrase and private keys secure, and watch out for phishing scams.
New technology brings convenience, but its potential risks need careful evaluation.
📖 Learn about EIP-7702 delegation risks and how to protect yourself: https://t.co/NMmIj8csz6
🔐 How to restake your ETH after leaving Ethpool
To reduce slashing risk when switching providers, exit your Ethpool validators and wait for your ETH to be withdrawn before staking again.
1️⃣Log in to Ethpool and select Profile → Leave Ethpool → EXIT VALIDATORS.
2️⃣Wait for your validators to exit and the ETH to arrive at your withdrawal address.
3️⃣Restake with imToken Stake.
Ethpool’s official FAQ: https://t.co/drifCZd0zh
Ethpool is shutting down. What’s next for your ETH?
imToken has supported ETH staking for five years, with no reported security incidents.
With imToken Stake, you can stake non-custodially, compound rewards automatically, and stay in control of withdrawals.
🎬 Watch the video guide to get started.
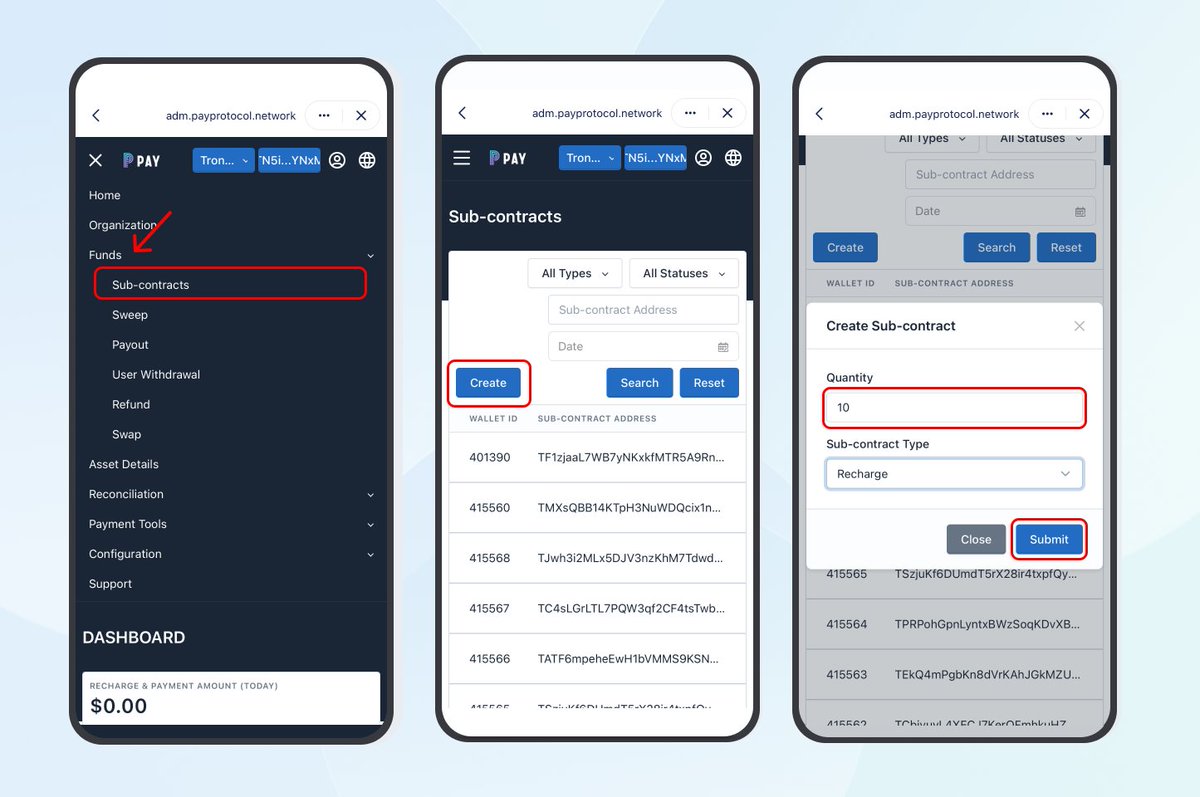
Create deposit addresses in Funds → Sub-contracts. Test with at least 1 USDT on the correct network and check the deposit report.
Sweep funds to the vault, then withdraw to your treasury wallet. Automation is optional.
Quick start: https://t.co/oydzqPt7kw
Guide: https://t.co/aRShq2Gr9m
imToken × Pay Protocol
We're partnering with @pay_protocol to help merchants accept and manage digital asset payments.
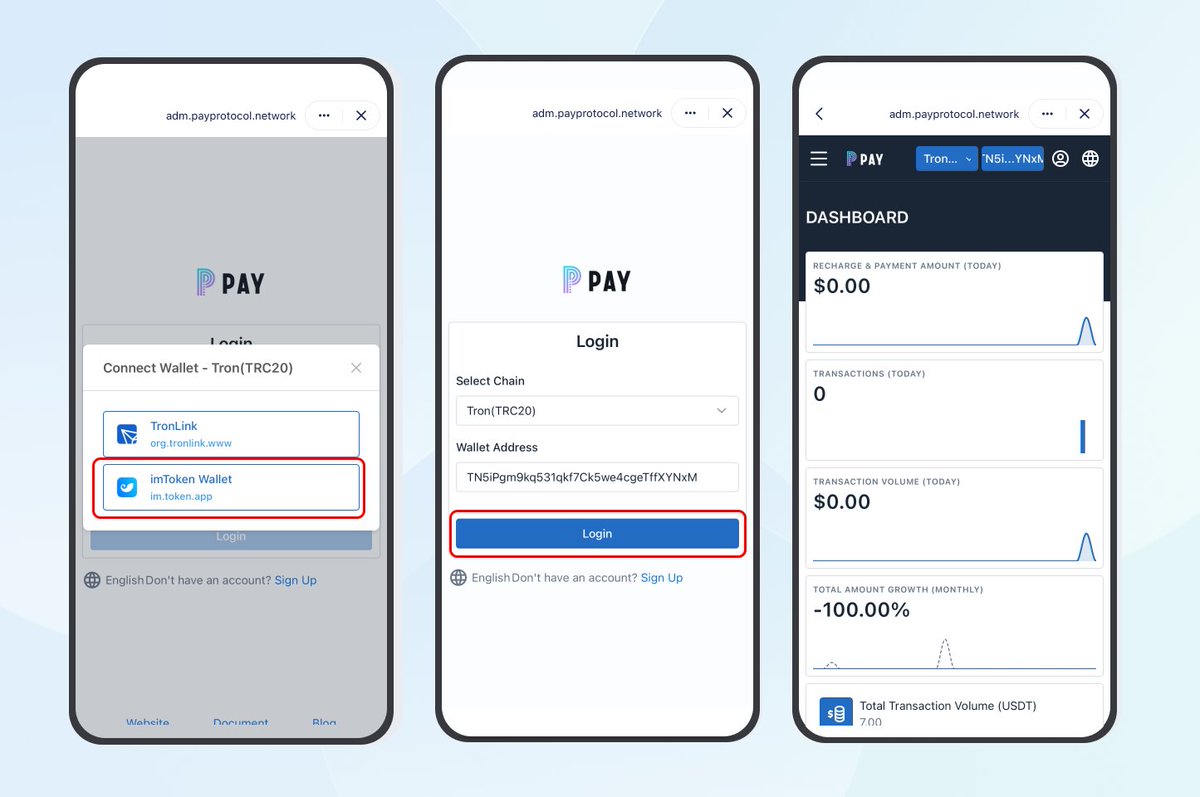
Connect through imToken to create payment addresses, track deposits, and manage funds—with non-custodial contracts and multisig controls.
Prepare 3 admin wallets and 1 treasury wallet, each with a separate seed phrase. Apply for an invite and register.
After approval and contract deployment, select your TRON account in imToken, open the dashboard via Browser, and sign in with an admin wallet.
Want to take part in Ethereum while staying in control?
With imToken Stake, your private keys stay with you. You remain in charge of access, without relying on a centralized platform.
Get started: https://t.co/oKjWqMDcwB
Your ETH can help secure Ethereum, block after block.
imToken Stake is live. Take part in staking and get protocol incentives over time.
Here’s what happens when you stake:
⚠️ Security Reminder
Your device is the first line of defense for keeping your wallet secure.
🔄 Update your iPhone, iPad, and Mac to the latest system versions.
🔗 Only install apps from trusted sources. Stay cautious with unknown links and suspicious websites.
🔐 Protect your recovery phrase. Never screenshot it, store it online, or enter it on untrusted devices.
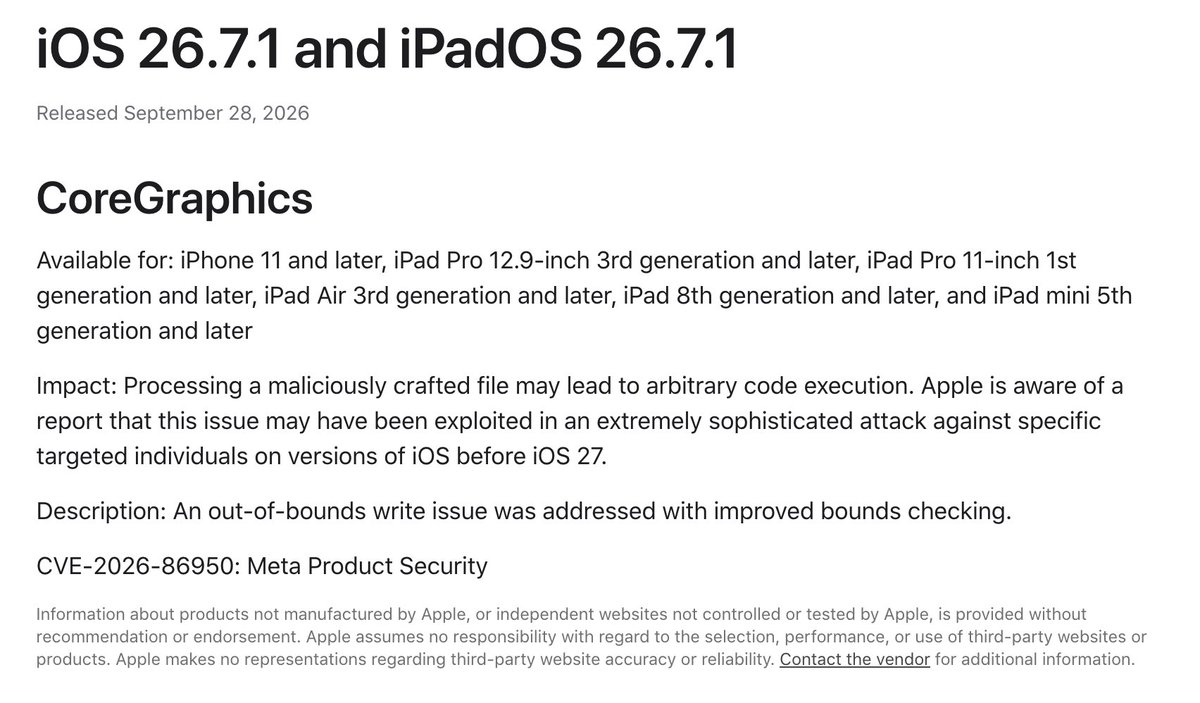
🚨 Apple has released an important security update for iOS/iPadOS 26.7.1, addressing CVE-2026-86950, an out-of-bounds write vulnerability that may lead to arbitrary code execution.
As we previously reported, this update is highly relevant to the iOS attack activity we have been tracking. Apple confirmed that the vulnerability may have been exploited in highly sophisticated attacks targeting specific individuals on iOS versions before iOS 27.
For crypto users, this is especially concerning given the iOS exploitation activity we have observed targeting sensitive wallet data.
🔐 Please:
• Update your iPhone, iPad, Mac and other Apple devices to the latest available security updates.
• Avoid installing apps from unknown or untrusted sources.
• Do not open suspicious links in Safari or in-app browsers.
• Treat unexpected files, links and app installation prompts with caution.
Stay alert and keep your devices updated.
Apple Security Update: https://t.co/9Y38Vqsl2u