🚩After years of working in offensive security, taking different certifications and exams, and seeing the real challenges in Application Security, I felt there was a need for something more practical.
That's why we built https://t.co/e6ln5StlQJ
🚩After years in offensive security, earning different certifications and working with real-world security challenges, I realized that AppSec needs more than just learning how to find vulnerabilities.
It’s about understanding how to detect, exploit, and fix them.
That’s why we built https://t.co/hj3CIfp9S6 to make practical Application Security education accessible, from finding vulnerabilities to detecting and fixing them.
#appsec #blackfriday #cybersecurity
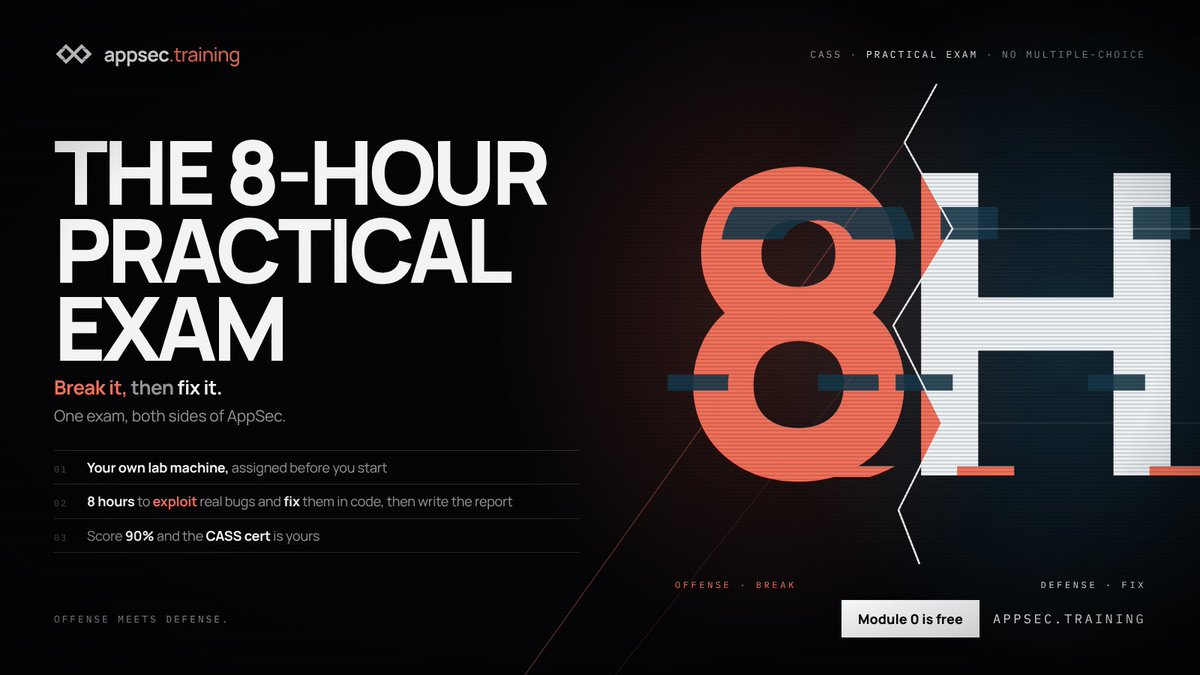
📌The 8-Hour Practical Exam
Break it, then fix it. One exam, both sides of AppSec.
🧪 Your own lab machine, assigned before you start
⏱️ 8 hours to exploit real bugs AND fix them in code, then write the report
🎯 Score 90% and the CASS cert is yours
Offense meets defense. No multiple-choice. 🔴🔵
👉 Module 0 is free: https://t.co/iCQTOYzouR
#AppSec #CASS #blackfriday
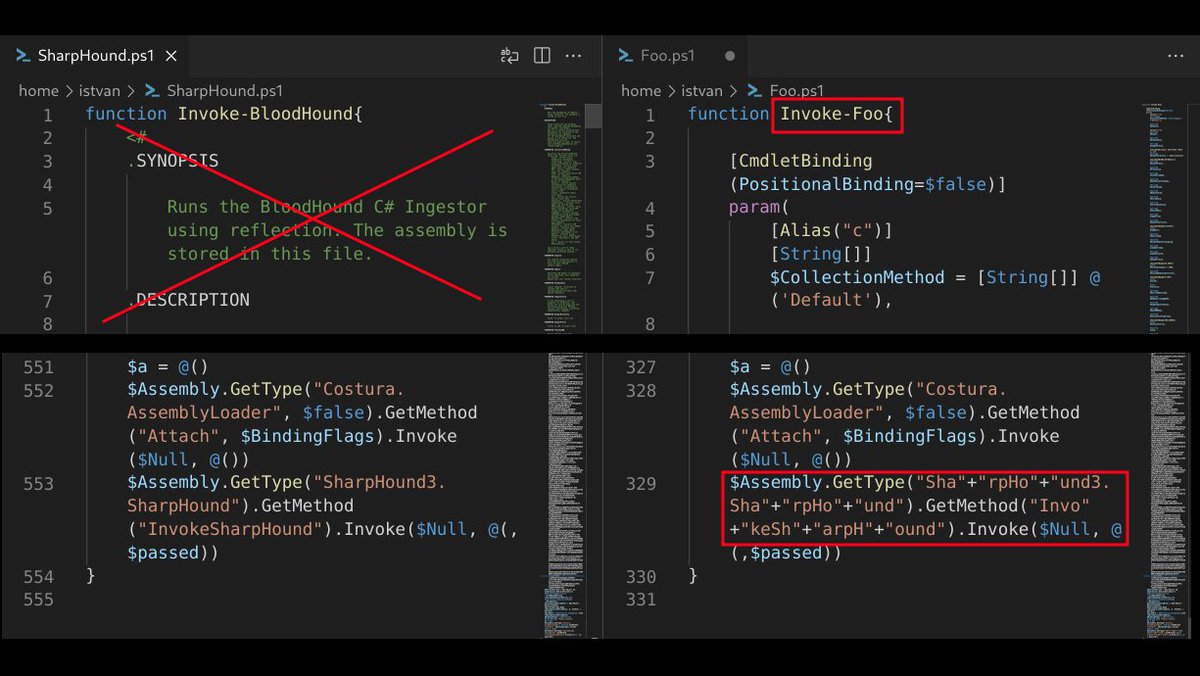
No surprise. Recently bypassed an EDR/AV for the PS assembly loader of #SharpHound only by:
1.) renaming the function
2.) removing comments
3.) splitting some essential strings
The orig version was mitigated, the modified bypassed using in-mem exec by iex+iwr. It is 2021. :)
Some cool #cybersecurity labs by @digininja for learning web #security topics -
Web Cache Poisoning
https://t.co/VjlFYQwXFw
Vulnerable LDAP
https://t.co/kKGrdYcYmG
CORS
https://t.co/mO1TGwgkXV
GraphQL
https://t.co/YSHAlepsXf
PostMessage
https://t.co/kpHfmB1087
#bugbounty
Burp Suite > Proxy > Options > TLS Pass Through.
Add these:
.*\.google\.com
.*\.gstatic\.com
.*\.mozilla\.com
.*\.googleapis\.com
.*\.pki\.goog
No more noise in your logs! #bugbountytips#Bugbounty#CyberSecurity