and here is tsc-rs running inside a @Cloudflare Worker.
No container, no Node.
- compiled to WebAssembly: real tsc errors in ~100 ms round trip.
- Flip one switch and the same module runs in your browser instead: ~60 ms, works offline.
Agents write code against tool APIs. I'm exploring this to catch the made-up method before it runs...
https://t.co/UhOicT9ffe
https://t.co/XAIgOGAoK1
Build the next Github on Cloudflare and win $25,000. Rethink how multiple agents collaborate on code spaces for the next era of development.
https://t.co/IBpTmiPppR
excited to announce that @Cloudflare Artifacts is now in open beta!
with Artifacts, you can give every application and agent its own repo that you can manage programmatically
plus you can use it to store and deploy your Workers code (and ofc it integrates with Workers Previews)
open source is core to so much cloudflare does
today is the first day of @cloudflare birthday week, so here are a bunch of big updates to open source projects we maintain + some new ones:
1. we introduced forge — a new, free, OSS pipeline for auto generating SDKs, CLIs, docs, and libraries
2. cf cli — forge is in production and cloudflare is the first customer! our CLI now supports so much more than just workers
3. vinext 1.0 — what started out as a slopfork is now powering many organizations' production next.js apps
4. emdash 1.0 — the open source CMS that runs our blog (that we operate our network for)
5. 4 months of voidzero, speeding up the dev (and agent) toolchain — oxc compiles react.js 10x faster, vitest 5 is up to 50% faster, tsgolint is now stable (and up to 18x faster than eslint) and more!!
6. experimental preview of native rust in cloudflare workers!
7. big update to kitesurf — our open source agentic browser that runs on workers. webmcp and all
8. BEACON — open dataset of web performance data for you and your agents to go play with and explore
forever blown away for how much cloudflare can ship in one day? as if we didn't ship a bunch of major announcements last week and have a whole week ahead still...
We are releasing cf, our new command-line tool that mirrors the entire Cloudflare API and supports programmatic TypeScript configuration. We are also open-sourcing Forge, our internal SDK generator. https://t.co/WxjMkPWJVx #BirthdayWeek
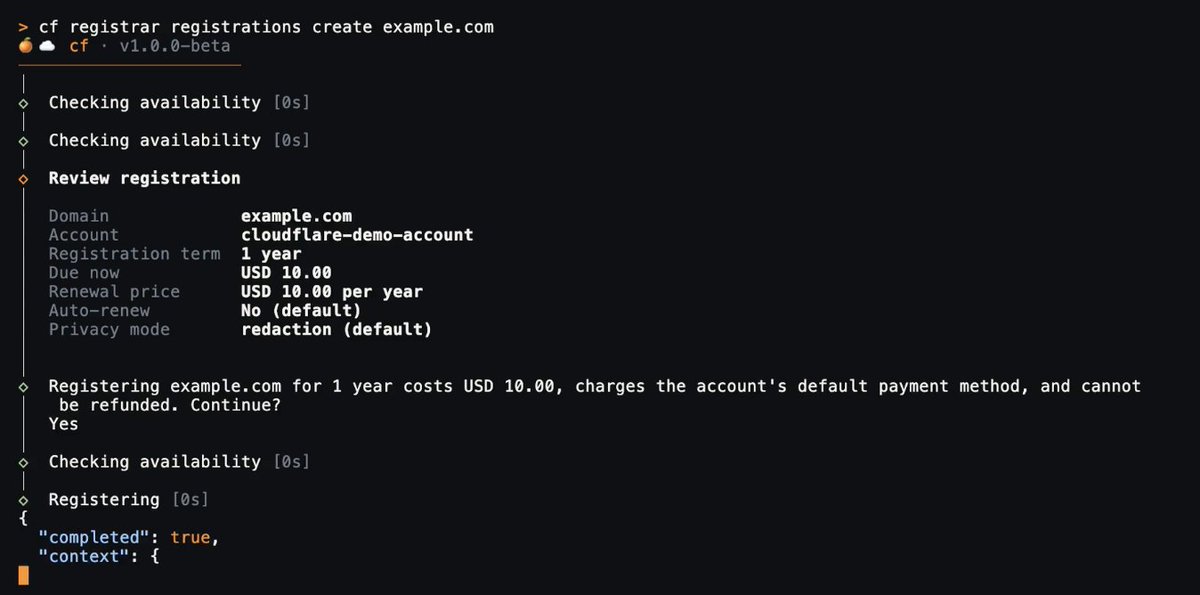
Introducing "cf", an agentic CLI for the entire Cloudflare API.
You can do nearly anything. Even buying a domain is incredibly simple from the CLI.
Don't know what command you need? Run `cf cli search "look at messages stuck in my queue"` and it will return a list of relevant commands.
https://t.co/22z5R5ArEW
cloudflare built the most agentic CLI i've ever seen
we were moving our company brain DO (durable object) to its own worker from our main worker to reduce the memory load
i was not able to find what happens mid-migration, so AGENT used the wrangler cli to
1. spun up two workers
2. wrote dummy rows
3. ran the migration
4. held a live request open
5. deleted both workers
all of this against real cloudflare infra.
cmg to our question, the data is fine. only the requests already running get dropped. while mid-migration
great work @CloudflareDev team 👏
Twice in nine days. OpenAI's models chained a zero-day to get out of an eval environment. Anthropic just found three incidents of the same shape.
This is what capable models do. Every reachable path is an invitation. Credit to both for publishing.
We rebuilt Cloudflare OS, our internal agent platform, assuming exactly this. Sandboxes have no network path out. Agents don't get every MCP tool up front, each workspace gets only what it needs. And instead of stopping for every approval until someone gives up and enables auto-approve, the platform simulates pending actions so the agent keeps working, then queues the real ones for review at the end.
The app side goes further. Apps carry no auth code at all, the sandbox provides it, so there is no auth logic to get wrong. Multi-document apps are isolated per document, so a bug can't leak between separately shared items. Anyone viewing an app must have direct permission to each of its data sources, so a dashboard on sensitive data can't overshare. Actions need the user's own permission or an approval from someone who has it, so an app can't escalate its author's privileges. And everything an app does is logged, even when the service it calls doesn't support logging.
Most companies are about to point agents at real systems. Build for what the models actually do.
We will open source this next week!