REA is most dangerous thing on the internet right now...
It lets your AI agent reverse engineer any app, down to the binary
If you use it correctly, you can rebuild any feature you pay for, for FREE
In this article, I show you how: https://t.co/3P1FNXiXzl
This is getting f*cking scary.
The tools reverse engineers spend years learning are free on GitHub, and agents like REA are already driving them
[01] the core
ghidra: the NSA's free framework for disassembly, decompilation and scripting https://t.co/3nuRIfMEeT
Apktool: decodes Android apps back to near-original resources and rebuilds them https://t.co/OsFylLyV4p
binwalk: finds and extracts files hidden inside firmware, rewritten in Rust https://t.co/O2bbtCvEGh
unblob: recursively unpacks almost any container format from a binary blob https://t.co/FSe9tP484M
[02] debug and inspect
pwntools: a Python framework for writing exploit and CTF code fast https://t.co/ucOpCsnSRJ
pwndbg: makes GDB and LLDB readable for reverse engineers https://t.co/E6GFcOiXny
LIEF: parses and edits ELF, PE and Mach-O binaries from Python, C++ and Rust https://t.co/FRUxQ06KCw
Detect-It-Easy: identifies what a file is, with a scriptable rule engine https://t.co/Da8uOKau1J
[03] where agents plug in
ghidra-mcp: 200+ tools that let an agent drive Ghidra https://t.co/qRUhx7UOpl
jadx-ai-mcp: connects the JADX Android decompiler to Claude https://t.co/YEgkzZxqdo
radare2-mcp: an MCP server for radare2 that can be sandboxed to one directory https://t.co/fZ7WGm4Y4d
mcp-windbg: lets an agent run WinDbg commands for crash dumps and kernel debugging https://t.co/dlVSHkrlou
THIS IS AN ACTUAL F*CKING GOLDMINE
Anthropic just shared one of the best tricks for Claude Code.
The idea: run Sonnet, Haiku 5.5 and Opus 5.5 at once, each one doing only the job it's best at.
Better results and way fewer tokens, because every task lands on the right model.
You just launch Claude Code like this:
claude --model sonnet --advisor opus
here's the split:
→ Sonnet 5.5 runs the session, writes the code and applies the fixes
→ Haiku 5.5 swarms the repo in parallel: search, grep and diff audits
→ Opus 5.5 stays on call as advisor for the big calls and signs off on the diff
→ you stop burning Opus context on work that doesn't need it
Opus only steps in at three moments:
→ before a plan locks
→ when the same error shows up twice
→ before calling it done
Sonnet builds. Haiku swarms. Opus reviews.
JEV engineering is the same move one layer down: the forks that need no thinker (which file, which tool, retry or stop) go to JEV in milliseconds, and the big models only see the ones that split
the full tree
> Sonnet 5.5 runs the main session and coordinates the work
> search maps the repo on Haiku 5.5, read-only
> grep finds call sites on Haiku 5.5 in its own context
> audit checks the diff on Haiku 5.5 in a throwaway worktree
> Opus 5.5 on call as advisor, reviews the synthesized diff before sign-off
> JEV routes micro-forks in milliseconds
paste the tree and this prompt into Claude Code ↓
"Reconfigure my Claude Code setup around this tree:
1. Run the main session on Sonnet 5.5 with Opus 5.5 as advisor.
2. Create three Haiku 5.5 subagents in .claude/agents: search (maps the repo), grep (finds call sites), audit (checks the diff).
3. Set isolation: worktree on audit so its checks never touch my working branch.
4. Add one rule to CLAUDE.md: delegate every repo search and test run to the Haiku 5.5 subagents to keep the main context small.
5. Route fast deterministic forks (tool choice, path selection, retries) through JEV.
Show me every change as a diff first. No edits until I say go."
↳ https://t.co/YqkjQiqRGv
save it, it'll come in handy.
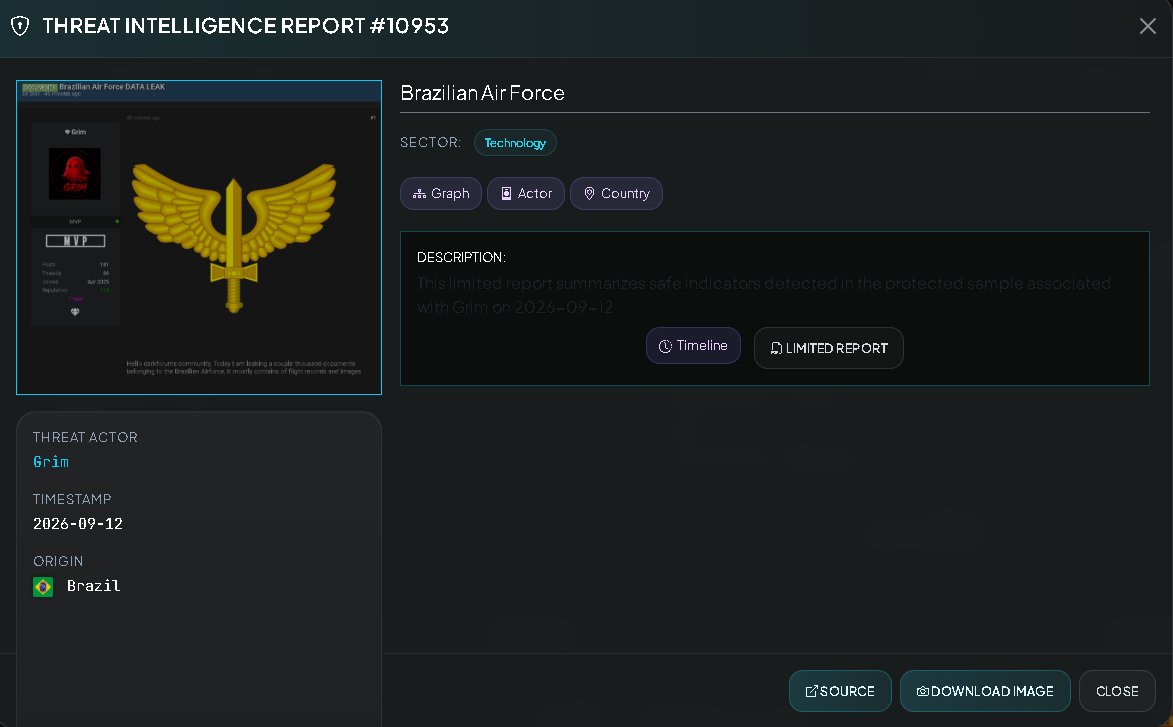
TARGETED PREVENTIVE ALERT 🇧🇷: ALLEGED EXFILTRATION AND PUBLICATION OF BRAZILIAN AIR FORCE (FAB) DATA
[STATUS: UNCONFIRMED; VISIBLE EVIDENCE BUT NOT VERIFIED / SOURCE: CYBERCRIME FORUMS (DARKFORUMS) / DATE: SEPTEMBER 12, 2026]
CENTRALIZED CYBER-INTELLIGENCE MONITORING HAS DETECTED THE ALLEGED PUBLICATION OF THOUSANDS OF DOCUMENTS—PRESUMABLY BELONGING TO THE BRAZILIAN AIR FORCE (FORÇA AÉREA BRASILEIRA)—BY THE THREAT ACTOR "Grim." THE REPORT ATTRIBUTES THE LEAK OF FLIGHT LOGS AND IMAGES, HOSTED ON AN EXTERNAL MEGA DOWNLOAD LINK, TO THIS ACTOR.
It is strictly noted that this has not been confirmed; while visible evidence exists on underground forums (DarkForums), the veracity, currency, and actual impact level of the exposed data and documents remain unverified.
Threat Actor: Grim
Victim / Affected Entity (Alleged): Brazilian Air Force
Nature of Data: Allegedly thousands of documents, including suspected flight logs and images.
Sector: 🛡️ Military / Defense / Government
Target Country: Brazil 🇧🇷
Source Platform: DarkForums
🛡️ PREVENTIVE TECHNICAL CONTAINMENT RECOMMENDATIONS (SOC / HARDENING)
Logistics and Defense Infrastructure Monitoring:
Entities, suppliers, and contractors within the region's aviation ecosystem are advised to monitor their systems for anomalies, while treating the reported intrusion as a suspected, unconfirmed threat.
External Record Auditing:
Proactively alert compliance and fraud control teams about the existence of this visible evidence to prevent potentially leaked logistics identifiers from being used in contract impersonation schemes.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Monitoring Console: https://t.co/5LuqwzYuS6
#Cybersecurity #ThreatIntel #DataLeak #FAB #Brazil #Grim #DarkForums #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #AllegedIncident #VisibleEvidence #SecurityAlert #GovSecurity #DefenseSecurity #FinancialFraud