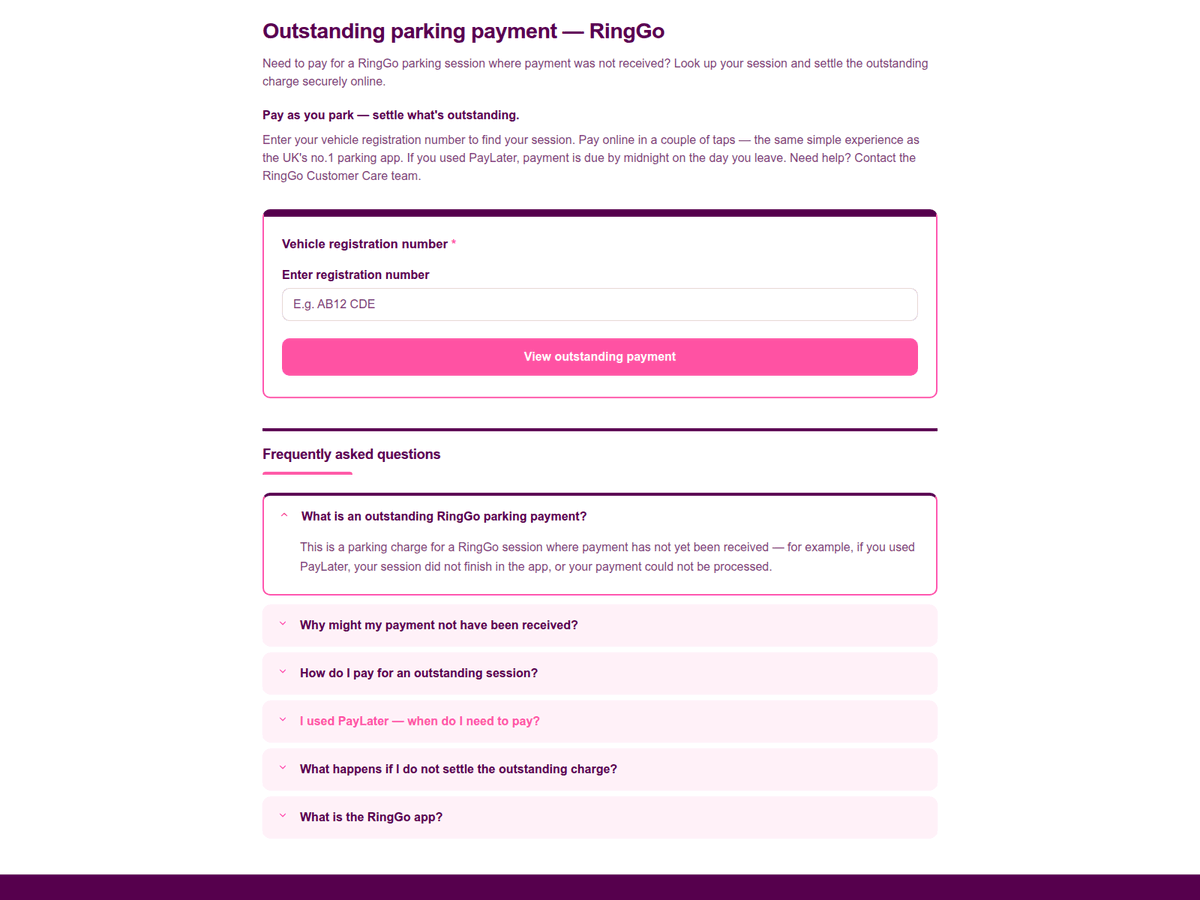
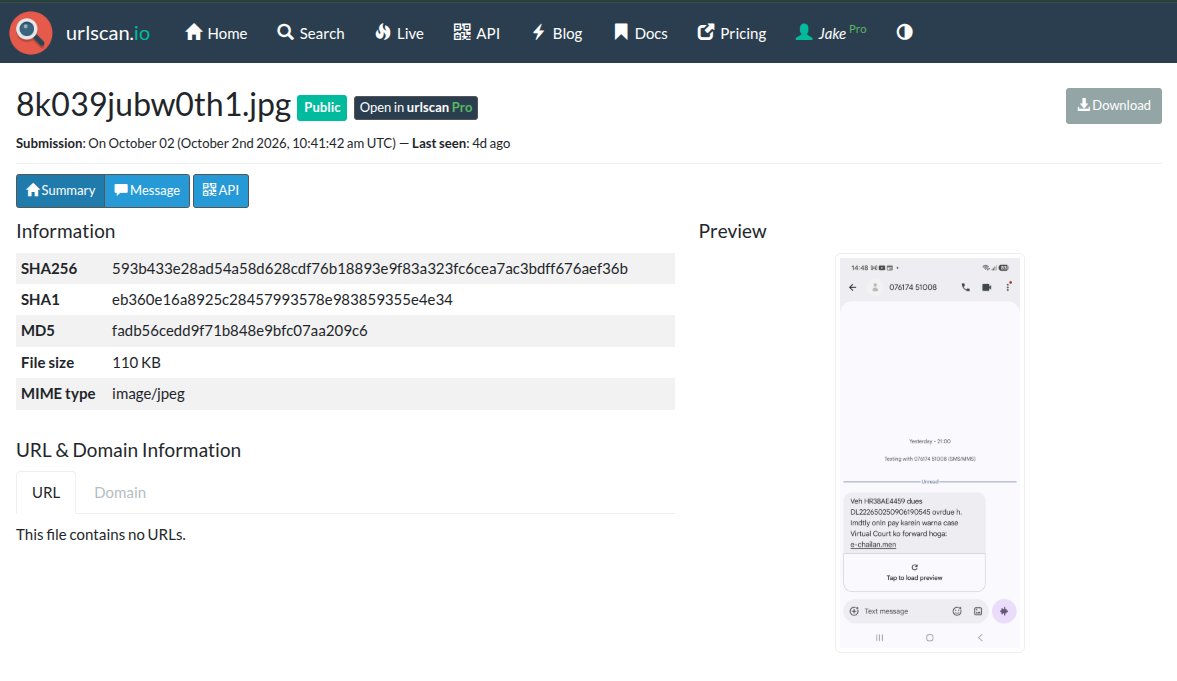
Using the new @urlscanio Files feature, I recently uncovered a targeted Indian eChallan malware campaign! 📱 🇮🇳
🎯 Here is how the attack chain unfolded:
The best part? By leveraging https://t.co/OZDj7hRuBU file capabilities, I was able to seamlessly upload the screenshot, scan the malicious landing page, and extract the APK for full analysis - all within a single workflow. 📈
This is a highly targeted banking cluster 🏦
🌐Clustering on web infrastructure was pivotal in this investigation
These admin panels are critical to managing this campaign 🎯
We pivoted on NS infrastructure to uncover a UK banking phishing network powered by two central panels: FastFlux and FluxPanel. Pages prompt victims for a 6-digit code provided by a phone "advisor" to trigger downloads of a RAT disguised as verification.
Report on urlscan Pro.
We pivoted on NS infrastructure to uncover a UK banking phishing network powered by two central panels: FastFlux and FluxPanel. Pages prompt victims for a 6-digit code provided by a phone "advisor" to trigger downloads of a RAT disguised as verification.
Report on urlscan Pro.
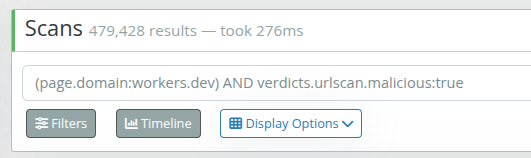
@Malwarehunterr You didn't check @urlscanio - Detected as malicious targeting Google.
Don't trust VT with phishing detection - Trust the experts at @urlscanio!!
https://t.co/wJmcGT2l9M
urlscan Pro University is officially LIVE!
Master urlscan search through hands-on challenges - from basic to advanced
Discover typosquat detection, threat verdicts, and phish hunting.
Solve challenges, submit flags, track your progress.
https://t.co/QXV9KYMxD1
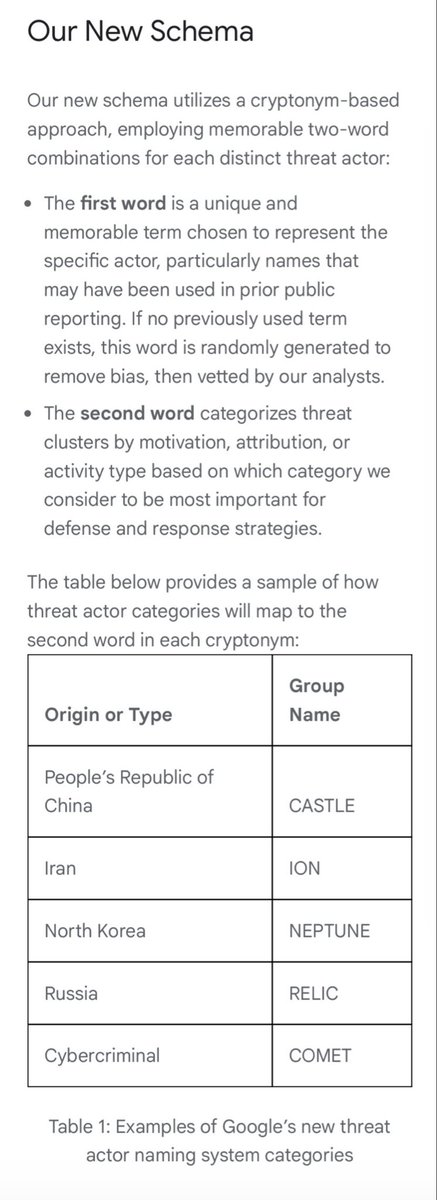
It always surprises me how companies rarely have unique ideas or thoughts. Everyone just copies everyone else.
Maybe someone should actually stop and think - Is this really the best way to be labeling threat clusters?
The answer is No. But because others do it we should copy.
CY-Kit (sorry for the boring name) is a new, previously undocumented, Chinese language phishing as a service kit 🇨🇳
🔎Read the public blog now with a more in-depth report for Pro users.
🥷🏼All scans linked to this framework are labelled on urlscan Pro making attribution easy!
New report 🚨
CY-Kit leverages socket-based communication and structured config files to manage phishing workflows.
A flexible framework built for scalable campaign execution.
The report is available on our public blog: https://t.co/JPYzyyhq9M
@volrant136@Huntio@urlscanio The URL pattern is due to the deploying actor so that it can't be used to track a framework. The HTML is the same and these sites trigger the phoenix system signatures. Happy to discuss more in DMs!
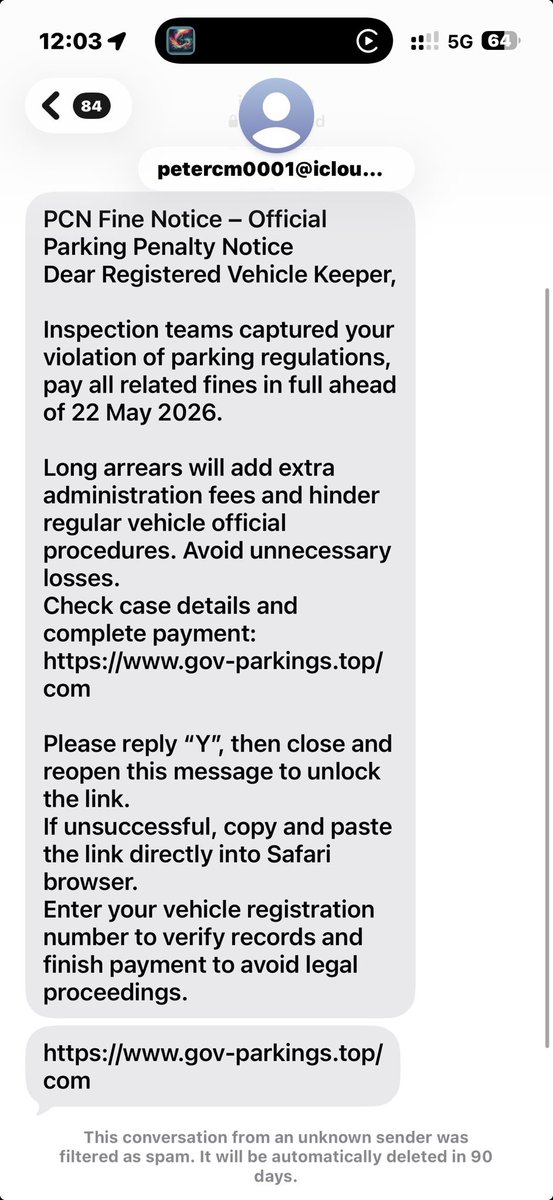
@Huntio@urlscanio Here is a UK SMS example of this framework.
These are some scans of the same cluster all on the same IP as the hostname in the SMS
🌐https://t.co/0DjjZKc7X3
🌐https://t.co/CDR6DTsk97
@Huntio This cluster is Mouse/Phoenix system 🐭
➡️Covered here: https://t.co/gFGxY83Seq
🔎And @urlscanio will have a report coming out very soon on this phishing framework.