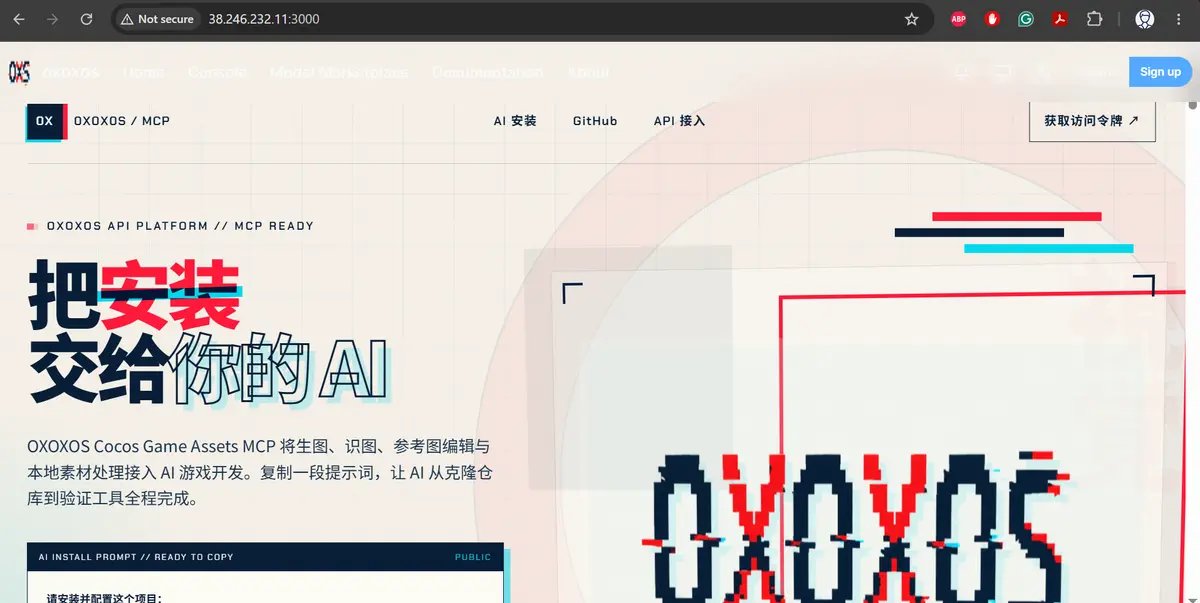
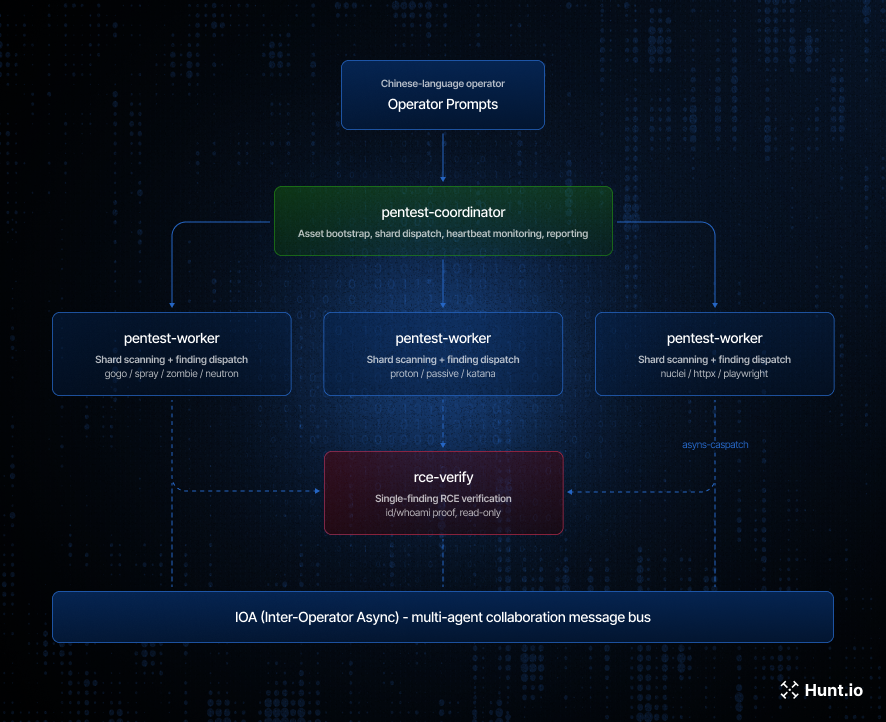
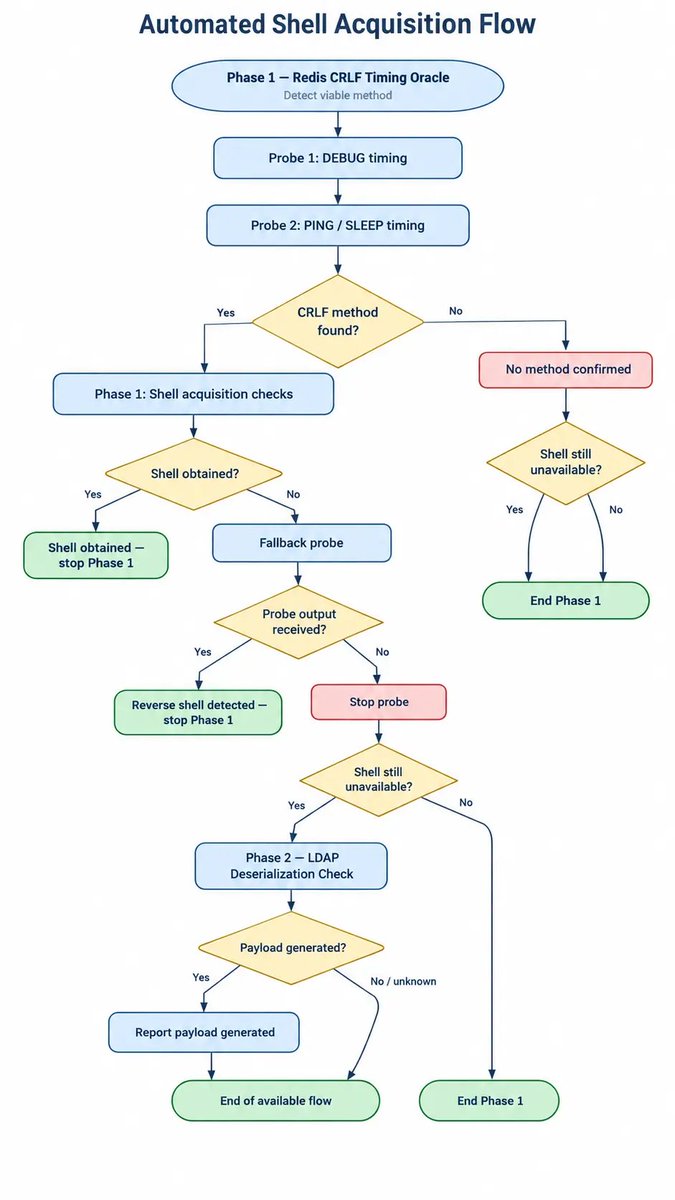
🚨#opendir from @Huntio at 31.77.229[.]26:80 with #PentAGI running and route through test-api[.claude[.gg using a letum-max model to target rbxcrate[.com.
#Attacks: Cloudflare bypass, SSRF, payment webhooks, IDOR, race conditions, CVE-2026-111497 as a Brotli probe hypothesis.
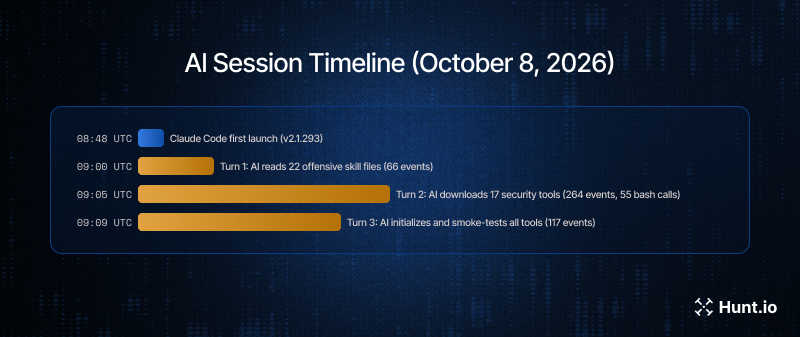
An AI-powered #offensive platform (aiscan + DeepSeek v4-pro) that read 22 #attack playbooks, downloaded 17 security tools, and #confirmed operational readiness in under 9 minutes.
Full dissection 👇
https://t.co/R1RdJAI11a
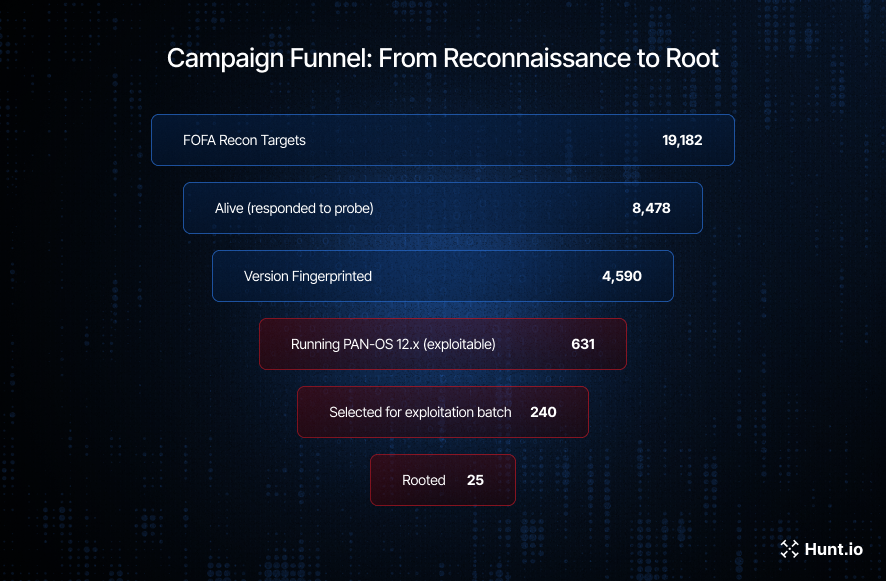
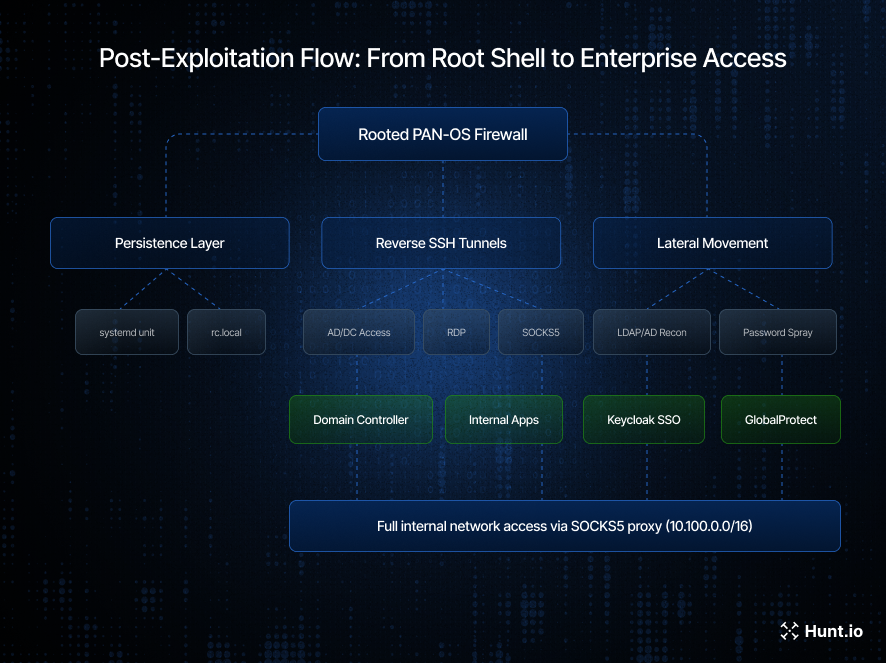
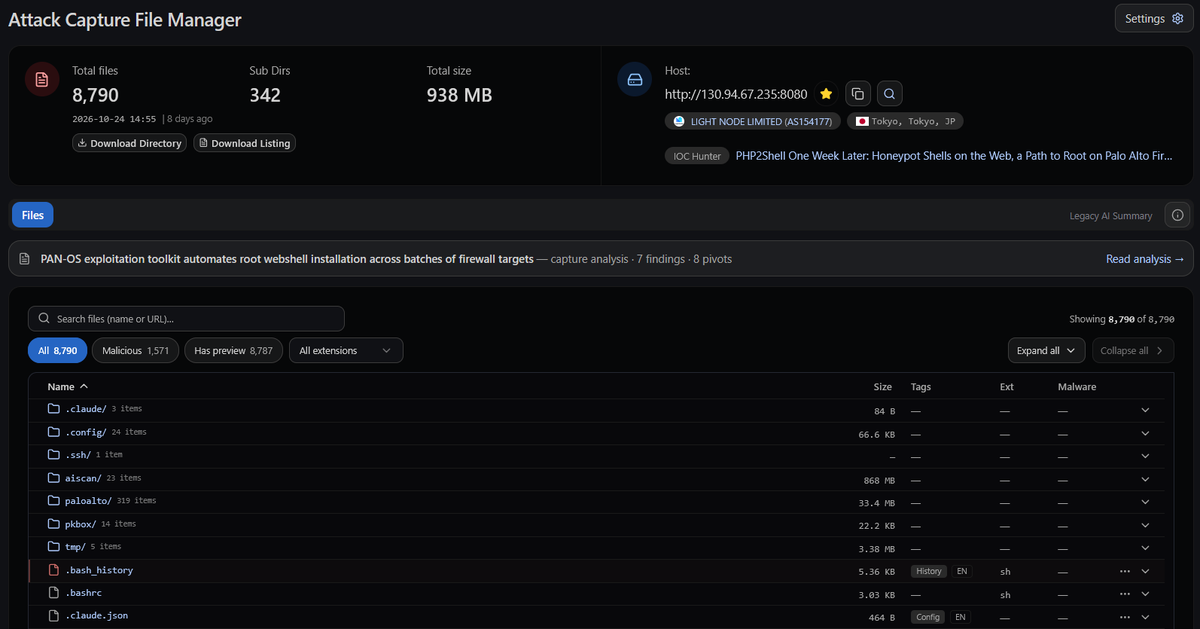
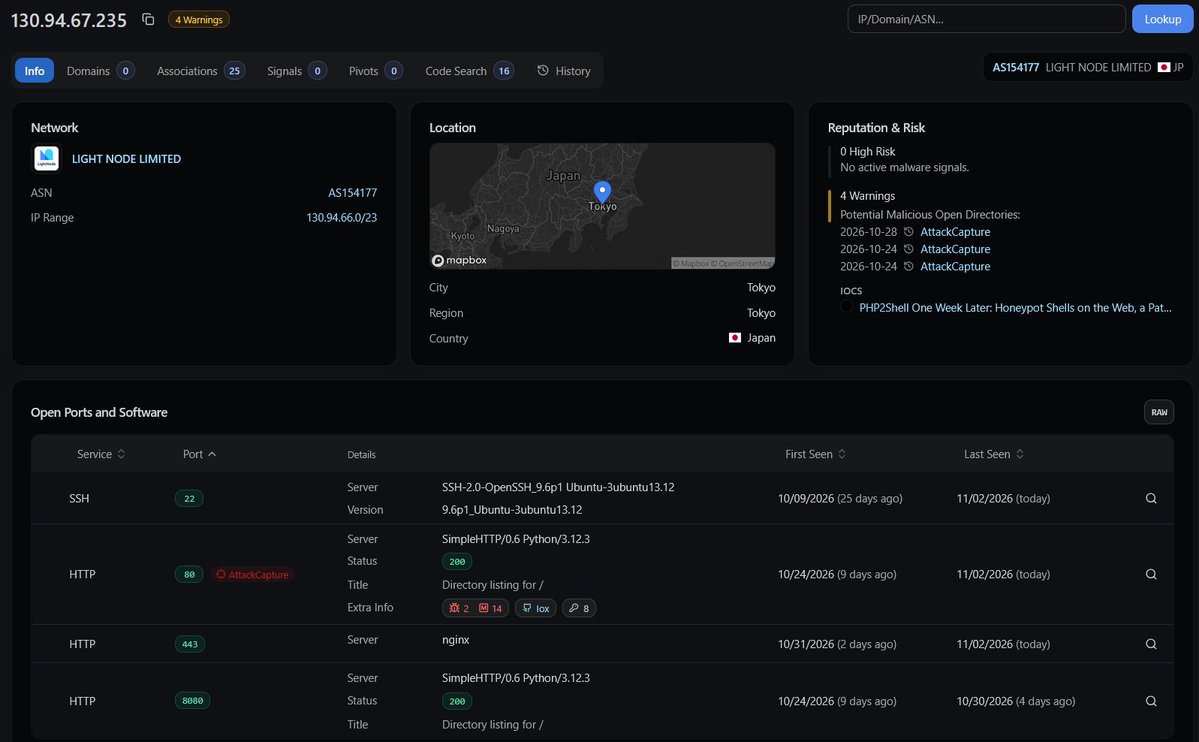
New Investigation on Palo Alto #Exploitation@Huntio AttackCapture™ caught a fully operational exploitation #toolkit at 130.94.67[.]235:8080. Inside: a 4-stage #exploit chain (#PHP memory corruption → #Fragnesia kernel LPE) that achieves root on #Palo#Alto firewalls.
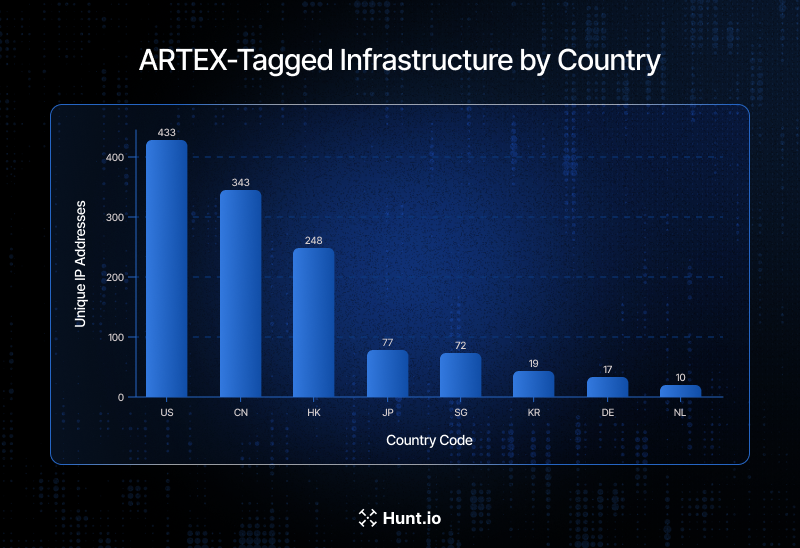
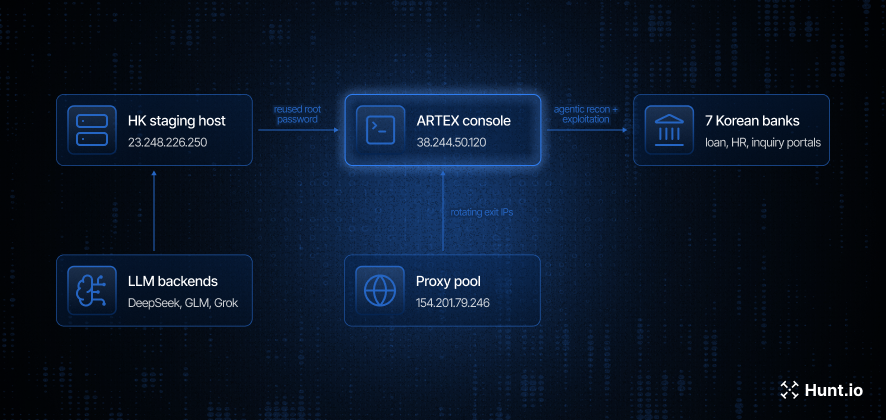
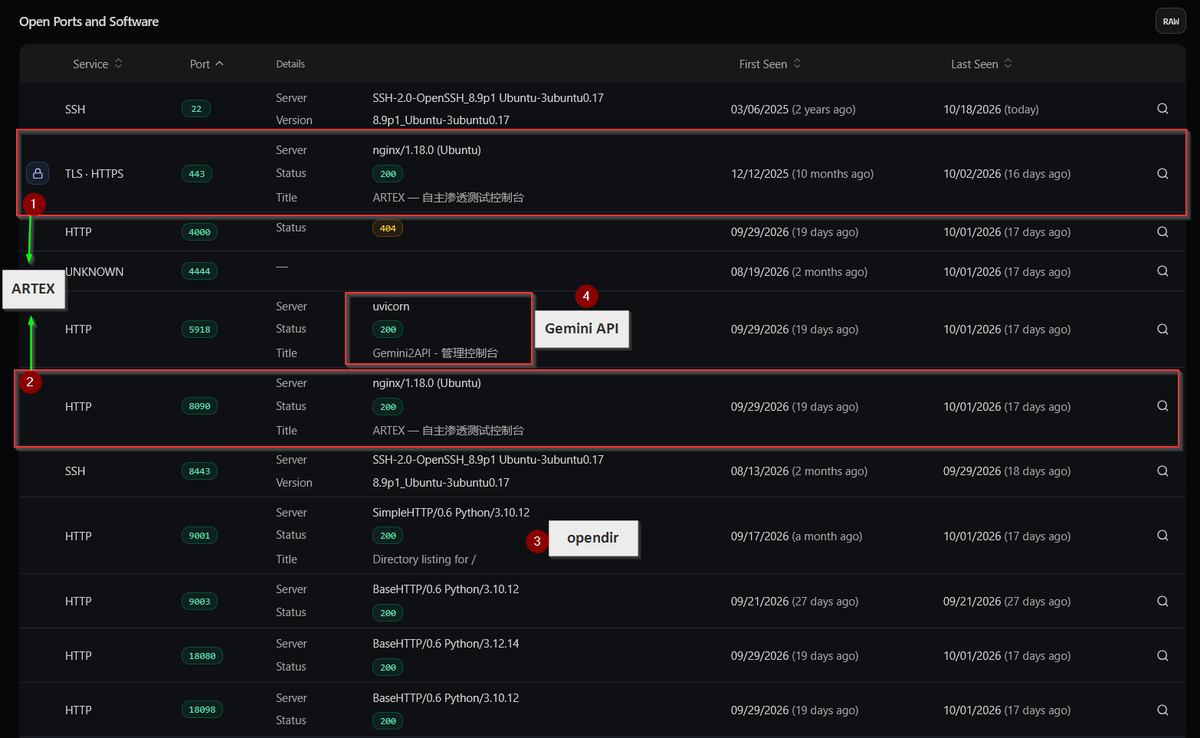
New Blog on #ARTEX from @Huntio#Pivoted from the known console host 38.244.50[.]120 to a second #opendir at 23.248.226[.]250 — a Hong Kong jump server exposing .secrets files, reverse SSH tunnels, Claude Code + DeepSeek/GLM/Grok routing shims, and a staged JNDI/LDAP #RCE chain.
New #threatintel research using @Huntio 🔥
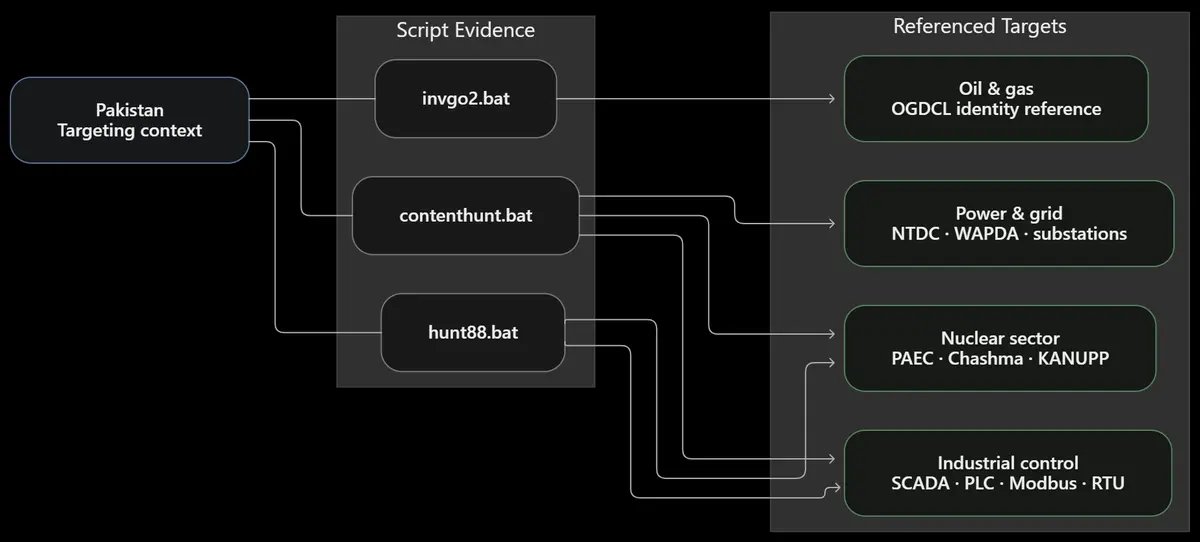
An exposed #opendir on 193.29.104[.]84:8099 leaked 48 files from what looks like an active #APT#DONOT operation targeting #Pakistan’s nuclear and energy sectors.
Full breakdown:
https://t.co/QzAYu3Zqfi
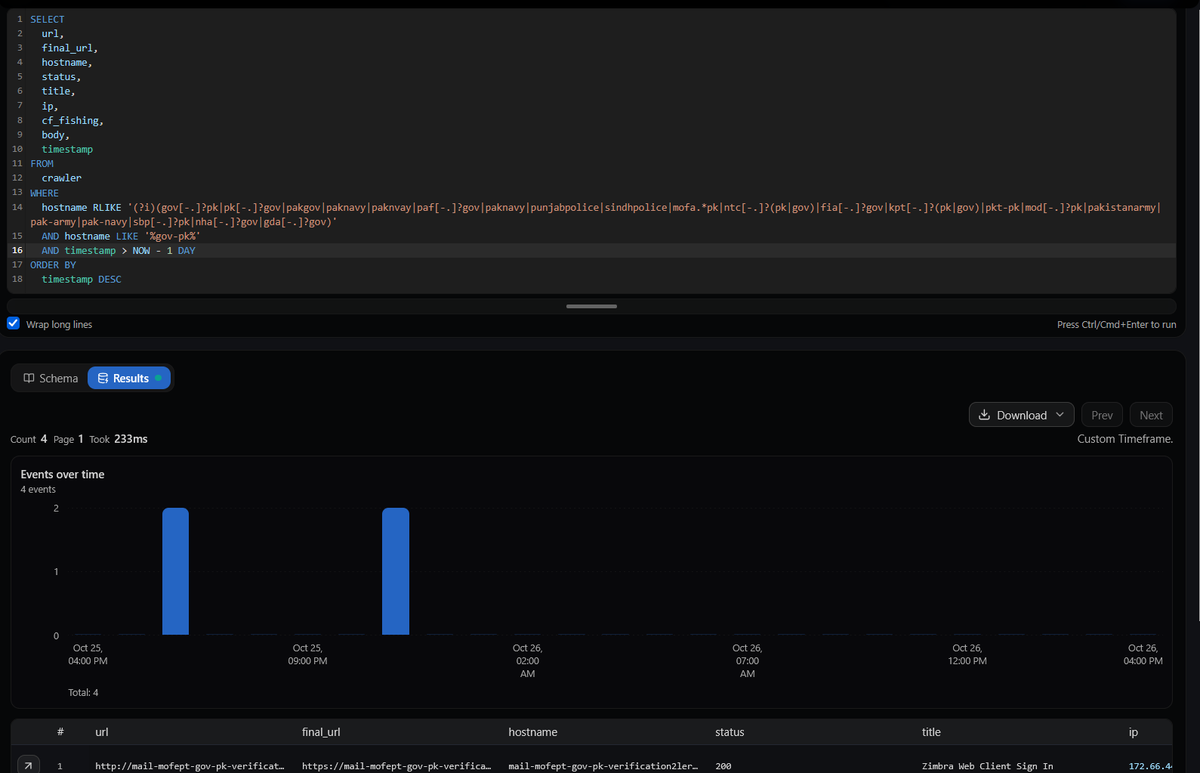
Noticed a fully FUD on VT Cobalt archive that was seen from Singapore. It's a strange one:
C2 domain base: PNAlumni.dgitd.anchorbolnorth[.]com - the registrant is supposedly from Pakistan
IP: 119.160.105[.]93 - belongs to a Pakistani telecom company, and in 2024, the "official website of the Pakistan Navy War College (PNWC)" was seen resolving to this IP...
🤔
🤷♂️
@Huntio The #operator built a rogue #LDAP federation provider pointing to their own server, a script-based authenticator running Runtime.getRuntime().exec("id"), and a custom theme provider targeting a writable path.
All of it configured inside the #ministry’s #Keycloak instance.
@Huntio The #primary target: the #MoFA’s Keycloak SSO at sso-ingo[.mofa[.gov.]vn.
The toolkit confirms admin-level access — a 420 KB /admin/serverinfo export, realm #config dumps for cucngoaivu and master, and a captured #JWT with impersonation + manage-users permissions.
3/
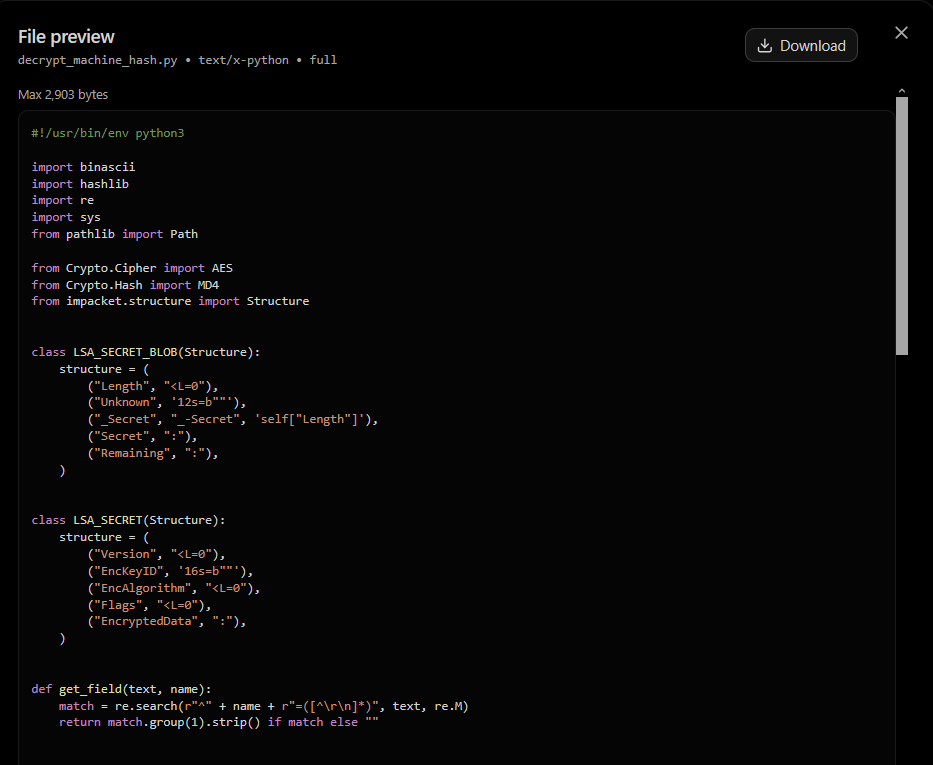
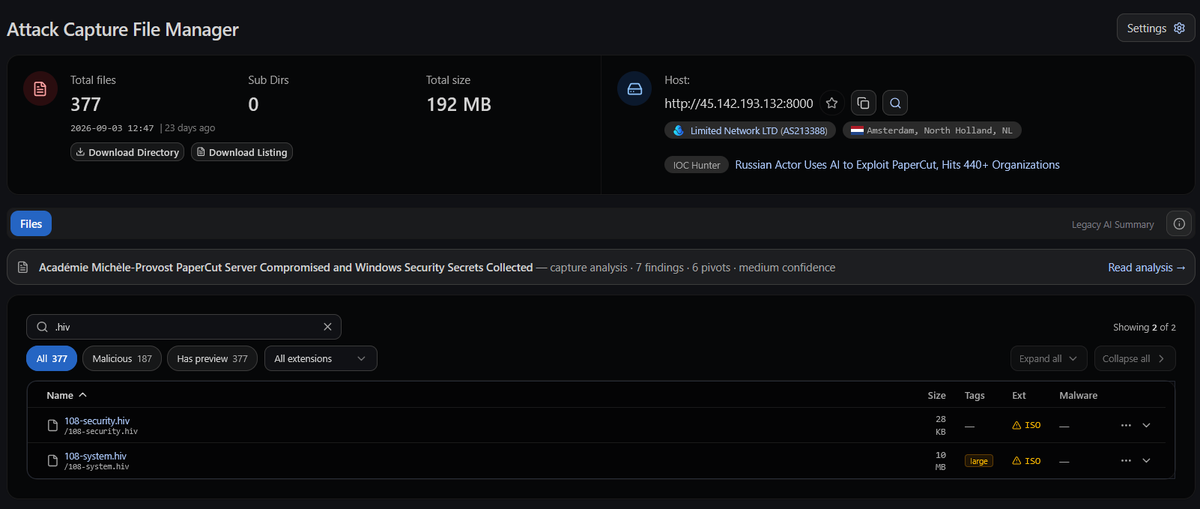
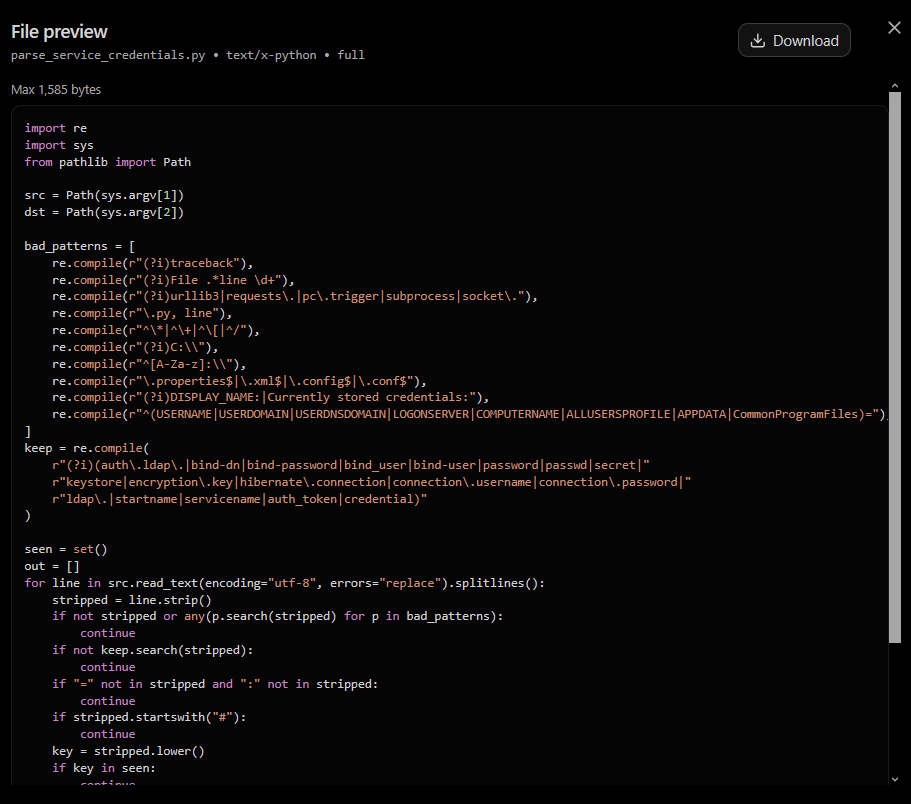
A full post-exploitation pipeline: Windows credential/#LSA#harvesting, #PaperCut servers converted into internal network pivots via reverse #SOCKS5, automated #Metasploit exploitation at scale, and ready-to-redeploy “kits” for confirmed victims.
🚨New Research from @Huntio
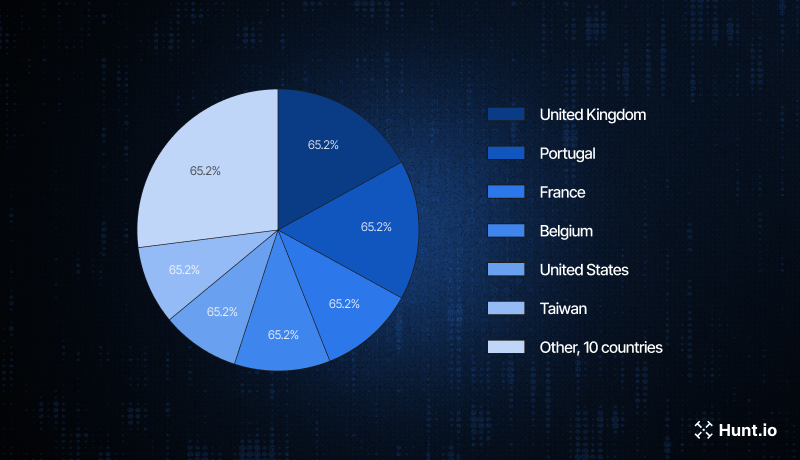
A #PaperCut attacker left their #AI exploitation workbench exposed on an #opendir. We got a look inside: agent instructions, exploit code, a second #RCE path, and victims in 45+ countries.
Full writeup: https://t.co/ixuRjdK2v9
2/ Beyond the known #Tapestry#bypass (CVE-2026-81578 / CVE-2026-82078), the actor’s own notes document a second #RCE path by abusing PaperCut’s XML-RPC API when token/network controls are weak.
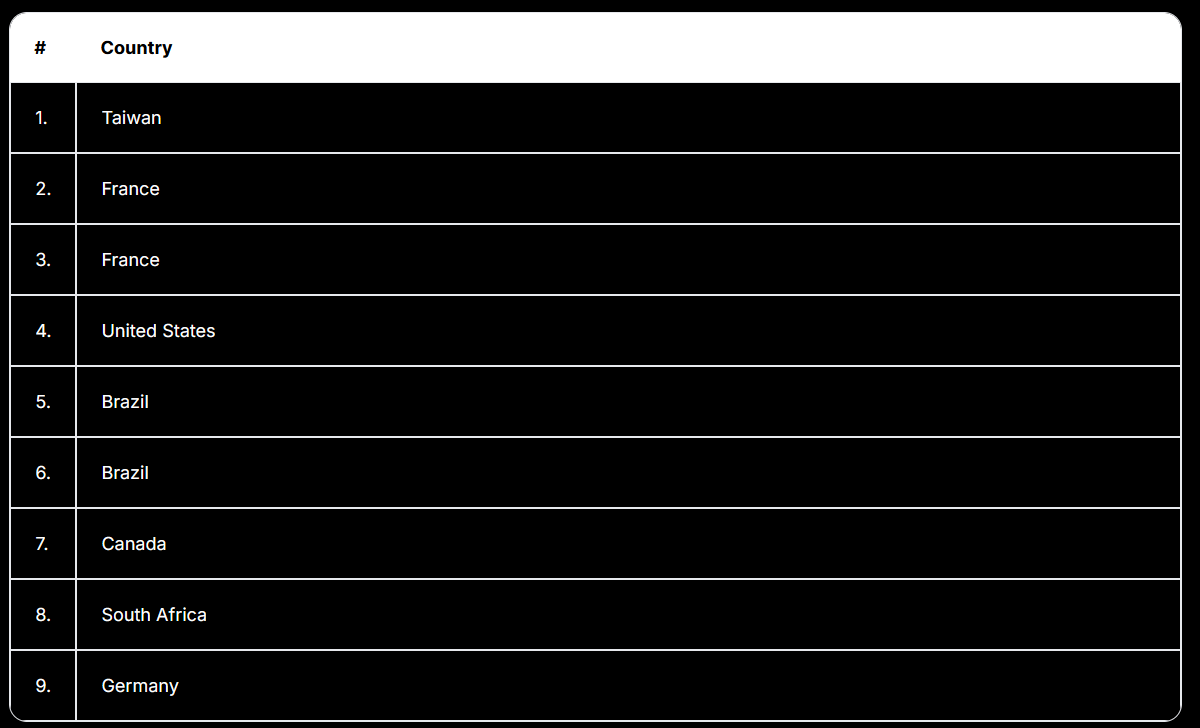
Almost 9 hosts from different #countries were targeted in #undocumented Exploit.


![volrant136's tweet photo. 🚨#opendir from @Huntio at 31.77.229[.]26:80 with #PentAGI running and route through test-api[.claude[.gg using a letum-max model to target rbxcrate[.com.
#Attacks: Cloudflare bypass, SSRF, payment webhooks, IDOR, race conditions, CVE-2026-111497 as a Brotli probe hypothesis. https://t.co/i7zhwNQ76N](https://pbs.twimg.com/media/HWdgtwxbUAAgS0M.jpg)
![volrant136's tweet photo. 🚨#opendir from @Huntio at 31.77.229[.]26:80 with #PentAGI running and route through test-api[.claude[.gg using a letum-max model to target rbxcrate[.com.
#Attacks: Cloudflare bypass, SSRF, payment webhooks, IDOR, race conditions, CVE-2026-111497 as a Brotli probe hypothesis. https://t.co/i7zhwNQ76N](https://pbs.twimg.com/media/HWdfhwEawAAbKN7.png)
![volrant136's tweet photo. 🚨#opendir from @Huntio at 31.77.229[.]26:80 with #PentAGI running and route through test-api[.claude[.gg using a letum-max model to target rbxcrate[.com.
#Attacks: Cloudflare bypass, SSRF, payment webhooks, IDOR, race conditions, CVE-2026-111497 as a Brotli probe hypothesis. https://t.co/i7zhwNQ76N](https://pbs.twimg.com/media/HWdfdKgawAAlgt8.jpg)







![volrant136's tweet photo. @Huntio The #primary target: the #MoFA’s Keycloak SSO at sso-ingo[.mofa[.gov.]vn.
The toolkit confirms admin-level access — a 420 KB /admin/serverinfo export, realm #config dumps for cucngoaivu and master, and a captured #JWT with impersonation + manage-users permissions. https://t.co/hgUVvsbPyn](https://pbs.twimg.com/media/HVKW419boAEUGin.jpg)
![volrant136's tweet photo. @Huntio The #primary target: the #MoFA’s Keycloak SSO at sso-ingo[.mofa[.gov.]vn.
The toolkit confirms admin-level access — a 420 KB /admin/serverinfo export, realm #config dumps for cucngoaivu and master, and a captured #JWT with impersonation + manage-users permissions. https://t.co/hgUVvsbPyn](https://pbs.twimg.com/media/HVKW12ja4AAxN70.jpg)
![volrant136's tweet photo. @Huntio The #primary target: the #MoFA’s Keycloak SSO at sso-ingo[.mofa[.gov.]vn.
The toolkit confirms admin-level access — a 420 KB /admin/serverinfo export, realm #config dumps for cucngoaivu and master, and a captured #JWT with impersonation + manage-users permissions. https://t.co/hgUVvsbPyn](https://pbs.twimg.com/media/HVKWyqLbEAE7CxE.jpg)